Best Attack Surface Management Software

How Many Attack Surface Management Software Products Does G2 Track?

Total Products under this Category: 191

Category Stats (Oct 2026)

  • Average Rating: 4.59/5 (↓0.01 vs Sep 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Hunto AI (+1.58%) - Among all products in this category, Hunto AI recorded the largest rating increase compared to last month

Last updated: October 07, 2026

How Does G2 Rank Attack Surface Management Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,900+ Authentic Reviews
  • 191+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

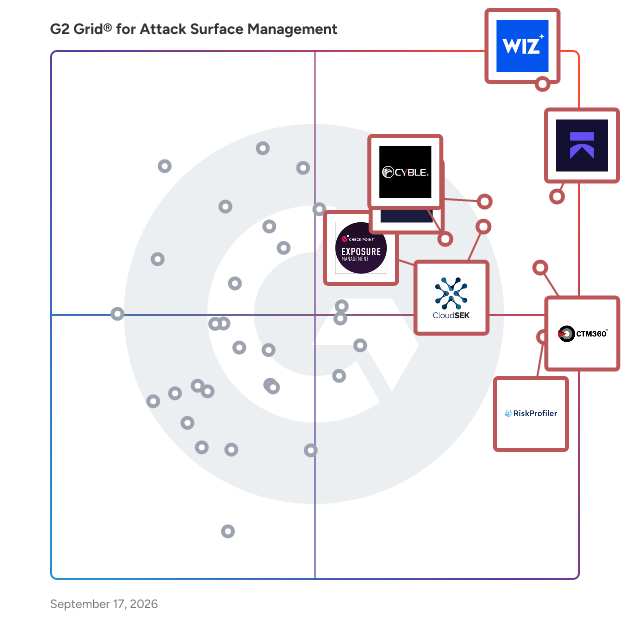
G2 Grid® for Attack Surface Management Software

G2 Grid® for  Attack Surface Management Software plotting products by satisfaction and market presence

Highlighted products: Wiz, Aikido Security, SOCRadar Extended Threat Intelligence, CTM360, CloudSEK, Cyble, RiskProfiler - External Threat Exposure Management, and Check Point Exposure Management.

Underlying data: [Grid® JSON](https://www.g2.com/categories/attack-surface-management/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=aikido-security&focus%5B%5D=socradar-extended-threat-intelligence&focus%5B%5D=ctm360-ctm360&focus%5B%5D=cloudsek&focus%5B%5D=cyble&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=check-point-exposure-management)

Wiz

Wiz transforms cloud security for customers – including more than 50% of the Fortune 100 – by enabling a new operating model. With Wiz, organizations can democratize security across the development lifecycle, empowering them to build fast and securely. Its Cloud Native Application Protection Platform (CNAPP) consolidates CSPM, KSPM, CWPP, Vulnerability management, IaC scanning, CIEM, DSPM into a single platform. Wiz drives visibility, risk prioritization, and business agility. Protecting Your Cloud Environments Requires a Unified, Cloud Native Platform. Wiz connects to every cloud environment, scans every layer, and covers every aspect of your cloud security - including elements that normally require installing agents. Its comprehensive approach has all of these cloud security solutions built in. Hundreds of organizations worldwide, including 50 percent of the Fortune 100, to rapidly identify and remove critical risks in cloud environments. Its customers include Salesforce, Slack, Mars, BMW, Avery Dennison, Priceline, Cushman & Wakefield, DocuSign, Plaid, and Agoda, among others. Wiz is backed by Sequoia, Index Ventures, Insight Partners, Salesforce, Blackstone, Advent, Greenoaks, Lightspeed and Aglaé. Visit https://www.wiz.io for more information.

Average Rating: 4.7/5.0

Total Reviews: 841

How Do G2 Users Rate Wiz?

  • Vulnerability Intelligence: 9.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.8/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Wiz?

  • Seller: Wiz
  • Company Website:
  • Year Founded: 2020
  • HQ Location: New York, US
  • Twitter: @wiz_io
    24,733 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,147 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CISO, Security Engineer
  • Top Industries: Financial Services, Computer Software
  • Company Size: 53% Large, 39% Medium

What Do G2 Reviewers Say About Wiz?

AI-generated summary from verified user reviews

Pros
  • Users value the robust APIs and user-friendly UI, appreciating ongoing improvements and a wealth of insightful issues.
  • Users value the continuous enhancement of security features by Wiz, appreciating the support and innovation in their tool.
  • Users appreciate the ease of use of Wiz, benefiting from its user-friendly interface and seamless integration.
  • Users value the comprehensive visibility Wiz provides, enhancing security and prioritizing essential aspects of their cloud environment.
  • Users appreciate the easy setup of Wiz, enabling a quick and seamless integration into their workflows.
Cons
  • Users find a significant learning curve in mastering Wiz's extensive features, which can hinder initial usage.
  • Users find the feature limitations of Wiz frustrating, especially with complex management and reporting challenges.
  • Users note that improvement is needed for laggy query responses and better dashboard reporting capabilities.
  • Users identify improvements needed in dashboard reporting and feature streamlining for better usability and budgeting.
  • Users find the interface overwhelming initially, facing a steep learning curve and complex licensing issues.

What Are Recent G2 Reviews of Wiz?

Aikido Security

Aikido Security is the developer-first security platform that unifies code, cloud, protection, and attack testing in one suite of best-in-class products. Built by developers for developers, Aikido helps teams of any size ship secure software faster, automate protection, and simulate real-world attacks with AI-driven precision. The platform’s proprietary AI cuts noise by 95%, delivers one-click fixes, and saves developers 10+ hours per week. Aikido Intel proactively uncovers vulnerabilities in open source packages before disclosure, helping secure more than 50,000 organizations worldwide, including Revolut, Niantic, Visma, Montblanc, and GoCardless.

Average Rating: 4.6/5.0

Total Reviews: 266

How Do G2 Users Rate Aikido Security?

  • Ease of Admin: 9.4/10 (Category avg: 9.0/10)

Who Is the Company Behind Aikido Security?

  • Seller: Aikido Security
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Ghent, Belgium
  • Twitter: @AikidoSecurity
    11,770 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    320 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Founder, CTO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 78% Small, 15% Medium

What Do G2 Reviewers Say About Aikido Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Aikido Security, thanks to its clear insights and seamless integration.
  • Users appreciate Aikido Security's robust security capabilities, providing a comprehensive and seamless integration in their workflow.
  • Users value the intuitive dashboard of Aikido Security, which simplifies security issue identification and management.
  • Users value the easy integrations of Aikido Security, enhancing workflows with seamless connections to existing GitLab repositories.
  • Users find Aikido's easy setup highly efficient, enabling quick implementation and immediate usability for security assessments.
Cons
  • Users note the lack of advanced features in Aikido Security, such as dark mode and in-depth analysis options.
  • Users find the pricing structure expensive for micro businesses, making upgrades difficult to justify.
  • Users note the limited features of Aikido Security, wishing for more customization and advanced options.
  • Users find the pricing issues challenging, especially for micro businesses, due to the steep upgrade costs.
  • Users feel Aikido Security is lacking features like advanced reporting and deeper compliance analysis compared to competitors.

What Are Recent G2 Reviews of Aikido Security?

SOCRadar Extended Threat Intelligence

Since 2019, SOCRadar has been a pioneer in SaaS cybersecurity, now serving over 900 customers across 75 countries. Our mission is to provide accessible, proactive threat intelligence. Today, SOCRadar empowers security teams with our groundbreaking Extended Threat Intelligence (XTI) platform and is leading the charge toward the future with Agentic Threat Intelligence (ATI). What does SOCRadar do? At its core, SOCRadar provides a unified, cloud-hosted platform designed to enrich your cyber threat intelligence by contextualizing it with data from your attack surface, digital footprint, dark web exposure, and supply chain. We help security teams see what attackers see by combining External Attack Surface Management, Cyber Threat Intelligence, and Digital Risk Protection into a single, easy-to-use solution. This enables your organization to discover hidden vulnerabilities, detect data leaks, and shut down threats like phishing and brand impersonation before they can harm your business. By combining these critical security functions, SOCRadar replaces the need for separate, disconnected tools. Our holistic approach offers a streamlined, modular experience, providing a complete, real-time view of your threat landscape to help you stay ahead of attackers. Our vision for Agentic Threat Intelligence (ATI) goes beyond today's chatbots and LLMs. We are focused on making it practical for security teams to use AI agents to solve real-world problems. Our initiative will empower you to either deploy pre-built agents or easily create your own, leveraging deep integrations to automate complex tasks that were previously difficult to perform accurately. SOCRadar is dedicated to pioneering this change, making autonomous security an accessible reality for your team.

Average Rating: 4.7/5.0

Total Reviews: 119

How Do G2 Users Rate SOCRadar Extended Threat Intelligence?

  • Vulnerability Intelligence: 9.2/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.3/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.4/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.2/10 (Category avg: 9.0/10)

Who Is the Company Behind SOCRadar Extended Threat Intelligence?

  • Seller: SOCRadar
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Delaware
  • Twitter: @socradar
    5,748 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    195 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 43% Medium, 41% Large

What Do G2 Reviewers Say About SOCRadar Extended Threat Intelligence?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of SOCRadar, enjoying its intuitive dashboards and centralized threat data management.
  • Users value the comprehensive Threat Intelligence features of SOCRadar, enabling effective risk awareness and proactive security measures.
  • Users value the comprehensive and actionable alert notifications from SOCRadar, enhancing their security monitoring and response efforts.
  • Users appreciate the exceptional visibility into external threats, benefiting from a centralized and proactive intelligence platform.
  • Users value the exceptional visibility SOCRadar provides into external threats, enhancing proactive security measures significantly.
Cons
  • Users are frustrated by the inefficient alerts, leading to noise and fatigue from duplicate notifications and false positives.
  • Users report that the inefficient alert system leads to alert fatigue and necessitates extensive tuning for effectiveness.
  • Users struggle with false positives and duplicate notifications, leading to alert fatigue and a need for extensive tuning.
  • Users note the limited features in SOCRadar Extended Threat Intelligence, hindering deeper analysis without upgrading.
  • Users find the insufficient information from SOCRadar Extended Threat Intelligence to hinder effective decision-making.

What Are Recent G2 Reviews of SOCRadar Extended Threat Intelligence?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

CTM360

CTM360 is a consolidated external security platform that integrates External Attack Surface Management, Digital Risk Protection, Cyber Threat Intelligence, Brand Protection & Anti-phishing, Surface, Deep, & Dark Web Monitoring, Security Ratings, Third-party risk Management, and fully managed unlimited Takedowns. As a pioneer and innovator in preemptive security, CTM360 operates as an external CTEM technology platform outside an organization’s perimeter. Seamless and turn-key, CTM360 requires no configurations, installations or inputs from the end-user, with all data pre-populated and specific to your organization. All aspects are managed by CTM360.

Average Rating: 4.6/5.0

Total Reviews: 173

How Do G2 Users Rate CTM360?

  • Vulnerability Intelligence: 9.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.1/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.8/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.7/10 (Category avg: 9.0/10)

Who Is the Company Behind CTM360?

  • Seller: CTM360
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Manama, BH
  • Twitter: @teamCTM360
    999 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    136 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Banking, Financial Services
  • Company Size: 37% Medium, 37% Large

What Do G2 Reviewers Say About CTM360?

AI-generated summary from verified user reviews

Pros
  • Users commend the top-notch customer support of CTM360, highlighting responsive and knowledgeable assistance at every level.
  • Users commend the ease of use of CTM360, appreciating its straightforward setup and user-friendly interface.
  • Users admire the comprehensive platform of CTM360, which effectively enhances proactive cybersecurity and incident response.
  • Users commend the effective monitoring capabilities of CTM360, aiding quick identification of risks and enhancing security posture.
  • Users praise the high detection efficiency of CTM360, appreciating its accuracy and proactive risk management capabilities.
Cons
  • Users note the limited features of CTM360, particularly on the Android app compared to the web portal.
  • Users are frustrated by the integration issues with existing security infrastructures, seeking better compatibility and usability.
  • Users note a lack of features in CTM360, particularly compared to the web portal and community edition limitations.
  • Users face a lack of integration with existing security systems, limiting automated data feeds and user experience.
  • Users find the lack of integrations with existing security tools limits automated daily security feeds and functionality.

What Are Recent G2 Reviews of CTM360?

CloudSEK

CloudSEK is a contextual AI company that predicts Cyber Threats. We combine the power of Cyber Crime monitoring, Brand Monitoring, Attack Surface monitoring, and Supply Chain intelligence to give context to our customers’ digital risks.

Average Rating: 4.8/5.0

Total Reviews: 137

How Do G2 Users Rate CloudSEK?

  • Vulnerability Intelligence: 9.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.6/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.4/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.6/10 (Category avg: 9.0/10)

Who Is the Company Behind CloudSEK?

  • Seller: CloudSEK
  • Year Founded: 2015
  • HQ Location: Singapore, SG
  • Twitter: @cloudsek
    2,417 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    247 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Analyst, Analyst
  • Top Industries: Financial Services, Airlines/Aviation
  • Company Size: 53% Large, 31% Medium

What Do G2 Reviewers Say About CloudSEK?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of CloudSEK, noting its smooth functions and intuitive dashboard for seamless monitoring.
  • Users value the continuous monitoring and real-time alerts provided by CloudSEK for effective brand oversight.
  • Users praise the responsive customer support of CloudSEK, which effectively resolves issues quickly and efficiently.
  • Users praise CloudSEK's excellent coverage and AI-driven threat intelligence, enhancing cybersecurity and providing invaluable insights.
  • Users value the real-time visibility into external threats offered by CloudSEK, enhancing proactive risk management.
Cons
  • Users are frustrated by the high rate of false positives in alerts for credential breaches and domain impersonation.
  • Users experience inefficient alerts from CloudSEK, often overwhelming them with false positives and complicating threat prioritization.
  • Users experience dashboard issues with false positives, cluttered layouts, and a need for further customization and basic features.
  • Users experience inefficient alert systems, struggling with false positives and difficulty in managing genuine threats effectively.
  • Users find the complex UI of CloudSEK overwhelming, making it challenging to interpret key information effectively.

What Are Recent G2 Reviews of CloudSEK?

Cyble

Cyble is an AI-native cybersecurity solution designed to help organizations enhance their digital security posture through real-time intelligence, detection, and response capabilities. By leveraging advanced agentic AI and processing vast amounts of data, Cyble empowers businesses to navigate the complexities of the cyber threat landscape effectively. Its unique approach involves collecting and enriching signals from various sources, including the dark web, deep web, and surface web, providing unparalleled visibility into emerging threats and adversarial activities. Targeting a wide range of industries, Cyble's platform is particularly beneficial for security teams, risk management professionals, and organizations that prioritize safeguarding their digital assets. The comprehensive suite of solutions offered by Cyble includes Threat Intelligence, Dark Web & Deep Web Monitoring, Attack Surface Management (ASM), and Brand Intelligence, among others. These tools are designed to address specific use cases such as identifying vulnerabilities, monitoring brand reputation, and managing third-party risks, making it an essential resource for organizations aiming to bolster their cybersecurity measures. Cyble's key features are centered around its unified platform, which integrates multiple cybersecurity functions into a single interface. This integration allows for seamless communication between different security components, enabling teams to anticipate, identify, and neutralize threats with remarkable speed and precision. For instance, the Digital Forensics & Incident Response (DFIR) capabilities equip organizations with the tools needed to investigate and respond to incidents effectively, while the DDoS Protection and Cloud Security Posture Management (CSPM) features ensure that businesses can maintain operational integrity even under attack. Moreover, Cyble stands out in its category by combining vast data intelligence with cutting-edge AI automation. This proactive defense strategy not only helps organizations react to cyber threats but also empowers them to stay ahead of potential risks. By enhancing visibility into the threat landscape and providing actionable insights, Cyble enables enterprises to protect their assets, safeguard brand trust, and operate with confidence in an increasingly complex digital environment. The result is a robust cybersecurity framework that supports organizations in navigating the ever-evolving challenges of the cyber world.

Average Rating: 4.8/5.0

Total Reviews: 147

How Do G2 Users Rate Cyble?

  • Vulnerability Intelligence: 9.5/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.5/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.1/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.6/10 (Category avg: 9.0/10)

Who Is the Company Behind Cyble?

  • Seller: Cyble
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Alpharetta, US
  • Twitter: @cybleglobal
    16,252 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    233 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 39% Large, 17% Medium

What Do G2 Reviewers Say About Cyble?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the intuitive dashboard and user-friendly UI of Cyble, enhancing their overall experience with the platform.
  • Users value Cyble for its comprehensive threat intelligence, ensuring quick responses and seamless integrations within their security operations.
  • Users value Cyble's state-of-the-art tools for threat hunting, seamlessly combining protection and monitoring in one solution.
  • Users value the real-time insights and ease of use of Cyble for effective cybersecurity management.
  • Users appreciate the real-time threat detection of Cyble, greatly enhancing their digital risk protection and response capabilities.
Cons
  • Users report inefficient alerts with Cyble, experiencing duplicate notifications and unreliable delivery leading to alert fatigue.
  • Users are frustrated with the limited customization options in Cyble, impacting their efficiency and dashboard usability.
  • Users find the poor customer support of Cyble lacking in staff and effective timezone assistance.
  • Users experience poor support management, often facing slow responses that hinder timely resolution of urgent issues.
  • Users experience significant false positives in alerts from Cyble, leading to confusion and inefficient threat management.

What Are Recent G2 Reviews of Cyble?

RiskProfiler - External Threat Exposure Management

RiskProfiler is an advanced cybersecurity platform purpose-built for Continuous Threat Exposure Management (CTEM). It unifies external, cloud, vendor, and brand risk intelligence into a single ecosystem—providing organizations with real-time visibility, contextual threat insights, and actionable remediation guidance. Through its integrated suite, External Attack Surface Managemnet, Third_party Risk Management, Cloud Attack Surface Management, and Brand Risk Protection; the platform continuously discovers, classifies, and evaluates external-facing assets and risks across the internet, multi-cloud environments, and third-party ecosystems. Powered by AI-enabled risk questionnaires, RiskProfiler automates the exchange, validation, and scoring of security assessments, dramatically accelerating third-party due diligence and compliance validation. The platform’s context-enriched graph engine correlates vulnerabilities, exposures, and configurations with real-world threat data, revealing how attackers might exploit an organization’s digital footprint. Its newly enhanced Cyber Threat Intelligence (CTI) module provides live insights into industry-specific attack trends, threat actor profiles, and evolving TTPs, directly embedded within the dashboard. By analyzing CVEs, IOCs, and exploit patterns, it maps these to relevant assets and potential attack paths, enabling focused, prioritized mitigation. From identifying exposed cloud resources across AWS, Azure, and Google Cloud to uncovering brand impersonation, phishing campaigns, or logo abuse, RiskProfiler delivers unified visibility and continuous monitoring that extends beyond the perimeter. It helps organizations anticipate, contextualize, and neutralize threats before they turn into breaches, transforming exposure management into a truly intelligent, predictive defense capability.

Average Rating: 5.0/5.0

Total Reviews: 135

How Do G2 Users Rate RiskProfiler - External Threat Exposure Management?

  • Vulnerability Intelligence: 10.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.9/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.9/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.7/10 (Category avg: 9.0/10)

Who Is the Company Behind RiskProfiler - External Threat Exposure Management?

  • Seller: Riskprofiler
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Rock Hill , US
  • Twitter: @riskprofilerio
    209 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    35 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Security Consultant
  • Top Industries: Information Technology and Services, Design
  • Company Size: 65% Medium, 30% Small

What Do G2 Reviewers Say About RiskProfiler - External Threat Exposure Management?

AI-generated summary from verified user reviews

Pros
  • Users value the multi-dimensional threat intelligence of RiskProfiler, enabling efficient management of external threats and vendor risks.
  • Users value the seamless integration features of RiskProfiler, enhancing real-time monitoring and adaptability in their workflows.
  • Users praise the fast and efficient customer support of RiskProfiler, enhancing their overall experience and threat management.
  • Users value the ease of use of RiskProfiler, as it seamlessly integrates and enhances external threat management.
  • Users highlight the easy setup of RiskProfiler, facilitating quick implementation and seamless integration for effective threat management.
Cons
  • Users face a steep learning curve with RiskProfiler, needing sufficient time for training and customization.
  • Users find the complexity of RiskProfiler challenging, requiring time for training and adjustment to navigate effectively.
  • Users find the difficult learning curve challenging, requiring significant time and training for effective platform use.
  • Users find a steep learning curve with RiskProfiler, requiring time and training for effective use.
  • Users find the complex setup of RiskProfiler challenging, hindering smooth adoption and integration for non-specialist teams.

What Are Recent G2 Reviews of RiskProfiler - External Threat Exposure Management?

Check Point Exposure Management

Exposure Management is changing how organizations react to vulnerabilities that put them in risk. Attackers exploit exposed assets, leaked credentials, and misconfigurations within hours using sophisticated AI attack tools. Meanwhile, security teams are left sorting through dashboards, alerts, and disconnected tools. For a limited time only, we are providing an Agentic Exposure Validation Scan at no cost. It delivers proven, evidence-backed findings your team can act on immediately. Request scan here - https://checkpoint.cyberint.com/limited-time-offer-aev-scan Check Point Exposure Management closes that gap by combining billions of external intelligence signals into a Unified Intelligence Fabric. The platform continuously identifies, validates, prioritizes, and safely remediates the exposures attackers are most likely to exploit. With Cyber Asset Attack Surface Management (CAASM), security teams gain a real-time inventory across cloud, SaaS, on-premises infrastructure, endpoints, and identities through 150+ agentless integrations. Unlike traditional vulnerability management, Check Point prioritizes exposures based on real-world exploitability, active threat intelligence, business context, and existing security controls, eliminating duplicate alerts and reducing remediation noise. It does so while maintaining business continuity. Safe-by-design remediation then validates every action before enforcement, enabling capabilities such as virtual patching, IPS activation, configuration hardening, and policy enforcement without disrupting business operations. Organizations using the platform achieve a 93% true positive rate, 12-hour average takedown MTTR, and 504 safe remediations per organization every month. Built around Gartner's Continuous Threat Exposure Management (CTEM) framework, Check Point helps organizations move from visibility to measurable risk reduction. Gartner predicts organizations adopting CTEM with mobilization will experience 50% fewer successful cyberattacks by 2028. Ready to see Exposure Management in action? Get a 15-minute demo: https://l.cyberint.com/exposure-management-demo

Average Rating: 4.6/5.0

Total Reviews: 198

How Do G2 Users Rate Check Point Exposure Management?

  • Vulnerability Intelligence: 8.8/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 8.7/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.3/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.1/10 (Category avg: 9.0/10)

Who Is the Company Behind Check Point Exposure Management?

Who Uses This Product?

  • Who Uses This: Security Threat Analyst, Cyber Security Analyst
  • Top Industries: Banking, Financial Services
  • Company Size: 66% Large, 21% Medium

What Do G2 Reviewers Say About Check Point Exposure Management?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Check Point Exposure Management, enjoying its intuitive interface for threat detection.
  • Users value the comprehensive threat intelligence from Cyberint, enhancing detection and response to potential threats effectively.
  • Users commend the enhanced threat detection capabilities of Check Point Exposure Management, improving situational awareness and response efficiency.
  • Users value the comprehensive intelligence feeds of Check Point Exposure Management, enhancing threat detection and situational awareness.
  • Users value the immediate alerts from Check Point Exposure Management, allowing prompt action against potential security threats.
Cons
  • Users face challenges with inefficient alerts due to false positives, complicating the verification process for analysts.
  • Users experience false positives that necessitate additional validation time, complicating the overall alert management process.
  • Users find the inefficient alert system complicates handling excessive alerts and delays threat intel on compromised accounts.
  • Users note integration issues with Check Point Exposure Management, particularly regarding centralizing alerts and connecting security tools.
  • Users note the limited features of Check Point Exposure Management, specifically regarding alert tuning and user account restrictions.

What Are Recent G2 Reviews of Check Point Exposure Management?

What Are G2 Users Discussing About Check Point Exposure Management?

Falcon Security and IT operations

CrowdStrike Falcon for IT is a comprehensive IT operations and security solution that combines powerful endpoint management capabilities with enterprise-grade security protection. By unifying IT operations and security functions on a single platform, Falcon for IT enables organizations to streamline device management, automate software deployment, ensure compliance, and maintain robust security across their entire endpoint ecosystem. The solution leverages CrowdStrike's cloud-native architecture to provide real-time visibility, control, and protection for all managed devices, whether on-premises or remote. Designed for modern IT teams, Falcon for IT simplifies daily operations through automated patch management, application inventory, USB device control, and system performance monitoring. The platform's intuitive interface and automated workflows help IT professionals efficiently manage their endpoint environment while maintaining security best practices and reducing operational overhead. Whether managing software updates, deploying applications, or responding to IT incidents, Falcon for IT serves as a unified solution that empowers IT teams to maintain operational excellence while ensuring enterprise-grade security protection across their organization.

Average Rating: 4.6/5.0

Total Reviews: 22

How Do G2 Users Rate Falcon Security and IT operations?

  • Vulnerability Intelligence: 9.2/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.6/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.9/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.2/10 (Category avg: 9.0/10)

Who Is the Company Behind Falcon Security and IT operations?

  • Seller: CrowdStrike
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • Twitter: @CrowdStrike
    110,809 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®
  • Ownership: NASDAQ: CRWD

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 45% Medium, 41% Large

What Do G2 Reviewers Say About Falcon Security and IT operations?

AI-generated summary from verified user reviews

Pros
  • Users find Falcon Security and IT operations to be easy to use, facilitating seamless monitoring and implementation.
  • Users value the easy integrations of Falcon Security, enhancing operational efficiency and simplifying security management across platforms.
  • Users highlight the easy setup of Falcon, streamlining integration and enhancing security operations efficiently.
  • Users appreciate the high-level security provided by Falcon Security, enhancing protection against breaches and simplifying operations.
  • Users value the comprehensive security insights and ease of use provided by Falcon Security and IT Operations.
Cons
  • Users find the cost and complexity of Falcon Security and IT operations a significant barrier for adoption.
  • Users find false positives challenging, complicating investigations and prolonging search times for potential threats.
  • Users experience slow loading times when searching for non-malicious activities, making investigations inefficient.
  • Users experience slow performance with Falcon Security, with long search times hampering investigative processes.
  • Users report bugs in processing and installation that hinder the overall functionality and experience of Falcon Security.

What Are Recent G2 Reviews of Falcon Security and IT operations?

Tenable Nessus

Built for security practitioners, by security professionals, Nessus products by Tenable are the de-facto industry standard for vulnerability assessment. Nessus performs point-in-time assessments to help security professionals quickly and easily identify and fix vulnerabilities, including software flaws, missing patches, malware, and misconfigurations - across a variety of operating systems, devices, and applications. With features such as pre-built policies and templates, customizable reporting, group “snooze” functionality, and real-time updates, Nessus is designed to make vulnerability assessment simple, easy, and intuitive. The result: less time and effort to assess, prioritize, and remediate issues.

Average Rating: 4.5/5.0

Total Reviews: 299

How Do G2 Users Rate Tenable Nessus?

  • Vulnerability Intelligence: 10.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.2/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.6/10 (Category avg: 8.7/10)
  • Ease of Admin: 8.9/10 (Category avg: 9.0/10)

Who Is the Company Behind Tenable Nessus?

  • Seller: Tenable
  • Company Website:
  • HQ Location: Columbia, MD
  • Twitter: @TenableSecurity
    87,752 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,361 employees on LinkedIn®
  • Ownership: NASDAQ: TENB

Who Uses This Product?

  • Who Uses This: Security Engineer, Network Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Medium, 33% Large

What Do G2 Reviewers Say About Tenable Nessus?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the extensive vulnerability identification capabilities of Tenable Nessus, enhancing their security risk management efforts.
  • Users value the comprehensive vulnerability detection in Tenable Nessus, enhancing their ability to manage security risks effectively.
  • Users praise the automated scanning of Tenable Nessus for its thoroughness and comprehensive vulnerability reporting.
  • Users value the ease of use of Tenable Nessus, appreciating its simple setup and user-friendly interface.
  • Users value the extensive reporting and automation capabilities of Tenable Nessus for better asset scanning.
Cons
  • Users note that slow scanning can take 2-3 days and may disrupt production environments due to high resource usage.
  • Users highlight the high costs of maintaining Tenable Nessus, which can be a barrier for many organizations.
  • Users find the limited features of Tenable Nessus restrictive, especially regarding host capacity and mobile app testing.
  • Users find the complexity of licensing and features in Tenable Nessus challenging, impacting overall usability and resource management.
  • Users report that false positives from Nessus can create additional workload and complicate vulnerability management processes.

What Are Recent G2 Reviews of Tenable Nessus?

What Are G2 Users Discussing About Tenable Nessus?

Intruder

Intruder's continuous exposure management platform helps security, IT, and engineering teams stop breaches before they start. By unifying AI penetration testing, attack surface monitoring, cloud security, and vulnerability management in one intuitive platform, Intruder gives stretched teams an always-on security source of truth. Our approach focuses on continuous automated scanning using expertise and agentic solutions to ensure that the findings we deliver are accurate, prioritized by real-world risk, and ready to act on. Founded in 2015 by Chris Wallis, a former ethical hacker turned corporate blue teamer, Intruder is now protecting over 3,000 companies worldwide. Intruder has been awarded multiple accolades, was selected for GCHQ’s Cyber Accelerator, included on Deloitte’s Tech Fast 50 2023 list as the fastest-growing cybersecurity company in the UK and was named in G2’s 2026 Best Software Awards.

Average Rating: 4.8/5.0

Total Reviews: 219

How Do G2 Users Rate Intruder?

  • Vulnerability Intelligence: 9.6/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.7/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.3/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.5/10 (Category avg: 9.0/10)

Who Is the Company Behind Intruder?

  • Seller: Intruder
  • Company Website:
  • Year Founded: 2015
  • HQ Location: London
  • Twitter: @intruder_io
    979 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    81 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, Director
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 56% Small, 37% Medium

What Do G2 Reviewers Say About Intruder?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Intruder, with quick setup and intuitive system design enhancing their experience.
  • Users value the clarity and prioritization of Intruder's findings, enabling effective risk management and actionable insights.
  • Users value the quick and efficient customer support from Intruder, enhancing their overall scanning experience.
  • Users appreciate the intuitive interface of Intruder, finding it easy to set up and navigate.
  • Users value the efficient vulnerability identification from Intruder, enhancing their cybersecurity management effortlessly.
Cons
  • Users find the product expensive due to high costs for add-ons and fees per endpoint scanned.
  • Users find the slow scanning process frustrating, leading to inefficiencies and missed vulnerabilities during security assessments.
  • Users find licensing issues challenging, particularly regarding costs and constraints that affect system configurations.
  • Users experience false positives which can obscure the detection of critical vulnerabilities in security monitoring.
  • Users find the limited features of Intruder less accommodating for specific reporting and customization needs.

What Are Recent G2 Reviews of Intruder?

What Are G2 Users Discussing About Intruder?

SentinelOne Singularity Cloud Security

Singularity Cloud Security is SentinelOne’s comprehensive, cloud-native application protection platform (CNAPP). It combines the best of agentless insights with AI-powered threat protection, to secure and protect your multi-cloud infrastructure, services, and containers from build time to runtime. SentinelOne’s CNAPP applies an attacker’s mindset to help security practitioners better prioritize their remediation tasks with evidence-backed Verified Exploit Paths™. The efficient and scalable runtime protection, proven over 5 years and trusted by many of the world’s leading cloud enterprises, harnesses local, autonomous AI engines to detect and thwart runtime threats in real-time. CNAPP data and workload telemetry is recorded to SentinelOne’s unified security lake, for easy access and investigation.

Average Rating: 4.9/5.0

Total Reviews: 122

How Do G2 Users Rate SentinelOne Singularity Cloud Security?

  • Vulnerability Intelligence: 9.7/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.9/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.8/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.7/10 (Category avg: 9.0/10)

Who Is the Company Behind SentinelOne Singularity Cloud Security?

  • Seller: SentinelOne
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • Twitter: @SentinelOne
    57,863 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,529 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 59% Medium, 30% Large

What Do G2 Reviewers Say About SentinelOne Singularity Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the real-time threat alerts of SentinelOne Singularity Cloud Security, enhancing proactive protection against vulnerabilities.
  • Users appreciate the intuitive and user-friendly interface of SentinelOne Singularity, enhancing security management for everyone.
  • Users value the automated vulnerability detection of PingSafe, enabling proactive security and swift threat identification.
  • Users praise PingSafe for its comprehensive cloud security solutions that enhance threat detection and proactive risk management.
  • Users value the strong visibility and protection offered by SentinelOne Singularity Cloud Security, enhancing their operational efficiency.
Cons
  • Users note the complexity of configuring SentinelOne Singularity Cloud Security, requiring time and experience for effective use.
  • Users find that ineffective alerts require tuning, complicating setup and alignment with organizational workflows.
  • Users find the complex setup of SentinelOne Singularity Cloud Security can be time-consuming and challenging to navigate.
  • Users find the difficult configuration of SentinelOne Singularity Cloud Security can complicate setup and usage experience.
  • Users feel the UI of SentinelOne Singularity is clunky, making the platform harder to navigate and set up.

What Are Recent G2 Reviews of SentinelOne Singularity Cloud Security?

Darktrace / HYBRID NETWORK

Darktrace / HYBRID NETWORK uses Adaptive AI to continuously learn behavior across your infrastructure, combining NDR, CDR, OT security, ITDR, exposure management, attack path modelling and forensic investigations into a single solution. - Unify visibility - Detect and contain known, novel and insider threats - AI-led triage and investigations - Increase resilience Named a Leader in the 2025 and 2026 Gartner® Magic Quadrant™ for NDR and the only Visionary in the 2025 Gartner® Magic Quadrant™ for CPS.

Average Rating: 4.4/5.0

Total Reviews: 47

How Do G2 Users Rate Darktrace / HYBRID NETWORK?

  • Ease of Admin: 7.7/10 (Category avg: 9.0/10)

Who Is the Company Behind Darktrace / HYBRID NETWORK?

  • Seller: Darktrace
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Cambridgeshire, England
  • Twitter: @Darktrace
    18,177 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,597 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 63% Medium, 31% Large

What Do G2 Reviewers Say About Darktrace / HYBRID NETWORK?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the excellent monitoring capabilities of Darktrace, offering impressive visibility and efficient network analysis.
  • Users appreciate the self-learning AI technology of Darktrace/Network, effectively adapting to threats without extensive configuration.
  • Users commend Darktrace's rapid threat detection, ensuring robust security with minimal manual intervention for maximum efficiency.
  • Users commend the responsive customer support of Darktrace/Network, enhancing learning and facilitating efficient troubleshooting.
  • Users highlight the autonomous AI-driven cybersecurity of Darktrace, which effectively detects and responds to threats in real time.
Cons
  • Users report a significant learning curve with Darktrace as the AI generates numerous alerts during initial setup.
  • Users note that the product can be expensive, particularly for smaller organizations with constrained budgets and significant training costs.
  • Users experience alert issues with Darktrace, needing extensive manual tuning to manage false positives during the learning phase.
  • Users find the complex setup of Darktrace challenging, requiring skilled teams for effective management and configuration.
  • Users experience false positives occasionally, requiring IT support to resolve issues affecting network connectivity.

What Are Recent G2 Reviews of Darktrace / HYBRID NETWORK?

What Are G2 Users Discussing About Darktrace / HYBRID NETWORK?

Bitsight

Bitsight is the global leader in cyber risk intelligence, leveraging advanced AI to empower organizations with precise insights derived from the industry’s most extensive external cybersecurity dataset. With more than 3,500 customers and over 68,000 organizations active on its platform, Bitsight delivers real-time visibility into cyber risk and threat exposure, enabling teams to rapidly identify vulnerabilities, detect emerging threats, prioritize remediation, and mitigate risks across their extended attack surface. Bitsight proactively uncovers security gaps across infrastructure, cloud environments, digital identities, and third- and fourth-party ecosystems. From security operations and governance teams to executive boardrooms, Bitsight provides the unified intelligence backbone required to confidently manage cyber risk and address exposures before they impact performance.

Average Rating: 4.5/5.0

Total Reviews: 76

How Do G2 Users Rate Bitsight?

  • Vulnerability Intelligence: 8.3/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.8/10 (Category avg: 8.7/10)
  • Ease of Admin: 8.8/10 (Category avg: 9.0/10)

Who Is the Company Behind Bitsight?

  • Seller: Bitsight
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Boston, MA
  • Twitter: @BitSight
    4,503 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    694 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Hospital & Health Care
  • Company Size: 71% Large, 24% Medium

What Do G2 Reviewers Say About Bitsight?

AI-generated summary from verified user reviews

Pros
  • Users value the comprehensive security posture that Bitsight provides for both their organization and suppliers.
  • Users value Bitsight for its comprehensive risk assessment, enabling effective management of cyber risks and third-party suppliers.
  • Users appreciate the intuitive interface of Bitsight, finding it user-friendly and easy to navigate for daily tasks.
  • Users value the intuitive interface and comprehensive insights provided by Bitsight, enhancing security management efficiency.
  • Users commend Bitsight's fantastic customer support, recognizing their knowledge, responsiveness, and intuitive assistance.
Cons
  • Users express frustration over the missing features in Bitsight, particularly regarding questionnaire management and transparency in scoring.
  • Users express concerns about the lack of clarity in Bitsight's findings and scoring methodology, affecting overall trust.
  • Users experience poor customer support and inadequate documentation, hindering effective use of the Bitsight platform.
  • Users face poor notifications from BitSight, with alerts often delayed and historical breaches not reflecting current vulnerabilities.
  • Users experience slow loading times and timeouts that hinder workflow and overall satisfaction with Bitsight.

What Are Recent G2 Reviews of Bitsight?

What Are G2 Users Discussing About Bitsight?

Recorded Future

Recorded Future is the world’s largest threat intelligence company. Recorded Future’s Intelligence Cloud provides end-to-end intelligence across adversaries, infrastructure, and targets. Indexing the internet across the open web, dark web, and technical sources, Recorded Future provides real-time visibility into an expanding attack surface and threat landscape, empowering clients to act with speed and confidence to reduce risk and securely drive business forward. Headquartered in Boston with offices and employees around the world, Recorded Future works with over 1,900 businesses and government organizations across 80 countries to provide real-time, unbiased and actionable intelligence. Learn more at recordedfuture.com.

Average Rating: 4.5/5.0

Total Reviews: 241

How Do G2 Users Rate Recorded Future?

  • Vulnerability Intelligence: 8.6/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 7.9/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 7.6/10 (Category avg: 8.7/10)
  • Ease of Admin: 8.5/10 (Category avg: 9.0/10)

Who Is the Company Behind Recorded Future?

  • Seller: Recorded Future
  • Company Website:
  • Year Founded: 2009
  • HQ Location: Somerville, US
  • Twitter: @RecordedFuture
    107,965 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,150 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Cyber Threat Intelligence Analyst, Threat Intelligence Analyst
  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 62% Large, 21% Medium

What Do G2 Reviewers Say About Recorded Future?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Recorded Future, finding the interface intuitive and features beneficial for daily tasks.
  • Users enjoy the advanced customization features of Recorded Future, providing in-depth insights and alerts for cyber threats.
  • Users value the intelligent insights from Recorded Future, enhancing their understanding of critical data relationships effectively.
  • Users value the effective threat detection capabilities of Recorded Future, enabling prompt response to potential security risks.
  • Users value the actionable threat intelligence from Recorded Future, enhancing their vulnerability management and overall security posture.
Cons
  • Users find the navigation complex in Recorded Future, leading to difficulties in creating accurate queries and managing data.
  • Users often mention the high cost of Recorded Future, which can be challenging for teams with tight budgets.
  • Users find the learning curve steep, requiring significant time and effort to master the platform's features.
  • Users find difficult learning curves due to complexity and advanced settings, hindering team accessibility and efficiency.
  • Users express concern over inaccuracy issues in Recorded Future, affecting predictions and relevant alerts significantly.

What Are Recent G2 Reviews of Recorded Future?

What Are G2 Users Discussing About Recorded Future?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated April 10, 2026