Top Free Attack Surface Management Software

How Many Attack Surface Management Software Products Does G2 Track?

Total Products under this Category: 188

Category Stats (Sep 2026)

  • Average Rating: 4.6/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: ReliaQuest GreyMatter (+1.61%) - Among all products in this category, ReliaQuest GreyMatter recorded the largest rating increase compared to last month

Last updated: September 01, 2026

How Does G2 Rank Attack Surface Management Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,800+ Authentic Reviews
  • 188+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

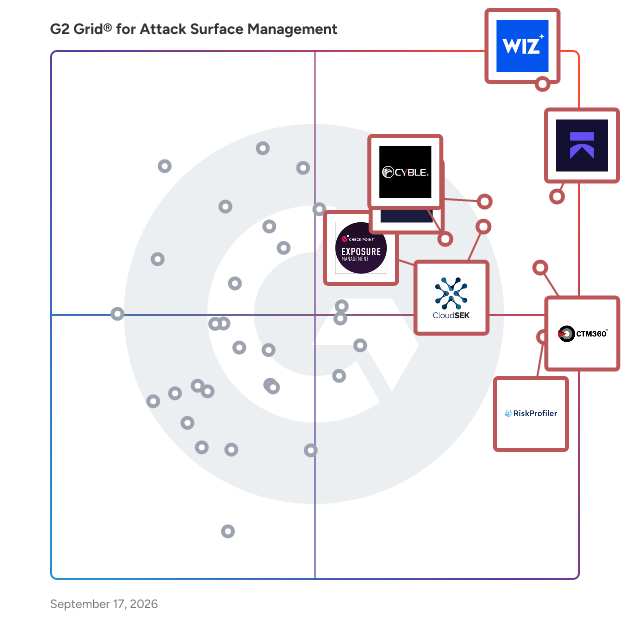
G2 Grid® for Attack Surface Management Software

G2 Grid® for  Attack Surface Management Software plotting products by satisfaction and market presence

Highlighted products: Wiz, Aikido Security, SOCRadar Extended Threat Intelligence, CTM360, CloudSEK, Cyble, RiskProfiler - External Threat Exposure Management, and Check Point Exposure Management.

Underlying data: [Grid® JSON](https://www.g2.com/categories/attack-surface-management/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=aikido-security&focus%5B%5D=socradar-extended-threat-intelligence&focus%5B%5D=ctm360-ctm360&focus%5B%5D=cloudsek&focus%5B%5D=cyble&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=check-point-exposure-management)

Wiz

Wiz transforms cloud security for customers – including more than 50% of the Fortune 100 – by enabling a new operating model. With Wiz, organizations can democratize security across the development lifecycle, empowering them to build fast and securely. Its Cloud Native Application Protection Platform (CNAPP) consolidates CSPM, KSPM, CWPP, Vulnerability management, IaC scanning, CIEM, DSPM into a single platform. Wiz drives visibility, risk prioritization, and business agility. Protecting Your Cloud Environments Requires a Unified, Cloud Native Platform. Wiz connects to every cloud environment, scans every layer, and covers every aspect of your cloud security - including elements that normally require installing agents. Its comprehensive approach has all of these cloud security solutions built in. Hundreds of organizations worldwide, including 50 percent of the Fortune 100, to rapidly identify and remove critical risks in cloud environments. Its customers include Salesforce, Slack, Mars, BMW, Avery Dennison, Priceline, Cushman & Wakefield, DocuSign, Plaid, and Agoda, among others. Wiz is backed by Sequoia, Index Ventures, Insight Partners, Salesforce, Blackstone, Advent, Greenoaks, Lightspeed and Aglaé. Visit https://www.wiz.io for more information.

Average Rating: 4.7/5.0

Total Reviews: 841

How Do G2 Users Rate Wiz?

  • Vulnerability Intelligence: 9.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.8/10 (Category avg: 8.6/10)
  • Ease of Admin: 9.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Wiz?

  • Seller: Wiz
  • Company Website:
  • Year Founded: 2020
  • HQ Location: New York, US
  • Twitter: @wiz_io
    24,733 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,147 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CISO, Security Engineer
  • Top Industries: Financial Services, Computer Software
  • Company Size: 53% Large, 39% Medium

What Do G2 Reviewers Say About Wiz?

AI-generated summary from verified user reviews

Pros
  • Users value the robust APIs and user-friendly UI, appreciating ongoing improvements and a wealth of insightful issues.
  • Users value the continuous enhancement of security features by Wiz, appreciating the support and innovation in their tool.
  • Users appreciate the ease of use of Wiz, benefiting from its user-friendly interface and seamless integration.
  • Users value the comprehensive visibility Wiz provides, enhancing security and prioritizing essential aspects of their cloud environment.
  • Users appreciate the easy setup of Wiz, enabling a quick and seamless integration into their workflows.
Cons
  • Users find a significant learning curve in mastering Wiz's extensive features, which can hinder initial usage.
  • Users find the feature limitations of Wiz frustrating, especially with complex management and reporting challenges.
  • Users note that improvement is needed for laggy query responses and better dashboard reporting capabilities.
  • Users identify improvements needed in dashboard reporting and feature streamlining for better usability and budgeting.
  • Users find the interface overwhelming initially, facing a steep learning curve and complex licensing issues.

What Are Recent G2 Reviews of Wiz?

Aikido Security

Aikido Security is the developer-first security platform that unifies code, cloud, protection, and attack testing in one suite of best-in-class products. Built by developers for developers, Aikido helps teams of any size ship secure software faster, automate protection, and simulate real-world attacks with AI-driven precision. The platform’s proprietary AI cuts noise by 95%, delivers one-click fixes, and saves developers 10+ hours per week. Aikido Intel proactively uncovers vulnerabilities in open source packages before disclosure, helping secure more than 50,000 organizations worldwide, including Revolut, Niantic, Visma, Montblanc, and GoCardless.

Average Rating: 4.6/5.0

Total Reviews: 263

How Do G2 Users Rate Aikido Security?

  • Ease of Admin: 9.4/10 (Category avg: 9.0/10)

Who Is the Company Behind Aikido Security?

  • Seller: Aikido Security
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Ghent, Belgium
  • Twitter: @AikidoSecurity
    11,770 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    320 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Founder, CTO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 79% Small, 14% Medium

What Do G2 Reviewers Say About Aikido Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Aikido Security, thanks to its clear insights and seamless integration.
  • Users appreciate Aikido Security's robust security capabilities, providing a comprehensive and seamless integration in their workflow.
  • Users value the intuitive dashboard of Aikido Security, which simplifies security issue identification and management.
  • Users value the easy integrations of Aikido Security, enhancing workflows with seamless connections to existing GitLab repositories.
  • Users find Aikido's easy setup highly efficient, enabling quick implementation and immediate usability for security assessments.
Cons
  • Users note the lack of advanced features in Aikido Security, such as dark mode and in-depth analysis options.
  • Users find the pricing structure expensive for micro businesses, making upgrades difficult to justify.
  • Users note the limited features of Aikido Security, wishing for more customization and advanced options.
  • Users find the pricing issues challenging, especially for micro businesses, due to the steep upgrade costs.
  • Users feel Aikido Security is lacking features like advanced reporting and deeper compliance analysis compared to competitors.

What Are Recent G2 Reviews of Aikido Security?

SOCRadar Extended Threat Intelligence

Since 2019, SOCRadar has been a pioneer in SaaS cybersecurity, now serving over 900 customers across 75 countries. Our mission is to provide accessible, proactive threat intelligence. Today, SOCRadar empowers security teams with our groundbreaking Extended Threat Intelligence (XTI) platform and is leading the charge toward the future with Agentic Threat Intelligence (ATI). What does SOCRadar do? At its core, SOCRadar provides a unified, cloud-hosted platform designed to enrich your cyber threat intelligence by contextualizing it with data from your attack surface, digital footprint, dark web exposure, and supply chain. We help security teams see what attackers see by combining External Attack Surface Management, Cyber Threat Intelligence, and Digital Risk Protection into a single, easy-to-use solution. This enables your organization to discover hidden vulnerabilities, detect data leaks, and shut down threats like phishing and brand impersonation before they can harm your business. By combining these critical security functions, SOCRadar replaces the need for separate, disconnected tools. Our holistic approach offers a streamlined, modular experience, providing a complete, real-time view of your threat landscape to help you stay ahead of attackers. Our vision for Agentic Threat Intelligence (ATI) goes beyond today's chatbots and LLMs. We are focused on making it practical for security teams to use AI agents to solve real-world problems. Our initiative will empower you to either deploy pre-built agents or easily create your own, leveraging deep integrations to automate complex tasks that were previously difficult to perform accurately. SOCRadar is dedicated to pioneering this change, making autonomous security an accessible reality for your team.

Average Rating: 4.7/5.0

Total Reviews: 118

How Do G2 Users Rate SOCRadar Extended Threat Intelligence?

  • Vulnerability Intelligence: 9.2/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.2/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.4/10 (Category avg: 8.6/10)
  • Ease of Admin: 9.2/10 (Category avg: 9.0/10)

Who Is the Company Behind SOCRadar Extended Threat Intelligence?

  • Seller: SOCRadar
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Delaware
  • Twitter: @socradar
    5,748 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    195 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 43% Medium, 41% Large

What Do G2 Reviewers Say About SOCRadar Extended Threat Intelligence?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of SOCRadar, enjoying its intuitive dashboards and centralized threat data management.
  • Users value the comprehensive Threat Intelligence features of SOCRadar, enabling effective risk awareness and proactive security measures.
  • Users value the comprehensive and actionable alert notifications from SOCRadar, enhancing their security monitoring and response efforts.
  • Users appreciate the exceptional visibility into external threats, benefiting from a centralized and proactive intelligence platform.
  • Users value the exceptional visibility SOCRadar provides into external threats, enhancing proactive security measures significantly.
Cons
  • Users are frustrated by the inefficient alerts, leading to noise and fatigue from duplicate notifications and false positives.
  • Users report that the inefficient alert system leads to alert fatigue and necessitates extensive tuning for effectiveness.
  • Users struggle with false positives and duplicate notifications, leading to alert fatigue and a need for extensive tuning.
  • Users note the limited features in SOCRadar Extended Threat Intelligence, hindering deeper analysis without upgrading.
  • Users find the insufficient information from SOCRadar Extended Threat Intelligence to hinder effective decision-making.

What Are Recent G2 Reviews of SOCRadar Extended Threat Intelligence?

CTM360

CTM360 is a consolidated external security platform that integrates External Attack Surface Management, Digital Risk Protection, Cyber Threat Intelligence, Brand Protection & Anti-phishing, Surface, Deep, & Dark Web Monitoring, Security Ratings, Third-party risk Management, and fully managed unlimited Takedowns. As a pioneer and innovator in preemptive security, CTM360 operates as an external CTEM technology platform outside an organization’s perimeter. Seamless and turn-key, CTM360 requires no configurations, installations or inputs from the end-user, with all data pre-populated and specific to your organization. All aspects are managed by CTM360.

Average Rating: 4.6/5.0

Total Reviews: 173

How Do G2 Users Rate CTM360?

  • Vulnerability Intelligence: 9.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.1/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.8/10 (Category avg: 8.6/10)
  • Ease of Admin: 9.7/10 (Category avg: 9.0/10)

Who Is the Company Behind CTM360?

  • Seller: CTM360
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Manama, BH
  • Twitter: @teamCTM360
    999 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    136 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Banking, Financial Services
  • Company Size: 37% Large, 37% Medium

What Do G2 Reviewers Say About CTM360?

AI-generated summary from verified user reviews

Pros
  • Users commend the top-notch customer support of CTM360, highlighting responsive and knowledgeable assistance at every level.
  • Users commend the ease of use of CTM360, appreciating its straightforward setup and user-friendly interface.
  • Users admire the comprehensive platform of CTM360, which effectively enhances proactive cybersecurity and incident response.
  • Users commend the effective monitoring capabilities of CTM360, aiding quick identification of risks and enhancing security posture.
  • Users praise the high detection efficiency of CTM360, appreciating its accuracy and proactive risk management capabilities.
Cons
  • Users note the limited features of CTM360, particularly on the Android app compared to the web portal.
  • Users are frustrated by the integration issues with existing security infrastructures, seeking better compatibility and usability.
  • Users note a lack of features in CTM360, particularly compared to the web portal and community edition limitations.
  • Users face a lack of integration with existing security systems, limiting automated data feeds and user experience.
  • Users find the lack of integrations with existing security tools limits automated daily security feeds and functionality.

What Are Recent G2 Reviews of CTM360?

CloudSEK

CloudSEK is a contextual AI company that predicts Cyber Threats. We combine the power of Cyber Crime monitoring, Brand Monitoring, Attack Surface monitoring, and Supply Chain intelligence to give context to our customers’ digital risks.

Average Rating: 4.8/5.0

Total Reviews: 137

How Do G2 Users Rate CloudSEK?

  • Vulnerability Intelligence: 9.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.6/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.4/10 (Category avg: 8.6/10)
  • Ease of Admin: 9.6/10 (Category avg: 9.0/10)

Who Is the Company Behind CloudSEK?

  • Seller: CloudSEK
  • Year Founded: 2015
  • HQ Location: Singapore, SG
  • Twitter: @cloudsek
    2,417 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    247 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Analyst, Analyst
  • Top Industries: Financial Services, Airlines/Aviation
  • Company Size: 53% Large, 31% Medium

What Do G2 Reviewers Say About CloudSEK?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of CloudSEK, noting its smooth functions and intuitive dashboard for seamless monitoring.
  • Users value the continuous monitoring and real-time alerts provided by CloudSEK for effective brand oversight.
  • Users praise the responsive customer support of CloudSEK, which effectively resolves issues quickly and efficiently.
  • Users praise CloudSEK's excellent coverage and AI-driven threat intelligence, enhancing cybersecurity and providing invaluable insights.
  • Users value the real-time visibility into external threats offered by CloudSEK, enhancing proactive risk management.
Cons
  • Users are frustrated by the high rate of false positives in alerts for credential breaches and domain impersonation.
  • Users experience inefficient alerts from CloudSEK, often overwhelming them with false positives and complicating threat prioritization.
  • Users experience dashboard issues with false positives, cluttered layouts, and a need for further customization and basic features.
  • Users experience inefficient alert systems, struggling with false positives and difficulty in managing genuine threats effectively.
  • Users find the complex UI of CloudSEK overwhelming, making it challenging to interpret key information effectively.

What Are Recent G2 Reviews of CloudSEK?

Cyble

Cyble is an AI-native cybersecurity solution designed to help organizations enhance their digital security posture through real-time intelligence, detection, and response capabilities. By leveraging advanced agentic AI and processing vast amounts of data, Cyble empowers businesses to navigate the complexities of the cyber threat landscape effectively. Its unique approach involves collecting and enriching signals from various sources, including the dark web, deep web, and surface web, providing unparalleled visibility into emerging threats and adversarial activities. Targeting a wide range of industries, Cyble's platform is particularly beneficial for security teams, risk management professionals, and organizations that prioritize safeguarding their digital assets. The comprehensive suite of solutions offered by Cyble includes Threat Intelligence, Dark Web & Deep Web Monitoring, Attack Surface Management (ASM), and Brand Intelligence, among others. These tools are designed to address specific use cases such as identifying vulnerabilities, monitoring brand reputation, and managing third-party risks, making it an essential resource for organizations aiming to bolster their cybersecurity measures. Cyble's key features are centered around its unified platform, which integrates multiple cybersecurity functions into a single interface. This integration allows for seamless communication between different security components, enabling teams to anticipate, identify, and neutralize threats with remarkable speed and precision. For instance, the Digital Forensics & Incident Response (DFIR) capabilities equip organizations with the tools needed to investigate and respond to incidents effectively, while the DDoS Protection and Cloud Security Posture Management (CSPM) features ensure that businesses can maintain operational integrity even under attack. Moreover, Cyble stands out in its category by combining vast data intelligence with cutting-edge AI automation. This proactive defense strategy not only helps organizations react to cyber threats but also empowers them to stay ahead of potential risks. By enhancing visibility into the threat landscape and providing actionable insights, Cyble enables enterprises to protect their assets, safeguard brand trust, and operate with confidence in an increasingly complex digital environment. The result is a robust cybersecurity framework that supports organizations in navigating the ever-evolving challenges of the cyber world.

Average Rating: 4.8/5.0

Total Reviews: 147

How Do G2 Users Rate Cyble?

  • Vulnerability Intelligence: 9.5/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.5/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.1/10 (Category avg: 8.6/10)
  • Ease of Admin: 9.6/10 (Category avg: 9.0/10)

Who Is the Company Behind Cyble?

  • Seller: Cyble
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Alpharetta, US
  • Twitter: @cybleglobal
    16,252 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    233 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 39% Large, 17% Medium

What Do G2 Reviewers Say About Cyble?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the intuitive dashboard and user-friendly UI of Cyble, enhancing their overall experience with the platform.
  • Users value Cyble for its comprehensive threat intelligence, ensuring quick responses and seamless integrations within their security operations.
  • Users value Cyble's state-of-the-art tools for threat hunting, seamlessly combining protection and monitoring in one solution.
  • Users value the real-time insights and ease of use of Cyble for effective cybersecurity management.
  • Users appreciate the real-time threat detection of Cyble, greatly enhancing their digital risk protection and response capabilities.
Cons
  • Users report inefficient alerts with Cyble, experiencing duplicate notifications and unreliable delivery leading to alert fatigue.
  • Users are frustrated with the limited customization options in Cyble, impacting their efficiency and dashboard usability.
  • Users find the poor customer support of Cyble lacking in staff and effective timezone assistance.
  • Users experience poor support management, often facing slow responses that hinder timely resolution of urgent issues.
  • Users experience significant false positives in alerts from Cyble, leading to confusion and inefficient threat management.

What Are Recent G2 Reviews of Cyble?

RiskProfiler - External Threat Exposure Management

RiskProfiler is an advanced cybersecurity platform purpose-built for Continuous Threat Exposure Management (CTEM). It unifies external, cloud, vendor, and brand risk intelligence into a single ecosystem—providing organizations with real-time visibility, contextual threat insights, and actionable remediation guidance. Through its integrated suite, External Attack Surface Managemnet, Third_party Risk Management, Cloud Attack Surface Management, and Brand Risk Protection; the platform continuously discovers, classifies, and evaluates external-facing assets and risks across the internet, multi-cloud environments, and third-party ecosystems. Powered by AI-enabled risk questionnaires, RiskProfiler automates the exchange, validation, and scoring of security assessments, dramatically accelerating third-party due diligence and compliance validation. The platform’s context-enriched graph engine correlates vulnerabilities, exposures, and configurations with real-world threat data, revealing how attackers might exploit an organization’s digital footprint. Its newly enhanced Cyber Threat Intelligence (CTI) module provides live insights into industry-specific attack trends, threat actor profiles, and evolving TTPs, directly embedded within the dashboard. By analyzing CVEs, IOCs, and exploit patterns, it maps these to relevant assets and potential attack paths, enabling focused, prioritized mitigation. From identifying exposed cloud resources across AWS, Azure, and Google Cloud to uncovering brand impersonation, phishing campaigns, or logo abuse, RiskProfiler delivers unified visibility and continuous monitoring that extends beyond the perimeter. It helps organizations anticipate, contextualize, and neutralize threats before they turn into breaches, transforming exposure management into a truly intelligent, predictive defense capability.

Average Rating: 5.0/5.0

Total Reviews: 135

How Do G2 Users Rate RiskProfiler - External Threat Exposure Management?

  • Vulnerability Intelligence: 10.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.9/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.9/10 (Category avg: 8.6/10)
  • Ease of Admin: 9.7/10 (Category avg: 9.0/10)

Who Is the Company Behind RiskProfiler - External Threat Exposure Management?

  • Seller: Riskprofiler
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Rock Hill , US
  • Twitter: @riskprofilerio
    209 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    35 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Security Consultant
  • Top Industries: Information Technology and Services, Design
  • Company Size: 65% Medium, 30% Small

What Do G2 Reviewers Say About RiskProfiler - External Threat Exposure Management?

AI-generated summary from verified user reviews

Pros
  • Users value the multi-dimensional threat intelligence of RiskProfiler, enabling efficient management of external threats and vendor risks.
  • Users value the seamless integration features of RiskProfiler, enhancing real-time monitoring and adaptability in their workflows.
  • Users praise the fast and efficient customer support of RiskProfiler, enhancing their overall experience and threat management.
  • Users value the ease of use of RiskProfiler, as it seamlessly integrates and enhances external threat management.
  • Users highlight the easy setup of RiskProfiler, facilitating quick implementation and seamless integration for effective threat management.
Cons
  • Users face a steep learning curve with RiskProfiler, needing sufficient time for training and customization.
  • Users find the complexity of RiskProfiler challenging, requiring time for training and adjustment to navigate effectively.
  • Users find the difficult learning curve challenging, requiring significant time and training for effective platform use.
  • Users find a steep learning curve with RiskProfiler, requiring time and training for effective use.
  • Users find the complex setup of RiskProfiler challenging, hindering smooth adoption and integration for non-specialist teams.

What Are Recent G2 Reviews of RiskProfiler - External Threat Exposure Management?

Tenable Nessus

Built for security practitioners, by security professionals, Nessus products by Tenable are the de-facto industry standard for vulnerability assessment. Nessus performs point-in-time assessments to help security professionals quickly and easily identify and fix vulnerabilities, including software flaws, missing patches, malware, and misconfigurations - across a variety of operating systems, devices, and applications. With features such as pre-built policies and templates, customizable reporting, group “snooze” functionality, and real-time updates, Nessus is designed to make vulnerability assessment simple, easy, and intuitive. The result: less time and effort to assess, prioritize, and remediate issues.

Average Rating: 4.5/5.0

Total Reviews: 295

How Do G2 Users Rate Tenable Nessus?

  • Vulnerability Intelligence: 10.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.2/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.6/10 (Category avg: 8.6/10)
  • Ease of Admin: 8.9/10 (Category avg: 9.0/10)

Who Is the Company Behind Tenable Nessus?

  • Seller: Tenable
  • Company Website:
  • HQ Location: Columbia, MD
  • Twitter: @TenableSecurity
    87,752 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,361 employees on LinkedIn®
  • Ownership: NASDAQ: TENB

Who Uses This Product?

  • Who Uses This: Security Engineer, Network Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Medium, 33% Large

What Do G2 Reviewers Say About Tenable Nessus?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the extensive vulnerability identification capabilities of Tenable Nessus, enhancing their security risk management efforts.
  • Users value the comprehensive vulnerability detection in Tenable Nessus, enhancing their ability to manage security risks effectively.
  • Users praise the automated scanning of Tenable Nessus for its thoroughness and comprehensive vulnerability reporting.
  • Users value the ease of use of Tenable Nessus, appreciating its simple setup and user-friendly interface.
  • Users value the extensive reporting and automation capabilities of Tenable Nessus for better asset scanning.
Cons
  • Users note that slow scanning can take 2-3 days and may disrupt production environments due to high resource usage.
  • Users highlight the high costs of maintaining Tenable Nessus, which can be a barrier for many organizations.
  • Users find the limited features of Tenable Nessus restrictive, especially regarding host capacity and mobile app testing.
  • Users find the complexity of licensing and features in Tenable Nessus challenging, impacting overall usability and resource management.
  • Users report that false positives from Nessus can create additional workload and complicate vulnerability management processes.

What Are Recent G2 Reviews of Tenable Nessus?

What Are G2 Users Discussing About Tenable Nessus?

SentinelOne Singularity Cloud Security

Singularity Cloud Security is SentinelOne’s comprehensive, cloud-native application protection platform (CNAPP). It combines the best of agentless insights with AI-powered threat protection, to secure and protect your multi-cloud infrastructure, services, and containers from build time to runtime. SentinelOne’s CNAPP applies an attacker’s mindset to help security practitioners better prioritize their remediation tasks with evidence-backed Verified Exploit Paths™. The efficient and scalable runtime protection, proven over 5 years and trusted by many of the world’s leading cloud enterprises, harnesses local, autonomous AI engines to detect and thwart runtime threats in real-time. CNAPP data and workload telemetry is recorded to SentinelOne’s unified security lake, for easy access and investigation.

Average Rating: 4.9/5.0

Total Reviews: 122

How Do G2 Users Rate SentinelOne Singularity Cloud Security?

  • Vulnerability Intelligence: 9.7/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.9/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.8/10 (Category avg: 8.6/10)
  • Ease of Admin: 9.7/10 (Category avg: 9.0/10)

Who Is the Company Behind SentinelOne Singularity Cloud Security?

  • Seller: SentinelOne
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • Twitter: @SentinelOne
    57,863 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    6,571 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 59% Medium, 30% Large

What Do G2 Reviewers Say About SentinelOne Singularity Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the real-time threat alerts of SentinelOne Singularity Cloud Security, enhancing proactive protection against vulnerabilities.
  • Users appreciate the intuitive and user-friendly interface of SentinelOne Singularity, enhancing security management for everyone.
  • Users value the automated vulnerability detection of PingSafe, enabling proactive security and swift threat identification.
  • Users praise PingSafe for its comprehensive cloud security solutions that enhance threat detection and proactive risk management.
  • Users value the strong visibility and protection offered by SentinelOne Singularity Cloud Security, enhancing their operational efficiency.
Cons
  • Users note the complexity of configuring SentinelOne Singularity Cloud Security, requiring time and experience for effective use.
  • Users find that ineffective alerts require tuning, complicating setup and alignment with organizational workflows.
  • Users find the complex setup of SentinelOne Singularity Cloud Security can be time-consuming and challenging to navigate.
  • Users find the difficult configuration of SentinelOne Singularity Cloud Security can complicate setup and usage experience.
  • Users feel the UI of SentinelOne Singularity is clunky, making the platform harder to navigate and set up.

What Are Recent G2 Reviews of SentinelOne Singularity Cloud Security?

Intruder

Intruder's continuous exposure management platform helps security, IT, and engineering teams stop breaches before they start. By unifying AI penetration testing, attack surface monitoring, cloud security, and vulnerability management in one intuitive platform, Intruder gives stretched teams an always-on security source of truth. Our approach focuses on continuous automated scanning using expertise and agentic solutions to ensure that the findings we deliver are accurate, prioritized by real-world risk, and ready to act on. Founded in 2015 by Chris Wallis, a former ethical hacker turned corporate blue teamer, Intruder is now protecting over 3,000 companies worldwide. Intruder has been awarded multiple accolades, was selected for GCHQ’s Cyber Accelerator, included on Deloitte’s Tech Fast 50 2023 list as the fastest-growing cybersecurity company in the UK and was named in G2’s 2026 Best Software Awards.

Average Rating: 4.8/5.0

Total Reviews: 219

How Do G2 Users Rate Intruder?

  • Vulnerability Intelligence: 9.6/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.7/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.3/10 (Category avg: 8.6/10)
  • Ease of Admin: 9.5/10 (Category avg: 9.0/10)

Who Is the Company Behind Intruder?

  • Seller: Intruder
  • Company Website:
  • Year Founded: 2015
  • HQ Location: London
  • Twitter: @intruder_io
    979 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    81 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, Director
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 56% Small, 37% Medium

What Do G2 Reviewers Say About Intruder?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Intruder, with quick setup and intuitive system design enhancing their experience.
  • Users value the clarity and prioritization of Intruder's findings, enabling effective risk management and actionable insights.
  • Users value the quick and efficient customer support from Intruder, enhancing their overall scanning experience.
  • Users appreciate the intuitive interface of Intruder, finding it easy to set up and navigate.
  • Users value the efficient vulnerability identification from Intruder, enhancing their cybersecurity management effortlessly.
Cons
  • Users find the product expensive due to high costs for add-ons and fees per endpoint scanned.
  • Users find the slow scanning process frustrating, leading to inefficiencies and missed vulnerabilities during security assessments.
  • Users find licensing issues challenging, particularly regarding costs and constraints that affect system configurations.
  • Users experience false positives which can obscure the detection of critical vulnerabilities in security monitoring.
  • Users find the limited features of Intruder less accommodating for specific reporting and customization needs.

What Are Recent G2 Reviews of Intruder?

What Are G2 Users Discussing About Intruder?

Bitsight

Bitsight is the global leader in cyber risk intelligence, leveraging advanced AI to empower organizations with precise insights derived from the industry’s most extensive external cybersecurity dataset. With more than 3,500 customers and over 68,000 organizations active on its platform, Bitsight delivers real-time visibility into cyber risk and threat exposure, enabling teams to rapidly identify vulnerabilities, detect emerging threats, prioritize remediation, and mitigate risks across their extended attack surface. Bitsight proactively uncovers security gaps across infrastructure, cloud environments, digital identities, and third- and fourth-party ecosystems. From security operations and governance teams to executive boardrooms, Bitsight provides the unified intelligence backbone required to confidently manage cyber risk and address exposures before they impact performance.

Average Rating: 4.5/5.0

Total Reviews: 76

How Do G2 Users Rate Bitsight?

  • Vulnerability Intelligence: 8.3/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.8/10 (Category avg: 8.6/10)
  • Ease of Admin: 8.8/10 (Category avg: 9.0/10)

Who Is the Company Behind Bitsight?

  • Seller: Bitsight
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Boston, MA
  • Twitter: @BitSight
    4,503 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    694 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Hospital & Health Care
  • Company Size: 71% Large, 24% Medium

What Do G2 Reviewers Say About Bitsight?

AI-generated summary from verified user reviews

Pros
  • Users value the comprehensive security posture that Bitsight provides for both their organization and suppliers.
  • Users value Bitsight for its comprehensive risk assessment, enabling effective management of cyber risks and third-party suppliers.
  • Users appreciate the intuitive interface of Bitsight, finding it user-friendly and easy to navigate for daily tasks.
  • Users value the intuitive interface and comprehensive insights provided by Bitsight, enhancing security management efficiency.
  • Users commend Bitsight's fantastic customer support, recognizing their knowledge, responsiveness, and intuitive assistance.
Cons
  • Users express frustration over the missing features in Bitsight, particularly regarding questionnaire management and transparency in scoring.
  • Users express concerns about the lack of clarity in Bitsight's findings and scoring methodology, affecting overall trust.
  • Users experience poor customer support and inadequate documentation, hindering effective use of the Bitsight platform.
  • Users face poor notifications from BitSight, with alerts often delayed and historical breaches not reflecting current vulnerabilities.
  • Users experience slow loading times and timeouts that hinder workflow and overall satisfaction with Bitsight.

What Are Recent G2 Reviews of Bitsight?

What Are G2 Users Discussing About Bitsight?

Halo Security

Halo Security is an External Attack Surface Management (EASM) platform that helps organizations discover, monitor, and secure their external digital footprint against cyber threats. The solution enables security teams to view their infrastructure from an attacker's perspective, providing continuous visibility into vulnerabilities, exposed assets, and potential security risks across web applications, cloud resources, and third-party services. Halo Security was founded in 2013 and is headquartered in the United States. With a team of experienced security professionals, the company has assisted thousands of organizations in strengthening their security posture. Their fully US-based operations have earned the trust of organizations across various industries seeking to protect their digital assets from evolving cyber threats. The platform combines automated discovery with expert analysis to deliver comprehensive attack surface monitoring, vulnerability detection, and technology identification. Key features include continuous asset discovery that automatically identifies unknown digital resources, real-time alerts for newly discovered vulnerabilities delivered via integrations with dozens of tools, technology fingerprinting to detect potential vulnerabilities in third-party services, and subdomain takeover protection that identifies dangerous DNS misconfigurations before attackers can exploit them. Halo Security empowers organizations to eliminate blind spots in their attack surface, prioritize remediation efforts based on real risk, and secure their external-facing assets against increasingly sophisticated cyber threats. The solution solves critical challenges for security teams by providing visibility into forgotten or unknown assets, detecting vulnerabilities in third-party platforms, and alerting teams to changes that introduce security risks. Whether managing a growing digital footprint or meeting compliance requirements, Halo Security provides the visibility and tools needed to maintain a strong security posture in today's complex threat landscape.

Average Rating: 4.5/5.0

Total Reviews: 56

How Do G2 Users Rate Halo Security?

  • Vulnerability Intelligence: 8.5/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.4/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.3/10 (Category avg: 8.6/10)
  • Ease of Admin: 8.4/10 (Category avg: 9.0/10)

Who Is the Company Behind Halo Security?

  • Seller: Halo Security
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Miami Beach, US
  • Twitter: @halohackers
    84 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    33 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Retail
  • Company Size: 54% Medium, 23% Large

What Do G2 Reviewers Say About Halo Security?

AI-generated summary from verified user reviews

Pros
  • Users praise the ease of use of Halo Security, noting its simplicity and seamless integration for effective protection.
  • Users value the easy integrations of Halo Security, seamlessly enhancing their security workflows and overall efficiency.
  • Users commend Halo Security for its comprehensive attack surface visibility and seamless integration, enhancing overall security management.
  • Users value the real-time notifications from Halo Security, enabling proactive management of potential security risks effectively.
  • Users highlight Halo Security's strong security capabilities, appreciating its seamless integration and actionable insights for robust protection.
Cons
  • Users find it difficult to navigate the Halo Security portal, leading to occasional frustration in locating functions.
  • Users find the complex UI challenging, especially with the organization and display of menus post-update.
  • Users find the complexity of the setup for multiple scan targets to be cumbersome and inefficient.
  • Users find the complex setup of Halo Security frustrating, noting it requires too many steps for multiple scan targets.
  • Users dislike the dashboard navigation issues in Halo Security, finding the new console cumbersome and uncomfortable to use.

What Are Recent G2 Reviews of Halo Security?

UpGuard Breach Risk

UpGuard Breach Risk is an AI-powered attack surface management solution that empowers lean security teams to see what attackers see and take control of their external risk. As part of the UpGuard Cyber Risk Posture Management (CRPM) platform, it integrates seamlessly with Vendor Risk and User Risk to provide a unified defense against modern cyber threats. As organizations scale, their digital footprint expands beyond the firewall, creating dangerous blind spots. Traditional tools often miss these external signals, leaving teams vulnerable to shadow IT, exposed credentials, and brand abuse. Breach Risk solves this by combining Attack Surface Management (ASM), Digital Risk Protection (DRP), and advanced Threat Monitoring into a single, automated platform. Key Capabilities: • Continuous Attack Surface Discovery: You can’t protect what you can’t see. Breach Risk continuously maps your internet-facing assets like domains, IPs, and cloud resources, to uncover shadow IT and misconfigurations. We automatically inventory your digital footprint to close the gaps that attackers exploit, ensuring no asset goes unmonitored. • AI-Powered Threat Monitoring: Move beyond static feeds. Our Threat Monitoring engine scans the open, deep, and dark web to detect leaked employee credentials, infostealer logs, and malware signals before they are weaponized. Unlike traditional threat intelligence that floods you with raw data, our AI Threat Analyst triages signals to filter out noise and prioritize high-fidelity threats for immediate action. • Brand Protection & Disinformation Defense: Safeguard your reputation against fraud. We proactively detect lookalike domains (typosquatting) and fraudulent social media profiles used to launch phishing attacks and disinformation campaigns. Our integrated workflows help you identify and neutralize these impersonation attempts before they erode customer trust. • Actionable Remediation: We don’t just find problems; we help you fix them. Breach Risk provides guided remediation plans and integrates with your security tech stack, allowing lean teams to accelerate response times without adding headcount. By translating complex technical risks into a quantifiable Cyber Risk Score, UpGuard enables security leaders to benchmark performance, justify budget, and prove risk reduction to the board.

Average Rating: 4.5/5.0

Total Reviews: 27

How Do G2 Users Rate UpGuard Breach Risk?

  • Vulnerability Intelligence: 10.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.7/10 (Category avg: 9.2/10)
  • Ease of Admin: 8.3/10 (Category avg: 9.0/10)

Who Is the Company Behind UpGuard Breach Risk?

  • Seller: UpGuard
  • Company Website:
  • Year Founded: 2012
  • HQ Location: Mountain View, California
  • Twitter: @UpGuard
    8,705 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    402 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 59% Large, 37% Medium

What Are Recent G2 Reviews of UpGuard Breach Risk?

Saner CVEM

Prevention-first Vulnerability and Exposure Management for unified visibility, prioritization, compliance, and remediation Saner Continuous Vulnerability and Exposure Management unifies asset exposure, posture anomaly detection, vulnerability assessment, compliance management, risk prioritization, patching, and endpoint actions in one dashboard. Saner CVEM is built to help teams continuously detect, assess, prioritize, and remediate vulnerabilities and other security risks from a unified console Why Choose Saner CVEM? • Unified dashboard with interactive views across visibility, detection, prioritization, and remediation for a single source of truth • Complete asset visibility across endpoint and non-endpoint devices, operating system applications, third-party applications, and lifecycle changes • Continuous risk discovery with rapid scans, daily-updated risk intelligence, and posture anomaly detection that helps surface outliers and misconfigurations faster • Context-driven prioritization with SSVC categories such as Act, Attend, Track, and Track* so teams can focus on the risks that deserve action first. • Continuous compliance management with built-in templates, customizable profiles, daily checks, and deviation tracking across common frameworks. • Integrated patching and remediation with vulnerability-to-patch mapping, automated deployment workflows, and endpoint actions from the same ecosystem. • Machine-learning-assisted analysis to identify deeper risk patterns, detect unusual posture, and support smarter remediation decisions. • Customizable, audit-ready reporting for security, IT, and compliance teams that need clearer evidence and easier tracking. • Flexible deployment on cloud or on-premises, with remediation support across Windows, Linux, macOS, and AIX environments.

Average Rating: 4.5/5.0

Total Reviews: 72

How Do G2 Users Rate Saner CVEM?

  • Vulnerability Intelligence: 9.5/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.0/10 (Category avg: 8.6/10)
  • Ease of Admin: 9.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Saner CVEM?

  • Seller: SecPod
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Redwood City, California
  • Twitter: @secpod
    542 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    182 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Small, 38% Medium

What Do G2 Reviewers Say About Saner CVEM?

AI-generated summary from verified user reviews

Pros
  • Users value the automatic security updates from Saner CVEM, ensuring timely compliance for remote workforce systems.
  • Users appreciate the advanced automation features of Saner CVEM, streamlining security patch management for remote systems.
  • Users value the seamless integrations of Saner CVEM, enhancing operational efficiency and strengthening digital security across IT processes.
  • Users value the automated compliance management of Saner CVEM, enhancing efficiency and reducing manual intervention significantly.
  • Users highlight the exceptional customer support from Saner CVEM, enhancing security and helping organizations stay protected.
Cons
  • Users often face integration issues with Saner CVEM, leading to frustrations during setup and ongoing maintenance.
  • Users note limited features in Saner CVEM, especially in multi-tenant support and integration capabilities, impacting efficiency.
  • Users experience slow performance when loading large data sets and during initial setup, affecting usability.
  • Users experience slow scanning, especially with initial dashboard load times and large data sets affecting daily checks.
  • Users find the limited cloud integration challenging, requiring workarounds and custom scripts for effective use.

What Are Recent G2 Reviews of Saner CVEM?

What Are G2 Users Discussing About Saner CVEM?

Detectify

Detectify sets a new standard for advanced application security testing, challenging traditional DAST by providing evolving coverage of each and every exposed asset across the changing attack surface. AppSec teams trust Detectify to expose how attackers will exploit their Internet-facing applications. The Detectify platform automates continuous real-world, payload-based attacks fuelled by its global community of elite ethical hackers into its own expert-built engines, exposing critical weaknesses before it's too late. The Detectify solution includes: - Automated discovery of known and unknown digital assets via domain & cloud connectors - Continuous coverage (24/7) of every corner of the attack surface with dynamic testing. Not just predefined targets - 100% payload-based testing fuelled by elite ethical hackers for a high signal-to-noise ratio - Distributed coverage across an unmatched array of relevant technologies - Actionable remediation tips for software development teams - Team functionality to easily share reports - Powerful integrations platform to prioritize and triage vulnerability findings onward to development teams -Advanced API functionality -Capabilities to set custom attack surface security policies

Average Rating: 4.5/5.0

Total Reviews: 49

How Do G2 Users Rate Detectify?

  • Vulnerability Intelligence: 9.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 10.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.4/10 (Category avg: 8.6/10)
  • Ease of Admin: 8.7/10 (Category avg: 9.0/10)

Who Is the Company Behind Detectify?

  • Seller: Detectify
  • Year Founded: 2013
  • HQ Location: Stockholm, Sweden
  • Twitter: @detectify
    11,256 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    96 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 47% Small, 35% Medium

What Do G2 Reviewers Say About Detectify?

AI-generated summary from verified user reviews

Pros
  • Users praise Detectify for its automation capabilities, making security testing seamless and adaptable to existing workflows.
  • Users appreciate Detectify's automation testing capabilities, making security assessments easier and more efficient to manage.
  • Users appreciate the customizability of Detectify, enjoying its easy integration and tailored security testing options.
  • Users praise Detectify for its easy integration and comprehensive dynamic application security testing, enhancing security without complex setups.
  • Users value Detectify for its effective dynamic application security testing and seamless integration into existing workflows.
Cons
  • Users find the initial setup complex, which can create challenges in getting started with Detectify.
  • Users struggle with the complex queries in Detectify, which hinder understanding of the spidering outcomes and assessments.
  • Users find the complex setup of Detectify challenging, making initial use more difficult than expected.
  • Users find Detectify expensive when testing multiple sites, affecting its accessibility for wider use.
  • Users face inaccuracies in Detectify's spidering results, leading to uncertainty in thorough application assessments.

What Are Recent G2 Reviews of Detectify?

What Are G2 Users Discussing About Detectify?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated April 10, 2026