Best Security Information and Event Management (SIEM) Software for Small Business

How Many Security Information and Event Management (SIEM) Software Products Does G2 Track?

Total Products under this Category: 145

Category Stats (Oct 2026)

  • Average Rating: 4.46/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: EventSentry (+0.55%) - Among all products in this category, EventSentry recorded the largest rating increase compared to last month

Last updated: October 07, 2026

How Does G2 Rank Security Information and Event Management (SIEM) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,300+ Authentic Reviews
  • 145+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

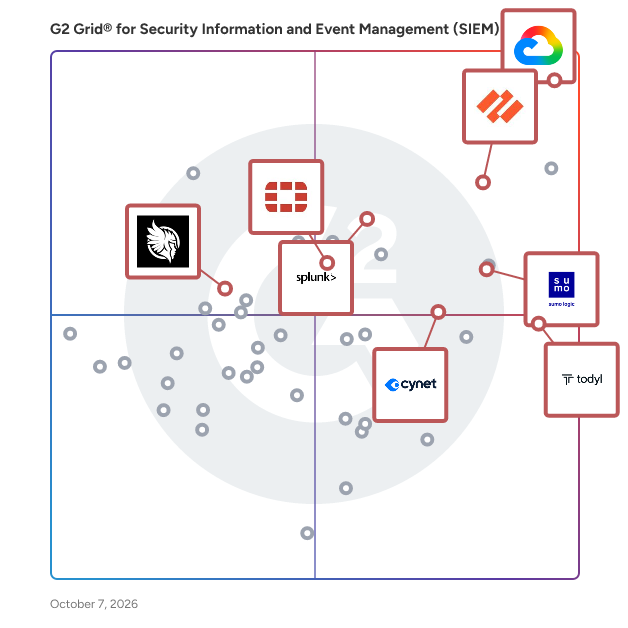
G2 Grid® for Security Information and Event Management (SIEM) Software

G2 Grid® for Security Information and Event Management (SIEM) Software plotting products by satisfaction and market presence

Highlighted products: Google Security Operations, Todyl Security Platform, Palo Alto Cortex XSIAM, Huntress Managed SIEM, Splunk Enterprise, Sumo Logic, FortiSIEM, and Cynet.

Underlying data: [Grid® JSON](https://www.g2.com/categories/security-information-and-event-management-siem/grids.json?focus%5B%5D=google-security-operations&focus%5B%5D=todyl-security-platform&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=huntress-managed-siem&focus%5B%5D=splunk-enterprise&focus%5B%5D=sumo-logic&focus%5B%5D=fortisiem&focus%5B%5D=cynet&segment=small-business)

Google Security Operations

Google Security Operations offers a unified experience across SIEM, SOAR, and threat intelligence to drive better detection, investigation, and response. Collect security telemetry data, apply threat intel to identify high priority threats, drive response with playbook automation, case management, and collaboration. It also provides Gemini-native agentic defense to help autonomously handle workflows like alert triage, threat hunting, and detection engineering. Google Security Operations also supports AI Threat Defense to monitor, detect, and respond to threats from code you do not own or cannot patch.

Average Rating: 4.4/5.0

Total Reviews: 144

How Do G2 Users Rate Google Security Operations?

  • Activity Monitoring: 9.8/10 (Category avg: 9.1/10)
  • Data Examination: 9.3/10 (Category avg: 8.6/10)
  • Ease of Use: 8.4/10 (Category avg: 8.8/10)
  • Log Management: 9.1/10 (Category avg: 9.1/10)

Who Is the Company Behind Google Security Operations?

  • Seller: Google
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • Twitter: @google
    31,899,995 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG

Who Uses This Product?

  • Who Uses This: Student, Developer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 42% Small, 33% Medium

What Do G2 Reviewers Say About Google Security Operations?

AI-generated summary from verified user reviews

Pros
  • Users value the centralized detection and investigation of Google Security Operations, enhancing efficiency in threat management.
  • Users value the high-level threat detection capabilities of Google Security Operations, enhancing their security response efficiency.
  • Users find Google Security Operations very easy to use, allowing for quick incident analysis and efficient responses.
  • Users value the comprehensive security of Google Security Operations for effectively detecting and responding to threats.
  • Users appreciate the seamless integrations of Google Security Operations, enhancing threat detection and providing a unified security view.
Cons
  • Users find the costly upkeep of Google Security Operations challenging, especially for large organizations.
  • Users often face a steep learning curve with Google Security Operations, especially if unfamiliar with Google Cloud services.
  • Users find the implementation and configuration complex, requiring more time and resources compared to other tools.
  • Users find the learning difficulty of Google Security Operations challenging due to its complex features and setup.
  • Users find limited customization in Google Security Operations hinders adaptability and user experience for specific security needs.

What Are Recent G2 Reviews of Google Security Operations?

Todyl Security Platform

Todyl is an AI-powered Cybersecurity and Assurance Platform for threat, risk, and compliance management delivered through a single agent and a single portal. Our platform defends against modern, advanced threats spanning identity, endpoint, network, cloud, SaaS, and more. We also simplify meeting and demonstrating extensive compliance and insurance requirements with centralized data collection and reporting, easy-to-use assessment tools, a built-in risk register, and dashboards to cut back on manual reporting and spreadsheet sprawl. Our platform delivers a layered approach to cybersecurity, spanning SASE, Micro-Segmentation (LZT), Endpoint Security, SIEM, MXDR, and GRC all delivered through the same agent, in a cloud native platform. It’s easy to implement as a cost effective, fully integrated single solution that can consolidate and simplify your security and compliance programs. You can also deploy individual modules to meet your current needs, with a simple toggle within the UI to add or trial new modules when you need them. And an integrated Assurance Marketplace helps you complete your security program with additional services like incident response and penetration testing, and streamlined access to cyber insurance providers.

Average Rating: 4.7/5.0

Total Reviews: 107

How Do G2 Users Rate Todyl Security Platform?

  • Activity Monitoring: 9.4/10 (Category avg: 9.1/10)
  • Data Examination: 9.0/10 (Category avg: 8.6/10)
  • Ease of Use: 8.7/10 (Category avg: 8.8/10)
  • Log Management: 9.4/10 (Category avg: 9.1/10)

Who Is the Company Behind Todyl Security Platform?

  • Seller: Todyl
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Denver, CO
  • LinkedIn® Page: www.linkedin.com
    120 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Owner, President
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 76% Small, 7% Medium

What Do G2 Reviewers Say About Todyl Security Platform?

AI-generated summary from verified user reviews

Pros
  • Users praise the ease of use of Todyl, highlighting its intuitive interface and seamless integration capabilities.
  • Users highlight the responsive and accessible customer support of Todyl, enhancing their overall experience and efficiency.
  • Users praise the convenient deployment and comprehensive integration features of Todyl Security Platform for enhanced security.
  • Users value the comprehensive security offered by Todyl, appreciating its ease of installation and cost-effectiveness.
  • Users praise the deployment ease of Todyl, appreciating its intuitive interface and seamless integration across platforms.
Cons
  • Users find there are improvements needed in customization, integrations, and the steep learning curve for Todyl's platform.
  • Users report integration issues with Todyl, noting limited API capabilities and inconsistencies with third-party connections.
  • Users find the reporting options inadequate, lacking ease of access and integration for strategic reviews.
  • Users notice the limited features in Todyl, particularly in customization, API, and reporting capabilities.
  • Users find the reporting tools inadequate, making it hard to extract useful insights for strategic reviews.

What Are Recent G2 Reviews of Todyl Security Platform?

Palo Alto Cortex XSIAM

Product Description: Palo Alto Networks' Cortex XSIAM is an AI-driven security operations platform designed to transform traditional Security Operations Centers by integrating and automating key functions such as data centralization, threat detection, and incident response. By leveraging machine learning and automation, it enables organizations to detect and respond to threats more efficiently, reducing manual workloads and improving overall security posture. Key Features and Functionality: - Data Centralization: Aggregates data from various sources into a unified platform, providing comprehensive visibility across the enterprise. - AI-Powered Threat Detection: Utilizes machine learning algorithms to identify anomalies and potential threats in real-time. - Automated Incident Response: Streamlines response processes through automation, enabling rapid mitigation of security incidents. - Integrated SOC Capabilities: Combines functions such as Extended Detection and Response , Security Orchestration, Automation, and Response , Attack Surface Management , and Security Information and Event Management into a cohesive platform, eliminating the need for multiple disparate tools. - Scalability: Designed to handle large volumes of data and adapt to the evolving needs of modern enterprises. Primary Value and Problem Solved: Cortex XSIAM addresses the challenges of disjointed data, weak threat defense, and heavy reliance on manual work in traditional SOCs. By centralizing data and automating security operations, it simplifies processes, enhances threat detection accuracy, and accelerates incident response times. This transformation enables organizations to proactively outpace threats, reduce operational costs, and achieve a more robust security posture.

Average Rating: 4.4/5.0

Total Reviews: 103

How Do G2 Users Rate Palo Alto Cortex XSIAM?

  • Activity Monitoring: 9.5/10 (Category avg: 9.1/10)
  • Data Examination: 8.5/10 (Category avg: 8.6/10)
  • Ease of Use: 8.7/10 (Category avg: 8.8/10)
  • Log Management: 9.5/10 (Category avg: 9.1/10)

Who Is the Company Behind Palo Alto Cortex XSIAM?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • Twitter: @PaloAltoNtwks
    128,951 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Large, 35% Medium

What Do G2 Reviewers Say About Palo Alto Cortex XSIAM?

AI-generated summary from verified user reviews

Pros
  • Users value the best-in-class log management of Palo Alto Cortex XSIAM, benefiting from its effective alerting and integration features.
  • Users find the user-friendly dashboard of Palo Alto Cortex XSIAM essential for monitoring and understanding alerts effectively.
  • Users value the real-time monitoring capabilities of Palo Alto Cortex XSIAM, enhancing threat detection and response efficiency.
  • Users value the simple and user-friendly interface of Palo Alto Cortex XSIAM, making monitoring effortless.
  • Users value the good dashboard creation tools in Palo Alto Cortex XSIAM, enhancing ease of use and implementation.
Cons
  • Users note that Palo Alto Cortex XSIAM requires significant resources, impacting implementation time and increasing infrastructure costs.
  • Users find the complexity of implementation for Palo Alto Cortex XSIAM to be time-consuming and resource-intensive.
  • Users find the cost of Palo Alto Cortex XSIAM to be high, especially for smaller businesses.
  • Users face dashboard issues with XSIAM, finding it difficult to monitor assets and navigate the interface.
  • Users face difficult setup issues with Palo Alto Cortex XSIAM, requiring expertise and extensive time for initial implementation.

What Are Recent G2 Reviews of Palo Alto Cortex XSIAM?

What Are G2 Users Discussing About Palo Alto Cortex XSIAM?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Huntress Managed SIEM

Huntress Managed SIEM is a fully managed Security Information and Event Management (SIEM) solution that centralizes and correlates security event data from firewalls, endpoints, identities, and cloud environments, backed by a 24/7, human-staffed Security Operations Center (SOC). Built for managed service providers (MSPs) and small to mid-sized businesses (SMBs) without the resources to run an in-house SIEM, it pairs automated log aggregation and threat detection with expert analysts who filter out noise and investigate suspicious activity in real time. When paired with Huntress Managed EDR or Managed ITDR, it correlates endpoint and identity signals with broader network activity to build a complete picture of an attack. Huntress Managed SIEM also supports compliance and regulatory reporting requirements, giving lean security teams enterprise-grade visibility and faster threat detection without the cost or complexity of a traditional SIEM deployment. The target audience for Huntress includes internal IT teams that may lack the resources or expertise to manage cybersecurity independently, as well as MSPs looking for reliable solutions to enhance their service offerings. These businesses often face unique challenges, such as budget constraints and limited IT staff, making it essential for them to adopt a cybersecurity strategy that is both effective and affordable. Huntress addresses these needs by providing a suite of purpose-built solutions tailored to these specific requirements, ensuring they can defend against cyber threats without compromising their operational efficiency. Key features of Huntress include its Managed Security Platform, which offers real-time threat detection and response capabilities. The platform continuously monitors for malicious activity, enabling rapid identification and remediation of potential threats. Additionally, the 24/7 SOC staffed by cybersecurity experts ensures that any incidents are promptly addressed, providing peace of mind to businesses that may not have in-house security teams. Huntress also emphasizes education, offering resources and training to help users understand cybersecurity best practices and stay informed about the latest threats. By delivering a combination of technology, services, and expertise, Huntress stands out in the cybersecurity landscape. The proactive approach of Huntress not only helps businesses defend against current threats but also prepares them for future challenges, making it a valuable partner in the ongoing fight against cybercrime.

Average Rating: 4.7/5.0

Total Reviews: 51

How Do G2 Users Rate Huntress Managed SIEM?

  • Ease of Use: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Huntress Managed SIEM?

  • Seller: Huntress Labs
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Ellicott City, US
  • Twitter: @HuntressLabs
    40,338 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    978 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 65% Small, 23% Medium

What Are Recent G2 Reviews of Huntress Managed SIEM?

Splunk Enterprise

Find out what is happening in your business and take meaningful action quickly with Splunk Enterprise. Automate the collection, indexing and alerting of machine data that's critical to your operations. Uncover the actionable insights from all your data — no matter the source or format. Leverage artificial intelligence and machine learning for predictive and proactive business decisions.

Average Rating: 4.3/5.0

Total Reviews: 415

How Do G2 Users Rate Splunk Enterprise?

  • Activity Monitoring: 9.1/10 (Category avg: 9.1/10)
  • Data Examination: 8.4/10 (Category avg: 8.6/10)
  • Ease of Use: 8.2/10 (Category avg: 8.8/10)
  • Log Management: 9.3/10 (Category avg: 9.1/10)

Who Is the Company Behind Splunk Enterprise?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • Twitter: @Cisco
    720,366 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 64% Large, 28% Medium

What Do G2 Reviewers Say About Splunk Enterprise?

AI-generated summary from verified user reviews

Pros
  • Users find Splunk Enterprise's ease of use remarkable, enabling quick access and seamless integration of large datasets.
  • Users value the robust data ingestion capabilities of Splunk Enterprise, efficiently managing diverse data sources.
  • Users commend the great integration capabilities of Splunk Enterprise, facilitating seamless implementation across various networks and systems.
  • Users value the flexibility and visualization capabilities of Splunk Enterprise, enabling effective data analysis and troubleshooting.
  • Users praise the visualization capabilities of Splunk Enterprise dashboards for effective data analysis and decision-making.
Cons
  • Users find Splunk Enterprise to be expensive, with high renewal costs and limitations that affect large organizations.
  • Users find the learning curve steep, struggling to quickly grasp Splunk Enterprise's many features and functionalities.
  • Users experience slow performance with Splunk Enterprise, noting occasional crashes and delays in processing saved searches.
  • Users find the complex configuration of Splunk Enterprise challenging, impacting performance optimization and overall user experience.
  • Users find the pricing issues with Splunk Enterprise burdensome, especially regarding storage costs and data limits.

What Are Recent G2 Reviews of Splunk Enterprise?

What Are G2 Users Discussing About Splunk Enterprise?

Sumo Logic

Sumo Logic, Inc. unifies and analyzes enterprise data, translating it into actionable insights through one AI-powered cloud-native log analytics platform. This single source of truth enables Dev, Sec and Ops teams to simplify complexity, collaborate efficiently and accelerate data-driven decisions that drive business value. Customers around the world rely on the Sumo Logic SaaS Log Analytics Platform for trusted insights to ensure application reliability, secure and protect against modern security threats, and gain insights into their cloud infrastructures. For more information, visit: SUMOLOGIC.COM

Average Rating: 4.3/5.0

Total Reviews: 406

How Do G2 Users Rate Sumo Logic?

  • Activity Monitoring: 9.1/10 (Category avg: 9.1/10)
  • Data Examination: 9.0/10 (Category avg: 8.6/10)
  • Ease of Use: 8.2/10 (Category avg: 8.8/10)
  • Log Management: 9.4/10 (Category avg: 9.1/10)

Who Is the Company Behind Sumo Logic?

  • Seller: Sumo Logic
  • Company Website:
  • Year Founded: 2010
  • HQ Location: Redwood City, CA
  • Twitter: @SumoLogic
    6,542 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    824 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 48% Medium, 38% Large

What Do G2 Reviewers Say About Sumo Logic?

AI-generated summary from verified user reviews

Pros
  • Users highlight the ease of use in Sumo Logic, citing its simple query language and intuitive configurations.
  • Users value the ease of searching and configuring logs with Sumo Logic, enhancing their monitoring and tracing efficiency.
  • Users appreciate the Comprehensive Continuous Intelligence feature of Sumo Logic for transforming data into actionable insights quickly.
  • Users value the powerful visual insights and efficient log management capabilities of Sumo Logic for fast resolution.
  • Users value the real-time monitoring capabilities of Sumo Logic, enjoying swift insights and effective data management.
Cons
  • Users find Sumo Logic expensive, prompting concerns about whether its value justifies the high pricing.
  • Users find the difficult learning curve of Sumo Logic challenging, requiring significant time to become proficient.
  • Users face a steep learning curve with Sumo Logic, requiring significant time to master its features and query language.
  • Users face a steep learning curve with Sumo Logic, requiring significant time to master complex features and queries.
  • Users experience slow performance with Sumo Logic, facing delays in alerting and a cumbersome user interface.

What Are Recent G2 Reviews of Sumo Logic?

What Are G2 Users Discussing About Sumo Logic?

FortiSIEM

The complexity of managing network and security operations is resulting in increases in breaches worldwide. Discovery, isolation, and remediation of these incidents are measured in hundreds of days. And with a dwindling pool of skilled cyber security personnel able to manage the wide array of devices and data sources to protect their network assets, success requires a new approach. FortiSIEM provides organizations of all sizes with a comprehensive, holistic, and scalable solution for security, performance, and compliance management, from IoT to the cloud. FortiSIEM expands network visibility through the Fortinet Security Fabric's integrations with the leading security products present in most networks today.

Average Rating: 4.3/5.0

Total Reviews: 40

How Do G2 Users Rate FortiSIEM?

  • Activity Monitoring: 8.7/10 (Category avg: 9.1/10)
  • Data Examination: 7.9/10 (Category avg: 8.6/10)
  • Ease of Use: 8.6/10 (Category avg: 8.8/10)
  • Log Management: 8.7/10 (Category avg: 9.1/10)

Who Is the Company Behind FortiSIEM?

  • Seller: Fortinet
  • Year Founded: 2000
  • HQ Location: Sunnyvale, CA
  • Twitter: @Fortinet
    151,422 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    16,564 employees on LinkedIn®
  • Ownership: NASDAQ: FTNT

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 46% Medium, 29% Large

What Do G2 Reviewers Say About FortiSIEM?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time visibility of FortiSIEM, enhancing threat detection and troubleshooting across their infrastructure.
  • Users value the single-pane-of-glass visibility in FortiSIEM, which enhances real-time threat detection and troubleshooting.
  • Users appreciate the real-time threat detection and visibility offered by FortiSIEM for effective security management.
  • Users appreciate the real-time log correlation of FortiSIEM, enhancing their ability to troubleshoot and detect threats quickly.
  • Users value the real-time visibility of FortiSIEM, enhancing threat detection and troubleshooting across the infrastructure.
Cons
  • Users find the complex configuration of FortiSIEM challenging for initial setup and advanced reporting usability.
  • Users find the initial setup and customization complex, making it challenging to navigate advanced use cases effectively.
  • Users find the difficult customization of FortiSIEM challenging, particularly during setup and when trying to navigate the interface.
  • Users find the learning curve for setup and customization of FortiSIEM to be challenging and time-consuming.
  • Users find the poor interface design of FortiSIEM challenging, especially during setup and advanced reporting tasks.

What Are Recent G2 Reviews of FortiSIEM?

What Are G2 Users Discussing About FortiSIEM?

Cynet

Cynet is the unified, AI-powered cybersecurity platform that delivers robust and comprehensive protection for security teams while maximizing operational efficiency for managed service providers (MSPs). This platform consolidates a wide array of security capabilities into a single, user-friendly interface, ensuring that organizations can effectively safeguard their digital assets without the complexity often associated with multi-solution environments. Cynet’s platform simplifies security management by integrating various functionalities, such as endpoint protection, threat detection, and incident response, into one cohesive system. This integration not only streamlines operations but also allows organizations to allocate their resources more effectively, ultimately enhancing their overall security posture. One of the standout features of Cynet’s platform is its remarkable performance in the MITRE ATT&CK Evaluations. Cynet delivered 100% visibility and 100% analytic coverage without requiring any configuration changes three years in a row. This capability ensures that organizations can monitor their environments comprehensively and respond to threats with precision. The platform’s built-in analytics and reporting tools provide actionable insights, enabling users to make informed decisions about their cybersecurity strategies. Additionally, Cynet offers 24/7 expert support, which is crucial for organizations that may not have in-house cybersecurity expertise. This round-the-clock assistance ensures that users can quickly address any security incidents or concerns, minimizing potential downtime and damage. The combination of advanced technology and dedicated support positions Cynet as a valuable partner for SMEs and service providers looking to enhance their cybersecurity measures. In summary, Cynet’s unified, AI-powered cybersecurity platform stands out in the crowded cybersecurity market by offering a unified solution tailored to the needs of MSPs. Its comprehensive features, exceptional performance in industry evaluations, and continuous expert support make it a compelling choice for organizations seeking to bolster their cybersecurity defenses while maintaining operational efficiency.

Average Rating: 4.7/5.0

Total Reviews: 218

How Do G2 Users Rate Cynet?

  • Activity Monitoring: 9.4/10 (Category avg: 9.1/10)
  • Data Examination: 8.8/10 (Category avg: 8.6/10)
  • Ease of Use: 9.1/10 (Category avg: 8.8/10)
  • Log Management: 8.9/10 (Category avg: 9.1/10)

Who Is the Company Behind Cynet?

  • Seller: Cynet
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    335 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: SOC Analyst, Technical Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 58% Medium, 30% Small

What Do G2 Reviewers Say About Cynet?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Cynet, appreciating its straightforward yet comprehensive functionalities for effective protection.
  • Users value the unified platform of Cynet, which offers effective security through streamlined endpoint protection and detection.
  • Users praise Cynet for its effective threat detection and seamless monitoring, enhancing overall cybersecurity effortlessly.
  • Users commend Cynet for its exceptional customer support, ensuring a smooth and efficient deployment experience.
  • Users praise Cynet for its flawless threat monitoring and detection, enhancing overall cybersecurity effectiveness effortlessly.
Cons
  • Users find limited customization options in reporting and dashboards, affecting their ability to present necessary data.
  • Users note a lack of customization in reports, wishing for more options to tailor data presentation.
  • Users find the reporting features lacking, with requests for better customization and visualization tools.
  • Users find feature limitations in Cynet, with a desire for more customization options and broader integrations.
  • Users note limited features, such as basic reporting and few third-party integrations, impacting customization and deeper controls.

What Are Recent G2 Reviews of Cynet?

What Are G2 Users Discussing About Cynet?

Check Point Infinity Platform

Check Point Infinity is the only fully consolidated cyber security architecture that provides unprecedented protection against Gen V mega-cyber attacks as well as future cyber threats across all networks, endpoint, cloud and mobile. The architecture is designed to resolve the complexities of growing connectivity and inefficient security.

Average Rating: 4.6/5.0

Total Reviews: 109

How Do G2 Users Rate Check Point Infinity Platform?

  • Ease of Use: 9.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Check Point Infinity Platform?

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 44% Large, 37% Medium

What Do G2 Reviewers Say About Check Point Infinity Platform?

AI-generated summary from verified user reviews

Pros
  • Users commend the advanced security features of Check Point Infinity Platform, effectively preventing future attacks on cloud infrastructures.
  • Users value the cloud security features of Check Point Infinity Platform for efficient audits and infrastructure evaluations.
  • Users commend the proactive threat detection of Check Point Infinity Platform, enhancing security for cloud applications.
  • Users highlight the comprehensive security features of Check Point Infinity Platform, effectively shielding against future attacks.
  • Users value the advanced security features of Check Point Infinity for effectively safeguarding their cloud infrastructure.
Cons
  • Users find the steep learning curve of Check Point Infinity Platform challenging due to its complexity and extensive features.
  • Users find the complex setup process for Check Point Infinity Platform can be time-consuming and confusing at times.
  • Users feel that improvement is needed in real-time support and custom ruleset creation for better functionality.
  • Users express concerns about poor support services, indicating a need for improvement in customer assistance and log visibility.
  • Users find the limited customization options challenging, affecting their ability to tailor the platform to their needs.

What Are Recent G2 Reviews of Check Point Infinity Platform?

What Are G2 Users Discussing About Check Point Infinity Platform?

CrowdStrike Falcon Endpoint Protection Platform

Organizations today face a serious challenge: managing numerous security vendors and tools while confronting an ever-evolving threat landscape. Sophisticated adversaries are becoming smarter, faster, and more evasive, launching complex attacks that can strike in minutes or even seconds. Traditional security approaches struggle to keep pace, leaving businesses vulnerable. The CrowdStrike Falcon Platform addresses this by offering a unified, cloud-native solution. It consolidates previously siloed security solutions and incorporates third-party data into a single platform with one efficient and resource-conscious agent, leveraging advanced AI and real-time threat intelligence. This approach simplifies security operations, speeds analyst decision making, and enhances protection to stop the breach, allowing organizations to reduce risk with less complexity and lower costs. CrowdStrike's Falcon Platform includes: - Endpoint Security: Secure the endpoint, stop the breach - Identify Protection: Identity is the front line, defend it - Next-Gen SIEM: The future of SIEM, today - Data Protection: Real-time data protection from endpoint to cloud - Exposure Management: Understand risk to stop breaches - Charlotte AI: Powering the next evolution of the SOC

Average Rating: 4.7/5.0

Total Reviews: 547

How Do G2 Users Rate CrowdStrike Falcon Endpoint Protection Platform?

  • Activity Monitoring: 9.5/10 (Category avg: 9.1/10)
  • Data Examination: 8.9/10 (Category avg: 8.6/10)
  • Ease of Use: 9.0/10 (Category avg: 8.8/10)
  • Log Management: 8.7/10 (Category avg: 9.1/10)

Who Is the Company Behind CrowdStrike Falcon Endpoint Protection Platform?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • Twitter: @CrowdStrike
    110,809 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Analyst, Security Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 46% Large, 40% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Endpoint Protection Platform?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the lightweight performance and powerful threat detection of CrowdStrike Falcon, enhancing security without slowing down systems.
  • Users commend the effective threat detection capabilities of CrowdStrike Falcon, ensuring robust security without system slowdowns.
  • Users appreciate the ease of use of CrowdStrike Falcon, benefiting from its lightweight impact and efficient incident management.
  • Users appreciate the advanced real-time threat protection of CrowdStrike Falcon, ensuring efficient security without system performance issues.
  • Users praise the exceptional threat detection of CrowdStrike Falcon, noting its effectiveness against both known and unknown threats.
Cons
  • Users find the cost prohibitive for smaller organizations, especially with additional modules increasing overall expenses.
  • Users find the complexity of the user interface and additional costs challenging, complicating their overall experience.
  • Users face a steep learning curve with CrowdStrike’s query language, making transitions from other platforms challenging.
  • Users find the limited features challenging, especially concerning cost and technical accessibility for smaller businesses.
  • Users find that pricing can be a barrier for smaller organizations, complicating access to advanced features.

What Are Recent G2 Reviews of CrowdStrike Falcon Endpoint Protection Platform?

What Are G2 Users Discussing About CrowdStrike Falcon Endpoint Protection Platform?

IBM QRadar SIEM

Outsmart threats with an end-to-end award-winning security suite; proven to prevent, endure and recover from both known & unknown IT hazards faced by SoCs in the modern-day.

Average Rating: 4.4/5.0

Total Reviews: 284

How Do G2 Users Rate IBM QRadar SIEM?

  • Activity Monitoring: 8.7/10 (Category avg: 9.1/10)
  • Data Examination: 8.3/10 (Category avg: 8.6/10)
  • Ease of Use: 8.3/10 (Category avg: 8.8/10)
  • Log Management: 8.7/10 (Category avg: 9.1/10)

Who Is the Company Behind IBM QRadar SIEM?

  • Seller: IBM
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • Twitter: @IBMSecurity
    74,660 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®
  • Ownership: SWX:IBM

Who Uses This Product?

  • Who Uses This: Security Engineer, SOC Analyst
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 52% Large, 29% Medium

What Do G2 Reviewers Say About IBM QRadar SIEM?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of IBM QRadar SIEM, facilitating effective threat management and investigation.
  • Users appreciate the flexible integration capabilities of IBM QRadar SIEM, enhancing log management across diverse sources.
  • Users value the advanced threat detection and centralized log management features of IBM QRadar SIEM for enhanced security.
  • Users appreciate the easy integrations of IBM QRadar SIEM, enhancing its functionality with various platforms seamlessly.
  • Users appreciate the user-friendly interface of IBM QRadar SIEM, making it accessible for both tech and non-tech users.
Cons
  • Users find the UX improvements lacking, struggling with limited features and an unfriendly interface in QRadar SIEM.
  • Users find IBM QRadar SIEM expensive, particularly small and mid-sized companies struggling with the overall cost.
  • Users find the high cost of IBM QRadar SIEM challenging, particularly for smaller organizations needing comprehensive support.
  • Users face dashboard issues with IBM QRadar SIEM, lacking customization, usability, and integration for optimal performance.
  • Users find the time-consuming nature of QRadar SIEM frustrating, especially with complicated queries and log fetching delays.

What Are Recent G2 Reviews of IBM QRadar SIEM?

Splunk Enterprise Security

Splunk Enterprise Security (ES) is a data-centric, modern security information and event management (SIEM) solution that delivers data-driven insights for full breadth visibility into your security posture so you can protect your business and mitigate risk at scale. With unparalleled search and reporting, advanced analytics, integrated intelligence, and prepackaged security content, Splunk ES accelerates threat detection and investigation, letting you determine the scope of high-priority threats to your environment so you can quickly take action. Built on an open and scalable data platform, you can stay agile in the face of evolving threats and business needs. Our extensive ecosystem of Splunk, partner, and community-built integrations as well as flexible deployment options ensure your technology investments are working in tandem with Splunk ES whilst meeting you wherever you are on your cloud, multi-cloud, or hybrid journey.

Average Rating: 4.3/5.0

Total Reviews: 224

How Do G2 Users Rate Splunk Enterprise Security?

  • Activity Monitoring: 8.8/10 (Category avg: 9.1/10)
  • Data Examination: 8.5/10 (Category avg: 8.6/10)
  • Ease of Use: 8.2/10 (Category avg: 8.8/10)
  • Log Management: 9.3/10 (Category avg: 9.1/10)

Who Is the Company Behind Splunk Enterprise Security?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • Twitter: @Cisco
    720,366 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 59% Large, 30% Medium

What Do G2 Reviewers Say About Splunk Enterprise Security?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Splunk Enterprise Security, enhancing their monitoring and log management experience.
  • Users appreciate the easy integrations of Splunk Enterprise Security, enabling seamless connection with various platforms and systems.
  • Users highlight the impressive threat detection capabilities of Splunk Enterprise Security, enhancing security focus and reducing false alarms.
  • Users value the effective features of Splunk Enterprise Security, enhancing security analysis with comprehensive logs and insights.
  • Users appreciate the user-friendly interface of Splunk Enterprise Security, enabling efficient monitoring and attractive dashboards.
Cons
  • Users find the high costs associated with data ingestion to be a significant drawback of Splunk Enterprise Security.
  • Users find the initial implementation complex, needing expert resources and time to onboard Splunk Enterprise Security effectively.
  • Users find the complex implementation of Splunk Enterprise Security challenging, requiring extensive expertise and resources.
  • Users find the complex setup of Splunk Enterprise Security time-consuming and challenging, impacting initial deployment effectiveness.
  • Users find the difficult learning curve of Splunk Enterprise Security challenging, especially for those new to data analysis.

What Are Recent G2 Reviews of Splunk Enterprise Security?

What Are G2 Users Discussing About Splunk Enterprise Security?

Microsoft Sentinel

Microsoft Sentinel lets you see and stop threats before they cause harm, with SIEM reinvented for a modern world. Microsoft Sentinel is your birds-eye view across the enterprise. Put the cloud and large-scale intelligence from decades of Microsoft security experience to work. Make your threat detection and response smarter and faster with artificial intelligence (AI). Eliminate security infrastructure setup and maintenance, and elastically scale to meet your security needs—while reducing IT costs. With Microsoft Sentinel, you can: - Collect data at cloud scale—across all users, devices, applications, and infrastructure, both on-premises and in multiple clouds - Detect previously uncovered threats and minimize false positives using analytics and unparalleled threat intelligence from Microsoft - Investigate threats with AI and hunt suspicious activities at scale, tapping into decades of cybersecurity work at Microsoft -Respond to incidents rapidly with built-in orchestration and automation of common tasks

Average Rating: 4.4/5.0

Total Reviews: 275

How Do G2 Users Rate Microsoft Sentinel?

  • Activity Monitoring: 8.9/10 (Category avg: 9.1/10)
  • Data Examination: 8.5/10 (Category avg: 8.6/10)
  • Ease of Use: 8.5/10 (Category avg: 8.8/10)
  • Log Management: 8.8/10 (Category avg: 9.1/10)

Who Is the Company Behind Microsoft Sentinel?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • Twitter: @microsoft
    13,091,739 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT

Who Uses This Product?

  • Who Uses This: Senior Software Engineer, Security Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 42% Large, 31% Medium

What Do G2 Reviewers Say About Microsoft Sentinel?

AI-generated summary from verified user reviews

Pros
  • Users value the advanced threat detection of Microsoft Sentinel, enhancing security and proactive threat management.
  • Users value the easy integrations of Microsoft Sentinel, facilitating quick setup and streamlined security processes.
  • Users value the seamless integration of Microsoft Sentinel with various third-party and Microsoft products, enhancing functionality and management.
  • Users commend the ease of use of Microsoft Sentinel, facilitating quick integration and a user-friendly experience.
Cons
  • Users express concern over the high costs of Microsoft Sentinel, especially as data ingestion increases.
  • Users face integration issues with Microsoft Sentinel, especially when connecting to legacy systems and third-party tools.
  • Users find the complexity of Microsoft Sentinel challenging, requiring extensive training and effort for effective use.

What Are Recent G2 Reviews of Microsoft Sentinel?

What Are G2 Users Discussing About Microsoft Sentinel?

EventSentry

EventSentry is a hybrid Security Information and Event Management (SIEM) solution designed to assist users in monitoring and managing their IT infrastructure effectively. By combining real-time event log monitoring with comprehensive system health and network monitoring, EventSentry provides a holistic view of servers and endpoints, enabling organizations to maintain robust security and operational efficiency. This SIEM solution is particularly beneficial for IT security teams, system administrators, and compliance officers who require a centralized platform to oversee their network's security posture. It caters to various industries, including finance, healthcare, and technology, where data integrity and security are paramount. The product is designed for organizations of all sizes, from small businesses to large enterprises, looking to enhance their security monitoring capabilities while ensuring system health. One of the standout features of EventSentry is its security event log normalization and correlation engine. This functionality transforms cryptic Windows security events into easily understandable reports, providing users with valuable insights that go beyond raw event data. The descriptive email alerts generated by the system offer additional context, allowing users to respond swiftly to potential security incidents. This capability is crucial for organizations that need to comply with regulatory requirements and maintain a proactive security stance. Moreover, EventSentry includes 200 compliance and security checks that strengthen security settings and reduce the attack surface - proactively identifying issues before they become liabilities. Malware & Ransomware attacks can be mitigated and detected in real time with innovative process activity monitoring and a flexible anomaly detection engine that can reveal suspicious patterns across any log source. EventSentry supports various integrations, making it adaptable to existing IT environments. This flexibility allows organizations to incorporate the SIEM solution seamlessly into their current systems, enhancing their overall security framework without significant disruption. The multi-tenancy feature further enables organizations to manage multiple clients or departments from a single platform, making it an ideal choice for managed service providers or organizations with diverse operational needs. In summary, EventSentry stands out in the SIEM category by providing a comprehensive approach to security and system monitoring. Its combination of real-time log analysis, health monitoring, and user-friendly reporting equips organizations with the tools necessary to safeguard their digital assets effectively. By leveraging this hybrid SIEM solution, users can achieve a clearer understanding of their security landscape, facilitating informed decision-making and enhancing overall cybersecurity resilience.

Average Rating: 4.6/5.0

Total Reviews: 64

How Do G2 Users Rate EventSentry?

  • Activity Monitoring: 9.1/10 (Category avg: 9.1/10)
  • Data Examination: 8.7/10 (Category avg: 8.6/10)
  • Ease of Use: 8.9/10 (Category avg: 8.8/10)
  • Log Management: 9.1/10 (Category avg: 9.1/10)

Who Is the Company Behind EventSentry?

  • Seller: NETIKUS.NET ltd
  • Company Website:
  • Year Founded: 2002
  • HQ Location: Chicago, Illinois
  • Twitter: @netikus
    971 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    4 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 51% Medium, 31% Small

What Do G2 Reviewers Say About EventSentry?

AI-generated summary from verified user reviews

Pros
  • Users highlight the exceptional customer support from EventSentry, praising quick responses and helpful, knowledgeable staff.
  • Users value the effective alerting system of EventSentry, ensuring they receive only the most important notifications.
  • Users find implementation simple, with easy deployment and minimal resource requirements, making setup quick and efficient.
  • Users find EventSentry's affordable pricing and performance unmatched, appreciating excellent support and easy implementation.
  • Users highlight the world-class support of EventSentry, ensuring quick resolutions and expert assistance whenever needed.
Cons
  • Users note the steep initial learning curve, but resources are available to help overcome it effectively.
  • Users note a steep initial learning curve, but find helpful resources available to aid in their understanding.
  • Users are frustrated with EventSentry's inadequate handling of Linux logs and outdated log aggregation that hinder its effectiveness.
  • Users face challenges with log management issues in EventSentry, particularly with Linux logs and outdated aggregators.
  • Users note that graphical features for report generation need improvement for easier server management and selection.

What Are Recent G2 Reviews of EventSentry?

What Are G2 Users Discussing About EventSentry?

Blumira Automated Detection & Response

Blumira is an integrated security operations platform built for growing teams and the partners supporting them to gain complete visibility into their environment, identify and address risk faster, and deliver advanced security and compliance. The platform includes: - Managed Detections for automated threat hunting to identify attacks early - AI Investigation with 98.5% accurate, human-in-the-loop triage validated against real cases - Rapid Response with automation and 1-click actions to contain and block threats immediately - One Year of Data Retention with unlimited log ingestion to satisfy compliance requirements - Advanced Reporting and dashboards for forensics and easy investigation - Endpoint & Identity Protection (EDR/ITDR) for real-time remediation across devices and users - 24/7 Security Operations support for critical priority issues

Average Rating: 4.6/5.0

Total Reviews: 122

How Do G2 Users Rate Blumira Automated Detection & Response?

  • Activity Monitoring: 8.7/10 (Category avg: 9.1/10)
  • Data Examination: 8.4/10 (Category avg: 8.6/10)
  • Ease of Use: 9.0/10 (Category avg: 8.8/10)
  • Log Management: 8.7/10 (Category avg: 9.1/10)

Who Is the Company Behind Blumira Automated Detection & Response?

  • Seller: Blumira
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Ann Arbor, Michigan
  • Twitter: @blumira
    1 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    55 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Medium, 36% Small

What Do G2 Reviewers Say About Blumira Automated Detection & Response?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the easy setup of Blumira Automated Detection & Response, enabling quick integration and efficient use.
  • Users appreciate the responsive customer support of Blumira, finding it reliable and personal for their IT needs.
  • Users praise the setup ease of Blumira, appreciating its quick integration and automated alert features.
  • Users appreciate the reliable real-time alerting of Blumira, valuing its clarity and ease of use for all techs.
  • Users value the reliable real-time alerting of Blumira, appreciating its ease of use and helpful implementation.
Cons
  • Users find limited customization with detection filters, relying on support for creating necessary custom detections.
  • Users express concern over false positives that can disrupt business functions and lead to frustration with repeated alerts.
  • Users find Blumira's pricing expensive, citing inflexible models and insufficient features in lower tiers.
  • Users express frustration over false positives that waste time and complicate the overall experience with Blumira.
  • Users express concern over insufficient information, desiring better data accessibility and clearer deployment status.

What Are Recent G2 Reviews of Blumira Automated Detection & Response?

What Are G2 Users Discussing About Blumira Automated Detection & Response?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated