Best Deception Technology Software

How Many Deception Technology Software Products Does G2 Track?

Total Products under this Category: 41

Category Stats (Oct 2026)

  • Average Rating: 4.55/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Cynet (+0.04%) - Among all products in this category, Cynet recorded the largest rating increase compared to last month

Last updated: October 07, 2026

How Does G2 Rank Deception Technology Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 500+ Authentic Reviews
  • 41+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

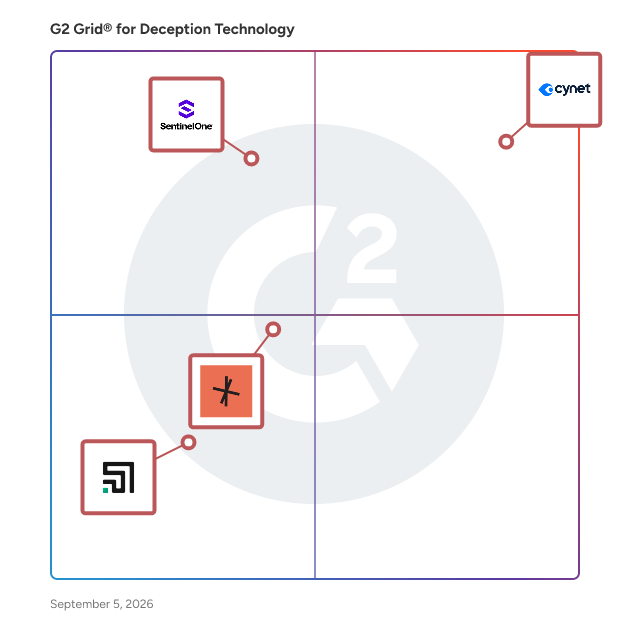
G2 Grid® for Deception Technology Software

G2 Grid® for Deception Technology Software plotting products by satisfaction and market presence

Highlighted products: Cynet, SentinelOne Singularity Endpoint, Tracebit, and Labyrinth Cyber Deception Platform.

Underlying data: [Grid® JSON](https://www.g2.com/categories/deception-technology/grids.json?focus%5B%5D=cynet&focus%5B%5D=sentinelone-singularity-endpoint&focus%5B%5D=tracebit&focus%5B%5D=labyrinth-cyber-deception-platform)

Cynet

Cynet is the unified, AI-powered cybersecurity platform that delivers robust and comprehensive protection for security teams while maximizing operational efficiency for managed service providers (MSPs). This platform consolidates a wide array of security capabilities into a single, user-friendly interface, ensuring that organizations can effectively safeguard their digital assets without the complexity often associated with multi-solution environments. Cynet’s platform simplifies security management by integrating various functionalities, such as endpoint protection, threat detection, and incident response, into one cohesive system. This integration not only streamlines operations but also allows organizations to allocate their resources more effectively, ultimately enhancing their overall security posture. One of the standout features of Cynet’s platform is its remarkable performance in the MITRE ATT&CK Evaluations. Cynet delivered 100% visibility and 100% analytic coverage without requiring any configuration changes three years in a row. This capability ensures that organizations can monitor their environments comprehensively and respond to threats with precision. The platform’s built-in analytics and reporting tools provide actionable insights, enabling users to make informed decisions about their cybersecurity strategies. Additionally, Cynet offers 24/7 expert support, which is crucial for organizations that may not have in-house cybersecurity expertise. This round-the-clock assistance ensures that users can quickly address any security incidents or concerns, minimizing potential downtime and damage. The combination of advanced technology and dedicated support positions Cynet as a valuable partner for SMEs and service providers looking to enhance their cybersecurity measures. In summary, Cynet’s unified, AI-powered cybersecurity platform stands out in the crowded cybersecurity market by offering a unified solution tailored to the needs of MSPs. Its comprehensive features, exceptional performance in industry evaluations, and continuous expert support make it a compelling choice for organizations seeking to bolster their cybersecurity defenses while maintaining operational efficiency.

Average Rating: 4.7/5.0

Total Reviews: 218

Who Is the Company Behind Cynet?

  • Seller: Cynet
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    335 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: SOC Analyst, Technical Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 58% Medium, 30% Small

What Do G2 Reviewers Say About Cynet?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Cynet, appreciating its straightforward yet comprehensive functionalities for effective protection.
  • Users value the unified platform of Cynet, which offers effective security through streamlined endpoint protection and detection.
  • Users praise Cynet for its effective threat detection and seamless monitoring, enhancing overall cybersecurity effortlessly.
  • Users commend Cynet for its exceptional customer support, ensuring a smooth and efficient deployment experience.
  • Users praise Cynet for its flawless threat monitoring and detection, enhancing overall cybersecurity effectiveness effortlessly.
Cons
  • Users find limited customization options in reporting and dashboards, affecting their ability to present necessary data.
  • Users note a lack of customization in reports, wishing for more options to tailor data presentation.
  • Users find the reporting features lacking, with requests for better customization and visualization tools.
  • Users find feature limitations in Cynet, with a desire for more customization options and broader integrations.
  • Users note limited features, such as basic reporting and few third-party integrations, impacting customization and deeper controls.

What Are Recent G2 Reviews of Cynet?

What Are G2 Users Discussing About Cynet?

SentinelOne Singularity Endpoint

SentinelOne® Singularity™ Endpoint is an autonomous endpoint security platform that stops threats in real-time. It unifies endpoint protection (EPP), endpoint detection and response (EDR), and autonomous remediation to stop ransomware, zero-day exploits, supply chain attacks, and fileless malware. Singularity Endpoint protects workstations, mobile devices, servers, and cloud workloads across SaaS, on-premises, hybrid, and air-gapped environments. Behavioral and static AI detection models stop known and unknown threats by identifying how threats behave, not just what they look like. SentinelOne catches what signatures miss, without waiting on updates. Storyline® automatically correlates telemetry into one visual attack story, and patented one-click rollback restores systems to a trusted state in seconds. The result is stronger protection with fewer incidents and less operational overhead: lower dwell time, fewer false positives, and faster response. With Purple AI™, teams accelerate triage, threat hunting, and investigation. From alert to verdict without manual investigation. Purple AI's Agentic Investigation runs the analysis, surfaces the evidence, and tells your team exactly what to do next. The same SentinelOne agent that protects endpoints also defends every identity behind them. Detect credential abuse, shrink your attack surface, and contain identity threats from one console. Seamless integration of endpoint, identity, cloud, and third-party telemetry eliminates blind spots. Built AI-native from day one, Singularity Endpoint delivers best-in-industry coverage across Windows, macOS, Linux, and mobile operating systems, including legacy OSes. Trusted by more than 11,500 customers, SentinelOne is a six-time Gartner® Magic Quadrant™ Leader for Endpoint Protection.

Average Rating: 4.7/5.0

Total Reviews: 206

Who Is the Company Behind SentinelOne Singularity Endpoint?

  • Seller: SentinelOne
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • Twitter: @SentinelOne
    57,863 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,529 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 46% Medium, 36% Large

What Do G2 Reviewers Say About SentinelOne Singularity Endpoint?

AI-generated summary from verified user reviews

Pros
  • Users value the tool efficiency of SentinelOne Singularity Endpoint, appreciating its user-friendly interface and effective threat detection.
  • Users find the ease of integration with Nable RMM and setup straightforward for daily operations.
  • Users praise the exceptional malware protection of SentinelOne, effectively stopping threats before they can cause harm.
  • Users find SentinelOne Singularity Endpoint to be a highly useful tool for incident notification and investigation.
  • Users appreciate the quick alerts and feature-rich capabilities of SentinelOne, enhancing security management and support.
Cons
  • Users face update issues with SentinelOne Singularity, leading to login problems and cumbersome agent management.
  • Users find the difficult learning curve of SentinelOne Singularity Endpoint challenging, especially for beginners navigating its features.
  • Users find the frequent updates challenging, as rapid changes lead to login issues and a steep learning curve.
  • Users report challenges with agent removal issues impacting application functionality and requiring improvement in uninstallation processes.
  • Users report ineffective alerts that hinder troubleshooting and prevent them from addressing application issues effectively.

What Are Recent G2 Reviews of SentinelOne Singularity Endpoint?

What Are G2 Users Discussing About SentinelOne Singularity Endpoint?

Tracebit

Tracebit automatically deploys security canaries across your cloud accounts, endpoints, SaaS applications, and CI/CD pipelines at scale. When attackers touch them, you know immediately. Security canaries are decoy resources and credentials that blend into your environment. They reveal attackers as they move laterally, escalate privileges, or access credentials. Tracebit supports AWS, Azure, Google Cloud, Kubernetes, identity systems, workstations, and developer pipelines. Security teams deploy in 30 minutes using infrastructure-as-code. Tracebit analyzes your environment and recommends canaries that match your naming conventions and resource types, then manages them as your environment evolves. No agents to maintain. No servers to patch. When canaries trigger, you get high-fidelity alerts with forensic context: which principal accessed what resource, from which IP address, using what user agent, and at what time. Alerts integrate with your existing security workflows so your team can investigate and respond. Canaries detect attackers; they do not prevent every breach. Tracebit makes deception technology practical to deploy and maintain, giving security teams detection that works from day one.

Average Rating: 4.9/5.0

Total Reviews: 16

Who Is the Company Behind Tracebit?

  • Seller: Tracebit
  • Year Founded: 2022
  • HQ Location: London, GB
  • Twitter: @tracebit_com
    312 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    44 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 63% Medium, 25% Small

What Do G2 Reviewers Say About Tracebit?

AI-generated summary from verified user reviews

Pros
  • Users value the effective security alerts from Tracebit, ensuring prompt responses to unusual activities across accounts.
  • Users value the continuous monitoring of Tracebit, ensuring security and quick response to unusual activities effectively.
  • Users highlight the feature-rich capabilities of Tracebit, praising its real-time monitoring and seamless integrations.
  • Users praise the easy integrations of Tracebit, quickly adding servers and improving cloud security effortlessly.
  • Users value the robust security features of Tracebit, ensuring quick detection and response to potential threats.
Cons
  • Users find the confusing interface of Tracebit cluttered, hindering smooth navigation crucial for a security tool.
  • Users find the difficult navigation due to a cluttered layout, impacting the overall usability of Tracebit.
  • Users experience false positives in alerts, requiring time-consuming manual reviews that hinder efficiency.
  • Users feel that Tracebit has limited features compared to more established products, impacting its attractiveness for enterprise customers.
  • Users find the high learning curve of Tracebit challenging, especially during the initial setup process.

What Are Recent G2 Reviews of Tracebit?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Labyrinth Cyber Deception Platform

Labyrinth Platform changes an attack surface providing adversaries with an illusion of real infrastructure vulnerabilities. Each part of the imitated environment reproduces the services and content of a real network segment. The solution is based on Points - smart imitation hosts that mimic special software services, content, routers, devices, etc. Points detect all malicious activities inside a corporate network providing comprehensive coverage of all the possible attack vectors.

Average Rating: 4.9/5.0

Total Reviews: 15

Who Is the Company Behind Labyrinth Cyber Deception Platform?

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 44% Small, 38% Medium

What Are Recent G2 Reviews of Labyrinth Cyber Deception Platform?

Morphisec

Morphisec fortifies your organization by diminishing the blast radius of attacks, to preemptively reduce the organization’s exposure to cyber risk, pro-actively prevent advanced threats, and ensure optimal anti-ransomware defense. Powered by Automated Moving Target Defense (AMTD), this streamlined solution effortlessly integrates with your current endpoint protection array, enhancing existing protection capabilities or standing strong independently when necessary.

Average Rating: 4.6/5.0

Total Reviews: 12

Who Is the Company Behind Morphisec?

  • Seller: Morphisec
  • Year Founded: 2014
  • HQ Location: Waltham, US
  • Twitter: @morphisec
    2,300 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    99 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 75% Medium, 17% Large

What Do G2 Reviewers Say About Morphisec?

AI-generated summary from verified user reviews

Pros
  • Users value the effective protection of Morphisec, successfully identifying advanced attacks that EDRs overlook.
  • Users value Morphisec for its ability to detection of advanced attacks that traditional EDRs often overlook.
  • Users value the advanced threat protection of Morphisec, effectively catching what EDRs often overlook.

What Are Recent G2 Reviews of Morphisec?

What Are G2 Users Discussing About Morphisec?

CRM Honeypots

CRM Honeypots is a CRM data breach detection tool that helps businesses discover when their contact database has been stolen or leaked. CRM data theft is a widespread but difficult-to-detect problem - stolen contact lists are often used for competitor outreach, spam campaigns, or resold on the black market, and most businesses only discover the breach long after the damage is done. It works by generating realistic-looking decoy contacts ("honeypots") that you plant directly inside your CRM - whether that's Salesforce, HubSpot, Pipedrive, or any other platform. Because these decoy records are indistinguishable from legitimate ones, any unauthorized party who obtains and attempts to use the stolen data will inevitably interact with them. Business value: - Provides early, concrete detection of CRM data theft before it escalates - Delivers actionable evidence, including details about who used the stolen data rather than vague indicators of compromise - Reduces the window between a breach occurring and a team becoming aware of it - Requires minimal technical setup, making it accessible without dedicated security tooling What alerts include: - Sender's email address and company name - IP address and geographic location - Full message content and timestamp Typical users: - Sales operations and revenue operations teams - IT and security staff managing CRM access - Organizations that work with third-party vendors, contractors, or external sales representatives who have access to CRM records How it works: - Decoy contacts are generated in batches and exported as a CSV file - The CSV is imported into any CRM that supports CSV upload, including Salesforce, HubSpot, and most CRM - Once in place, the honeypots require no ongoing maintenance or configuration - When a decoy contact is emailed, an automated alert is triggered immediately

Average Rating: 4.9/5.0

Total Reviews: 5

Who Is the Company Behind CRM Honeypots?

Who Uses This Product?

  • Company Size: 60% Small, 40% Medium

What Are Recent G2 Reviews of CRM Honeypots?

Kilpi Honeypot

Kilpi Honeypot is a fire alarm for your network that instantly alerts you in case of a breach. Honeypots are a common deception tool among cybersecurity experts, but often hard to deploy and maintain. Kilpi Honeypot is designed for IT professionals who handle cybersecurity as a side job allowing anyone to take advantage of this technology. No expertise required – deploy in minutes and protect your business.

Average Rating: 4.9/5.0

Total Reviews: 5

Who Is the Company Behind Kilpi Honeypot?

  • Seller: Kilpi
  • Year Founded: 2022
  • HQ Location: N/A
  • LinkedIn® Page: www.linkedin.com
    2 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 60% Medium, 40% Large

What Are Recent G2 Reviews of Kilpi Honeypot?

8i

Your holograms where you want them

Average Rating: 4.4/5.0

Total Reviews: 4

Who Is the Company Behind 8i?

  • Seller: 8i
  • Year Founded: 2014
  • HQ Location: Los Angeles, US
  • Twitter: @8iReality
    5,267 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    49 employees on LinkedIn®
  • Ownership: NASDAQ: JFKKU

Who Uses This Product?

  • Company Size: 75% Large, 25% Small

What Are Recent G2 Reviews of 8i?

LMNTRIX

LMNTRIX has reimagined cybersecurity, turning the tables in favor of the defenders once again. We have cut out the bloat of SIEM, log analysis and false positives resulting in alert fatigue, and we created new methods for confounding even the most advanced attackers. We believe that in a time of continuous compromise you need continuous response – not incident response. Our approach turns inward and assumes that you’re already breached and that you’re continually going to be breached, so we take a pro-active, offensive, hunting, and adversarial pursuit stance as opposed to a reactive, defensive, legacy stance with analysts staring at a SIEM console wishing they could detect an APT. LMNTRIX Active Defense is a best in class Managed Detection & Response (MDR) service that detects and responds to advanced threats that bypass perimeter controls. We combine deep expertise with cutting-edge technology, leading intelligence, and advanced analytics to detect and investigate threats with great speed, accuracy, and focus. The outcomes we deliver clients are validated breaches that are investigated, contained and remediated. All incidents are aligned to the kill chain and Mitre ATT&CK frameworks and contain detailed investigative actions and recommendations that your organisation follows to protect against the unknown, insider threat and malicious attacker. Active Defense is made up of 3 elements: LMNTRIX GRID (XDR) – This is our cyber defence SaaS platform that provides a new utility model for enterprise security, delivering pervasive visibility, automated threat detection & prevention, threat hunting, investigation, validation and unlimited forensic exploration on-demand and entirely from the cloud. It is a single investigative platform for insights into threats on enterprise, cloud, hybrid, and industrial control systems (ICS) networks. The LMNTRIX Grid delivers unique advantages over current network security solutions. It is a holistic and multi-vector platform with unlimited retention window of full-fidelity network traffic, innovative security visualizations, and the ease and cost-savings of an on-demand deployment model. LMNTRIX Technology Stack –This is our powerful proprietary threat detection stack that is deployed onsite, behind existing controls. It combines multiple threat detection systems, with deceptions everywhere, machine learning, threat intel, correlation, static file analysis, heuristics, and behavior and anomaly detection techniques to find threats in real-time. It decreases alarm fatigue by automatically determining which alerts should be elevated to security events, and reduces false positives by requiring consensus across detection. LMNTRIX Cyber Defense Centers - While these technologies are without peer, what sets us apart from the pack is our team of cybersecurity professionals who continually monitor our clients environments 24x7 while simultaneously hunting threats internally as well as monitoring developments on the deep and dark web. Our CDC's are a global network of cyber defense centers with highly trained and certified intrusion analysts who provide constant vigilance and on-demand analysis of your networks. Our intrusion analysts monitor your networks and endpoints 24x7, applying the latest intelligence and proprietary methodologies to look for signs of compromise. When a potential compromise is detected, the team performs an in- depth analysis on affected systems to confirm the breach. When data theft or lateral movement is imminent, our automated perimeter containment blocks attackers in their tracks while endpoint containment feature makes immediate reaction possible by quarantining affected hosts, whether they are on or off your corporate network, significantly reducing or eliminating the consequences of a breach.

Average Rating: 4.9/5.0

Total Reviews: 10

Who Is the Company Behind LMNTRIX?

  • Seller: LMNTRIX
  • Year Founded: 2015
  • HQ Location: Orange, California
  • Twitter: @lmntrixlabs
    75 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    76 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 60% Medium, 20% Large

What Are Recent G2 Reviews of LMNTRIX?

What Are G2 Users Discussing About LMNTRIX?

SentinelOne Singularity Hologram

Singularity Hologram™ is a network-based identity threat deception solution that lures both external and insider threat actors into revealing themselves. Hologram detects, misdirects, and isolates attackers that have established footholds in-network using decoys of production OSes, applications, and more. By engaging adversaries, you can block attacks, gain attacker intelligence, and build defenses.

Average Rating: 4.2/5.0

Total Reviews: 3

Who Is the Company Behind SentinelOne Singularity Hologram?

  • Seller: SentinelOne
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • Twitter: @SentinelOne
    57,863 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,529 employees on LinkedIn®
  • Ownership: NASDAQ: S

Who Uses This Product?

  • Company Size: 67% Medium, 33% Small

What Are Recent G2 Reviews of SentinelOne Singularity Hologram?

BOTsink

The Attivo BOTsink solution stands guard inside your network, using high-interaction deception and decoy technology to lure attackers into engaging and revealing themselves.

Average Rating: 4.0/5.0

Total Reviews: 2

Who Is the Company Behind BOTsink?

  • Seller: Attivo Networks
  • Year Founded: 2013
  • HQ Location: Mountain View, US
  • Twitter: @AttivoNetworks
    3,653 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,529 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Medium, 50% Large

What Are Recent G2 Reviews of BOTsink?

Minerva Anti-Evasion Platform

A comprehensive endpoint solution that prevents attacks through trickery and deception.

Average Rating: 3.8/5.0

Total Reviews: 2

Who Is the Company Behind Minerva Anti-Evasion Platform?

  • Seller: Minerva Labs
  • Year Founded: 2014
  • HQ Location: Boston, US
  • Twitter: @MinervaLabs
    1,869 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    8,746 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Large, 50% Medium

What Are Recent G2 Reviews of Minerva Anti-Evasion Platform?

What Are G2 Users Discussing About Minerva Anti-Evasion Platform?

FortiDeceptor

FortiDeceptor is a non-intrusive, agentless deception platform designed to detect and neutralize active in-network threats by deploying decoy assets that mimic real network devices. By luring attackers into engaging with these decoys, FortiDeceptor enables early detection and response, effectively disrupting the attack kill chain before significant damage occurs. Key Features and Functionality: - Diverse Decoy Deployment: Supports a wide range of decoy operating systems, including Windows, Linux, SCADA, IoT, VoIP, ERP, Medical, SSL-VPN, and POS, allowing for realistic simulation of various network assets. - Deception Lures: Incorporates services, applications, or user simulations within decoy VMs to create authentic user environments, enhancing the effectiveness of the deception. - Token Distribution: Utilizes tokens—such as fake credentials, database connections, and configuration files—placed on real endpoints to guide attackers toward decoys, increasing the deception surface and influencing lateral movement. - Comprehensive Monitoring: Tracks attacker activities through detailed logging of events, incidents, and campaigns, providing insights into their methods and movements within the network. - Seamless Integration: Integrates with Fortinet Security Fabric and third-party security controls like SIEM, SOAR, EDR, and sandbox solutions to enhance visibility and accelerate response times. Primary Value and Problem Solved: FortiDeceptor addresses the critical need for proactive threat detection and response within networks. By creating a dynamic deception environment, it diverts attackers from sensitive assets, reduces dwell time, and minimizes false positives. This approach not only detects early reconnaissance and lateral movements but also provides detailed forensics and threat intelligence, enabling organizations to stay ahead of both known and unknown cyber threats. Additionally, its agentless design ensures minimal impact on network performance and stability, making it an effective solution for safeguarding IT, OT, and IoT environments.

Average Rating: 4.0/5.0

Total Reviews: 1

Who Is the Company Behind FortiDeceptor?

  • Seller: Fortinet
  • Year Founded: 2000
  • HQ Location: Sunnyvale, CA
  • Twitter: @Fortinet
    151,422 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    16,564 employees on LinkedIn®
  • Ownership: NASDAQ: FTNT

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of FortiDeceptor?

SentinelOne Singularity Identity Detection & Response

Singularity Identity is an identity threat detection and response (ITDR) solution that protects on-premises and cloud-hosted Active Directory domain controllers and domain-joined endpoints in real time. A component of the Singularity Platform, Singularity Identity detects active attacks against all device types and OSes, and safeguards against unauthorized privilege escalation and lateral movement.

Average Rating: 5.0/5.0

Total Reviews: 2

Who Is the Company Behind SentinelOne Singularity Identity Detection & Response?

  • Seller: SentinelOne
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • Twitter: @SentinelOne
    57,863 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,529 employees on LinkedIn®
  • Ownership: NASDAQ: S

Who Uses This Product?

  • Company Size: 50% Medium, 50% Small

What Are Recent G2 Reviews of SentinelOne Singularity Identity Detection & Response?

Smokescreen

Smokescreen is a pioneer in deception-based threat detection and response. It is the solution of choice for offensive security teams, with a customer Net Promoter Score above 70. Smokescreen's deception platform protects many of the world’s most targeted organisations including leading financial institutions, energy companies, manufacturing giants, and technology leaders. It has been recognised by industry influencers like Gartner and SC Magazine and customers alike.

Average Rating: 4.0/5.0

Total Reviews: 1

Who Is the Company Behind Smokescreen?

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of Smokescreen?

What Are G2 Users Discussing About Smokescreen?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 3, 2024