Best AI SOC Agents

How Many AI SOC Agents Products Does G2 Track?

Total Products under this Category: 54

Category Stats (Oct 2026)

  • Average Rating: 4.64/5 (↓0.01 vs Sep 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Hunto AI (+1.58%) - Among all products in this category, Hunto AI recorded the largest rating increase compared to last month

Last updated: October 07, 2026

How Does G2 Rank AI SOC Agents Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,100+ Authentic Reviews
  • 54+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

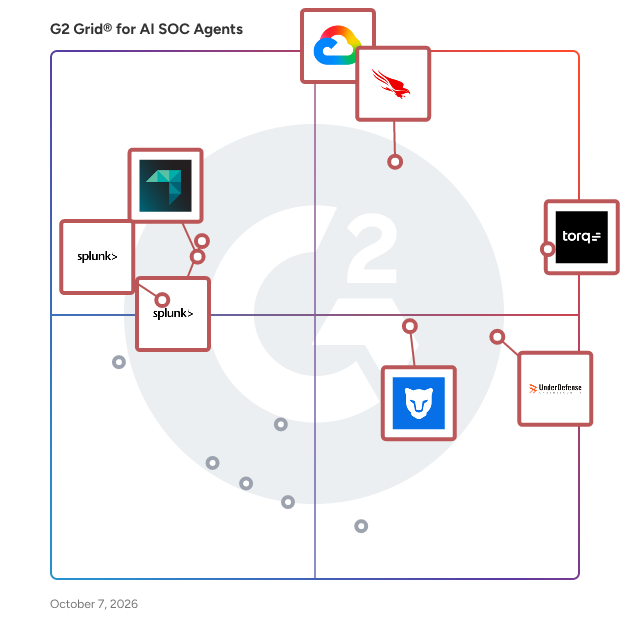
G2 Grid® for AI SOC Agents

G2 Grid® for AI SOC Agents plotting products by satisfaction and market presence

Highlighted products: Google Security Operations, Torq AI SOC Platform, CrowdStrike Charlotte AI, UnderDefense MAXI, Panther, Splunk Enterprise Security, ReliaQuest GreyMatter, and Splunk SOAR (Security Orchestration, Automation and Response).

Underlying data: [Grid® JSON](https://www.g2.com/categories/ai-soc-agents/grids.json?focus%5B%5D=google-security-operations&focus%5B%5D=torq-ai-soc-platform&focus%5B%5D=crowdstrike-charlotte-ai&focus%5B%5D=underdefense-maxi&focus%5B%5D=panther&focus%5B%5D=splunk-enterprise-security&focus%5B%5D=reliaquest-greymatter&focus%5B%5D=splunk-soar-security-orchestration-automation-and-response)

Google Security Operations

Google Security Operations offers a unified experience across SIEM, SOAR, and threat intelligence to drive better detection, investigation, and response. Collect security telemetry data, apply threat intel to identify high priority threats, drive response with playbook automation, case management, and collaboration. It also provides Gemini-native agentic defense to help autonomously handle workflows like alert triage, threat hunting, and detection engineering. Google Security Operations also supports AI Threat Defense to monitor, detect, and respond to threats from code you do not own or cannot patch.

Average Rating: 4.4/5.0

Total Reviews: 144

Who Is the Company Behind Google Security Operations?

  • Seller: Google
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • Twitter: @google
    31,899,995 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG

Who Uses This Product?

  • Who Uses This: Student, Developer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 42% Small, 33% Medium

What Do G2 Reviewers Say About Google Security Operations?

AI-generated summary from verified user reviews

Pros
  • Users value the centralized detection and investigation of Google Security Operations, enhancing efficiency in threat management.
  • Users value the high-level threat detection capabilities of Google Security Operations, enhancing their security response efficiency.
  • Users find Google Security Operations very easy to use, allowing for quick incident analysis and efficient responses.
  • Users value the comprehensive security of Google Security Operations for effectively detecting and responding to threats.
  • Users appreciate the seamless integrations of Google Security Operations, enhancing threat detection and providing a unified security view.
Cons
  • Users find the costly upkeep of Google Security Operations challenging, especially for large organizations.
  • Users often face a steep learning curve with Google Security Operations, especially if unfamiliar with Google Cloud services.
  • Users find the implementation and configuration complex, requiring more time and resources compared to other tools.
  • Users find the learning difficulty of Google Security Operations challenging due to its complex features and setup.
  • Users find limited customization in Google Security Operations hinders adaptability and user experience for specific security needs.

What Are Recent G2 Reviews of Google Security Operations?

Torq AI SOC Platform

Torq is the AI SOC platform that combines agentic insights and automation so that enterprises can triage, investigate, and respond to actual risks, faster. Torq streamlines every step from alert through resolution. The platform analyzes your risk context to identify your biggest threats. Working alongside your SecOps staff, the Torq platform integrates with your security stack to facilitate containment and remediation workflows.

Average Rating: 4.8/5.0

Total Reviews: 151

Who Is the Company Behind Torq AI SOC Platform?

  • Seller: torq
  • Company Website:
  • Year Founded: 2020
  • HQ Location: New York, US
  • Twitter: @torq_io
    1,944 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    470 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 49% Medium, 30% Small

What Do G2 Reviewers Say About Torq AI SOC Platform?

AI-generated summary from verified user reviews

Pros
  • Users praise the ease of use of Torq AI SOC Platform, making it accessible for all skill levels.
  • Users value the efficiency of automated security workflows in Torq, enhancing both speed and effectiveness in threat management.
  • Users value the automation capabilities of Torq AI SOC Platform, enhancing efficiency and streamlining security workflows effectively.
  • Users appreciate the no-code automation capabilities of Torq, streamlining workflows and enhancing overall operational efficiency.
  • Users value the real-time threat detection of Torq AI SOC Platform, enhancing efficiency in responding to security incidents.
Cons
  • Users face a difficult learning curve with Torq AI SOC Platform, requiring significant training and support for effective use.
  • Users face a significant learning curve with Torq AI SOC Platform, requiring time and proper training for effective use.
  • Users note the missing features in Torq AI SOC Platform, especially regarding playbooks and incident management capabilities.
  • Users note that improvement is needed in grouping findings, vendor integration, and overall flexibility for better experience.
  • Users face poor interface design in Torq, including unresponsive buttons and a challenging debugging process.

What Are Recent G2 Reviews of Torq AI SOC Platform?

CrowdStrike Charlotte AI

Charlotte AI is CrowdStrike’s agentic AI security analyst, built to help teams accelerate security outcomes. Combining human expertise and autonomous reasoning, it delivers mission-ready agents that automate time-intensive work (detection triage, malware analysis, etc), embedded genAI features across the Falcon console (chat, command-line explanations, incident summaries, etc), and gives security teams the ability to orchestrate agents with speed and control. Charlotte AI acts as a force multiplier for defenders by reducing manual tasks, streamlining complex workflows, and helping teams scale expertise across the SOC through AI-powered automation and intelligent, context-aware assistance. Work smarter, respond faster and reclaim an operating advantage in the AI era.

Average Rating: 4.4/5.0

Total Reviews: 20

Who Is the Company Behind CrowdStrike Charlotte AI?

  • Seller: CrowdStrike
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • Twitter: @CrowdStrike
    110,809 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®
  • Ownership: NASDAQ: CRWD

Who Uses This Product?

  • Company Size: 52% Medium, 29% Large

What Are Recent G2 Reviews of CrowdStrike Charlotte AI?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

UnderDefense MAXI

UnderDefense is an Agentic AI SOC & Compliance Automation platform trusted by 200+ enterprises in the US and EU. It works on top of the security stack you already own — no rip-and-replace, no added headcount — so your team spends its time on decisions, not triage. ◆ 10+ years of operations with zero ransomware incidents ◆ 250+ integrations across any SIEM, EDR, or cloud stack ◆ 24/7 IR team available whenever you need urgent support WHAT WE OFFER AGENTIC AI SOC UnderDefense Agentic AI SOC works on top of your existing security stack, turning every security team into a machine-speed defense unit without tool replacement or headcount expansion. It takes over the investigative routine that pulls your team away from strategic decisions: enrichment, correlation, triage. ▸ Investigation at Machine Speed: Agentic AI SOC accesses tools, enriches data, and performs deep cross-environment investigations at machine speed. It correlates, triages, and forms conclusions, offloading all repetitive work from your team. ▸ 2 Minutes Per Alert: Complete SIEM queries, threat intel checks, and cross-system correlations in 2 minutes. Every step fully observable and auditable. ▸ Human at Every Decision Point: The platform verifies suspicious activity with end-users via Slack or Teams, then routes containment decisions to your team or our 24/7 IR experts. COMPLIANCE AUTOMATION Stop chasing spreadsheets. UnderDefense MAXI Compliance AI automatically collects continuous evidence across ISO 27001, SOC 2, PCI DSS, GDPR, and HIPAA, and publishes your live posture through a shareable Trust Center link. ▸ 40% audit-ready in the first 40 minutes ▸ 2X faster time-to-compliance vs. traditional audit ▸ 24/7 continuous monitoring — posture always current, not point-in-time WHY WE ARE BETTER ✓ No rip-and-replace: Works with your current SIEM (Splunk, Sentinel, Chronicle, QRadar, Elastic), EDR, and cloud tools. Logs stay in your data lake. ✓ True Multi-Environment Coverage: Comprehensive visibility across on-premises, cloud (AWS, GCP, Azure), SaaS, network, identity, and OT/SCADA environments. ✓ The Only Agentic AI SOC with on-prem deployment: Full AI SOC inside your own infrastructure. No telemetry leaving your environment. Air-gapped available. ✓ Right-Sized for Any Enterprise: Detection engineering and support tailored to your organization, not a one-size-fits-all template. Start your free trial at underdefense.com

Average Rating: 4.9/5.0

Total Reviews: 56

Who Is the Company Behind UnderDefense MAXI?

  • Seller: UnderDefense
  • Year Founded: 2017
  • HQ Location: New York, NY
  • Twitter: @underdefense
    153 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    133 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO
  • Top Industries: Marketing and Advertising, Information Technology and Services
  • Company Size: 47% Small, 46% Medium

What Do G2 Reviewers Say About UnderDefense MAXI?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the visibility provided by UnderDefense MAXI, allowing them to focus on relevant security alerts effectively.
  • Users commend UnderDefense MAXI for its outstanding customer support, ensuring rapid responses and clear guidance throughout their cybersecurity needs.
  • Users appreciate the expert cybersecurity support from UnderDefense MAXI, enhancing their security posture and alert management.
  • Users commend the accuracy of information provided by UnderDefense MAXI, enhancing their security management and decision-making.
  • Users value the exceptional issue resolution by UnderDefense, enhancing security management with quick and effective solutions.
Cons
  • Users desire more automation in UnderDefense MAXI, seeking greater control over the dashboard and updates.
  • Users desire more control over the dashboard and automated updates for a better experience with UnderDefense MAXI.
  • Users note the limited integration requiring extra setup time, which can be a hurdle for new users.
  • Users note the setup difficulty requiring time and effort to properly integrate tools before full functionality can be enjoyed.

What Are Recent G2 Reviews of UnderDefense MAXI?

Panther

Panther is the AI SOC Platform that scales security expertise by embedding AI agents across your security operations with native access to your data lake, detection logic, and organizational knowledge. Unlike bolt-on tools, Panther's closed-loop architecture turns every alert into compounding intelligence that makes the system smarter over time. Request a demo today at: https://panther.com/product/request-a-demo/

Average Rating: 4.7/5.0

Total Reviews: 49

Who Is the Company Behind Panther?

  • Seller: Panther Labs
  • Year Founded: 2018
  • HQ Location: San Francisco, CA
  • Twitter: @runpanther
    4,437 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    269 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Senior Security Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 53% Medium, 29% Large

What Do G2 Reviewers Say About Panther?

AI-generated summary from verified user reviews

Pros
  • Users praise Panther's responsive customer support, which delivers expert assistance and resolves issues quickly and efficiently.
  • Users laud Panther's detection efficiency, appreciating its swift JSON parsing and robust, adaptable detection capabilities.
  • Users value Panther's ease of use, noting its intuitive interface and efficient operation for small teams.
  • Users praise Panther's intuitive interface and responsive support, enhancing ease of use and effectiveness for security teams.
  • Users praise the easy log source integration in Panther, simplifying onboarding and enhancing their security monitoring efforts.
Cons
  • Users find the raw log view limited due to lack of summaries, customization options, and cumbersome configuration for alerts.
  • Users face complex configuration challenges with Panther's setup, needing significant custom workflow adjustments and improvements.
  • Users find the dashboard issues overwhelming, highlighting limitations in customization and functionality that hinder effective use.
  • Users find Panther's limited access cumbersome, with challenges in integration, dashboards, and customizable alert features.
  • Users note a difficult learning curve for Panther, especially for those not familiar with programming languages.

What Are Recent G2 Reviews of Panther?

What Are G2 Users Discussing About Panther?

Splunk Enterprise Security

Splunk Enterprise Security (ES) is a data-centric, modern security information and event management (SIEM) solution that delivers data-driven insights for full breadth visibility into your security posture so you can protect your business and mitigate risk at scale. With unparalleled search and reporting, advanced analytics, integrated intelligence, and prepackaged security content, Splunk ES accelerates threat detection and investigation, letting you determine the scope of high-priority threats to your environment so you can quickly take action. Built on an open and scalable data platform, you can stay agile in the face of evolving threats and business needs. Our extensive ecosystem of Splunk, partner, and community-built integrations as well as flexible deployment options ensure your technology investments are working in tandem with Splunk ES whilst meeting you wherever you are on your cloud, multi-cloud, or hybrid journey.

Average Rating: 4.3/5.0

Total Reviews: 224

Who Is the Company Behind Splunk Enterprise Security?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • Twitter: @Cisco
    720,366 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 59% Large, 30% Medium

What Do G2 Reviewers Say About Splunk Enterprise Security?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Splunk Enterprise Security, enhancing their monitoring and log management experience.
  • Users appreciate the easy integrations of Splunk Enterprise Security, enabling seamless connection with various platforms and systems.
  • Users highlight the impressive threat detection capabilities of Splunk Enterprise Security, enhancing security focus and reducing false alarms.
  • Users value the effective features of Splunk Enterprise Security, enhancing security analysis with comprehensive logs and insights.
  • Users appreciate the user-friendly interface of Splunk Enterprise Security, enabling efficient monitoring and attractive dashboards.
Cons
  • Users find the high costs associated with data ingestion to be a significant drawback of Splunk Enterprise Security.
  • Users find the initial implementation complex, needing expert resources and time to onboard Splunk Enterprise Security effectively.
  • Users find the complex implementation of Splunk Enterprise Security challenging, requiring extensive expertise and resources.
  • Users find the complex setup of Splunk Enterprise Security time-consuming and challenging, impacting initial deployment effectiveness.
  • Users find the difficult learning curve of Splunk Enterprise Security challenging, especially for those new to data analysis.

What Are Recent G2 Reviews of Splunk Enterprise Security?

What Are G2 Users Discussing About Splunk Enterprise Security?

ReliaQuest GreyMatter

ReliaQuest’s agentic AI security operations platform, GreyMatter, allows security teams to detect threats at the source, contain them in under 5 minutes, and eliminate Tier 1 and Tier 2 work for faster investigation and response. GreyMatter orchestrates 6 agentic AI personas with 200+ agent skills and 400+ AI tools to exponentially scale security operations and help organizations predict what's next.

Average Rating: 4.7/5.0

Total Reviews: 20

Who Is the Company Behind ReliaQuest GreyMatter?

  • Seller: ReliaQuest
  • Company Website:
  • Year Founded: 2007
  • HQ Location: Tampa, Florida, United States
  • Twitter: @ReliaQuest
    2,577 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,106 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Consumer Services
  • Company Size: 40% Medium, 25% Small

What Do G2 Reviewers Say About ReliaQuest GreyMatter?

AI-generated summary from verified user reviews

Pros
  • Users value the exceptional visibility and integration capabilities of ReliaQuest GreyMatter, enhancing security operations across environments.
  • Users value the centralized management of ReliaQuest GreyMatter, enhancing visibility and streamlining security operations effectively.
  • Users highlight the exceptional customer support of ReliaQuest GreyMatter, enhancing satisfaction and streamlining security operations.
  • Users praise the ease of use of ReliaQuest GreyMatter, highlighting its straightforward setup and seamless integrations.
  • Users highlight the seamless integration with existing tools, streamlining security operations and enhancing overall efficiency.
Cons
  • Users note UX improvement needs in ReliaQuest GreyMatter, citing alert delays, slow report loading, and clunky Android app experience.
  • Users find the complexity of configurations in ReliaQuest GreyMatter can hinder usability and require significant fine-tuning.
  • Users experience an inefficient alert system with delays, duplicates, and slow report loading, affecting overall usability.
  • Users find the learning curve steep for advanced workflows, though documentation and support help eventually.
  • Users find login issues with the ReliaQuest GreyMatter app, particularly on Android, making the sign-in process frustrating.

What Are Recent G2 Reviews of ReliaQuest GreyMatter?

Splunk SOAR (Security Orchestration, Automation and Response)

Splunk SOAR provides security orchestration, automation and response capabilities that allow security analysts to work smarter by automating repetitive tasks; respond to security incidents faster with automated detection, investigation, and response; increase productivity, efficiency and accuracy; and strengthen defenses by connecting and coordinating complex workflows across their team and tools. Splunk SOAR also supports a broad range of security operations center (SOC) functions including event and case management, integrated threat intelligence, collaboration tools and reporting.

Average Rating: 4.4/5.0

Total Reviews: 39

Who Is the Company Behind Splunk SOAR (Security Orchestration, Automation and Response)?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • Twitter: @Cisco
    720,366 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO

Who Uses This Product?

  • Top Industries: Information Technology and Services, Consulting
  • Company Size: 43% Medium, 35% Large

What Do G2 Reviewers Say About Splunk SOAR (Security Orchestration, Automation and Response)?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the automation capabilities of Splunk SOAR, enabling efficient threat detection and response with minimal human error.
  • Users value the end-to-end security management of Splunk SOAR, enhancing incident response and threat detection efficiency.
  • Users appreciate the flexibility and integration capabilities of Splunk SOAR for tailoring security workflows to their needs.
  • Users commend the easy threat detection and analysis capabilities, enhancing security response with flexible workflows.
  • Users appreciate the ease of use in Splunk SOAR, benefiting from a user-friendly interface and seamless integrations.
Cons
  • Users find Splunk SOAR expensive, making it difficult for normal users to afford and implement effectively.
  • Users find the learning curve steep for Splunk SOAR, requiring extensive knowledge and training for effective use.
  • Users find the difficult learning curve of Splunk SOAR challenging, especially for beginners and new users of automation tools.
  • Users find the software's complexity challenging to navigate, particularly for beginners needing extensive training.
  • Users find the poor interface design of Splunk SOAR challenging, particularly for beginners navigating its features.

What Are Recent G2 Reviews of Splunk SOAR (Security Orchestration, Automation and Response)?

What Are G2 Users Discussing About Splunk SOAR (Security Orchestration, Automation and Response)?

Simbian

Simbian is self-improving defense: one product that takes your objective, does the security work, and measures itself against the result. It started as an AI SOC Agent and now covers the full SecOps lifecycle, so every investigation, hunt, pentest, and new detection runs on the same reasoning and the same context. Attackers now build a new exploit for every target and use it once. There is no signature to match, no playbook to run, and no patch to have applied, which is why adding analysts stops helping and why playbook-based SOC automation breaks on the first attack nobody has seen before. You give Simbian an objective (investigate every CrowdStrike alert to a verdict, close every path into the payment environment) and it decides which of its Agents to put on the problem, reads evidence from more than 100 of the tools you already run, acts back into those same controls, and scores itself against the objective you set. What it learns about your environment stays in a Context Lake™ private to you. Where it falls short, it proposes a change to its own skills and context, shows you the evidence, and applies it once you approve. Five Agents, one product: AI SOC Agent, AI Pentest Agent, AI Threat Hunt Agent, AI Detection Engineering Agent, and AI NetSecOps Agent. Adding a discipline is an Agent specification, not another tool to integrate. Across 300+ enterprise environments in production, Simbian investigates and responds to every threat, averaging under four minutes from detection to response. 95% of the responses it proposes are approved by the customer's own analysts, their call not ours, and in the other 5% it comes back with context that makes the next response better. Any action can require sign-off before it runs. Deploys in days as SaaS, private cloud, on-premises, or fully air-gapped. Bring your own key, bring your own model. Simbian is never trained on your data: we train it in a war lab against attacks we author and grade ourselves, and we publish what we find as the Cyber Defense Benchmark.

Average Rating: 4.6/5.0

Total Reviews: 13

Who Is the Company Behind Simbian?

  • Seller: Simbian
  • Year Founded: 2023
  • HQ Location: Mountain View, US
  • LinkedIn® Page: www.linkedin.com
    68 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 47% Small, 33% Medium

What Are Recent G2 Reviews of Simbian?

Wirespeed

Lighting-fast automated detection & response (ADR) that helps stop threats in seconds. Wirespeed Automated Detection & Response uses automation to analyze alerts in milliseconds and contain threats before they can spread, only escalating critical cases that require your expertise. It’s an evolution of MDR designed to stand up to today’s machine-speed threats. It’s deployable in a few clicks and works seamlessly with your existing security stack.

Average Rating: 5.0/5.0

Total Reviews: 11

Who Is the Company Behind Wirespeed?

Who Uses This Product?

  • Company Size: 55% Medium, 45% Small

What Do G2 Reviewers Say About Wirespeed?

AI-generated summary from verified user reviews

Pros
  • Users commend Wirespeed for its continuous monitoring, enhancing security with efficient alerts and real-time responsiveness.
  • Users highlight the easy integrations of Wirespeed, enabling quick setup and efficient threat monitoring seamlessly.
  • Users find Wirespeed to have exceptional ease of use, with seamless integration and user-friendly features enhancing their experience.
  • Users value the timely and relevant alerts from Wirespeed, enhancing their ability to respond to threats quickly.
  • Users commend Wirespeed for its exceptional customer support, with fast responses from real people enhancing their experience.

What Are Recent G2 Reviews of Wirespeed?

Blink

Automate Everything Security in the Blink of AI Blink is a security workflow automation platform designed to make building, collaborating, and scaling all things security & beyond effortless using generative AI. Whether you prefer code, low-code, or no-code, Blink has got you covered. Easily drag and drop the actions you want into a workflow, leveraging the over 30,000 integrations available in the automation library, or use Blink Copilot to generate a workflow with a natural language prompt. Use Blink as an automation hub, where security teams go to quickly develop, collaborate, and automate their security ideas. Leverage the platform’s 10,000+ workflows that come out of the box to quickly build workflows for real-time remediation. Generate automation workflows for standalone use cases or build an end-to-end proactive automation strategy, streamlining security responses across your entire organization.

Average Rating: 4.7/5.0

Total Reviews: 19

Who Is the Company Behind Blink?

  • Seller: Blink Ops
  • Company Website:
  • Year Founded: 2021
  • HQ Location: Austin, US
  • Twitter: @getBlinkOps
    706 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    126 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software
  • Company Size: 63% Medium, 21% Large

What Do G2 Reviewers Say About Blink?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Blink, enabling quick setup and a satisfying overall experience.
  • Users value the powerful automation and strong support of Blink, leading to effective security outcomes quickly.
  • Users value the excellent customer support of Blink, enhancing their experience and ensuring product effectiveness.
  • Users appreciate the easy setup of Blink, enabling quick and seamless initiation with the software.
  • Users find Blink's seamless JavaScript integration and quick setup invaluable for efficient web project execution.
Cons
  • Users find Blink's limited extensibility problematic for large projects, affecting adaptability across different departments.
  • Users find Blink's limited extensibility problematic, particularly for large and complex projects, hindering productivity.

What Are Recent G2 Reviews of Blink?

Hunto AI

Hunto AI is an agentic, 100% autonomous platform purpose-built for monitoring and quantifying your external threats. We proactively monitor external assets, detect real-world brand impersonation and fraud infrastructure, and execute rapid takedowns, while mapping every finding to audit-ready proof. - CTOs get measurable breach-probability reduction and time-to-mitigation SLAs. - CEOs/CMOs get brand-abuse suppression and revenue protection. - Compliance gets reports your auditors actually accept. Hunto AI offers a live, quantified view of exposure, external risk, and the fastest path to fix.

Average Rating: 4.8/5.0

Total Reviews: 16

Who Is the Company Behind Hunto AI?

  • Seller: Hunto AI
  • Year Founded: 2023
  • HQ Location: Melbourne, AU
  • LinkedIn® Page: www.linkedin.com
    14 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 50% Medium, 44% Small

What Do G2 Reviewers Say About Hunto AI?

AI-generated summary from verified user reviews

Pros
  • Users value the continuous monitoring by Hunto AI, appreciating its seamless integration for robust threat management.
  • Users value the seamless automation in Hunto AI, effectively enhancing threat detection and incident response efficiency.
  • Users value the proactive risk identification and automation features of Hunto AI, enhancing security management efficiency.
  • Users value the comprehensive integration of security features in Hunto AI, enhancing overall cyber resilience and efficiency.
  • Users commend Hunto AI for its quick threat detection, enhancing security and reducing human cyber risk effectively.
Cons
  • Users desire greater automation capabilities in Hunto AI to enhance efficiency and simplify their workflow.
  • Users desire more automation in Hunto AI to enhance efficiency and streamline their tasks.
  • Users believe that the few modules of Hunto AI could significantly improve with added risk scoring features.

What Are Recent G2 Reviews of Hunto AI?

Swimlane

Swimlane automates the work security teams hate. As the leader in agentic AI security automation, Swimlane unifies operations across the SOC and beyond with its platform, Swimlane Turbine. The problem is real: over three million SecOps roles sit unfilled, and analysts drown in alerts while juggling 30+ disconnected tools, each with its own schema and quirks. Meanwhile, the average breach now costs $4.5 million. Swimlane closes that gap. Swimlane Hero AI, embedded within the Turbine platform, turns natural-language prompts into automated investigations and responses, cutting MTTR by 75%. Analysts trigger remediation with one click, backed by NIST-aligned case management. Turbine Canvas lets teams build playbooks and agents with no, low, or full code, so automation doesn't wait on a developer's calendar. The Swimlane Marketplace adds a growing library of agents, integrations, and playbooks, built on demand at no cost, ending vendor lock-in for good. Under the hood, Swimlane's Active Sensing Fabric ingests data at scale, pushing capability beyond traditional SOAR. Cloud-native architecture backs it up: one customer runs 25 million automated actions a day at 75,000 actions per minute. That's not a demo number. That's production. Analysts get customizable dashboards and AI-augmented reporting that turn raw activity into KPIs executives actually read, proving ROI without a translation layer. The market has taken notice. Independent evaluations against 15+ competitors all point the same direction: Swimlane leads. Inc. named it Best in Business. Customers at Northern Power, Toshiba, Weedmaps, and InComm Payments back that up, citing customizable playbooks, dashboards, and a professional services team that shows up when it counts. Swimlane doesn't just orchestrate security tasks. It gives every security function, from vulnerability management to compliance to business continuity, a way to move faster than the threats they're chasing.

Average Rating: 4.5/5.0

Total Reviews: 45

Who Is the Company Behind Swimlane?

  • Seller: Swimlane
  • Year Founded: 2014
  • HQ Location: Boulder, US
  • Twitter: @swimlane
    1,628 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    271 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 60% Medium, 31% Small

What Do G2 Reviewers Say About Swimlane?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Swimlane, appreciating its low-code automation and seamless integration capabilities.
  • Users appreciate the easy integrations of Swimlane, enhancing their playbooks with fast and robust connectivity options.
  • Users appreciate the personalization and robust integration features of Swimlane, enhancing usability and flexibility in security management.
  • Users value the seamless integrations of Swimlane, enhancing playbook creation and collaboration across various technologies.
  • Users value the flexibility of low-code automation in Swimlane, enabling extensive opportunities for security operations enhancements.
Cons
  • Users find Swimlane complex to set up and maintain, but support is timely and helpful in overcoming challenges.
  • Users find the learning curve steep initially with Swimlane, requiring time to become comfortable and proficient.
  • Users find the limited resources available for Swimlane challenging, particularly during initial deployment and playbook design.
  • Users report poor customer support, with slow responses and challenges in diagnosing upgrade issues.
  • Users find Swimlane's poor interface design cluttered and difficult to navigate, requiring a more modern refresh.

What Are Recent G2 Reviews of Swimlane?

What Are G2 Users Discussing About Swimlane?

Intezer

Intezer automates the entire alert triage process, like an extension of your team handling Tier 1 SOC tasks for every alert at machine-speed. Intezer monitors incoming incidents from endpoint, reported phishing pipelines, or SIEM tools, then autonomously collects evidence, investigates, makes triage decisions, and escalates only the serious threats to your team for human intervention. Power your SOC with artificial intelligence that makes sure every alert is deeply analyzed (including every single artifact like files, URLs, endpoint memory, etc.), detecting malicious code in memory and other evasive threats. Fast set up and integrations with your SOC team's workflows (EDR, SOAR, SIEM, etc.) means Intezer's AI can immediately start filtering out false positives, giving you detailed analysis about every threat, and speeding up your incident response time. With Intezer: • Reduce Tier 1 escalation, sending only 4% of alerts on average to your team for immediate action. • Identify up to 97% of false positive alerts without taking any time from your analysts. • Reduce average triage time to 5 minutes or less, while giving your analysts deep context about every alert to prioritize critical treats and respond faster.

Average Rating: 4.5/5.0

Total Reviews: 187

Who Is the Company Behind Intezer?

  • Seller: Intezer
  • Year Founded: 2015
  • HQ Location: New York
  • Twitter: @IntezerLabs
    10,170 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    88 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Student
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 54% Small, 23% Medium

What Do G2 Reviewers Say About Intezer?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the robust security features of Intezer, ensuring timely detection and blocking of malware.
  • Users value the effective malware detection and security features of Intezer that enhance system protection.
  • Users value Intezer for its effective malware detection and response capabilities, enhancing overall security and incident management.
  • Users value the high detection accuracy of Intezer, ensuring timely malware detection and enhanced system security.
  • Users appreciate the ease of use of Intezer, making malware detection and incident response straightforward and efficient.
Cons
  • Users feel the inability to control file visibility limits their privacy and management options in certain situations.
  • Users report complex interface issues with Intezer, making navigation challenging and less intuitive.
  • Users are concerned about limited file visibility control, which may impact their data privacy and access management.
  • Users find the difficult navigation of Intezer frustrating, with a less-than-ideal UI and small text affecting readability.
  • Users find the expensive pricing of Intezer problematic, especially with the limited free tier and some GUI issues.

What Are Recent G2 Reviews of Intezer?

What Are G2 Users Discussing About Intezer?

SIRP

SIRP is an AI-native Autonomous SOC platform designed to evolve traditional Security Orchestration, Automation, and Response (SOAR) into governed, decision-driven security operations. Unlike legacy SOAR tools that rely on static playbooks and workflow automation, SIRP enables intelligent AI agents to analyze alerts, compute risk, execute response actions, and continuously learn from outcomes within defined policy boundaries. The platform combines contextual reasoning, real-time intelligence, and adaptive learning to reduce manual triage, minimize alert fatigue, and accelerate incident response while maintaining governance, auditability, and control. SIRP supports enterprise SOC teams and MSSPs seeking to operate at machine speed without sacrificing human oversight for high-impact decisions.

Average Rating: 4.7/5.0

Total Reviews: 22

Who Is the Company Behind SIRP?

  • Seller: SIRP
  • Year Founded: 2017
  • HQ Location: Bethesda, Maryland
  • Twitter: @sirp_io
    74 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    55 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 41% Small, 37% Medium

What Do G2 Reviewers Say About SIRP?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the comprehensive automation features of SIRP, enhancing their security orchestration and incident management efficiency.
  • Users value the excellent customer support from SIRP, enhancing their overall experience with the product.
  • Users praise SIRP for its ease of use, making security automation and incident management seamless and efficient.
  • Users value the easy integrations offered by SIRP, enhancing their security automation and orchestration experience.
  • Users praise SIRP for its ease of use and excellent support, along with comprehensive security features and integrations.

What Are Recent G2 Reviews of SIRP?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated April 9, 2026