Best Threat Intelligence Software for Small Business

How Many Threat Intelligence Software Products Does G2 Track?

Total Products under this Category: 295

Category Stats (Nov 2026)

  • Average Rating: 4.59/5 (↑0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Darktrace / EMAIL (+0.63%) - Among all products in this category, Darktrace / EMAIL recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Threat Intelligence Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 9,300+ Authentic Reviews
  • 295+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

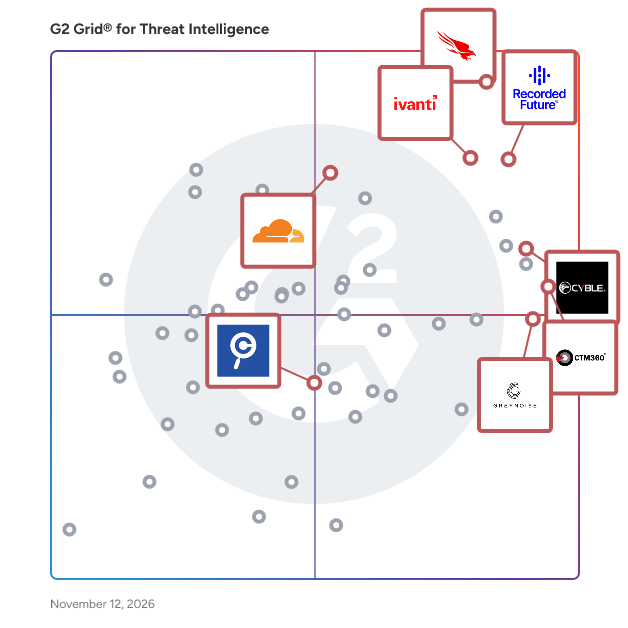
G2 Grid® for Threat Intelligence Software

G2 Grid® for Threat Intelligence Software plotting products by satisfaction and market presence

Highlighted products: Ivanti Autonomous Endpoint Management, CrowdStrike Falcon Endpoint Protection Platform, Recorded Future, Cloudflare Application Security and Performance, CTM360, GreyNoise, Cyble, and Criminal IP.

Underlying data: [Grid® JSON](https://www.g2.com/categories/threat-intelligence/grids.json?focus%5B%5D=ivanti-autonomous-endpoint-management&focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=recorded-future&focus%5B%5D=cloudflare-application-security-and-performance&focus%5B%5D=ctm360-ctm360&focus%5B%5D=greynoise&focus%5B%5D=cyble&focus%5B%5D=criminal-ip-criminal-ip&segment=small-business)

Ivanti Autonomous Endpoint Management

Ivanti Autonomous Endpoint Management is a software designed to automate and simplify the management of devices throughout their lifecycle. The software provides capabilities for endpoint discovery, configuration, security, monitoring, and remediation across various platforms, including Windows, macOS, Linux, and mobile devices. It enables organizations to reduce manual IT workloads by leveraging automation for patch management, software distribution, compliance enforcement, and device provisioning. The software also offers insights into device health and usage, helping businesses address vulnerabilities, ensure policy adherence, and maintain endpoint performance while supporting remote and hybrid work environments. Ivanti Autonomous Endpoint Management aims to improve operational efficiency by centralizing endpoint administration and minimizing risks associated with unmanaged or unpatched devices.

Average Rating: 4.3/5.0

Total Reviews: 410

How Do G2 Users Rate Ivanti Autonomous Endpoint Management?

  • Ease of Use: 8.3/10 (Category avg: 9.1/10)

Who Is the Company Behind Ivanti Autonomous Endpoint Management?

  • Seller: Ivanti
  • Company Website:
  • Year Founded: 1985
  • HQ Location: South Jordan, UT
  • LinkedIn® Page: www.linkedin.com
    3,026 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 45% Large, 34% Medium

What Do G2 Reviewers Say About Ivanti Autonomous Endpoint Management?

AI-generated summary from verified user reviews

Pros
  • Users value the strong automation features of Ivanti, which simplify patching and improve system management efficiency.
  • Users value the automation and intelligence features of Ivanti for enhancing efficiency and proactive issue management.
  • Users value the strong automation and self-healing features of Ivanti, enhancing efficiency and device management visibility.
  • Users value the access ease of Ivanti Autonomous Endpoint Management, simplifying integration across various operating systems effortlessly.
  • Users value the reliable Apple device management that prevents locked phones and enhances functionality through easy implementation.
Cons
  • Users experience communication delays, particularly in support responsiveness, impacting troubleshooting during critical updates.
  • Users experience feature issues with a cluttered UI, slow performance, and challenging setup and customization processes.
  • Users find the UI cluttered and non-intuitive, making navigation and access to tools frustrating and inefficient.
  • Users experience slow performance with Ivanti when managing large device counts, impacting efficiency during tasks.
  • Users find the complexity of Ivanti Autonomous Endpoint Management challenging due to a steep learning curve and cluttered UI.

What Are Recent G2 Reviews of Ivanti Autonomous Endpoint Management?

What Are G2 Users Discussing About Ivanti Autonomous Endpoint Management?

CrowdStrike Falcon Endpoint Protection Platform

Organizations today face a serious challenge: managing numerous security vendors and tools while confronting an ever-evolving threat landscape. Sophisticated adversaries are becoming smarter, faster, and more evasive, launching complex attacks that can strike in minutes or even seconds. Traditional security approaches struggle to keep pace, leaving businesses vulnerable. The CrowdStrike Falcon Platform addresses this by offering a unified, cloud-native solution. It consolidates previously siloed security solutions and incorporates third-party data into a single platform with one efficient and resource-conscious agent, leveraging advanced AI and real-time threat intelligence. This approach simplifies security operations, speeds analyst decision making, and enhances protection to stop the breach, allowing organizations to reduce risk with less complexity and lower costs. CrowdStrike's Falcon Platform includes: - Endpoint Security: Secure the endpoint, stop the breach - Identify Protection: Identity is the front line, defend it - Next-Gen SIEM: The future of SIEM, today - Data Protection: Real-time data protection from endpoint to cloud - Exposure Management: Understand risk to stop breaches - Charlotte AI: Powering the next evolution of the SOC

Average Rating: 4.7/5.0

Total Reviews: 642

How Do G2 Users Rate CrowdStrike Falcon Endpoint Protection Platform?

  • Security Validation: 9.4/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.4/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 9.1/10)

Who Is the Company Behind CrowdStrike Falcon Endpoint Protection Platform?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®
  • Ownership: NASDAQ: CRWD

Who Uses This Product?

  • Who Uses This: Security Engineer, Security Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 49% Large, 37% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Endpoint Protection Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the cloud-native architecture and effective features like workflow automation and asset management in CrowdStrike Falcon.
  • Users value the advanced threat detection capabilities of CrowdStrike Falcon, enhancing security and streamlining response efforts.
  • Users value the ease of use of CrowdStrike Falcon, benefiting from its lightweight agent and intuitive interface.
  • Users appreciate the robust security features of CrowdStrike Falcon, enhancing endpoint protection and system performance.
  • Users praise the superior detection capabilities of CrowdStrike Falcon, consistently delivering reliable and swift responses.
Cons
  • Users find that CrowdStrike Falcon's high licensing cost can be burdensome, particularly for smaller teams and organizations.
  • Users express frustration over the complexity of CrowdStrike Falcon's management console and its steep learning curve.
  • Users find the steep learning curve of CrowdStrike Falcon challenging due to its complex management console.
  • Users face limited functionality in adding hash values to CrowdStrike Falcon, which restricts monitoring capabilities.
  • Users express concern over the high pricing of CrowdStrike Falcon, especially for smaller organizations.

What Are Recent G2 Reviews of CrowdStrike Falcon Endpoint Protection Platform?

What Are G2 Users Discussing About CrowdStrike Falcon Endpoint Protection Platform?

Recorded Future

Recorded Future is the world’s largest threat intelligence company. Recorded Future’s Intelligence Cloud provides end-to-end intelligence across adversaries, infrastructure, and targets. Indexing the internet across the open web, dark web, and technical sources, Recorded Future provides real-time visibility into an expanding attack surface and threat landscape, empowering clients to act with speed and confidence to reduce risk and securely drive business forward. Headquartered in Boston with offices and employees around the world, Recorded Future works with over 1,900 businesses and government organizations across 80 countries to provide real-time, unbiased and actionable intelligence. Learn more at recordedfuture.com.

Average Rating: 4.5/5.0

Total Reviews: 251

How Do G2 Users Rate Recorded Future?

  • Security Validation: 8.2/10 (Category avg: 9.1/10)
  • Intelligence Reports: 8.8/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 7.8/10 (Category avg: 8.7/10)
  • Ease of Use: 8.4/10 (Category avg: 9.1/10)

Who Is the Company Behind Recorded Future?

  • Seller: Recorded Future
  • Company Website:
  • Year Founded: 2009
  • HQ Location: Somerville, US
  • LinkedIn® Page: www.linkedin.com
    1,150 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Cyber Threat Intelligence Analyst, Threat Intelligence Analyst
  • Top Industries: Financial Services, Computer & Network Security
  • Company Size: 61% Large, 21% Medium

What Do G2 Reviewers Say About Recorded Future?

AI-generated summary from verified user reviews

Pros
  • Users find Recorded Future to be easy to use, with a smooth setup and helpful support throughout the process.
  • Users appreciate the impressive API connectivity and diverse threat intelligence sources of Recorded Future, enhancing workflow automation.
  • Users value the world-class threat intelligence of Recorded Future, benefiting from comprehensive insights and automation capabilities.
  • Users value the world-class threat detection of Recorded Future, leveraging diverse intelligence for enhanced security insights.
  • Users commend the world-class threat intelligence of Recorded Future, providing deep and valuable insights for cybersecurity professionals.
Cons
  • Users find the complexity of Recorded Future overwhelming initially, requiring significant time to learn and adapt.
  • Users feel the product is expensive, with licensing limitations affecting overall usability and access to necessary features.
  • Users find the learning curve steep, requiring significant time and training to effectively utilize Recorded Future's features.
  • Users find the insufficient information in Recorded Future limits the product's effectiveness and context for breaches.
  • Users find the difficult learning curve for Recorded Future challenging, especially for those new to the platform.

What Are Recent G2 Reviews of Recorded Future?

What Are G2 Users Discussing About Recorded Future?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

GreyNoise

GreyNoise provides security teams with real-time, verifiable perimeter threat intelligence. We observe and analyze both global and targeted internet scanning and exploitation traffic, and make this intelligence available to customers in real-time. This allows security teams to improve the efficiency of their SOC, perform threat hunting campaigns, and focus on critical threats to their network.

Average Rating: 4.8/5.0

Total Reviews: 128

How Do G2 Users Rate GreyNoise?

  • Security Validation: 9.1/10 (Category avg: 9.1/10)
  • Intelligence Reports: 8.7/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.0/10 (Category avg: 8.7/10)
  • Ease of Use: 9.6/10 (Category avg: 9.1/10)

Who Is the Company Behind GreyNoise?

  • Seller: GreyNoise
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Washington, D.C.
  • LinkedIn® Page: www.linkedin.com
    64 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Network Engineer
  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 70% Medium, 34% Small

What Do G2 Reviewers Say About GreyNoise?

AI-generated summary from verified user reviews

Pros
  • Users find GreyNoise incredibly easy to use, simplifying network monitoring and enhancing their ability to track unusual traffic.
  • Users value the automation of vulnerability scans in GreyNoise, enhancing security and prioritizing critical threats effortlessly.
  • Users value the strong visibility and detailed analysis provided by GreyNoise, enhancing security and simplifying threat assessments.
  • Users value the accurate threat detection of GreyNoise, enabling informed decisions and effective vulnerability management.
  • Users value the alert system of GreyNoise, enhancing their understanding of network traffic and improving security measures.
Cons
  • Users experience slow loading times with GreyNoise, particularly when running multiple IP lookups in succession.
  • Users experience dashboard issues, including shallow historical views and confusion navigating UI and reports, affecting productivity.
  • Users experience integration issues with GreyNoise, requiring extra effort to mesh with existing security tools and workflows.
  • Users find the navigation issues in GreyNoise cumbersome, often requiring extra clicks and leading to inefficiencies.
  • Users find the inefficient alert system limits flexibility and increases configuration workload for threat notifications.

What Are Recent G2 Reviews of GreyNoise?

CTM360

CTM360 is a consolidated external security platform that integrates External Attack Surface Management, Digital Risk Protection, Cyber Threat Intelligence, Brand Protection & Anti-phishing, Surface, Deep, & Dark Web Monitoring, Security Ratings, Third-party risk Management, and fully managed unlimited Takedowns. As a pioneer and innovator in preemptive security, CTM360 operates as an external CTEM technology platform outside an organization’s perimeter. Seamless and turn-key, CTM360 requires no configurations, installations or inputs from the end-user, with all data pre-populated and specific to your organization. All aspects are managed by CTM360.

Average Rating: 4.6/5.0

Total Reviews: 174

How Do G2 Users Rate CTM360?

  • Security Validation: 8.6/10 (Category avg: 9.1/10)
  • Intelligence Reports: 8.7/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.0/10 (Category avg: 8.7/10)
  • Ease of Use: 9.3/10 (Category avg: 9.1/10)

Who Is the Company Behind CTM360?

  • Seller: CTM360
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Manama, BH
  • LinkedIn® Page: www.linkedin.com
    136 employees on LinkedIn®
  • Phone: +97377360360

Who Uses This Product?

  • Top Industries: Banking, Financial Services
  • Company Size: 37% Medium, 37% Large

What Do G2 Reviewers Say About CTM360?

AI-generated summary from verified user reviews

Pros
  • Users value the responsive and reliable customer support of CTM360, enhancing their overall experience and satisfaction.
  • Users appreciate the ease of use of CTM360, finding its dashboard intuitive for all users, including executives.
  • Users value the seamless onboarding and efficient takedowns, appreciating CTM360's customer-centric approach and ease of use.
  • Users value the strong monitoring and efficient case handling, enhancing their cyber risk visibility and response capabilities.
  • Users value the high detection efficiency of CTM360, appreciating the minimal false positives and quick impersonation detection.
Cons
  • Users find CTM360 has limited features, lacking capabilities found on the web portal and needing additional tools for security.
  • Users face integration issues with CTM360, as it struggles to seamlessly connect with existing security infrastructures.
  • Users note a lack of features in CTM360, indicating a need for improvements and additional tools for better functionality.
  • Users are frustrated by the lack of integration with existing security tools, hindering effective automated security management.
  • Users note a significant lack of integrations with existing security infrastructure, limiting automated security workflows.

What Are Recent G2 Reviews of CTM360?

Cloudflare Application Security and Performance

Cloudflare is the connectivity cloud for the "everywhere world," on a mission to help build a better Internet. We provide a unified platform of networking, security, and developer services delivered from a single, intelligent global network that spans hundreds of cities in over 125 countries. This empowers organizations of all sizes, from small businesses to the world's largest enterprises, to make their employees, applications, and networks faster and more secure everywhere, while significantly reducing complexity and cost. Our comprehensive platform includes: - Advanced Security: Protect your online presence with industry-leading DDoS protection, a robust Web Application Firewall (WAF), Bot mitigation, and API security. Implement Zero Trust security to secure remote access, data, and applications for your entire workforce. - Superior Performance: Accelerate website and application loading times globally with our Content Delivery Network (CDN), intelligent DNS, and smart routing capabilities. Optimize images and deliver dynamic content with unparalleled speed. - Powerful Developer Tools: Empower your developers to build and deploy full-stack applications at the edge using Cloudflare Workers (serverless functions), R2 Storage (object storage without egress fees), and D1 (serverless SQL database). Cloudflare helps connect and protect millions of customers globally, offering the control, visibility, and reliability businesses need to work, develop, and accelerate their operations in today's hyperconnected landscape. Our global network continuously learns and adapts, ensuring your digital assets are always protected and performing at their best.

Average Rating: 4.5/5.0

Total Reviews: 783

How Do G2 Users Rate Cloudflare Application Security and Performance?

  • Security Validation: 10.0/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.7/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.8/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 9.1/10)

Who Is the Company Behind Cloudflare Application Security and Performance?

  • Seller: Cloudflare, Inc.
  • Company Website:
  • Year Founded: 2009
  • HQ Location: San Francisco, California
  • LinkedIn® Page: www.linkedin.com
    8,094 employees on LinkedIn®
  • Ownership: NYSE: NET

Who Uses This Product?

  • Who Uses This: Web Developer, Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 62% Small, 27% Medium

What Do G2 Reviewers Say About Cloudflare Application Security and Performance?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the strong security features of Cloudflare Application Security and Performance, enhancing protection against threats effectively.
  • Users appreciate the ease of use of Cloudflare, enjoying its intuitive dashboard and straightforward setup process.
  • Users appreciate the combination of security and performance in Cloudflare, enhancing site speed and protection effortlessly.
  • Users value the combined security and performance features of Cloudflare, enhancing site speed and protection effortlessly.
  • Users value the reliable security and performance of Cloudflare, offering peace of mind and improved website management.
Cons
  • Users find the complex user interface daunting, especially for advanced configurations and navigating powerful features.
  • Users find Cloudflare's services expensive due to advanced features being restricted to higher-tier plans.
  • Users find the complex setup challenging, especially new users navigating advanced configurations and limited feature access.
  • Users find the complexity of configuration challenging, especially when navigating advanced features and pricing options.
  • Users find the learning curve challenging, particularly with complex configurations and limitations on advanced features for new users.

What Are Recent G2 Reviews of Cloudflare Application Security and Performance?

What Are G2 Users Discussing About Cloudflare Application Security and Performance?

Cyble

Cyble is an AI-native cybersecurity solution designed to help organizations enhance their digital security posture through real-time intelligence, detection, and response capabilities. By leveraging advanced agentic AI and processing vast amounts of data, Cyble empowers businesses to navigate the complexities of the cyber threat landscape effectively. Its unique approach involves collecting and enriching signals from various sources, including the dark web, deep web, and surface web, providing unparalleled visibility into emerging threats and adversarial activities. Targeting a wide range of industries, Cyble's platform is particularly beneficial for security teams, risk management professionals, and organizations that prioritize safeguarding their digital assets. The comprehensive suite of solutions offered by Cyble includes Threat Intelligence, Dark Web & Deep Web Monitoring, Attack Surface Management (ASM), and Brand Intelligence, among others. These tools are designed to address specific use cases such as identifying vulnerabilities, monitoring brand reputation, and managing third-party risks, making it an essential resource for organizations aiming to bolster their cybersecurity measures. Cyble's key features are centered around its unified platform, which integrates multiple cybersecurity functions into a single interface. This integration allows for seamless communication between different security components, enabling teams to anticipate, identify, and neutralize threats with remarkable speed and precision. For instance, the Digital Forensics & Incident Response (DFIR) capabilities equip organizations with the tools needed to investigate and respond to incidents effectively, while the DDoS Protection and Cloud Security Posture Management (CSPM) features ensure that businesses can maintain operational integrity even under attack. Moreover, Cyble stands out in its category by combining vast data intelligence with cutting-edge AI automation. This proactive defense strategy not only helps organizations react to cyber threats but also empowers them to stay ahead of potential risks. By enhancing visibility into the threat landscape and providing actionable insights, Cyble enables enterprises to protect their assets, safeguard brand trust, and operate with confidence in an increasingly complex digital environment. The result is a robust cybersecurity framework that supports organizations in navigating the ever-evolving challenges of the cyber world.

Average Rating: 4.8/5.0

Total Reviews: 146

How Do G2 Users Rate Cyble?

  • Security Validation: 9.3/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.6/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.3/10 (Category avg: 8.7/10)
  • Ease of Use: 9.5/10 (Category avg: 9.1/10)

Who Is the Company Behind Cyble?

  • Seller: Cyble
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Alpharetta, US
  • LinkedIn® Page: www.linkedin.com
    233 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 39% Large, 17% Medium

What Do G2 Reviewers Say About Cyble?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Cyble, appreciating its quick setup and streamlined reporting capabilities.
  • Users highly value Cyble for its first-hand threat intelligence, enabling timely responses to potential cybersecurity risks.
  • Users value Cyble for its comprehensive threat intelligence, offering real-time data and advanced protection features for cybersecurity.
  • Users find Cyble to be invaluable for threat intelligence, providing accurate data and rapid insights for effective cybersecurity.
  • Users value Cyble's comprehensive threat detection, enabling proactive responses to security risks and enhanced visibility.
Cons
  • Users find the inefficient alerts lead to overwhelming notifications, causing critical threats to be missed.
  • Users face occasional false positives in alerts, requiring extra effort to validate findings and manage notifications.
  • Users find limited customization in Cyble restrictive, hindering their ability to tailor alerts and dashboards effectively.
  • Users highlight the need for poor customer support, citing slow responses and a lack of available resources.
  • Users feel that poor support management affects response times and overall experience with Cyble.

What Are Recent G2 Reviews of Cyble?

Criminal IP

Criminal IP is a cyber threat intelligence solution that provides decision-ready threat intelligence, and attack surface management solutions to security teams worldwide. By continuously scanning the global internet, Criminal IP aggregates and contextualizes threat signals across IPs, domains, URLs, and attack infrastructure, covering malicious indicators, known vulnerabilities, exposed assets, and attacker behavior. Criminal IP's mission is to give organizations real visibility into their cyber landscape and accelerate threat detection and response by delivering the intelligence needed to outsmart attackers.

Average Rating: 4.6/5.0

Total Reviews: 26

How Do G2 Users Rate Criminal IP?

  • Security Validation: 10.0/10 (Category avg: 9.1/10)
  • Intelligence Reports: 10.0/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.3/10 (Category avg: 8.7/10)
  • Ease of Use: 9.0/10 (Category avg: 9.1/10)

Who Is the Company Behind Criminal IP?

  • Seller: Criminal IP
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Las Vegas, US
  • LinkedIn® Page: www.linkedin.com
    29 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 80% Small, 17% Medium

What Do G2 Reviewers Say About Criminal IP?

AI-generated summary from verified user reviews

Pros
  • Users admire the automation capabilities of Criminal IP, streamlining security data for effective real-time threat visualization.
  • Users appreciate the ease of use of Criminal IP, benefiting from its simple navigation and seamless integration.
  • Users appreciate the intuitive data visualization and seamless API integration, making threat management straightforward and efficient.
  • Users value the quick response time of Criminal IP, enabling seamless real-time threat data visualization and action.
  • Users value the easy setup of Criminal IP, appreciating its intuitive navigation and seamless integration capabilities.
Cons
  • Users experience a difficult learning curve due to advanced search filters, highlighting the need for better onboarding.
  • Users face a steep learning curve due to insufficient training on advanced search filters, impacting their experience.
  • Users experience slow loading times on the web interface, which can hinder the overall usability of Criminal IP.

What Are Recent G2 Reviews of Criminal IP?

ZeroFox

ZeroFox is the solution used to illuminate threat actor intent, mitigate threats and exposures, remove threats from the internet, and preemptively safeguard your reputation. ZeroFox uniquely fuses the core capabilities of Cyber Threat Intelligence, Brand and Domain Protection, Attack Surface Intelligence, Executive Protection and Physical Security Intelligence in one platform packed with intelligence you’ll actually use. ZeroFox defends your business from the everyday attacks that impact revenue, erode trust, and frustrate teams by: Discovering exposed assets, brands, domains, accounts, and emerging threats Validating the risks that matter most to you and your digital estate Disrupting attacks before they harm your business, your customers, and your people Our continuous cycle—Discover, Validate, Disrupt—delivers outcomes and helps organizations achieve deeper threat contextualization, faster detection and response times, and longer-term cost savings by anticipating, understanding, and mitigating external digital threats at scale. Join thousands of customers, including some of the largest public sector organizations and leaders in finance, media, technology, retail, and healthcare, and let ZeroFox deliver timely, personal, and usable intelligence so you can stay ahead of what’s next and reclaim what’s right.

Average Rating: 4.4/5.0

Total Reviews: 176

How Do G2 Users Rate ZeroFox?

  • Security Validation: 8.5/10 (Category avg: 9.1/10)
  • Intelligence Reports: 8.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 7.9/10 (Category avg: 8.7/10)
  • Ease of Use: 8.8/10 (Category avg: 9.1/10)

Who Is the Company Behind ZeroFox?

  • Seller: ZeroFox
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Baltimore, MD
  • LinkedIn® Page: www.linkedin.com
    856 employees on LinkedIn®
  • Ownership: NASDAQ: ZFOX

Who Uses This Product?

  • Who Uses This: Cyber Security Analyst
  • Top Industries: Financial Services, Banking
  • Company Size: 51% Large, 29% Medium

What Do G2 Reviewers Say About ZeroFox?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the intuitive dashboard of ZeroFox, facilitating quick assessments and high adoption rates within teams.
  • Users value the timely and relevant alerts from ZeroFox, significantly saving team time and improving efficiency.
  • Users value the effective threat detection features of ZeroFox, enhancing security and simplifying alert management processes.
  • Users value the timely and relevant alert notifications from ZeroFox, enhancing their threat awareness and response efficiency.
  • Users value the timely and relevant alerts from ZeroFox, saving time and enhancing threat management efficiency.
Cons
  • Users express frustration with inefficient alerts, citing excessive noise and delays in actioning relevant threats.
  • Users experience false alarms with irrelevant alerts from ZeroFox, complicating threat management and causing unnecessary noise.
  • Users experience slow performance with ZeroFox, facing delays in takedowns and overwhelming volumes of alerts.
  • Users frequently face false positive alerts from ZeroFox, leading to irrelevant notifications and wasted time on noise.
  • Users face an inefficient alert system in ZeroFox, struggling with irrelevant alerts and slow response to threats.

What Are Recent G2 Reviews of ZeroFox?

What Are G2 Users Discussing About ZeroFox?

CloudSEK

CloudSEK is a contextual AI company that predicts Cyber Threats. We combine the power of Cyber Crime monitoring, Brand Monitoring, Attack Surface monitoring, and Supply Chain intelligence to give context to our customers’ digital risks.

Average Rating: 4.8/5.0

Total Reviews: 137

How Do G2 Users Rate CloudSEK?

  • Security Validation: 9.4/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.4/10 (Category avg: 8.7/10)
  • Ease of Use: 9.6/10 (Category avg: 9.1/10)

Who Is the Company Behind CloudSEK?

  • Seller: CloudSEK
  • Year Founded: 2015
  • HQ Location: Singapore, SG
  • LinkedIn® Page: www.linkedin.com
    247 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Analyst, Analyst
  • Top Industries: Financial Services, Airlines/Aviation
  • Company Size: 53% Large, 31% Medium

What Do G2 Reviewers Say About CloudSEK?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of CloudSEK, enhancing efficiency in managing security threats and brand monitoring.
  • Users value the proactive monitoring of CloudSEK, enabling early detection of threats and enhancing overall security response.
  • Users commend the excellent customer support of CloudSEK, enhancing their experience in managing security risks effectively.
  • Users appreciate the timely and actionable visibility provided by CloudSEK for managing external threats effectively.
  • Users value the real-time threat intelligence of CloudSEK, enhancing their ability to respond swiftly to potential threats.
Cons
  • Users find the high number of false positives in CloudSEK alerts overwhelming and hinders effective analysis.
  • Users find the inefficient alerts overwhelming, complicating analysis and management during busy periods.
  • Users find the dashboard issues overwhelming and complex, requiring time to properly interpret the information presented.
  • Users find the inefficient alert system overwhelming due to excessive and repetitive alerts, complicating analysis and responses.
  • Users find the complex UI of CloudSEK overwhelming, requiring time to understand and navigate effectively.

What Are Recent G2 Reviews of CloudSEK?

SOCRadar Extended Threat Intelligence

Since 2019, SOCRadar has been a pioneer in SaaS cybersecurity, now serving over 900 customers across 75 countries. Our mission is to provide accessible, proactive threat intelligence. Today, SOCRadar empowers security teams with our groundbreaking Extended Threat Intelligence (XTI) platform and is leading the charge toward the future with Agentic Threat Intelligence (ATI). What does SOCRadar do? At its core, SOCRadar provides a unified, cloud-hosted platform designed to enrich your cyber threat intelligence by contextualizing it with data from your attack surface, digital footprint, dark web exposure, and supply chain. We help security teams see what attackers see by combining External Attack Surface Management, Cyber Threat Intelligence, and Digital Risk Protection into a single, easy-to-use solution. This enables your organization to discover hidden vulnerabilities, detect data leaks, and shut down threats like phishing and brand impersonation before they can harm your business. By combining these critical security functions, SOCRadar replaces the need for separate, disconnected tools. Our holistic approach offers a streamlined, modular experience, providing a complete, real-time view of your threat landscape to help you stay ahead of attackers. Our vision for Agentic Threat Intelligence (ATI) goes beyond today's chatbots and LLMs. We are focused on making it practical for security teams to use AI agents to solve real-world problems. Our initiative will empower you to either deploy pre-built agents or easily create your own, leveraging deep integrations to automate complex tasks that were previously difficult to perform accurately. SOCRadar is dedicated to pioneering this change, making autonomous security an accessible reality for your team.

Average Rating: 4.7/5.0

Total Reviews: 125

How Do G2 Users Rate SOCRadar Extended Threat Intelligence?

  • Security Validation: 8.9/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.1/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.5/10 (Category avg: 8.7/10)
  • Ease of Use: 9.2/10 (Category avg: 9.1/10)

Who Is the Company Behind SOCRadar Extended Threat Intelligence?

  • Seller: SOCRadar
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Delaware
  • LinkedIn® Page: www.linkedin.com
    195 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 42% Medium, 41% Large

What Do G2 Reviewers Say About SOCRadar Extended Threat Intelligence?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of SOCRadar Extended Threat Intelligence, appreciating its intuitive interface and smooth integration.
  • Users value the comprehensive Threat Intelligence of SOCRadar, enabling proactive responses to potential cyber threats.
  • Users value the real-time alerts from SOCRadar, enabling proactive responses to emerging security threats.
  • Users appreciate the comprehensive threat intelligence of SOCRadar, enabling effective data leak detection and proactive risk management.
  • Users value the real-time monitoring capabilities of SOCRadar, enhancing their threat detection and incident response efficiency.
Cons
  • Users experience inefficient alerts, leading to overwhelming noise and necessitating manual verification for actionable intelligence.
  • Users experience inefficient alert systems that create noise, requiring extensive manual verification and leading to analyst fatigue.
  • Users express concerns over false positives from alerts, requiring manual verification and careful tuning to manage effectively.
  • Users feel there is insufficient information on critical CVEs and updates, limiting effective third-party risk assessments.
  • Users express concerns about limited features, particularly regarding alert noise and insufficient depth in supply chain intelligence.

What Are Recent G2 Reviews of SOCRadar Extended Threat Intelligence?

Cisco Talos

Cisco Talos is a threat intelligence organization dedicated to providing protection before, during, and after cybersecurity attacks.

Average Rating: 4.4/5.0

Total Reviews: 38

How Do G2 Users Rate Cisco Talos?

  • Security Validation: 9.2/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.1/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.9/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 9.1/10)

Who Is the Company Behind Cisco Talos?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO
  • Phone: 847-678-6600

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 42% Medium, 33% Large

What Do G2 Reviewers Say About Cisco Talos?

AI-generated summary from verified user reviews

Pros
  • Users value the strong threat intelligence of Cisco Talos, enhancing their security decisions with real-time insights and trends.
  • Users praise the accuracy of information provided by Cisco Talos, benefiting from precise threat intelligence updates.
  • Users appreciate the automation capabilities of Cisco Talos, enhancing efficiency and providing comprehensive security services.
  • Users value the reliable and timely threat intelligence from Cisco Talos, enhancing confidence in security decision-making.
  • Users value the reliable and timely threat intelligence of Cisco Talos, boosting confidence in security decisions.
Cons
  • Users find the complex interface and limited customization challenging, particularly for those unfamiliar with the system.
  • Users find integration issues with Cisco Talos, as it works best with other Cisco tools, limiting flexibility.
  • Users face challenges with limited customization and complex interfaces, hindering the usability of Cisco Talos.
  • Users highlight poor reporting capabilities, especially for non-Cisco tools, making the interface challenging for newcomers.
  • Users find the time-consuming nature of technical details challenging, especially in mixed environments with other tools.

What Are Recent G2 Reviews of Cisco Talos?

What Are G2 Users Discussing About Cisco Talos?

BlackFog

Data can’t be stolen if it never leaves. BlackFog prevents data exfiltration from endpoints, stopping sensitive information from flowing to ransomware groups, AI tools, cloud services, and other unauthorized destinations. While most cybersecurity solutions focus on detecting threats, BlackFog focuses on preventing the outcome attackers want most: access to your data. Our endpoint-native platform monitors and controls outbound communications in real time, preventing data loss through ransomware, insider threats, shadow AI, and other exfiltration channels. BlackFog pioneered anti data exfiltration (ADX), a category built around a simple principle: the endpoint is the last place data can be stopped before it’s gone. By operating directly on the device, BlackFog provides visibility and control across browsers, cloud applications, AI tools, encrypted connections, and emerging AI workflows that traditional network-based approaches often miss. Today, organizations use BlackFog to prevent ransomware data theft, govern AI usage, reduce data loss risk, and protect sensitive information wherever users work. Key Capabilities * Anti data exfiltration (ADX) * Ransomware Data Theft Prevention * Shadow AI Discovery and Governance * AI Data Loss Prevention * Insider Threat Protection * Real-Time Outbound Traffic Control * Endpoint Data Protection * Compliance and Privacy Enforcement

Average Rating: 4.8/5.0

Total Reviews: 39

How Do G2 Users Rate BlackFog?

  • Security Validation: 9.8/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.7/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.8/10 (Category avg: 8.7/10)
  • Ease of Use: 9.2/10 (Category avg: 9.1/10)

Who Is the Company Behind BlackFog?

  • Seller: BlackFog
  • Company Website:
  • Year Founded: 2015
  • HQ Location: BlackFog Inc. Suite 1400 4 Embarcadero Ctr San Francisco CA 94111, United States
  • LinkedIn® Page: www.linkedin.com
    31 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 60% Small, 28% Medium

What Do G2 Reviewers Say About BlackFog?

AI-generated summary from verified user reviews

Pros
  • Users value the robust security features of BlackFog, effectively preventing data theft and enhancing overall protection.
  • Users feel secure and protected with BlackFog, appreciating its ability to operate quietly while preventing ransomware.
  • Users commend BlackFog for its exceptional customer support, enhancing user experience and ensuring seamless software deployment.
  • Users value the ease of use of BlackFog, praising its simple integration and straightforward management.
  • Users praise BlackFog for its effective real-time protection, ensuring data safety and peace of mind effortlessly.
Cons
  • Users feel that BlackFog lacks advanced features like scheduling reports and device management, necessitating additional solutions.
  • Users find the UI design lacking, with odd translucent windows that detract from an otherwise user-friendly experience.
  • Users find BlackFog has limited features, lacking advanced device management tools for comprehensive security needs.
  • Users often face false positives in alert management, leading to time-consuming processes and frustration in handling alerts.
  • Users find the complex user interface of BlackFog challenging, especially for newcomers unfamiliar with cybersecurity tools.

What Are Recent G2 Reviews of BlackFog?

What Are G2 Users Discussing About BlackFog?

Lookout

Lookout is a mobile app that fights cybercriminals by predicting and stopping mobile attacks before they do harm.

Average Rating: 4.3/5.0

Total Reviews: 67

How Do G2 Users Rate Lookout?

  • Security Validation: 8.8/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.6/10 (Category avg: 8.7/10)
  • Ease of Use: 8.8/10 (Category avg: 9.1/10)

Who Is the Company Behind Lookout?

  • Seller: Lookout
  • Year Founded: 2007
  • HQ Location: San Francisco, CA
  • LinkedIn® Page: www.linkedin.com
    514 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 43% Small, 41% Large

What Do G2 Reviewers Say About Lookout?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Lookout, finding it simplifies device monitoring and enhances safety.
  • Users love the comprehensive security features of Lookout, ensuring protection for online safety, privacy, and devices.
  • Users love Lookout for its comprehensive online security features, providing easy monitoring and protection for devices.
  • Users love the user-friendly safety features of Lookout, finding the mobile app compact and management view highly useful.
  • Users find the management view of Lookout surprisingly useful for addressing all their cybersecurity needs efficiently.
Cons
  • Users find the limited features of Lookout insufficient, requiring additional apps for essential functionalities.
  • Users report a lack of detailed alert information, hindering their ability to understand site-specific issues effectively.
  • Users find the complex configuration and tagging process time-consuming and frustrating with unwanted automatic installations.
  • Users find deployment issues with frequent updates and suggest improvements for the app design impacting user experience.
  • Users find difficult configuration processes frustrating, with unwanted automatic installations complicating their experience.

What Are Recent G2 Reviews of Lookout?

What Are G2 Users Discussing About Lookout?

Check Point Exposure Management

Exposure Management is changing how organizations react to vulnerabilities that put them in risk. Attackers exploit exposed assets, leaked credentials, and misconfigurations within hours using sophisticated AI attack tools. Meanwhile, security teams are left sorting through dashboards, alerts, and disconnected tools. For a limited time only, we are providing an Agentic Exposure Validation Scan at no cost. The scan delivers proven, evidence-backed findings your team can act on immediately. Request scan here - https://checkpoint.cyberint.com/limited-time-offer-aev-scan Check Point Exposure Management closes that gap by combining billions of external intelligence signals into a Unified Intelligence Fabric. The platform continuously identifies, validates, prioritizes, and safely remediates the exposures attackers are most likely to exploit. With Cyber Asset Attack Surface Management (CAASM), security teams gain a real-time inventory across cloud, SaaS, on-premises infrastructure, endpoints, and identities through 150+ agentless integrations. Unlike traditional vulnerability management, Check Point prioritizes exposures based on real-world exploitability, active threat intelligence, business context, and existing security controls, eliminating duplicate alerts and reducing remediation noise. It does so while maintaining business continuity. Safe-by-design remediation then validates every action before enforcement, enabling capabilities such as virtual patching, IPS activation, configuration hardening, and policy enforcement without disrupting business operations. Organizations using the platform achieve a 93% true positive rate on alerts, 12-hour average takedown MTTR, and 504 safe remediations per organization every month. Built around Gartner's Continuous Threat Exposure Management (CTEM) framework, Check Point helps organizations move from visibility to measurable risk reduction. Gartner predicts organizations adopting CTEM with mobilization will experience 50% fewer successful cyberattacks by 2028. Ready to see Exposure Management in action? Get a 15-minute demo: https://l.cyberint.com/exposure-management-demo

Average Rating: 4.6/5.0

Total Reviews: 198

How Do G2 Users Rate Check Point Exposure Management?

  • Security Validation: 8.8/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.0/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.4/10 (Category avg: 8.7/10)
  • Ease of Use: 9.1/10 (Category avg: 9.1/10)

Who Is the Company Behind Check Point Exposure Management?

Who Uses This Product?

  • Who Uses This: Cyber Security Analyst, Security Threat Analyst
  • Top Industries: Banking, Financial Services
  • Company Size: 66% Large, 21% Medium

What Do G2 Reviewers Say About Check Point Exposure Management?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Check Point Exposure Management, enabling quick data requests and straightforward setup.
  • Users value the fidelity of alerts and expert analysts, enhancing threat detection and remediation efficiency.
  • Users value the fidelity of alerts and experienced analysts, enabling timely remediation and proactive threat identification.
  • Users value the fidelity of alerts and expert remediation support from Check Point Exposure Management for proactive threat management.
  • Users value the quick and responsive customer support from Cyberint, enhancing their confidence in threat intelligence services.
Cons
  • Users experience inefficient alerts, facing repetitive notifications and high alert noise that complicates management efforts.
  • Users encounter false positives with Check Point Exposure Management, leading to confusion and redundant alerts in their experience.
  • Users report an inefficient alert system that generates excessive notifications, impacting overall usability and user experience.
  • Users notice integration issues with Check Point Exposure Management, limiting third-party tool compatibility and overall usability.
  • Users express concerns about the limited features of Check Point Exposure Management, particularly regarding alert tuning and integrations.

What Are Recent G2 Reviews of Check Point Exposure Management?

What Are G2 Users Discussing About Check Point Exposure Management?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated