Best Enterprise Security Orchestration, Automation, and Response (SOAR) Software

How Many Security Orchestration, Automation, and Response (SOAR) Software Products Does G2 Track?

Total Products under this Category: 101

Category Stats (Nov 2026)

  • Average Rating: 4.52/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Singularity AI SIEM (+2.27%) - Among all products in this category, Singularity AI SIEM recorded the largest rating increase compared to last month

Last updated: November 12, 2026

How Does G2 Rank Security Orchestration, Automation, and Response (SOAR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,800+ Authentic Reviews
  • 101+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

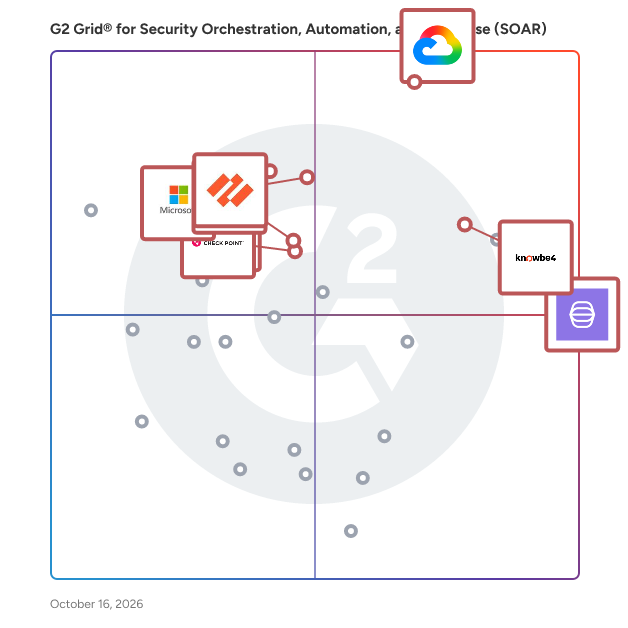
G2 Grid® for Security Orchestration, Automation, and Response (SOAR) Software

G2 Grid® for Security Orchestration, Automation, and Response (SOAR) Software plotting products by satisfaction and market presence

Highlighted products: Tines Stories, Google Security Operations, ServiceNow Security Operations, Palo Alto Cortex XSIAM, Microsoft Sentinel, Cortex XSOAR, Check Point Infinity Platform, and KnowBe4 PhishER/PhishER Plus.

Underlying data: [Grid® JSON](https://www.g2.com/categories/security-orchestration-automation-and-response-soar/grids.json?focus%5B%5D=tines-stories&focus%5B%5D=google-security-operations&focus%5B%5D=servicenow-security-operations&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=microsoft-sentinel&focus%5B%5D=cortex-xsoar&focus%5B%5D=check-point-infinity-platform&focus%5B%5D=knowbe4-phisher-phisher-plus&segment=enterprise)

Tines Stories

Tines is the intelligent workflow platform trusted by the world's most advanced organizations. Companies like Coinbase, Databricks, Mars, Reddit, and SAP use Tines to power their most important workflows. With Tines, they’ve built a secure, flexible foundation to operationalize AI agents and intelligent workflows, unlocking productivity, moving faster, and future-proofing how work gets done.

Average Rating: 4.7/5.0

Total Reviews: 425

How Do G2 Users Rate Tines Stories?

  • Automated Remediation: 9.3/10 (Category avg: 8.7/10)
  • Quality of Support: 9.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 9.2/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.6/10 (Category avg: 8.7/10)

Who Is the Company Behind Tines Stories?

  • Seller: Tines
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Dublin, IE
  • LinkedIn® Page: www.linkedin.com
    619 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Engineer, Software Engineer
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 39% Medium, 35% Large

What Do G2 Reviewers Say About Tines Stories?

AI-generated summary from verified user reviews

Pros
  • Users praise the intuitive ease of use of Tines Stories, facilitating quick workflow setup and management.
  • Users value the powerful automation capabilities of Tines, making complex workflows accessible and streamlined for all skill levels.
  • Users praise Tines for its responsive and helpful customer support, enhancing their overall experience with the tool.
  • Users love Tines for its amazing integrations and exceptional support, making automation accessible for all skill levels.
  • Users find Tines Stories to be a time-saving solution, enabling quick and efficient automation of tasks.
Cons
  • Users acknowledge a learning curve with Tines Stories, but find support alleviates challenges and enhances usability.
  • Users note missing features in Tines Stories, including limited JavaScript use and a need for improved ticketing functionality.
  • Users are frustrated by the lack of features in Tines Stories, particularly for scripting and ticketing functionalities.
  • Users find Tines Stories to have a steep learning curve, as creating structures can be intimidating without clear guidance.
  • Users find difficult learning curves in Tines Stories, especially with advanced functions and formulas requiring more accessible documentation.

What Are Recent G2 Reviews of Tines Stories?

What Are G2 Users Discussing About Tines Stories?

Google Security Operations

Google Security Operations offers a unified experience across SIEM, SOAR, and threat intelligence to drive better detection, investigation, and response. Collect security telemetry data, apply threat intel to identify high priority threats, drive response with playbook automation, case management, and collaboration. It also provides Gemini-native agentic defense to help autonomously handle workflows like alert triage, threat hunting, and detection engineering. Google Security Operations also supports AI Threat Defense to monitor, detect, and respond to threats from code you do not own or cannot patch.

Average Rating: 4.4/5.0

Total Reviews: 125

How Do G2 Users Rate Google Security Operations?

  • Automated Remediation: 9.9/10 (Category avg: 8.7/10)
  • Quality of Support: 8.4/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.1/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.6/10 (Category avg: 8.7/10)

Who Is the Company Behind Google Security Operations?

  • Seller: Google
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG
  • Phone: +1 (650) 253-0000

Who Uses This Product?

  • Who Uses This: Developer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 37% Medium, 36% Small

What Do G2 Reviewers Say About Google Security Operations?

AI-generated summary from verified user reviews

Pros
  • Users value the centralized detection and investigation capabilities of Google Security Operations for efficient threat management.
  • Users appreciate the scalability and efficiency of Google Security Operations for effective threat detection and response.
  • Users find Google Security Operations to have a user-friendly interface, enabling quick analysis and effective threat responses.
  • Users value the comprehensive security capabilities of Google Security Operations for effective threat detection and response.
  • Users appreciate the seamless integrations of Google Security Operations, enhancing threat detection and data analysis across the ecosystem.
Cons
  • Users feel that the high cost of Google Security Operations is a significant drawback affecting overall satisfaction.
  • Users find a steep learning curve when trying to utilize Google Security Operations effectively, especially for the inexperienced.
  • Users find the implementation complexity of Google Security Operations challenging, requiring significant time and resources to manage.
  • Users find the learning difficulty of Google Security Operations challenging, requiring substantial time to master its features.
  • Users find limited customization in Google Security Operations hinders adaptability to specific security requirements and user-friendliness.

What Are Recent G2 Reviews of Google Security Operations?

ServiceNow Security Operations

ServiceNow Security Operations is a sophisticated software solution designed to enhance threat and vulnerability management as well as incident response for organizations. By leveraging artificial intelligence, this platform empowers security teams to operate more efficiently and effectively, allowing for streamlined collaboration across IT, security, and risk management departments. The primary goal of ServiceNow Security Operations is to simplify complex security processes while minimizing risks associated with cybersecurity threats. Targeted at security teams within organizations of various sizes, ServiceNow Security Operations addresses the need for a cohesive approach to managing security incidents and vulnerabilities. It is particularly beneficial for organizations that utilize multiple security tools, as it integrates security and vulnerability data from these existing systems. This integration enables teams to respond to threats more rapidly by automating critical workflows and processes, thus reducing the manual effort traditionally required in incident response. The platform is suitable for both small businesses and large enterprises, making it a versatile choice for organizations looking to enhance their cybersecurity measures. Key features of ServiceNow Security Operations include intelligent workflows that automate routine tasks, allowing security professionals to focus on more strategic initiatives. The platform’s AI-driven capabilities facilitate the automatic correlation of threat intelligence from diverse sources, such as the MITRE ATT&CK framework. This feature enhances situational awareness and enables teams to prioritize threats effectively based on real-time data. Additionally, the ability to take action within other security or IT management tools from a centralized console streamlines operations, ensuring that teams can respond to incidents without unnecessary delays. This centralized approach not only improves efficiency but also fosters better communication among different departments involved in security management. Moreover, the use of digital security workflows and orchestration significantly accelerates tasks such as analysis, prioritization, and remediation. By automating these processes, organizations can improve their response times and enhance their overall cybersecurity posture. The integration of AI-driven automation within the ServiceNow AI Platform® further strengthens the platform's capabilities, enabling organizations to drive cyber resilience and reduce their exposure to potential threats. This proactive approach to cybersecurity ensures that organizations are not only reacting to incidents but are also prepared to prevent them. ServiceNow Security Operations stands out in the cybersecurity landscape by offering a comprehensive solution that addresses the complexities of modern cybersecurity challenges. By automating and simplifying threat and vulnerability management, it empowers security teams to respond more effectively, thereby enhancing the overall security framework of an organization. This makes it an essential tool for any organization looking to bolster its defenses against the ever-evolving landscape of cyber threats.

Average Rating: 4.4/5.0

Total Reviews: 86

How Do G2 Users Rate ServiceNow Security Operations?

  • Automated Remediation: 8.8/10 (Category avg: 8.7/10)
  • Quality of Support: 8.4/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.5/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.4/10 (Category avg: 8.7/10)

Who Is the Company Behind ServiceNow Security Operations?

  • Seller: ServiceNow
  • Company Website:
  • Year Founded: 2004
  • HQ Location: Santa Clara, CA
  • LinkedIn® Page: www.linkedin.com
    35,078 employees on LinkedIn®
  • Ownership: NYSE:NOW

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 54% Large, 22% Medium

What Do G2 Reviewers Say About ServiceNow Security Operations?

AI-generated summary from verified user reviews

Pros
  • Users value the remarkable integration capabilities of ServiceNow Security Operations, facilitating seamless management of security incidents.
  • Users value the seamless integration with third-party tools in ServiceNow Security Operations, enhancing productivity and workflow efficiency.
  • Users appreciate the ease of use of ServiceNow Security Operations, facilitating efficient management of security incidents.
  • Users praise the seamless integration capabilities of ServiceNow Security Operations, enhancing efficiency and productivity in incident management.
  • Users appreciate the end-to-end management of incidents in ServiceNow Security Operations, enhancing efficiency and integration.
Cons
  • Users find the difficult setup of ServiceNow Security Operations to be a significant barrier to effective implementation.
  • Users face integration issues with ServiceNow Security Operations, citing difficulties in setup and limited direct integrations.
  • Users feel the licensing issues with ServiceNow Security Operations limit playbook options, impacting remediation and increasing costs.
  • Users struggle with the complexity of building playbooks in ServiceNow Security Operations, highlighting a need for simplification.
  • Users face difficult customization when building playbooks in ServiceNow Security Operations, hindering their effectiveness and efficiency.

What Are Recent G2 Reviews of ServiceNow Security Operations?

What Are G2 Users Discussing About ServiceNow Security Operations?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Palo Alto Cortex XSIAM

Product Description: Palo Alto Networks' Cortex XSIAM is an AI-driven security operations platform designed to transform traditional Security Operations Centers by integrating and automating key functions such as data centralization, threat detection, and incident response. By leveraging machine learning and automation, it enables organizations to detect and respond to threats more efficiently, reducing manual workloads and improving overall security posture. Key Features and Functionality: - Data Centralization: Aggregates data from various sources into a unified platform, providing comprehensive visibility across the enterprise. - AI-Powered Threat Detection: Utilizes machine learning algorithms to identify anomalies and potential threats in real-time. - Automated Incident Response: Streamlines response processes through automation, enabling rapid mitigation of security incidents. - Integrated SOC Capabilities: Combines functions such as Extended Detection and Response , Security Orchestration, Automation, and Response , Attack Surface Management , and Security Information and Event Management into a cohesive platform, eliminating the need for multiple disparate tools. - Scalability: Designed to handle large volumes of data and adapt to the evolving needs of modern enterprises. Primary Value and Problem Solved: Cortex XSIAM addresses the challenges of disjointed data, weak threat defense, and heavy reliance on manual work in traditional SOCs. By centralizing data and automating security operations, it simplifies processes, enhances threat detection accuracy, and accelerates incident response times. This transformation enables organizations to proactively outpace threats, reduce operational costs, and achieve a more robust security posture.

Average Rating: 4.4/5.0

Total Reviews: 109

How Do G2 Users Rate Palo Alto Cortex XSIAM?

  • Automated Remediation: 7.6/10 (Category avg: 8.7/10)
  • Quality of Support: 8.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.3/10 (Category avg: 8.6/10)
  • Workflow Automation: 7.2/10 (Category avg: 8.7/10)

Who Is the Company Behind Palo Alto Cortex XSIAM?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Large, 36% Medium

What Do G2 Reviewers Say About Palo Alto Cortex XSIAM?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Palo Alto Cortex XSIAM, benefiting from its intuitive interface and seamless integration.
  • Users value the advanced threat detection capabilities of Palo Alto Cortex XSIAM, ensuring both known and unknown threats are managed effectively.
  • Users value the seamless integrations of Palo Alto Cortex XSIAM, enhancing overall functionality across various platforms.
  • Users value the unified console of Palo Alto Cortex XSIAM for simplifying security management across endpoints, network, and cloud.
  • Users value the single console integration, highlighting its ease of use and reliability for threat detection.
Cons
  • Users find the Cortex XSIAM to be very expensive compared to other solutions, impacting overall satisfaction.
  • Users find the difficult learning curve of Palo Alto Cortex XSIAM a challenge due to its complexity and setup.
  • Users find the complexity of the console overwhelming, requiring significant time and expertise to navigate effectively.
  • Users report integration issues with Palo Alto Cortex XSIAM, facing challenges with non-native equipment and log maintenance.
  • Users find the UX improvement of Palo Alto Cortex XSIAM lacking in customization and intuitive design for features.

What Are Recent G2 Reviews of Palo Alto Cortex XSIAM?

What Are G2 Users Discussing About Palo Alto Cortex XSIAM?

Microsoft Sentinel

Microsoft Sentinel lets you see and stop threats before they cause harm, with SIEM reinvented for a modern world. Microsoft Sentinel is your birds-eye view across the enterprise. Put the cloud and large-scale intelligence from decades of Microsoft security experience to work. Make your threat detection and response smarter and faster with artificial intelligence (AI). Eliminate security infrastructure setup and maintenance, and elastically scale to meet your security needs—while reducing IT costs. With Microsoft Sentinel, you can: - Collect data at cloud scale—across all users, devices, applications, and infrastructure, both on-premises and in multiple clouds - Detect previously uncovered threats and minimize false positives using analytics and unparalleled threat intelligence from Microsoft - Investigate threats with AI and hunt suspicious activities at scale, tapping into decades of cybersecurity work at Microsoft -Respond to incidents rapidly with built-in orchestration and automation of common tasks

Average Rating: 4.4/5.0

Total Reviews: 275

How Do G2 Users Rate Microsoft Sentinel?

  • Automated Remediation: 8.7/10 (Category avg: 8.7/10)
  • Quality of Support: 8.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.3/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.4/10 (Category avg: 8.7/10)

Who Is the Company Behind Microsoft Sentinel?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT
  • Phone: +1 (877) 276-2464

Who Uses This Product?

  • Who Uses This: Security Analyst, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 42% Large, 31% Medium

What Do G2 Reviewers Say About Microsoft Sentinel?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time monitoring of Microsoft Sentinel, gaining enhanced visibility and streamlined incident handling across their systems.
  • Users appreciate the effective alerting of Microsoft Sentinel, enhancing security through automated responses to unusual activities.
  • Users value the seamless dashboard usability of Microsoft Sentinel, enhancing their security management and threat response efficiency.
  • Users value the fast and secure threat response of Microsoft Sentinel, enhancing their security and alert management.
  • Users value the centralized data collection feature of Microsoft Sentinel, enhancing security analytics and threat visibility.
Cons
  • Users find the cloud dependency of Microsoft Sentinel challenging, making custom reporting and integration cumbersome.
  • Users find the complex configuration of Microsoft Sentinel challenging, often requiring extensive documentation and exploration.
  • Users find configuration issues in Microsoft Sentinel challenging, requiring time, effort, and technical expertise to navigate.
  • Users find the difficult setup of Microsoft Sentinel frustrating, often requiring extensive documentation exploration for configuration.
  • Users find the poor interface design of Microsoft Sentinel challenging, making navigation and understanding features difficult.

What Are Recent G2 Reviews of Microsoft Sentinel?

What Are G2 Users Discussing About Microsoft Sentinel?

Cortex XSOAR

Palo Alto Networks' Cortex XSOAR is a comprehensive Security Orchestration, Automation, and Response (SOAR) platform designed to streamline and enhance security operations. By integrating automation, case management, real-time collaboration, and threat intelligence management, Cortex XSOAR empowers security teams to respond to incidents more efficiently and effectively. Key Features and Functionality: - Process Standardization and Automation: Cortex XSOAR offers over 270 out-of-the-box playbooks, enabling the automation of numerous security use cases. These playbooks orchestrate response actions across more than 350 third-party products, facilitating seamless integration and operational consistency. - Security-Focused Case Management: The platform unifies alerts, incidents, and indicators from various sources into a single case management framework. This consolidation accelerates incident response by providing a comprehensive view of security events. - Real-Time Collaboration: Cortex XSOAR includes a Virtual War Room equipped with built-in ChatOps and a command-line interface. This feature allows security teams to collaborate in real time, execute commands across the entire product stack, and manage incidents more effectively. - Threat Intelligence Management: The platform aggregates disparate threat intelligence sources, customizes and scores feeds, and matches indicators against the organization's specific environment. This capability enables security teams to take informed actions swiftly. Primary Value and Problem Solving: Cortex XSOAR addresses the challenges faced by security teams, such as the overwhelming volume of alerts and the need for rapid incident response. By automating repetitive tasks and standardizing processes, the platform reduces the time spent on incidents by up to 90%, allowing analysts to focus on critical threats. The integration of threat intelligence management with SOAR capabilities ensures that organizations can operationalize threat feeds effectively, enhancing their overall security posture. Additionally, the platform's extensive integration ecosystem, with over 360 third-party integrations, enables organizations to orchestrate complex workflows across their existing security infrastructure without extensive custom development.

Average Rating: 4.6/5.0

Total Reviews: 29

How Do G2 Users Rate Cortex XSOAR?

  • Automated Remediation: 9.0/10 (Category avg: 8.7/10)
  • Quality of Support: 8.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.8/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.0/10 (Category avg: 8.7/10)

Who Is the Company Behind Cortex XSOAR?

  • Seller: Palo Alto Networks
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW
  • Total Revenue (USD mm): $3,408

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 52% Large, 31% Medium

What Do G2 Reviewers Say About Cortex XSOAR?

AI-generated summary from verified user reviews

Pros
  • Users value the customization and automation capabilities of Cortex XSOAR, enhancing their incident response efficiency.
  • Users find the intuitive and powerful UI of Cortex XSOAR enhances their incident response and automation capabilities.
  • Users appreciate the accuracy of information in Palo Alto Networks Cortex XSOAR, enabling safe and efficient tool integration.
  • Users appreciate the powerful automation capabilities of Cortex XSOAR for incident response tasks and customization options.
  • Users appreciate the direct customer support of Palo Alto Networks Cortex XSOAR, enhancing their incident response experience.
Cons
  • Users find the learning curve steep, requiring significant time to become proficient with Cortex XSOAR.
  • Users find limited customization options in Cortex XSOAR, wishing for enhanced reporting capabilities to meet their needs.
  • Users find that logging issues hinder quick readability of data logs, requiring new tabs for better access.
  • Users find log management issues arise due to difficult-to-read data logs, impacting efficiency and usability.
  • Users find the reporting capabilities lacking, expressing a desire for enhanced customization options in Cortex XSOAR.

What Are Recent G2 Reviews of Cortex XSOAR?

What Are G2 Users Discussing About Cortex XSOAR?

KnowBe4 PhishER/PhishER Plus

KnowBe4 PhishER Plus delivers automated incident response to eliminate SOC noise and remediate malicious emails across your organization simultaneously. It leverages AI to categorize reported messages across email and Microsoft Teams, automatically responding to reporters, flagging high-risk messages, and removing threats across all mailboxes. SOC teams can even flip malicious messages into training simulations to see who would have fallen victim. Customers report saving upwards of 99% of triage time, highly praising the platform's intuitive, user-friendly interface that transforms overwhelming manual workflows into fast, consistent actions. This layer of defense reviews threats slipping past other security layers, offering a single pane of glass view with leading third-party integrations like CrowdStrike, Webroot, and VirusTotal. PhishER Plus turns manual email triaging into a proactive, automated security posture.

Average Rating: 4.6/5.0

Total Reviews: 573

How Do G2 Users Rate KnowBe4 PhishER/PhishER Plus?

  • Automated Remediation: 8.7/10 (Category avg: 8.7/10)
  • Quality of Support: 9.2/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.9/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.6/10 (Category avg: 8.7/10)

Who Is the Company Behind KnowBe4 PhishER/PhishER Plus?

  • Seller: KnowBe4, Inc.
  • Company Website:
  • Year Founded: 2010
  • HQ Location: Clearwater, FL
  • LinkedIn® Page: www.linkedin.com
    2,655 employees on LinkedIn®
  • Ownership: NASDAQ: KNBE

Who Uses This Product?

  • Who Uses This: IT Manager, Director of IT
  • Top Industries: Financial Services, Primary/Secondary Education
  • Company Size: 75% Medium, 13% Large

What Do G2 Reviewers Say About KnowBe4 PhishER/PhishER Plus?

AI-generated summary from verified user reviews

Pros
  • Users love how KnowBe4 PhishER/PhishER Plus simplifies phishing email management, streamlining workflows and enhancing security efficiently.
  • Users value the automatic sorting and prioritization of suspicious emails, enhancing response efficiency and security.
  • Users appreciate the automation of KnowBe4 PhishER, which simplifies managing reported phishing emails effectively.
  • Users appreciate the enhanced security provided by KnowBe4 PhishER/PhishER Plus, simplifying phishing email management and response.
  • Users commend the ease of use of KnowBe4 PhishER/PhishER Plus, simplifying phishing email management and enhancing security effectively.
Cons
  • Users experience frequent false positives, leading to wasted time and complicating the automation process of threat detection.
  • Users find the ineffective email security concerning, as threats sometimes bypass filters and reach inboxes unaddressed.
  • Users desire greater email management granularity in PhishER, noting inconsistencies and delays in filtering reported emails.
  • Users experience a time-consuming learning curve when configuring PhishER/PhishER Plus to their specific needs.
  • Users find the setup difficult, requiring extensive reading and outside help, complicating the initial onboarding process.

What Are Recent G2 Reviews of KnowBe4 PhishER/PhishER Plus?

What Are G2 Users Discussing About KnowBe4 PhishER/PhishER Plus?

Check Point Infinity Platform

Check Point Infinity is the only fully consolidated cyber security architecture that provides unprecedented protection against Gen V mega-cyber attacks as well as future cyber threats across all networks, endpoint, cloud and mobile. The architecture is designed to resolve the complexities of growing connectivity and inefficient security.

Average Rating: 4.6/5.0

Total Reviews: 109

How Do G2 Users Rate Check Point Infinity Platform?

  • Quality of Support: 8.8/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.6/10 (Category avg: 8.6/10)

Who Is the Company Behind Check Point Infinity Platform?

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 44% Large, 37% Medium

What Do G2 Reviewers Say About Check Point Infinity Platform?

AI-generated summary from verified user reviews

Pros
  • Users commend the advanced security features of Check Point Infinity Platform, effectively preventing future attacks on cloud infrastructures.
  • Users value the cloud security features of Check Point Infinity Platform for efficient audits and infrastructure evaluations.
  • Users commend the proactive threat detection of Check Point Infinity Platform, enhancing security for cloud applications.
  • Users highlight the comprehensive security features of Check Point Infinity Platform, effectively shielding against future attacks.
  • Users value the advanced security features of Check Point Infinity for effectively safeguarding their cloud infrastructure.
Cons
  • Users find the steep learning curve of Check Point Infinity Platform challenging due to its complexity and extensive features.
  • Users find the complex setup process for Check Point Infinity Platform can be time-consuming and confusing at times.
  • Users feel that improvement is needed in real-time support and custom ruleset creation for better functionality.
  • Users express concerns about poor support services, indicating a need for improvement in customer assistance and log visibility.
  • Users find the limited customization options challenging, affecting their ability to tailor the platform to their needs.

What Are Recent G2 Reviews of Check Point Infinity Platform?

What Are G2 Users Discussing About Check Point Infinity Platform?

Torq AI SOC Platform

Torq is the AI SOC platform that combines agentic insights and automation so that enterprises can triage, investigate, and respond to actual risks, faster. Torq streamlines every step from alert through resolution. The platform analyzes your risk context to identify your biggest threats. Working alongside your SecOps staff, the Torq platform integrates with your security stack to facilitate containment and remediation workflows.

Average Rating: 4.8/5.0

Total Reviews: 166

How Do G2 Users Rate Torq AI SOC Platform?

  • Automated Remediation: 9.2/10 (Category avg: 8.7/10)
  • Quality of Support: 9.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 9.3/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.4/10 (Category avg: 8.7/10)

Who Is the Company Behind Torq AI SOC Platform?

  • Seller: torq
  • Company Website:
  • Year Founded: 2020
  • HQ Location: New York, US
  • LinkedIn® Page: www.linkedin.com
    470 employees on LinkedIn®
  • Total Revenue (USD mm): $21

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 49% Medium, 30% Small

What Do G2 Reviewers Say About Torq AI SOC Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the user-friendly interface of Torq AI SOC Platform, enhancing their incident management and workflow efficiency.
  • Users value the strong security overview provided by Torq AI SOC Platform, enhancing incident tracking and vulnerability management.
  • Users appreciate the seamless automation of Torq AI SOC Platform, enhancing security and simplifying workflow management.
  • Users value the intuitive dashboards of Torq AI SOC Platform, centralizing incident views and enhancing security operations.
  • Users appreciate the comprehensive threat detection of Torq AI, delivering crucial insights and enhancing security across networks.
Cons
  • Users find the difficult learning curve challenging, requiring time and training to fully utilize Torq AI SOC Platform.
  • Users note a slight learning curve with the Torq AI SOC Platform, making it challenging for beginners to master.
  • Users feel the missing built-in playbooks hinder the ease of onboarding and overall management within the Torq AI SOC Platform.
  • Users suggest improvement needed in documentation and feature management for better usability of Torq AI SOC Platform.
  • Users experience poor interface design, with issues like unresponsive buttons and unintuitive navigation that hinder efficiency.

What Are Recent G2 Reviews of Torq AI SOC Platform?

IBM QRadar SOAR

IBM QRadar® SOAR is designed to help your security team respond to cyberthreats with confidence, automate with intelligence and collaborate with consistency. It guides your team in resolving incidents by codifying established incident response processes into dynamic playbooks. The open and agnostic platform helps accelerate and orchestrate their response by automating actions with intelligence and integrating with other security tools. IBM QRadar SOAR is available on AWS Marketplace.

Average Rating: 4.0/5.0

Total Reviews: 25

How Do G2 Users Rate IBM QRadar SOAR?

  • Automated Remediation: 7.5/10 (Category avg: 8.7/10)
  • Quality of Support: 7.9/10 (Category avg: 9.0/10)
  • Ease of Admin: 6.7/10 (Category avg: 8.6/10)
  • Workflow Automation: 7.4/10 (Category avg: 8.7/10)

Who Is the Company Behind IBM QRadar SOAR?

  • Seller: IBM
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®
  • Ownership: SWX:IBM
  • Phone: 1-866-277-7488

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 72% Large, 21% Medium

What Do G2 Reviewers Say About IBM QRadar SOAR?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of IBM QRadar SOAR, benefiting from user-friendly features and rapid support.
  • Users value the effective automation capabilities of IBM QRadar SOAR, reducing manual workloads and enhancing security efficiency.
  • Users value the easy integrations with various tools, making security workflows and processes streamlined and efficient.
  • Users appreciate the seamless integration with security and ticketing tools, simplifying routine security operations greatly.
  • Users value the responsive customer support from IBM, ensuring quick resolutions and an easy-to-use console.
Cons
  • Users face integration issues with IBM QRadar SOAR, resulting in limited out-of-the-box capabilities and complex implementations.
  • Users find IBM QRadar SOAR to be complex to work on initially, which can hinder the learning curve and usability.
  • Users experience limited integration with IBM QRadar SOAR, hindering advanced transformations and making implementations challenging.
  • Users find that IBM QRadar SOAR has system limitations that hinder sophisticated transformations and practical implementations.
  • Users often face bug issues like workflow errors and occasional lagging, impacting their overall experience.

What Are Recent G2 Reviews of IBM QRadar SOAR?

Sumo Logic

Sumo Logic, Inc. unifies and analyzes enterprise data, translating it into actionable insights through one AI-powered cloud-native log analytics platform. This single source of truth enables Dev, Sec and Ops teams to simplify complexity, collaborate efficiently and accelerate data-driven decisions that drive business value. Customers around the world rely on the Sumo Logic SaaS Log Analytics Platform for trusted insights to ensure application reliability, secure and protect against modern security threats, and gain insights into their cloud infrastructures. For more information, visit: SUMOLOGIC.COM

Average Rating: 4.4/5.0

Total Reviews: 413

How Do G2 Users Rate Sumo Logic?

  • Automated Remediation: 8.8/10 (Category avg: 8.7/10)
  • Quality of Support: 8.6/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.4/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.3/10 (Category avg: 8.7/10)

Who Is the Company Behind Sumo Logic?

  • Seller: Sumo Logic
  • Company Website:
  • Year Founded: 2010
  • HQ Location: Redwood City, CA
  • LinkedIn® Page: www.linkedin.com
    824 employees on LinkedIn®
  • Ownership: NASDAQ: SUMO

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 48% Medium, 38% Large

What Do G2 Reviewers Say About Sumo Logic?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use in Sumo Logic, enabling quick insights from data without complexity.
  • Users commend the powerful and accessible log management features of Sumo Logic, enhancing efficiency and visualization capabilities.
  • Users value the flexible analytics and powerful real-time features of Sumo Logic, enhancing collaboration and operational visibility.
  • Users value the real-time monitoring capabilities of Sumo Logic, enabling quick insights and effective data visualization.
  • Users value the powerful and accessible analytics of Sumo Logic, enhancing their data visualization and decision-making capabilities.
Cons
  • Users find the difficult learning curve of Sumo Logic challenging, especially transitioning from simpler tools.
  • Users face a steeper learning curve with Sumo Logic, especially when transitioning from tools like Splunk or Elastic.
  • Users note a steep learning curve with Sumo Logic that may challenge teams transitioning from other tools.
  • Users find Sumo Logic expensive, especially if data tiers are misconfigured, leading to unexpected high bills.
  • Users experience slow performance with Sumo Logic, facing delays and lag during queries, especially with large datasets.

What Are Recent G2 Reviews of Sumo Logic?

What Are G2 Users Discussing About Sumo Logic?

Splunk SOAR (Security Orchestration, Automation and Response)

Splunk SOAR provides security orchestration, automation and response capabilities that allow security analysts to work smarter by automating repetitive tasks; respond to security incidents faster with automated detection, investigation, and response; increase productivity, efficiency and accuracy; and strengthen defenses by connecting and coordinating complex workflows across their team and tools. Splunk SOAR also supports a broad range of security operations center (SOC) functions including event and case management, integrated threat intelligence, collaboration tools and reporting.

Average Rating: 4.4/5.0

Total Reviews: 39

How Do G2 Users Rate Splunk SOAR (Security Orchestration, Automation and Response)?

  • Automated Remediation: 8.6/10 (Category avg: 8.7/10)
  • Quality of Support: 8.8/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.1/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.7/10 (Category avg: 8.7/10)

Who Is the Company Behind Splunk SOAR (Security Orchestration, Automation and Response)?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO
  • Phone: 847-678-6600

Who Uses This Product?

  • Top Industries: Information Technology and Services, Consulting
  • Company Size: 43% Medium, 35% Large

What Do G2 Reviewers Say About Splunk SOAR (Security Orchestration, Automation and Response)?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the effective security management of Splunk SOAR, enhancing their ability to detect and respond to threats.
  • Users value the ease of threat detection with Splunk SOAR, enhancing their ability to analyze and respond swiftly.
  • Users appreciate the ease of use of Splunk SOAR, benefiting from its intuitive interface and seamless integrations.
  • Users value the real-time monitoring capabilities of Splunk SOAR, enhancing threat detection and response efficiency.
  • Users appreciate the real-time threat alerts from Splunk SOAR, enhancing security response and reducing human error.
Cons
  • Users find the pricing to be expensive, making it challenging for small businesses to adopt Splunk SOAR.
  • Users find it complex to learn Splunk SOAR, often needing support to navigate its features and configurations.
  • Users find a significant lack of guidance, requiring external help to understand complex workflows and configurations.
  • Users face poor customer support, making it challenging to resolve issues quickly and efficiently.
  • Users find the complex implementation of Splunk SOAR to be time-consuming and often requiring significant resources and expertise.

What Are Recent G2 Reviews of Splunk SOAR (Security Orchestration, Automation and Response)?

What Are G2 Users Discussing About Splunk SOAR (Security Orchestration, Automation and Response)?

D3 Security

D3 stands at the forefront of AI-powered security, providing real-time, autonomous SOC solutions that help organizations stay ahead of cyber threats. By merging autonomous investigation and triage with AI-guided remediation, D3 is delivering AI-powered, human-led cyber security solutions. Morpheus is D3 Security’s fully autonomous SOC solution that triages, investigates, and responds to every alert, 24/7. Morpheus covers 100% of your alerts — no exceptions — so your team never has to choose between chasing false positives or risking a breach. It triages 95% of alerts in under two minutes, integrating seamlessly with any SIEM, XDR, or security stack. Unlike traditional SOAR platforms, Morpheus doesn’t need endless playbook tuning; it can build response workflows on the fly, specific to your security stack. The result? Zero alert fatigue, fewer missed threats, and a dramatic boost in SOC efficiency, powered by a data privacy-friendly and SecOps-focused AI model.

Average Rating: 4.2/5.0

Total Reviews: 64

How Do G2 Users Rate D3 Security?

  • Automated Remediation: 8.3/10 (Category avg: 8.7/10)
  • Quality of Support: 9.0/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.2/10 (Category avg: 8.6/10)
  • Workflow Automation: 6.7/10 (Category avg: 8.7/10)

Who Is the Company Behind D3 Security?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 49% Large, 41% Medium

What Are Recent G2 Reviews of D3 Security?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated