Best Risk-Based Vulnerability Management Software for Small Business

How Many Risk-Based Vulnerability Management Software Products Does G2 Track?

Total Products under this Category: 222

Category Stats (Nov 2026)

  • Average Rating: 4.5/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: BMC Helix Remediate (+17.94%) - Among all products in this category, BMC Helix Remediate recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Risk-Based Vulnerability Management Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,200+ Authentic Reviews
  • 222+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

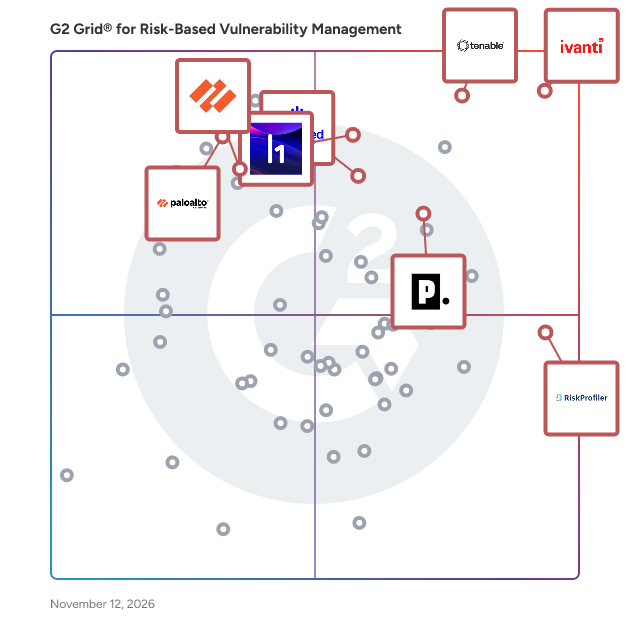
G2 Grid® for Risk-Based Vulnerability Management Software

G2 Grid® for Risk-Based Vulnerability Management Software plotting products by satisfaction and market presence

Highlighted products: Ivanti Autonomous Endpoint Management, Tenable Vulnerability Management, Palo Alto Cortex XSIAM, RiskProfiler - External Threat Exposure Management, H1 Platform, Pentera, Recorded Future, and Cortex Cloud.

Underlying data: [Grid® JSON](https://www.g2.com/categories/risk-based-vulnerability-management/grids.json?focus%5B%5D=ivanti-autonomous-endpoint-management&focus%5B%5D=tenable-vulnerability-management&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=h1-platform&focus%5B%5D=pentera&focus%5B%5D=recorded-future&focus%5B%5D=cortex-cloud&segment=small-business)

Ivanti Autonomous Endpoint Management

Ivanti Autonomous Endpoint Management is a software designed to automate and simplify the management of devices throughout their lifecycle. The software provides capabilities for endpoint discovery, configuration, security, monitoring, and remediation across various platforms, including Windows, macOS, Linux, and mobile devices. It enables organizations to reduce manual IT workloads by leveraging automation for patch management, software distribution, compliance enforcement, and device provisioning. The software also offers insights into device health and usage, helping businesses address vulnerabilities, ensure policy adherence, and maintain endpoint performance while supporting remote and hybrid work environments. Ivanti Autonomous Endpoint Management aims to improve operational efficiency by centralizing endpoint administration and minimizing risks associated with unmanaged or unpatched devices.

Average Rating: 4.3/5.0

Total Reviews: 410

How Do G2 Users Rate Ivanti Autonomous Endpoint Management?

  • Has the product been a good partner in doing business?: 8.5/10 (Category avg: 9.2/10)
  • Reporting: 8.3/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 8.3/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Ivanti Autonomous Endpoint Management?

  • Seller: Ivanti
  • Company Website:
  • Year Founded: 1985
  • HQ Location: South Jordan, UT
  • LinkedIn® Page: www.linkedin.com
    3,026 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 45% Large, 34% Medium

What Do G2 Reviewers Say About Ivanti Autonomous Endpoint Management?

AI-generated summary from verified user reviews

Pros
  • Users value the strong automation features of Ivanti, which simplify patching and improve system management efficiency.
  • Users value the automation and intelligence features of Ivanti for enhancing efficiency and proactive issue management.
  • Users value the strong automation and self-healing features of Ivanti, enhancing efficiency and device management visibility.
  • Users value the access ease of Ivanti Autonomous Endpoint Management, simplifying integration across various operating systems effortlessly.
  • Users value the reliable Apple device management that prevents locked phones and enhances functionality through easy implementation.
Cons
  • Users experience communication delays, particularly in support responsiveness, impacting troubleshooting during critical updates.
  • Users experience feature issues with a cluttered UI, slow performance, and challenging setup and customization processes.
  • Users find the UI cluttered and non-intuitive, making navigation and access to tools frustrating and inefficient.
  • Users experience slow performance with Ivanti when managing large device counts, impacting efficiency during tasks.
  • Users find the complexity of Ivanti Autonomous Endpoint Management challenging due to a steep learning curve and cluttered UI.

What Are Recent G2 Reviews of Ivanti Autonomous Endpoint Management?

What Are G2 Users Discussing About Ivanti Autonomous Endpoint Management?

Tenable Vulnerability Management

Tenable Vulnerability Management provides a risk-based approach to identifying, prioritizing, and remediating vulnerabilities across your entire attack surface. Powered by Nessus technology and AI-driven analytics, it goes beyond CVSS scores to assess exploitability, asset criticality, and business impact—so you can focus on what matters most. With continuous visibility, automated scanning, and real-time risk insights, security teams can quickly expose and close critical vulnerabilities before they’re exploited. Advanced asset identification ensures accurate tracking in dynamic environments, while intuitive dashboards, comprehensive reporting, and seamless third-party integrations help streamline workflows. As a cloud-based solution, Tenable Vulnerability Management scales with your organization, empowering security teams to maximize efficiency, reduce risk, and improve resilience against evolving threats.

Average Rating: 4.6/5.0

Total Reviews: 145

How Do G2 Users Rate Tenable Vulnerability Management?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.2/10)
  • Reporting: 8.0/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 9.1/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 9.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Tenable Vulnerability Management?

  • Seller: Tenable
  • Company Website:
  • HQ Location: Columbia, MD
  • LinkedIn® Page: www.linkedin.com
    2,361 employees on LinkedIn®
  • Ownership: NASDAQ: TENB

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 51% Large, 33% Medium

What Do G2 Reviewers Say About Tenable Vulnerability Management?

AI-generated summary from verified user reviews

Pros
  • Users highlight the user-friendly interface of Tenable Vulnerability Management, making vulnerability management straightforward and efficient.
  • Users value the scanning efficiency of Tenable Vulnerability Management for its comprehensive scanning and powerful prioritization capabilities.
  • Users value the effective vulnerability identification capabilities of Tenable Vulnerability Management, enhancing their security posture efficiently.
  • Users value the automated scanning features of Tenable Vulnerability Management for their efficiency and thoroughness.
  • Users value the robust scanning capabilities and intuitive reporting features of Tenable Vulnerability Management for effective vulnerability management.
Cons
  • Users find the platform to be expensive, complicating management for organizations with limited budgets or dynamic infrastructures.
  • Users find the pricing issues with Tenable Vulnerability Management to be complex and prohibitive for their budgets.
  • Users find the complexity of Tenable Vulnerability Management challenging, particularly in managing reports and licensing.
  • Users find the reporting feature inadequate, requiring external processing for more detailed vulnerability management insights.
  • Users find the reporting feature limited, requiring external processing for more detailed vulnerability management insights.

What Are Recent G2 Reviews of Tenable Vulnerability Management?

What Are G2 Users Discussing About Tenable Vulnerability Management?

Palo Alto Cortex XSIAM

Product Description: Palo Alto Networks' Cortex XSIAM is an AI-driven security operations platform designed to transform traditional Security Operations Centers by integrating and automating key functions such as data centralization, threat detection, and incident response. By leveraging machine learning and automation, it enables organizations to detect and respond to threats more efficiently, reducing manual workloads and improving overall security posture. Key Features and Functionality: - Data Centralization: Aggregates data from various sources into a unified platform, providing comprehensive visibility across the enterprise. - AI-Powered Threat Detection: Utilizes machine learning algorithms to identify anomalies and potential threats in real-time. - Automated Incident Response: Streamlines response processes through automation, enabling rapid mitigation of security incidents. - Integrated SOC Capabilities: Combines functions such as Extended Detection and Response , Security Orchestration, Automation, and Response , Attack Surface Management , and Security Information and Event Management into a cohesive platform, eliminating the need for multiple disparate tools. - Scalability: Designed to handle large volumes of data and adapt to the evolving needs of modern enterprises. Primary Value and Problem Solved: Cortex XSIAM addresses the challenges of disjointed data, weak threat defense, and heavy reliance on manual work in traditional SOCs. By centralizing data and automating security operations, it simplifies processes, enhances threat detection accuracy, and accelerates incident response times. This transformation enables organizations to proactively outpace threats, reduce operational costs, and achieve a more robust security posture.

Average Rating: 4.4/5.0

Total Reviews: 109

How Do G2 Users Rate Palo Alto Cortex XSIAM?

  • Has the product been a good partner in doing business?: 8.5/10 (Category avg: 9.2/10)
  • Reporting: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Palo Alto Cortex XSIAM?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Large, 36% Medium

What Do G2 Reviewers Say About Palo Alto Cortex XSIAM?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Palo Alto Cortex XSIAM, benefiting from its intuitive interface and seamless integration.
  • Users value the advanced threat detection capabilities of Palo Alto Cortex XSIAM, ensuring both known and unknown threats are managed effectively.
  • Users value the seamless integrations of Palo Alto Cortex XSIAM, enhancing overall functionality across various platforms.
  • Users value the unified console of Palo Alto Cortex XSIAM for simplifying security management across endpoints, network, and cloud.
  • Users value the single console integration, highlighting its ease of use and reliability for threat detection.
Cons
  • Users find the Cortex XSIAM to be very expensive compared to other solutions, impacting overall satisfaction.
  • Users find the difficult learning curve of Palo Alto Cortex XSIAM a challenge due to its complexity and setup.
  • Users find the complexity of the console overwhelming, requiring significant time and expertise to navigate effectively.
  • Users report integration issues with Palo Alto Cortex XSIAM, facing challenges with non-native equipment and log maintenance.
  • Users find the UX improvement of Palo Alto Cortex XSIAM lacking in customization and intuitive design for features.

What Are Recent G2 Reviews of Palo Alto Cortex XSIAM?

What Are G2 Users Discussing About Palo Alto Cortex XSIAM?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

RiskProfiler - External Threat Exposure Management

RiskProfiler is an advanced cybersecurity platform purpose-built for Continuous Threat Exposure Management (CTEM). It unifies external, cloud, vendor, and brand risk intelligence into a single ecosystem—providing organizations with real-time visibility, contextual threat insights, and actionable remediation guidance. Through its integrated suite, External Attack Surface Managemnet, Third_party Risk Management, Cloud Attack Surface Management, and Brand Risk Protection; the platform continuously discovers, classifies, and evaluates external-facing assets and risks across the internet, multi-cloud environments, and third-party ecosystems. Powered by AI-enabled risk questionnaires, RiskProfiler automates the exchange, validation, and scoring of security assessments, dramatically accelerating third-party due diligence and compliance validation. The platform’s context-enriched graph engine correlates vulnerabilities, exposures, and configurations with real-world threat data, revealing how attackers might exploit an organization’s digital footprint. Its newly enhanced Cyber Threat Intelligence (CTI) module provides live insights into industry-specific attack trends, threat actor profiles, and evolving TTPs, directly embedded within the dashboard. By analyzing CVEs, IOCs, and exploit patterns, it maps these to relevant assets and potential attack paths, enabling focused, prioritized mitigation. From identifying exposed cloud resources across AWS, Azure, and Google Cloud to uncovering brand impersonation, phishing campaigns, or logo abuse, RiskProfiler delivers unified visibility and continuous monitoring that extends beyond the perimeter. It helps organizations anticipate, contextualize, and neutralize threats before they turn into breaches, transforming exposure management into a truly intelligent, predictive defense capability.

Average Rating: 5.0/5.0

Total Reviews: 135

How Do G2 Users Rate RiskProfiler - External Threat Exposure Management?

  • Has the product been a good partner in doing business?: 9.9/10 (Category avg: 9.2/10)
  • Reporting: 9.9/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 9.9/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 9.9/10 (Category avg: 8.8/10)

Who Is the Company Behind RiskProfiler - External Threat Exposure Management?

  • Seller: Riskprofiler
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Rock Hill , US
  • LinkedIn® Page: www.linkedin.com
    35 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Security Consultant
  • Top Industries: Information Technology and Services, Design
  • Company Size: 65% Medium, 30% Small

What Do G2 Reviewers Say About RiskProfiler - External Threat Exposure Management?

AI-generated summary from verified user reviews

Pros
  • Users value the multi-dimensional threat intelligence of RiskProfiler, enabling efficient management of external threats and vendor risks.
  • Users value the seamless integration features of RiskProfiler, enhancing real-time monitoring and adaptability in their workflows.
  • Users praise the fast and efficient customer support of RiskProfiler, enhancing their overall experience and threat management.
  • Users value the ease of use of RiskProfiler, as it seamlessly integrates and enhances external threat management.
  • Users highlight the easy setup of RiskProfiler, facilitating quick implementation and seamless integration for effective threat management.
Cons
  • Users face a steep learning curve with RiskProfiler, needing sufficient time for training and customization.
  • Users find the complexity of RiskProfiler challenging, requiring time for training and adjustment to navigate effectively.
  • Users find the difficult learning curve challenging, requiring significant time and training for effective platform use.
  • Users find a steep learning curve with RiskProfiler, requiring time and training for effective use.
  • Users find the complex setup of RiskProfiler challenging, hindering smooth adoption and integration for non-specialist teams.

What Are Recent G2 Reviews of RiskProfiler - External Threat Exposure Management?

H1 Platform

HackerOne is a global leader in Continuous Threat Exposure Management (CTEM) and the only solution provider that pairs the simultaneous trust of the Fortune 500 and the world's largest community of security researchers to secure the AI-native enterprise. The H1 Platform unites agentic AI solutions with security researchers ingenuity to continuously discover, validate, prioritize, and remediate exposures across code, cloud, and AI systems. Through solutions like bug bounty, vulnerability disclosure, agentic pentesting, AI red teaming, and code security, HackerOne delivers measurable, continuous reduction of cyber risk for enterprises. Industry leaders, including Anthropic, Crypto.com, General Motors, Goldman Sachs, Lufthansa, Uber, UK Ministry of Defence, and the U.S. Department of Defense, trust HackerOne to safeguard their digital ecosystems. HackerOne was recognized in Gartner’s Emerging Tech Impact Radar: AI Cybersecurity Ecosystem report for its leadership in AI Security Testing.

Average Rating: 4.5/5.0

Total Reviews: 107

How Do G2 Users Rate H1 Platform?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.2/10)
  • Reporting: 10.0/10 (Category avg: 8.8/10)
  • Risk-Prioritization: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind H1 Platform?

  • Seller: HackerOne
  • Company Website:
  • Year Founded: 2012
  • HQ Location: San Francisco, California
  • LinkedIn® Page: www.linkedin.com
    7,090 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 47% Large, 34% Medium

What Do G2 Reviewers Say About H1 Platform?

AI-generated summary from verified user reviews

Pros
  • Users highlight the ease of use of H1 Platform, making it simple to manage and track bounty programs effectively.
  • Users highlight the helpful customer service of HackerOne, ensuring effective assistance and smooth platform navigation.
  • Users value the seamless collaboration facilitated by H1 Platform, enhancing communication with security researchers and team members.
  • Users value the enhanced security protection of H1 Platform, facilitating proactive vulnerability management and team collaboration.
  • Users value the exceptional customer support of H1 Platform, enhancing their overall experience and program management.
Cons
  • Users find the complexity issues in triaging and credentials management to be a challenge, impacting overall efficiency.
  • Users note the expensive pricing of H1 Platform, which may challenge smaller organizations despite its value.
  • Users face time management challenges with inconsistent triage speed and quality, impacting overall efficiency on the H1 Platform.
  • Users experience poor customer support with long ticket resolutions and unresolved queries impacting their overall satisfaction.
  • Users find the poor interface design of H1 Platform confusing and difficult to navigate, often missing reports.

What Are Recent G2 Reviews of H1 Platform?

What Are G2 Users Discussing About H1 Platform?

Pentera

Pentera is the category leader for Automated Security Validation, allowing every organization to test with ease the integrity of all cybersecurity layers, unfolding true, current security exposures at any moment, at any scale. Thousands of security professionals and service providers around the world use Pentera to guide remediation and close security gaps before they are exploited. Its customers include Casey's General Stores, Emeria, LuLu International Exchange, IP Telecom PT, BrewDog, City National Bank, Schmitz Cargobull, and MBC Group. Pentera is backed by leading investors such as K1 Investment Management, Insight Partners, Blackstone, Evolution Equity Partners, and AWZ. Visit https://pentera.io for more information.

Average Rating: 4.6/5.0

Total Reviews: 195

How Do G2 Users Rate Pentera?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Reporting: 7.8/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 8.3/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Pentera?

  • Seller: Pentera
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    460 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Government Administration, Computer & Network Security
  • Company Size: 52% Large, 34% Medium

What Do G2 Reviewers Say About Pentera?

AI-generated summary from verified user reviews

Pros
  • Users love the user-friendly UI of Pentera, which simplifies penetration testing and enhances overall efficiency.
  • Users value the effective vulnerability identification and remediation suggestions, enhancing their overall security posture.
  • Users appreciate the fully automated features of Pentera, noting its quick implementation and user-friendly interface.
  • Users value the responsive customer support of Pentera, enhancing overall satisfaction and efficiency in vulnerability management.
  • Users value the realistic testing capabilities of Pentera, enhancing company network security and response effectiveness.
Cons
  • Users find the reporting inadequate, lacking detail for enterprise-scale insights and missing multilingual support.
  • Users are disappointed with the lack of a robust RBAC system for effective user access control in Pentera.
  • Users desire improvements in handling false positives, but overall satisfaction remains high with current functionalities.
  • Users note that reporting lacks robustness, especially for enterprise-level insights and multilingual support.
  • Users express concerns about the missing features, such as insufficient vulnerabilities, limited RBAC, and lack of translation.

What Are Recent G2 Reviews of Pentera?

Cortex Cloud

Cortex Cloud by Palo Alto Networks, the next version of Prisma Cloud, understands a unified security approach is essential for effectively addressing AppSec, CloudSec, and SecOps. Connecting cloud security and SOC workflows enables teams to achieve holistic visibility, trace risk across the lifecycle, and correlate real-time threat activity with development and runtime contexts. Cortex Cloud is a unified platform built on three core pillars: data integration, AI-driven intelligence, and automation. Now you can safeguard applications, data, and infrastructure across multicloud and hybrid environments with a unified data model that consolidates telemetry from code, runtime, identity, and endpoints, all into a single data source. Empower teams with precise, AI-powered insights and 2200+ machine learning models to identify and stop zero-day threats with real-time advanced threat detection and response. And automate with 1000+ prebuilt playbooks across your cloud stack to reduce manual workloads, accelerate remediations, and cut response times tenfold. Cortex Cloud delivers more than tools—it transforms how organizations secure their cloud environments.

Average Rating: 4.1/5.0

Total Reviews: 126

How Do G2 Users Rate Cortex Cloud?

  • Has the product been a good partner in doing business?: 8.0/10 (Category avg: 9.2/10)
  • Reporting: 7.8/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 7.5/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 8.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Cortex Cloud?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Large, 32% Medium

What Do G2 Reviewers Say About Cortex Cloud?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Cortex Cloud, promoting faster performance monitoring and streamlined decision-making.
  • Users appreciate the centralized data and analytics of Cortex Cloud, enhancing efficiency and decision-making across security operations.
  • Users appreciate the centralized security management of Cortex Cloud, streamlining workload management and enhancing operational efficiency.
  • Users appreciate the centralized visibility of Cortex Cloud, enhancing data monitoring and facilitating better decision-making.
  • Users value the seamless integration of Cortex Cloud, enhancing efficiency in managing resources across different environments.
Cons
  • Users note the expensive pricing of Cortex Cloud, making it less accessible for smaller teams or businesses.
  • Users find the difficult learning curve of Cortex Cloud can slow down adoption for new teams and users.
  • Users find the steep learning curve of Cortex Cloud challenging, especially for those unfamiliar with its advanced features.
  • Users express concerns over high and unclear pricing, which complicates budgeting and can escalate with scaling needs.
  • Users experience a complex setup with Cortex Cloud, often struggling with intuitive navigation and steep learning curves.

What Are Recent G2 Reviews of Cortex Cloud?

Recorded Future

Recorded Future is the world’s largest threat intelligence company. Recorded Future’s Intelligence Cloud provides end-to-end intelligence across adversaries, infrastructure, and targets. Indexing the internet across the open web, dark web, and technical sources, Recorded Future provides real-time visibility into an expanding attack surface and threat landscape, empowering clients to act with speed and confidence to reduce risk and securely drive business forward. Headquartered in Boston with offices and employees around the world, Recorded Future works with over 1,900 businesses and government organizations across 80 countries to provide real-time, unbiased and actionable intelligence. Learn more at recordedfuture.com.

Average Rating: 4.5/5.0

Total Reviews: 251

How Do G2 Users Rate Recorded Future?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.2/10)
  • Reporting: 8.4/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 8.9/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 8.8/10 (Category avg: 8.8/10)

Who Is the Company Behind Recorded Future?

  • Seller: Recorded Future
  • Company Website:
  • Year Founded: 2009
  • HQ Location: Somerville, US
  • LinkedIn® Page: www.linkedin.com
    1,150 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Cyber Threat Intelligence Analyst, Threat Intelligence Analyst
  • Top Industries: Financial Services, Computer & Network Security
  • Company Size: 61% Large, 21% Medium

What Do G2 Reviewers Say About Recorded Future?

AI-generated summary from verified user reviews

Pros
  • Users find Recorded Future to be easy to use, with a smooth setup and helpful support throughout the process.
  • Users appreciate the impressive API connectivity and diverse threat intelligence sources of Recorded Future, enhancing workflow automation.
  • Users value the world-class threat intelligence of Recorded Future, benefiting from comprehensive insights and automation capabilities.
  • Users value the world-class threat detection of Recorded Future, leveraging diverse intelligence for enhanced security insights.
  • Users commend the world-class threat intelligence of Recorded Future, providing deep and valuable insights for cybersecurity professionals.
Cons
  • Users find the complexity of Recorded Future overwhelming initially, requiring significant time to learn and adapt.
  • Users feel the product is expensive, with licensing limitations affecting overall usability and access to necessary features.
  • Users find the learning curve steep, requiring significant time and training to effectively utilize Recorded Future's features.
  • Users find the insufficient information in Recorded Future limits the product's effectiveness and context for breaches.
  • Users find the difficult learning curve for Recorded Future challenging, especially for those new to the platform.

What Are Recent G2 Reviews of Recorded Future?

What Are G2 Users Discussing About Recorded Future?

Qualys VMDR

Qualys VMDR is an all-in-one risk-based vulnerability management solution that quantifies cyber risk. It gives organizations unprecedented insights into their risk posture and provides actionable steps to reduce risk. It also gives cybersecurity and IT teams a shared platform to collaborate, and the power to quickly align and automate no-code workflows to respond to threats with automated remediation and integrations with ITSM solutions such as ServiceNow.

Average Rating: 4.4/5.0

Total Reviews: 165

How Do G2 Users Rate Qualys VMDR?

  • Has the product been a good partner in doing business?: 8.5/10 (Category avg: 9.2/10)
  • Reporting: 8.3/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 8.7/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 8.5/10 (Category avg: 8.8/10)

Who Is the Company Behind Qualys VMDR?

  • Seller: Qualys
  • Year Founded: 1999
  • HQ Location: Foster City, CA
  • LinkedIn® Page: www.linkedin.com
    3,637 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Large, 29% Medium

What Do G2 Reviewers Say About Qualys VMDR?

AI-generated summary from verified user reviews

Pros
  • Users value the responsive customer support of Qualys VMDR, enhancing their ability to manage vulnerabilities effectively.
  • Users value the robust security features of Qualys VMDR, enhancing security and streamlining asset management effectively.
  • Users value the efficacy of vulnerability detection in Qualys VMDR, enhancing security through swift identification and remediation.
  • Users value the swift identification of vulnerabilities in Qualys VMDR, enhancing their security and response efficiency.
  • Users value the real-time alerting system of Qualys VMDR for promptly notifying them of critical vulnerabilities.
Cons
  • Users find the initial complexity of Qualys VMDR challenging, especially new users navigating the interface.
  • Users find the interface complex, especially for newcomers, making initial navigation challenging.
  • Users find the complex setup of Qualys VMDR challenging, particularly for those unfamiliar with the interface.
  • Users find the difficult learning curve challenging, especially for new users adapting to the interface.
  • Users find the interface complex, particularly challenging for new users during initial stages of use.

What Are Recent G2 Reviews of Qualys VMDR?

What Are G2 Users Discussing About Qualys VMDR?

Microsoft Defender Vulnerability Management

Defender Vulnerability Management delivers asset visibility, intelligent assessments, and built-in remediation tools for Windows, macOS, Linux, Android, iOS, and network devices. Leveraging Microsoft threat intelligence, breach likelihood predictions, business contexts, and devices assessments, Defender Vulnerability Management rapidly and continuously prioritizes the biggest vulnerabilities on your most critical assets and provides security recommendations to mitigate risk. Reduce risk with continuous vulnerability assessment, risk-based prioritization, and remediation. Defender Vulnerability Management is available for cloud workloads and endpoints. Defender for Endpoint Plan 2 customers can access advanced vulnerability management capabilities with the Defender Vulnerability Management add-on, now generally available.

Average Rating: 4.4/5.0

Total Reviews: 34

How Do G2 Users Rate Microsoft Defender Vulnerability Management?

  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.2/10)
  • Reporting: 8.7/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 8.8/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 8.8/10 (Category avg: 8.8/10)

Who Is the Company Behind Microsoft Defender Vulnerability Management?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT
  • Phone: +1 (877) 276-2464

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 41% Small, 35% Large

What Are Recent G2 Reviews of Microsoft Defender Vulnerability Management?

SecOps Solution

SecOps Solution is a next-gen, agentless patch and vulnerability management platform that helps organizations fix vulnerabilities fast — without agents, manual effort, or complex setups. We automate patching across operating systems and third-party applications, including remote and on-prem devices — all in a fraction of the time traditional tools take.

Average Rating: 4.8/5.0

Total Reviews: 52

How Do G2 Users Rate SecOps Solution?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Reporting: 9.7/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 9.7/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 9.7/10 (Category avg: 8.8/10)

Who Is the Company Behind SecOps Solution?

Who Uses This Product?

  • Top Industries: Financial Services, Computer Software
  • Company Size: 59% Small, 38% Medium

What Do G2 Reviewers Say About SecOps Solution?

AI-generated summary from verified user reviews

Pros
  • Users value the intuitive centralized dashboard of SecOps Solution, simplifying vulnerability and patch management significantly.
  • Users commend the supportive customer support team of SecOps Solution for their responsiveness and effective communication.
  • Users value the detailed reporting of SecOps Solution, enhancing communication about security status to stakeholders.
  • Users commend SecOps Solution for their fast and professional service, providing clear reports and comprehensive security tests.
  • Users value the reporting efficiency of SecOps Solution, enabling clear communication of security status to stakeholders.

What Are Recent G2 Reviews of SecOps Solution?

What Are G2 Users Discussing About SecOps Solution?

VulScan

Automated Vulnerability Scanning. Affordably Priced For Everyone! With almost 70 new hidden vulnerabilities identified every day, you would need to be a super hero with X-ray vision to find them all. Or, you can let VulScan do it for you. VulScan is purpose-built for MSPs and for IT Departments that handle their own IT security. It has all the features you need for both internal and external vulnerability management, but without all the complexity found in older solutions. Best of all, VulScan is priced so that cost is no longer a barrier to scanning as many assets as you need, as frequently as you want. That’s why our slogan is “Vulnerability Management For The Rest of Us! VulScan is an affordable cloud-based vulnerability management platform. It includes the software needed to spin up an unlimited number of virtual network scanner appliances using Hyper-V or VMWare, and a cloud-based portal to control the scanners and manage the discovered issues. For internal network scanning, the appliances can be installed on any existing computer that has excess capacity on the network, or installed on a dedicated box to be permanently installed. You can add multiple scanners and configure them each to scan separate parts of the network to get even faster results pushed into the same client site dashboard at no additional cost. For external scanning, the appliances are installed on the MSP’s data center or other remote location and “pointed” to the public facing IP addresses of the target network.

Average Rating: 4.1/5.0

Total Reviews: 121

How Do G2 Users Rate VulScan?

  • Has the product been a good partner in doing business?: 8.2/10 (Category avg: 9.2/10)
  • Reporting: 7.2/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 7.6/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 7.5/10 (Category avg: 8.8/10)

Who Is the Company Behind VulScan?

  • Seller: Kaseya
  • Company Website:
  • Year Founded: 2000
  • HQ Location: Miami, FL
  • LinkedIn® Page: www.linkedin.com
    5,483 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 66% Small, 32% Medium

What Do G2 Reviewers Say About VulScan?

AI-generated summary from verified user reviews

Pros
  • Users love the ease of use of VulScan, praising its simple interface and intuitive scheduling for scanning and reporting.
  • Users value the thorough scanning and intuitive UI of VulScan, enhancing both ease of use and security insights.
  • Users value the detailed reporting features of VulScan, which provide actionable insights and facilitate client communication.
  • Users appreciate the in-depth reporting features of VulScan, enabling easy identification and justification of security vulnerabilities.
  • Users value the scanning efficiency of VulScan, appreciating its ease of use and comprehensive vulnerability reports.
Cons
  • Users criticize the inadequate reporting of VulScan, finding it overwhelming and lacking clear, actionable insights.
  • Users find the difficult UX of VulScan frustrating due to its outdated design and lack of organization features.
  • Users find the difficult setup of VulScan frustrating, with a confusing UI and cumbersome documentation requirements.
  • Users find the limited reporting options inadequate, complicating client communication and overall usability of VulScan.
  • Users are frustrated by the poor customer support from VulScan, experiencing delays and lack of resolution for issues.

What Are Recent G2 Reviews of VulScan?

AI-Native Continuous Offensive Security Platform

RidgeBot by Ridge Security is an AI-powered platform for continuous security validation that enables CISOs to minimize cyber risks from increasingly sophisticated and frequent cyberattacks by validating the cybersecurity posture and controls that protect attack surfaces. RidgeBot delivers continuous threat exposure management by automatically testing an organization’s entire Internet Protocol (IP)-based attack surfaces, including network infrastructure, applications, websites, IoT, and OT. RidgeBot pinpoints the most critical vulnerabilities using ethical hacking techniques. RidgeBot’s dynamic AI-powered decision-making capability supports many use cases, including DevSecOps, compliance, incident response verification, and custom attack simulations. RidgeBot maintains a library of over 36,000 plugins to launch complex penetration tests and attack simulations, with detailed reporting of results and remediation recommendation.

Average Rating: 4.5/5.0

Total Reviews: 98

How Do G2 Users Rate AI-Native Continuous Offensive Security Platform?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Reporting: 8.7/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 9.0/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 9.1/10 (Category avg: 8.8/10)

Who Is the Company Behind AI-Native Continuous Offensive Security Platform?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Small, 45% Medium

What Do G2 Reviewers Say About AI-Native Continuous Offensive Security Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the automation features of RidgeBot, which efficiently streamline security validation and prioritization of threats.
  • Users find the ease of use exceptional, praising its intuitive interface and straightforward setup for security tasks.
  • Users appreciate the efficiency of automated pentesting with RidgeBot, significantly reducing manual validation and saving time.
  • Users value the autonomous vulnerability testing of RidgeBot, significantly enhancing efficiency and risk assessment in security processes.
  • Users appreciate the efficiency of RidgeBot in automating penetration testing and prioritizing critical vulnerabilities effectively.
Cons
  • Users find the platform's setup to be complex and challenging, especially in customized or legacy environments.
  • Users find the complex setup of the AI-Native platform challenging, particularly for newcomers and unique environments.
  • Users feel there are several missing features, like improved API testing and custom reporting templates for compliance.
  • Users find the customer support lacking, often leaving them to troubleshoot issues independently.
  • Users find the poor documentation challenging, making initial setup and troubleshooting difficult, especially for new admins.

What Are Recent G2 Reviews of AI-Native Continuous Offensive Security Platform?

Arctic Wolf

Arctic Wolf® is the cybersecurity and AI company that ends cyber risk by transforming it into business resilience. Powered by the Aurora® Superintelligence Platform, Arctic Wolf delivers modern security operations built on proprietary AI and decades of real-world expertise to manage and mitigate cyber threats. The platform is built on the Swarm of Experts™, which coordinates specialized AI agents across core security operations functions. The Security Operations Graph™ connects real-world telemetry and customer context to every workflow. The AI Trust Engine™ validates outcomes and keeps human experts in the loop. Arctic Wolf serves businesses of all sizes looking to strengthen their cybersecurity posture. IT and security teams turn to Arctic Wolf to streamline operations, gain a clearer view of their security landscape, and build resilience against cyberattacks. Arctic Wolf's Aurora-branded solutions include Aurora® Managed Detection and Response (MDR), which provides 24x7 monitoring and rapid threat detection and response. Aurora® Attack Surface Management and Aurora® Vulnerability Management help organizations identify and remediate vulnerabilities to reduce their attack surface. Aurora® Endpoint Security safeguards devices against threats. Aurora® Security Awareness and Training helps employees reduce human error in cybersecurity. Aurora® Incident Response helps organizations respond when a security incident occurs. The Concierge Security® Team delivers personalized support, working closely with organizations to understand their unique challenges and build tailored strategies for stronger cyber resilience. By combining AI-driven automation with expert validated precision, Arctic Wolf helps organizations confidently manage cyber risk, so they can operate with control and the freedom to innovate.

Average Rating: 4.7/5.0

Total Reviews: 276

How Do G2 Users Rate Arctic Wolf?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.2/10)
  • Reporting: 9.5/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 9.6/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 9.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Arctic Wolf?

Who Uses This Product?

  • Who Uses This: IT Manager, IT Director
  • Top Industries: Hospital & Health Care, Information Technology and Services
  • Company Size: 71% Medium, 20% Large

What Do G2 Reviewers Say About Arctic Wolf?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the quick and proactive customer support from Arctic Wolf, enhancing their security management experience.
  • Users value Arctic Wolf's proactive threat detection, experiencing enhanced security and peace of mind through expert support.
  • Users commend Arctic Wolf for its hands-on and proactive security approach, acting as an extension of their team.
  • Users appreciate the ease of use of Arctic Wolf, highlighting its seamless onboarding and user-friendly platform.
  • Users value the proactive alerts from Arctic Wolf, enhancing security while freeing up time for critical tasks.
Cons
  • Users note the high cost of Arctic Wolf, which may be out of budget for some potential customers.
  • Users experience a significant number of false positives with Arctic Wolf, leading to increased investigation time and ticket generation.
  • Users experience a steep learning curve initially, though support during onboarding helps navigate the complexities.
  • Users face overwhelming cybersecurity risks with Arctic Wolf, resulting in many alerts and complex reports to manage.
  • Users face dashboard issues that require adjustment, but support is available to help navigate the complexities.

What Are Recent G2 Reviews of Arctic Wolf?

What Are G2 Users Discussing About Arctic Wolf?

Cisco Vulnerability Management (formerly Kenna.VM)

Cisco Vulnerability Management (formerly Kenna.VM), the original SaaS risk-based vulnerability management platform, prioritizes vulnerabilities that pose a real risk, enabling Security and IT teams to focus their limited resources and remediate more efficiently. Cisco’s data science-driven prioritization evaluates both enterprise data and a wealth of data on real-world exploit activity and translates that context into actionable intelligence to guide remediation.

Average Rating: 4.3/5.0

Total Reviews: 200

How Do G2 Users Rate Cisco Vulnerability Management (formerly Kenna.VM)?

  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.2/10)
  • Reporting: 8.5/10 (Category avg: 8.8/10)
  • Vulnerability Intelligence: 8.7/10 (Category avg: 8.7/10)
  • Risk-Prioritization: 9.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Cisco Vulnerability Management (formerly Kenna.VM)?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO
  • Phone: 847-678-6600

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 76% Large, 17% Medium

What Are Recent G2 Reviews of Cisco Vulnerability Management (formerly Kenna.VM)?

What Are G2 Users Discussing About Cisco Vulnerability Management (formerly Kenna.VM)?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated
Reviews & FAQs

Reviews Summary: The Best Risk-Based Vulnerability Management Software for Small-Business Businesses

Thanks to 5275 Risk-Based Vulnerability Management software reviews and associated data from users working for small-sized companies, at G2 we have some of the most definitive data on the best Risk-Based Vulnerability Management software for the smaller space. We have identified 24 individual Risk-Based Vulnerability Management products offering the features, pricing and support that Small-Business companies look for when comparing Risk-Based Vulnerability Management software and solutions. These reviews are generated using the qualitative and quantitative feedback from G2 members working in small-sized companies and who have used these Risk-Based Vulnerability Management software products.

When G2 reviewers submit their Risk-Based Vulnerability Management software reviews, they often provide information on the type of company they work for and what market segment they belong to. We break these different market segments into three distinct groups:

  • Small Business Risk-Based Vulnerability Management Software Reviews (< 50 employees)
  • smaller Risk-Based Vulnerability Management Software Reviews (51-1,000 employees)
  • Enterprise Risk-Based Vulnerability Management Software Reviews (1,001+ employees)

smaller businesses have their own unique requirements when it comes to Risk-Based Vulnerability Management software compared to small or enterprise companies. That is why these individual small-sized company Risk-Based Vulnerability Management software reviews are especially helpful when comparing product set up, ease of use and overall cost.

Below you will find FAQs and review snippets for Risk-Based Vulnerability Management software products that work well in smaller environments. These reviews are written by real G2 users working for these Small-Business companies who have real-world experience with these Risk-Based Vulnerability Management software products.

FAQs About Risk-Based Vulnerability Management Software for Small-Business Businesses

Q. What are the best Risk-Based Vulnerability Management software products for small-sized businesses, according to G2 reviewers?
  • Ivanti Autonomous Endpoint Management - 4.4-stars, 60 reviews (20% from smaller reviewers)
  • Tenable Vulnerability Management - 4.7-stars, 17 reviews (15% from smaller reviewers)
  • RiskProfiler - External Threat Exposure Management - 5.0-stars, 39 reviews (33% from smaller reviewers)
  • Pentera - 4.6-stars, 13 reviews (19% from smaller reviewers)
  • Cortex Cloud - 4.4-stars, 12 reviews (27% from smaller reviewers)
Q. What are the least-liked Risk-Based Vulnerability Management software products for professionals at small-sized companies, based on the overall G2 rating?
  • HostedScan.com - 4.2-stars, 10 reviews (83% from smaller reviewers)
  • Tenable Security Center - 4.4-stars, 10 reviews (15% from smaller reviewers)
  • IBM QRadar EDR - 4.0-stars, 18 reviews (49% from smaller reviewers)
  • Fortra VM - 4.3-stars, 18 reviews (32% from smaller reviewers)
  • BugBase - 4.4-stars, 11 reviews (55% from smaller reviewers)
Q. What are the highest-rated Risk-Based Vulnerability Management software tool features according to employees at Small-Business companies?
  • Risk Scoring - 4.5-stars
  • Risk-Prioritization - 4.5-stars
  • Vulnerability Scanning - 4.5-stars
Q. What are the features that are rated lowest by employees at Small-Business companies?
  • Automated Remediation - 4.0-stars
  • Workflow Automation - 4.1-stars
  • Test Automation - 4.2-stars
Q. How many Risk-Based Vulnerability Management software reviews are from users working in smaller companies?

517 out of all Risk-Based Vulnerability Management software reviews on G2 are from users working in Small-Business companies (10%).

Here's What Reviewers Working at smaller Businesses Have to Say About Risk-Based Vulnerability Management Software

What Small-Business Professionals Liked What Small-Business Professionals Disliked

Qualys VMDR: “Ability to quickly prioritize Vulnerabilities and being able to present executive-friendly metrics with the usage of dynamic dashboards that showcase the riskiest areas of our customers”

Read Review

VulScan: “It didn't work very much. We never got it to watch rk and does not work without an h8ur long install and only if you have a domain controller”

Read Review

Semperis Purple Knight: “Although there are numerous tools capable of auditing Active Directory, Purple distinguishes itself by not only conducting audits but also offering detailed explanations for every vulnerability it uncovers. Additionally, it provides clear guidance on how to address these issues. Purple knight is also easy to implement, it leads you to give the missing permission, and is running pretty quick And the best of it, the tool is free, thank you Semperis.”

Read Review

Cyrisma: “I find it very difficult to navigate the system and setting up of the reports. There is limited device updating offered by CYRISMA. I have yet to get my system working after years of using and asking for help. There is minimal effort from CYRISMA customer success with the product. I had a call with the new account manager and have not heard back from him since the last call. Also, he knew I was having issues and yet he still thought it was good to follow up again in 3 months. I have yet to hear back from him to date. It has been a disappointing experience of the product support in order to have success with it. Could be a great product if I knew how it works. I am disappointed.”

Read Review

VulScan: “Friendly GUI console. Easy to work and easy to setup”

Read Review

Titania Nipper InfraSight: “I find it challenging that Titania Nipper InfraSight is a desktop-based application. It should be a web application.”

Read Review

Recommendations To Others Problems Solved & Benefits

Strobes Security: “Very reliable and the team behind this is very accommodative and support you in every situation.”

Read Review

Tenable Vulnerability Management: “Tenable Vulnerability Management provides a comprehensive view of vulnerability management, helping to determine the impact on the company and manage associated risks. I also value its user-friendly graphical interface and the organization of information in the modules.”

Read Review

Cisco Vulnerability Management (formerly Kenna.VM): “Good product”

Read Review

Ivanti Autonomous Endpoint Management: “Provides the ability to manage remote and on-prem devices easily. Can create different patching policies to ensure devices are properly patched, and build bots to perform self-healing, perform actions based on different query criteria. Edge intelligence is useful to pull realtime information off of devices and see who may be having issues before anything is reported.”

Read Review

InsightVM (Nexpose): “Don't forget to consider the cloud portion of InsightVM versus the on-prem only version (Nexpose). I've found the cloud portion allows for folks who don't need to be in the tool daily (managers and executives) to still get value without needing to learn a new tool. It is also super useful for dashboarding.”

Read Review

Tenable Vulnerability Management: “Tenable helps us identify, prioritize, and track vulnerabilities across our environment. This improves visibility, supports faster remediation, and reduces the risk of critical vulnerabilities remaining unresolved.”

Read Review