Best Application Security Posture Management (ASPM) Software for Medium-Sized Businesses

How Many Application Security Posture Management (ASPM) Software Products Does G2 Track?

Total Products under this Category: 50

Category Stats (Nov 2026)

  • Average Rating: 4.53/5 (↓0.02 vs Oct 2026) The average rating of products in this category, based on all submitted ratings

Last updated: November 01, 2026

How Does G2 Rank Application Security Posture Management (ASPM) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,300+ Authentic Reviews
  • 50+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

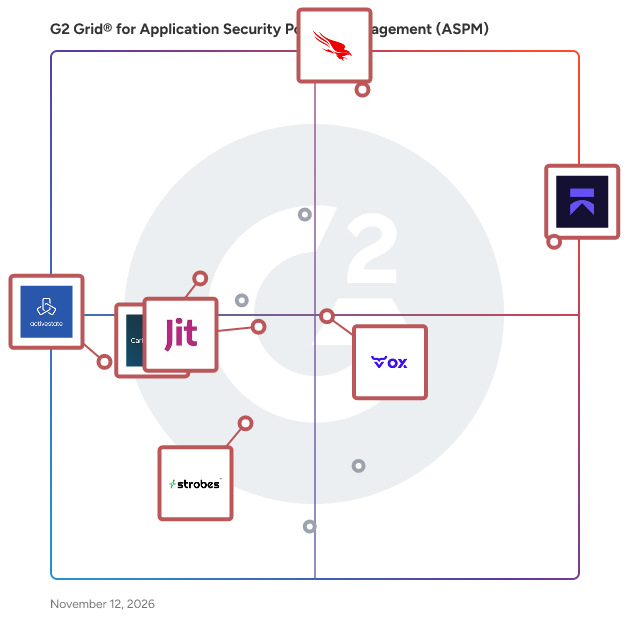
G2 Grid® for Application Security Posture Management (ASPM) Software

G2 Grid® for Application Security Posture Management (ASPM) Software plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Cloud Security, Aikido Security, OX Security, Strobes Security, Carbon Black App Control, Jit, and ActiveState.

Underlying data: [Grid® JSON](https://www.g2.com/categories/application-security-posture-management-aspm/grids.json?focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=aikido-security&focus%5B%5D=ox-security&focus%5B%5D=strobes-security&focus%5B%5D=carbon-black-app-control&focus%5B%5D=jit&focus%5B%5D=activestate&segment=mid-market)

CrowdStrike Falcon Cloud Security

Crowdstrike Falcon Cloud Security is the only CNAPP to stop breaches in the cloud Built for today’s hybrid and multi-cloud environments, Falcon Cloud Security protects the entire cloud attack surface - from code to runtime - by combining continuous agentless visibility with real-time detection and response. At runtime, Falcon Cloud Security delivers best-in-class cloud workload protection and real-time cloud detection and response (CDR) to stop active threats across hybrid environments. Integrated with the CrowdStrike Falcon platform, it correlates signals across endpoint, identity, and cloud to detect sophisticated cross-domain attacks that point solutions miss—enabling teams to respond faster and stop breaches in progress. To reduce risk before attacks occur, Falcon Cloud Security also delivers agentless-driven posture management that proactively shrinks the cloud attack surface. Unlike typical solutions, Crowdstrike enriches cloud risk detections with adversary intelligence and graph-based context, enabling security teams to prioritize exploitable exposures and prevent breaches before they happen. Customers using Falcon Cloud Security consistently see measurable results: 89% faster cloud detection and response 100x reduction in false positives by prioritizing exploitable, business-critical risk 83% reduction in cloud security licenses due to elimination of redundant tools

Average Rating: 4.5/5.0

Total Reviews: 243

Who Is the Company Behind CrowdStrike Falcon Cloud Security?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®
  • Ownership: NASDAQ: CRWD

Who Uses This Product?

  • Who Uses This: Analyst
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 52% Large, 31% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their protection in cloud environments.
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their cloud security management significantly.
  • Users value the real-time detection efficiency of CrowdStrike Falcon Cloud Security for enhanced cloud threat management.
  • Users value the real-time vulnerability detection of CrowdStrike Falcon Cloud Security, enhancing proactive risk management and security.
  • Users appreciate the ease of use of CrowdStrike Falcon Cloud Security, making it a top choice for cloud cybersecurity.
Cons
  • Users find CrowdStrike Falcon Cloud Security to be expensive, particularly challenging for small businesses with budget constraints.
  • Users face issues with alert fatigue and response lag, calling for improved prioritization and better support resources.
  • Users experience alert fatigue and desire improved response times and better training resources for CrowdStrike Falcon.
  • Users find the feature complexity of CrowdStrike Falcon Cloud Security can overwhelm new users and necessitate a learning curve.
  • Users report a challenging learning curve with CrowdStrike Falcon, especially for those unfamiliar with similar tools.

What Are Recent G2 Reviews of CrowdStrike Falcon Cloud Security?

Aikido Security

Aikido Security is the developer-first security platform that unifies code, cloud, protection, and attack testing in one suite of best-in-class products. Built by developers for developers, Aikido helps teams of any size ship secure software faster, automate protection, and simulate real-world attacks with AI-driven precision. The platform’s proprietary AI cuts noise by 95%, delivers one-click fixes, and saves developers 10+ hours per week. Aikido Intel proactively uncovers vulnerabilities in open source packages before disclosure, helping secure more than 50,000 organizations worldwide, including Revolut, Niantic, Visma, Montblanc, and GoCardless.

Average Rating: 4.5/5.0

Total Reviews: 272

Who Is the Company Behind Aikido Security?

  • Seller: Aikido Security
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Ghent, Belgium
  • LinkedIn® Page: www.linkedin.com
    320 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Founder, CTO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 78% Small, 15% Medium

What Do G2 Reviewers Say About Aikido Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Aikido Security, thanks to its clear insights and seamless integration.
  • Users appreciate Aikido Security's robust security capabilities, providing a comprehensive and seamless integration in their workflow.
  • Users value the intuitive dashboard of Aikido Security, which simplifies security issue identification and management.
  • Users value the easy integrations of Aikido Security, enhancing workflows with seamless connections to existing GitLab repositories.
  • Users find Aikido's easy setup highly efficient, enabling quick implementation and immediate usability for security assessments.
Cons
  • Users note the lack of advanced features in Aikido Security, such as dark mode and in-depth analysis options.
  • Users find the pricing structure expensive for micro businesses, making upgrades difficult to justify.
  • Users note the limited features of Aikido Security, wishing for more customization and advanced options.
  • Users find the pricing issues challenging, especially for micro businesses, due to the steep upgrade costs.
  • Users feel Aikido Security is lacking features like advanced reporting and deeper compliance analysis compared to competitors.

What Are Recent G2 Reviews of Aikido Security?

OX Security

OX rewires your security program for the Mythos Age: the era where AI writes the code, chains the exploits, and moves faster than human-built defenses can track. OX is an AI Native Application Protection Platform (AINAPP) unifying security from Prompt to Runtime. It moves your control surface upstream to the prompt, preventing and governing risk at the source instead of chasing it downstream in runtime. OX Mind and OX AI Context Lake connect AI-user governance, code security, cloud and runtime enforcement, and agentic pentesting into one system that shares context across the entire Agentic Development Lifecycle (ADLC), replacing fragmented point tools with a single platform. The platform runs on four connected pillars: OX VibeSec: Prevents unsafe AI decisions at the point of creation and governs every AI user in the organization, not just developers using coding assistants. Full visibility into which agents, MCPs, skills, and packages run, with what permissions, against what data. OX Code: Separates exploitable risk from theoretical noise using evidence from your actual deployment, threat model, and threat intelligence. OX Cloud: Prevents misconfigurations and enforces runtime boundaries that code and agents cannot cross, watching what actually runs in production. OX Agentic Pentester: Continuously simulates adversarial agent behavior to prove exploit paths back to their exact source, feeding what it finds back into OX VibeSec to sharpen governance. OX connects to your existing stack and traces every finding back to its origin (the prompt, the AI user, or the endpoint that created it), then fixes issues at the source rather than flagging them after the fact. For new deployments, OX consolidates governance, code security, cloud enforcement, and pentesting into one platform. For existing stacks, OX layers governance on top and makes current tools smarter through continuous learning, so the same issue never gets created twice. Visit https://ox.security for more information.

Average Rating: 4.8/5.0

Total Reviews: 51

Who Is the Company Behind OX Security?

Who Uses This Product?

  • Who Uses This: Security Engineer
  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 63% Medium, 25% Large

What Do G2 Reviewers Say About OX Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the seamless integration and comprehensive features of OX Security, enhancing efficiency and issue management.
  • Users appreciate the ease of use of OX Security, highlighting its user-friendly interface and quick setup.
  • Users commend the great support team from OX Security, enhancing their overall experience and success.
  • Users value the seamless integration with existing tools, enhancing security without disrupting workflows or creating bottlenecks.
  • Users value the comprehensive security capabilities of OX Security, enhancing their organization's security posture effectively.
Cons
  • Users experience integration issues with OX Security, citing incomplete documentation and limited functionality in certain areas.
  • Users note the missing features in OX Security, impacting usability and integration with certain platforms and systems.
  • Users find OX Security's complexity overwhelming, with a steep learning curve and inadequate documentation frustrating the experience.
  • Users find the inadequate reporting in OX Security limits their ability to showcase security progress effectively.
  • Users note the limited cloud integration with tools like Azure DevOps, affecting ease of use and accessibility.

What Are Recent G2 Reviews of OX Security?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Strobes Security

Strobes is an AI-driven exposure management platform designed to help organizations streamline their security operations by unifying various security methodologies, including Attack Surface Management (ASM), Application Security Posture Management (ASPM), Risk-Based Vulnerability Management (RBVM), and Penetration Testing as a Service (PTaaS). This comprehensive solution provides users with a holistic view of their security posture, enabling them to identify, assess, and respond to potential risks and vulnerabilities effectively. Targeted primarily at security teams and IT professionals, Strobes caters to organizations of all sizes that require a robust approach to managing their security exposure. The platform is particularly beneficial for those who need to navigate the complexities of modern security environments, where multiple tools and processes can lead to fragmented insights. By consolidating various security functions into a single workflow, Strobes empowers users to make informed decisions based on a complete understanding of their risk landscape. One of the key features of Strobes is its extensive integration capabilities, boasting over 120 integrations with existing security tools and systems. This allows organizations to pull findings from disparate sources into a single view, enriching data with contextual information that enhances the relevance of insights. The platform's advanced correlation capabilities help identify relationships between different vulnerabilities and risks, enabling security teams to prioritize their remediation efforts effectively. The user-friendly dashboards in Strobes serve as a central hub for monitoring security activities, encompassing everything from asset discovery and vulnerability insights to Service Level Agreement (SLA) tracking and ticketing. This comprehensive visibility supports continuous prioritization and fix validation, allowing teams to address the most critical issues first. By automating triage processes, Strobes ensures that real risks and exposures are highlighted, facilitating a more efficient response to potential threats. Overall, Strobes stands out in the exposure management landscape by providing a cohesive and intelligent approach to security management. Its ability to unify various methodologies, coupled with powerful automation and integration features, positions it as a valuable tool for organizations seeking to enhance their security posture and effectively manage their exposure to risks.

Average Rating: 4.5/5.0

Total Reviews: 44

Who Is the Company Behind Strobes Security?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 42% Medium, 33% Large

What Do G2 Reviewers Say About Strobes Security?

AI-generated summary from verified user reviews

Pros
  • Users value the rapid vulnerability assessments that enhance security fixes significantly, boosting efficiency and prioritization.
  • Users appreciate the rapid vulnerability assessments and prioritized remediation that enhance their security processes significantly.
  • Users value the thorough security measures of Strobes Security, impressed by its attention to detail in vulnerability management.
  • Users value the responsive customer support of Strobes Security, enhancing the experience with timely and effective assistance.
  • Users find Strobes Security exceptionally easy to use, enjoying quick setup and intuitive dashboards for efficient workflows.
Cons
  • Users express dissatisfaction with the inadequate reporting in Strobes Security, citing lack of transparency and customization options.
  • Users find the limited customization options in Strobes Security hinder initial workflow setup and usability improvements.
  • Users find Strobes Security's poor usability challenging initially, with a steep learning curve and complex dashboard navigation.
  • Users find the reporting issues in Strobes Security limit transparency and hinder customization for effective analysis.
  • Users find the user interface complex, making initial customization and workflow setup a challenging experience.

What Are Recent G2 Reviews of Strobes Security?

Carbon Black App Control

With the rise of security threats and malware, organizations need technologies to combat these risks. Unplanned downtime and performance degradation from security breaches impact productivity and reputation. As IT and security shift to the cloud, it's crucial to stay vigilant about security gaps. Many companies still rely on air-gapped servers or outdated operating systems (EOL OS) for critical systems and data storage. Carbon Black App Control offers proactive security for data centers, AWS, Azure, GCP, or hosted private clouds. App Control ensures trusted software runs, monitors file integrity, controls devices, protects memory and registry keys on Windows.

Average Rating: 4.6/5.0

Total Reviews: 44

Who Is the Company Behind Carbon Black App Control?

  • Seller: Broadcom
  • Year Founded: 1991
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    44,602 employees on LinkedIn®
  • Ownership: NASDAQ: CA
  • Phone: +1 800 225-5224

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 64% Large, 33% Medium

What Do G2 Reviewers Say About Carbon Black App Control?

AI-generated summary from verified user reviews

Pros
  • Users praise the awesome customer support of Carbon Black App Control, enhancing security and compliance effortlessly.
  • Users appreciate the ease of use in Carbon Black App Control, enhancing security and confidence in system management.
  • Users appreciate the easy implementation of Carbon Black App Control, enhancing security and compliance effortlessly.
  • Users appreciate the easy integrations of Carbon Black App Control, enhancing security and simplifying implementation.
  • Users value the easy implementation and strong security of Carbon Black App Control, enhancing compliance and trust in critical systems.
Cons
  • Users feel the pricing may be too expensive for smaller organizations despite its excellent security value.
  • Users have experienced false positives, but manual whitelisting helps mitigate this issue effectively.
  • Users experience high CPU usage with Carbon Black App Control, impacting performance and leading to unnecessary alerts.
  • Users often face high memory utilization with Carbon Black, leading to performance concerns and false alerts.
  • Users experience slow performance due to high CPU and memory usage, leading to frustration with the software's responsiveness.

What Are Recent G2 Reviews of Carbon Black App Control?

What Are G2 Users Discussing About Carbon Black App Control?

Jit

Jit is redefining application security by introducing the first Agentic AppSec Platform, seamlessly blending human expertise with AI-driven automation. Designed for modern development teams, Jit empowers organizations to proactively manage security risks across the entire software development lifecycle.​ AI-Powered Agents Jit's AI Agents, such as SERA (Security Evaluation and Remediation Agent) and COTA (Communication, Ops, and Ticketing Agent), collaborate with your teams to automate vulnerability triage, risk assessment, and remediation processes, significantly reducing manual workloads. ​ Comprehensive Security Scanning Achieve full-stack security coverage with integrated scanners for SAST, DAST, SCA, IaC, CSPM, and more. Jit's platform ensures continuous monitoring and immediate feedback on code changes, facilitating rapid identification and resolution of security issues. ​ Developer-Centric Experience With integrations into popular IDEs and CI/CD pipelines, Jit provides developers with contextual security insights directly within their workflows, promoting a shift-left approach without disrupting productivity. ​ Agentic AI for AppSec Teams Risk-Based Prioritization Utilizing the Model Context Protocol (MCP), Jit evaluates vulnerabilities in the context of runtime environments, business impact, and compliance requirements, enabling teams to focus on the most critical risks. ​ Seamless Integrations Jit integrates with a wide array of tools, including GitHub, GitLab, AWS, Azure, GCP, Jira, Slack, and more, ensuring that security processes are embedded within your existing technology stack. ​

Average Rating: 4.5/5.0

Total Reviews: 43

Who Is the Company Behind Jit?

  • Seller: jit
  • Year Founded: 2021
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    161 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Financial Services
  • Company Size: 44% Medium, 42% Small

What Do G2 Reviewers Say About Jit?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the automated and lightweight security controls of Jit, enhancing workflows without adding complexity.
  • Users praise the easy integrations of Jit, which streamline security management within existing development workflows effortlessly.
  • Users value the ease of use of Jit, enjoying seamless integration and simplified management within their workflows.
  • Users value the efficiency of Jit, streamlining workflows and reducing excess with lightweight, automated security controls.
  • Users appreciate the seamless integration support of Jit, enhancing their development workflow without added complexity.
Cons
  • Users face integration issues with Jit, as it lacks comprehensive support for all enterprise environments and tools.
  • Users find the limited features of Jit hinder integrations and onboarding, affecting complex environments and documentation quality.
  • Users experience limited integration capabilities with Jit, particularly for advanced configurations and third-party tools.
  • Users frequently find the documentation lacking, particularly for advanced configurations and integrations with third-party tools.
  • Users find the complexity of Jit overwhelming, particularly with advanced integrations and configuration for beginners.

What Are Recent G2 Reviews of Jit?

ActiveState

ActiveState provides the world's largest library of secure open source: 79 million (Java, Javascript, Python, R, Go, etc.) vetted components across all major language ecosystems, including transitive dependencies and OS-level libraries—built from source to ensure every component is verified, vulnerability-free, and continuously updated. Software teams improve security posture while accelerating development velocity. We deliver five critical outcomes. Counter Supply Chain Risks at Their Source Significantly reduce the possibility of inheriting malicious code from pre-built binaries. Replace risky, unvetted public components with secure, verifiable packages built directly from source. Gain provenance over your artifacts, ensuring bad actors and malware never reach your environment. - Protection from compromised package ecosystems and build systems - Mitigate high-profile malware attacks such as the npm Shai-Hulud attack and other future threats Continuous Remediation for Your Open Source Inventory Shift from reactive patching to proactive immunity. Maintain a hardened security posture with safe-by-default open source and continuous remediation across your inventory. ActiveState artifacts reduce your attack surface and evolve to help close vulnerabilities before they become incidents. - Up to 99% reduction in CVEs compared to community open source artifacts - Achieve up to 90% reduction in MTTR for future vulnerabilities Apply Frictionless Security Policies Embed governance directly into developer workflows without impeding engineering or adding costly CI/CD bloat. ActiveState solutions slot seamlessly into existing tools and AI coding assistants, transforming security policy from a blocker into an enabler that reduces open source approval workflows from weeks and days to just hours and minutes. - Reduce open source approval workflows from weeks and days to hours and minutes Audit Ready Compliance, Always Achieve continuous compliance with instant, granular visibility into components, licenses, and dependencies across your organization. ActiveState delivers comprehensive SBOMs and metadata by default, ensuring you can meet complex standards and minimizing the scramble of audit preparation. - Full visibility into your open source usage, including transitive and OS level dependencies Reclaim Developer Velocity and Focus Minimize high-value engineering hours on dependency conflicts, environment setup, research and remediation. ActiveState components and artifacts are fully managed to ensure they are always up to date and safe to use so your team can focus entirely on shipping revenue-generating features. - Free up 4-8 developer hours per CVE - 68% reduction in scanner noise from false positives

Average Rating: 4.1/5.0

Total Reviews: 32

Who Is the Company Behind ActiveState?

  • Seller: ActiveState
  • Company Website:
  • Year Founded: 1997
  • HQ Location: Vancouver, BC
  • LinkedIn® Page: www.linkedin.com
    70 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Computer & Network Security
  • Company Size: 51% Small, 29% Medium

What Are Recent G2 Reviews of ActiveState?

What Are G2 Users Discussing About ActiveState?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated