Best Extended Detection and Response (XDR) Platforms

How Many Extended Detection and Response (XDR) Platforms Products Does G2 Track?

Total Products under this Category: 113

Category Stats (Nov 2026)

  • Average Rating: 4.55/5 (↑0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Eye Security (+8.95%) - Among all products in this category, Eye Security recorded the largest rating increase compared to last month

Last updated: November 02, 2026

How Does G2 Rank Extended Detection and Response (XDR) Platforms Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,900+ Authentic Reviews
  • 113+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

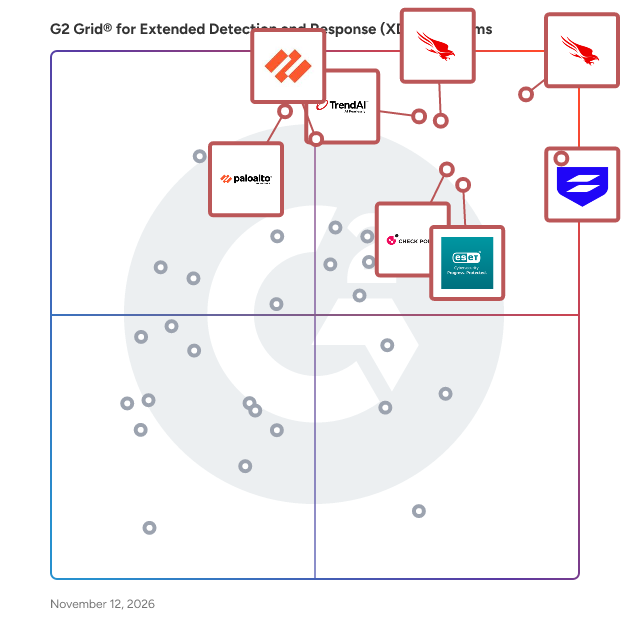
G2 Grid® for Extended Detection and Response (XDR) Platforms

G2 Grid® for Extended Detection and Response (XDR) Platforms plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Sophos Endpoint, CrowdStrike Falcon Cloud Security, TrendAI Vision One, Check Point Endpoint Security, ESET PROTECT, Palo Alto Cortex XSIAM, and Cortex XDR.

Underlying data: [Grid® JSON](https://www.g2.com/categories/extended-detection-and-response-xdr-platforms/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=sophos-endpoint&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=trendai-vision-one&focus%5B%5D=check-point-endpoint-security&focus%5B%5D=eset-protect&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=palo-alto-networks-cortex-xdr)

CrowdStrike Falcon Endpoint Protection Platform

Organizations today face a serious challenge: managing numerous security vendors and tools while confronting an ever-evolving threat landscape. Sophisticated adversaries are becoming smarter, faster, and more evasive, launching complex attacks that can strike in minutes or even seconds. Traditional security approaches struggle to keep pace, leaving businesses vulnerable. The CrowdStrike Falcon Platform addresses this by offering a unified, cloud-native solution. It consolidates previously siloed security solutions and incorporates third-party data into a single platform with one efficient and resource-conscious agent, leveraging advanced AI and real-time threat intelligence. This approach simplifies security operations, speeds analyst decision making, and enhances protection to stop the breach, allowing organizations to reduce risk with less complexity and lower costs. CrowdStrike's Falcon Platform includes: - Endpoint Security: Secure the endpoint, stop the breach - Identify Protection: Identity is the front line, defend it - Next-Gen SIEM: The future of SIEM, today - Data Protection: Real-time data protection from endpoint to cloud - Exposure Management: Understand risk to stop breaches - Charlotte AI: Powering the next evolution of the SOC

Average Rating: 4.7/5.0

Total Reviews: 642

How Do G2 Users Rate CrowdStrike Falcon Endpoint Protection Platform?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.2/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.3/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.5/10 (Category avg: 8.8/10)

Who Is the Company Behind CrowdStrike Falcon Endpoint Protection Platform?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®
  • Ownership: NASDAQ: CRWD

Who Uses This Product?

  • Who Uses This: Security Engineer, Security Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 49% Large, 37% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Endpoint Protection Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the cloud-native architecture and effective features like workflow automation and asset management in CrowdStrike Falcon.
  • Users value the advanced threat detection capabilities of CrowdStrike Falcon, enhancing security and streamlining response efforts.
  • Users value the ease of use of CrowdStrike Falcon, benefiting from its lightweight agent and intuitive interface.
  • Users appreciate the robust security features of CrowdStrike Falcon, enhancing endpoint protection and system performance.
  • Users praise the superior detection capabilities of CrowdStrike Falcon, consistently delivering reliable and swift responses.
Cons
  • Users find that CrowdStrike Falcon's high licensing cost can be burdensome, particularly for smaller teams and organizations.
  • Users express frustration over the complexity of CrowdStrike Falcon's management console and its steep learning curve.
  • Users find the steep learning curve of CrowdStrike Falcon challenging due to its complex management console.
  • Users face limited functionality in adding hash values to CrowdStrike Falcon, which restricts monitoring capabilities.
  • Users express concern over the high pricing of CrowdStrike Falcon, especially for smaller organizations.

What Are Recent G2 Reviews of CrowdStrike Falcon Endpoint Protection Platform?

What Are G2 Users Discussing About CrowdStrike Falcon Endpoint Protection Platform?

Sophos Endpoint

Sophos Endpoint is the world’s most comprehensive endpoint protection solution. Built to stop the widest range of attacks, Sophos Endpoint has been proven to prevent even the most advanced ransomware and malware by leveraging a unique combination of next-generation techniques. This includes the ability to detect never-before-seen malware with deep learning, stop ransomware with Sophos anti-ransomware technology, and deny attacker tools with signatureless exploit prevention. Sophos Endpoint also includes root cause analysis to provide insight into threats, and instant malware removal to ensure no attack remnants remain.

Average Rating: 4.6/5.0

Total Reviews: 807

How Do G2 Users Rate Sophos Endpoint?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.1/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.4/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Sophos Endpoint?

  • Seller: Sophos
  • Company Website:
  • Year Founded: 1985
  • HQ Location: Oxfordshire
  • LinkedIn® Page: www.linkedin.com
    5,550 employees on LinkedIn®
  • Ownership: LSE:SOPH

Who Uses This Product?

  • Who Uses This: IT Manager, IT Director
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 60% Medium, 18% Small

What Do G2 Reviewers Say About Sophos Endpoint?

AI-generated summary from verified user reviews

Pros
  • Users find Sophos Endpoint to be easy to use and maintain, streamlining daily management and integration with existing tools.
  • Users appreciate the effective threat detection and seamless integration of Sophos Endpoint, ensuring robust protection with minimal disruption.
  • Users praise the strong security integration of Sophos Endpoint, providing seamless protection without interrupting daily operations.
  • Users value the real-time threat detection and seamless integration of Sophos Endpoint, enhancing overall security management.
  • Users value the easy management of Sophos Endpoint, appreciating its straightforward setup and automated threat detection.
Cons
  • Users experience slow performance with Sophos Endpoint, particularly on low-performance devices during scans and updates.
  • Users experience high resource usage on older endpoints, leading to performance issues and confusing navigation.
  • Users find the learning curve steep with Sophos Endpoint, especially for beginners and those needing advanced configurations.
  • Users find the difficult configuration of Sophos Endpoint can be overwhelming, impacting their overall experience and efficiency.
  • Users report high CPU usage with Sophos Endpoint, particularly on older devices, affecting overall performance.

What Are Recent G2 Reviews of Sophos Endpoint?

What Are G2 Users Discussing About Sophos Endpoint?

CrowdStrike Falcon Cloud Security

Crowdstrike Falcon Cloud Security is the only CNAPP to stop breaches in the cloud Built for today’s hybrid and multi-cloud environments, Falcon Cloud Security protects the entire cloud attack surface - from code to runtime - by combining continuous agentless visibility with real-time detection and response. At runtime, Falcon Cloud Security delivers best-in-class cloud workload protection and real-time cloud detection and response (CDR) to stop active threats across hybrid environments. Integrated with the CrowdStrike Falcon platform, it correlates signals across endpoint, identity, and cloud to detect sophisticated cross-domain attacks that point solutions miss—enabling teams to respond faster and stop breaches in progress. To reduce risk before attacks occur, Falcon Cloud Security also delivers agentless-driven posture management that proactively shrinks the cloud attack surface. Unlike typical solutions, Crowdstrike enriches cloud risk detections with adversary intelligence and graph-based context, enabling security teams to prioritize exploitable exposures and prevent breaches before they happen. Customers using Falcon Cloud Security consistently see measurable results: 89% faster cloud detection and response 100x reduction in false positives by prioritizing exploitable, business-critical risk 83% reduction in cloud security licenses due to elimination of redundant tools

Average Rating: 4.5/5.0

Total Reviews: 243

How Do G2 Users Rate CrowdStrike Falcon Cloud Security?

  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.2/10)
  • Unified Visibility: 7.5/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.3/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind CrowdStrike Falcon Cloud Security?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®
  • Ownership: NASDAQ: CRWD

Who Uses This Product?

  • Who Uses This: Analyst
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 52% Large, 31% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their protection in cloud environments.
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their cloud security management significantly.
  • Users value the real-time detection efficiency of CrowdStrike Falcon Cloud Security for enhanced cloud threat management.
  • Users value the real-time vulnerability detection of CrowdStrike Falcon Cloud Security, enhancing proactive risk management and security.
  • Users appreciate the ease of use of CrowdStrike Falcon Cloud Security, making it a top choice for cloud cybersecurity.
Cons
  • Users find CrowdStrike Falcon Cloud Security to be expensive, particularly challenging for small businesses with budget constraints.
  • Users face issues with alert fatigue and response lag, calling for improved prioritization and better support resources.
  • Users experience alert fatigue and desire improved response times and better training resources for CrowdStrike Falcon.
  • Users find the feature complexity of CrowdStrike Falcon Cloud Security can overwhelm new users and necessitate a learning curve.
  • Users report a challenging learning curve with CrowdStrike Falcon, especially for those unfamiliar with similar tools.

What Are Recent G2 Reviews of CrowdStrike Falcon Cloud Security?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

TrendAI Vision One

TrendAI Vision One is a cloud-native security operations platform, serving cloud, hybrid, and on-premises environments. It combines ASM and XDR in a single console to effectively manage cyber risk across your organization. The platform provides powerful risk insights, earlier threat detection, and automated risk and threat response options. Utilize the platform’s predictive machine learning and advanced security analytics for a broader perspective and advanced context. TrendAI Vision One integrates with its own expansive protection platform portfolio and industry-leading global threat intelligence, in addition to a broad ecosystem of purpose-built and API-driven third-party integrations.

Average Rating: 4.7/5.0

Total Reviews: 248

How Do G2 Users Rate TrendAI Vision One?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.1/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind TrendAI Vision One?

  • Seller: TrendAI
  • Company Website:
  • Year Founded: 1988
  • HQ Location: Tokyo
  • LinkedIn® Page: www.linkedin.com
    7,996 employees on LinkedIn®
  • Ownership: OTCMKTS:TMICY

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 52% Large, 34% Medium

What Do G2 Reviewers Say About TrendAI Vision One?

AI-generated summary from verified user reviews

Pros
  • Users value the unified visibility of TrendAI Vision One, enhancing security operations and reducing alert fatigue effectively.
  • Users commend the unified visibility of TrendAI Vision One, enhancing security operations through effective threat detection and response.
  • Users appreciate the ease of use of TrendAI Vision One, enjoying its intuitive dashboard and seamless navigation.
  • Users appreciate the unified visibility of TrendAI Vision One, enhancing security operations across multiple platforms seamlessly.
  • Users value the powerful threat detection capabilities of TrendAI Vision One, enhancing security response and visibility.
Cons
  • Users find the complex interface of TrendAI Vision One overwhelming, affecting navigation and usability significantly.
  • Users report integration issues with TrendAI Vision One, leading to complexities with setup and third-party tools.
  • Users report a challenging learning curve with TrendAI Vision One, making onboarding difficult for new teams.
  • Users note the high cost of TrendAI Vision One compared to similar products, impacting overall value perception.
  • Users note the limited features of TrendAI Vision One, especially in reporting and dynamic dashboard capabilities.

What Are Recent G2 Reviews of TrendAI Vision One?

What Are G2 Users Discussing About TrendAI Vision One?

ESET PROTECT

ESET PROTECT is an AI-native cybersecurity platform that combines next-generation prevention, detection, and response capabilities with AI-powered security technologies and 24/7 managed detection and response (MDR) services delivered by ESET security experts. A single, unified management console provides centralized visibility across security operations, helping organizations automate repetitive tasks and enabling security teams to focus on higher-priority activities. With exceptional detection accuracy and fewer false positives, the platform helps reduce alert noise and identify real threats faster. Designed to help organizations stay ahead of known and emerging threats, ESET PROTECT strengthens cyber resilience, improves operational efficiency, and supports compliance initiatives. Why Organizations Choose ESET PROTECT Reduce Security Burden with Expert-Led Protection Fill cybersecurity skill gaps with 24/7 managed detection and response (MDR) backed by ESET experts. Gain faster incident response, actionable threat intelligence, and access to a team of experienced threat hunters. Secure AI Workflows Without Slowing Innovation Adopt AI confidently while protecting your organization from emerging AI-related threats. Secure AI conversations from malicious responses and risky prompts, protect against AI agent attacks, and detect suspicious AI agent behavior. Confidence in Cybersecurity with ESET AI Technologies Benefit from AI-powered technologies built specifically for cybersecurity. ESET helps security teams prevent threats earlier, prioritize and respond faster, improve threat detection, reduce noise, and protect people, devices, data, and businesses across multiple perimeters. Strengthen Compliance Readiness Navigate growing compliance demands with confidence. Our endpoint protection solutions help you assess risk, automate compliance processes, and demonstrate adherence to regulatory, customer, and industry requirements. Support compliance with NIS2, DORA, GDPR, ISO 27001, and more through continuous monitoring, automated evidence collection, and actionable recommendations to strengthen your security and compliance posture.

Average Rating: 4.6/5.0

Total Reviews: 978

How Do G2 Users Rate ESET PROTECT?

  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.7/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.8/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.7/10 (Category avg: 8.8/10)

Who Is the Company Behind ESET PROTECT?

  • Seller: ESET
  • Company Website:
  • Year Founded: 1992
  • HQ Location: Bratislava, Slovak Republic
  • LinkedIn® Page: www.linkedin.com
    2,014 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, Network Administrator
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 48% Medium, 45% Small

What Do G2 Reviewers Say About ESET PROTECT?

AI-generated summary from verified user reviews

Pros
  • Users find ESET PROTECT's intuitive interface makes setup and ongoing management straightforward and efficient.
  • Users value ESET PROTECT for its robust protection against cyber threats, safeguarding sensitive data effectively.
  • Users praise the reliability of ESET PROTECT, valuing its thorough threat detection and ease of management.
  • Users value the robust security features of ESET PROTECT, ensuring comprehensive protection against cyber threats.
  • Users value the centralized management of ESET PROTECT, streamlining policy application across all endpoints effortlessly.
Cons
  • Users find the learning curve steep with ESET PROTECT, citing frustrations with outdated interfaces and difficult configurations.
  • Users find difficult configuration challenges with ESET PROTECT, complicating management and requiring considerable expertise to navigate.
  • Users find ESET PROTECT to have a not user-friendly interface, making navigation and configuration challenging, especially for newcomers.
  • Users find the lack of clarity in ESET PROTECT's interface and settings can be challenging to navigate effectively.
  • Users find difficult navigation in ESET PROTECT's interface, complicating the configuration and usage for first-time users.

What Are Recent G2 Reviews of ESET PROTECT?

What Are G2 Users Discussing About ESET PROTECT?

Check Point Endpoint Security

Harmony Endpoint is a complete endpoint security solution offering a fleet of advanced endpoint threat prevention capabilities so you can safely navigate today’s menacing threat landscape. It provides a comprehensive system to proactively prevent, detect, and remediate evasive malware attacks.

Average Rating: 4.5/5.0

Total Reviews: 254

How Do G2 Users Rate Check Point Endpoint Security?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.2/10)

Who Is the Company Behind Check Point Endpoint Security?

Who Uses This Product?

  • Who Uses This: Network Engineer, Cyber Security Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 54% Medium, 28% Large

What Do G2 Reviewers Say About Check Point Endpoint Security?

AI-generated summary from verified user reviews

Pros
  • Users value the comprehensive, multi-layered protection of Check Point Endpoint Security against various advanced threats.
  • Users value the comprehensive multi-layered protection offered by Check Point Harmony Endpoint, enhancing confidence in security defenses.
  • Users appreciate the real-time threat detection of Check Point Endpoint Security, enhancing confidence in endpoint protection.
  • Users appreciate the comprehensive, multi-layered protection of Check Point Endpoint Security, enhancing confidence in safeguarding endpoints.
  • Users appreciate the intuitive management interface of Check Point Endpoint Security, simplifying threat monitoring and incident response.
Cons
  • Users report slow performance during scans and updates, impacting user experience on lower-spec devices.
  • Users find the high resource usage of Check Point Harmony Endpoint can negatively impact performance on lower-spec devices.
  • Users face difficult configuration challenges with Check Point Endpoint Security, complicating setup and impacting daily operations.
  • Users find Check Point Endpoint Security to be expensive, particularly challenging for small businesses with limited budgets.
  • Users face a steep learning curve with Check Point Endpoint Security, complicating setup and day-to-day operations.

What Are Recent G2 Reviews of Check Point Endpoint Security?

What Are G2 Users Discussing About Check Point Endpoint Security?

Palo Alto Cortex XSIAM

Product Description: Palo Alto Networks' Cortex XSIAM is an AI-driven security operations platform designed to transform traditional Security Operations Centers by integrating and automating key functions such as data centralization, threat detection, and incident response. By leveraging machine learning and automation, it enables organizations to detect and respond to threats more efficiently, reducing manual workloads and improving overall security posture. Key Features and Functionality: - Data Centralization: Aggregates data from various sources into a unified platform, providing comprehensive visibility across the enterprise. - AI-Powered Threat Detection: Utilizes machine learning algorithms to identify anomalies and potential threats in real-time. - Automated Incident Response: Streamlines response processes through automation, enabling rapid mitigation of security incidents. - Integrated SOC Capabilities: Combines functions such as Extended Detection and Response , Security Orchestration, Automation, and Response , Attack Surface Management , and Security Information and Event Management into a cohesive platform, eliminating the need for multiple disparate tools. - Scalability: Designed to handle large volumes of data and adapt to the evolving needs of modern enterprises. Primary Value and Problem Solved: Cortex XSIAM addresses the challenges of disjointed data, weak threat defense, and heavy reliance on manual work in traditional SOCs. By centralizing data and automating security operations, it simplifies processes, enhances threat detection accuracy, and accelerates incident response times. This transformation enables organizations to proactively outpace threats, reduce operational costs, and achieve a more robust security posture.

Average Rating: 4.4/5.0

Total Reviews: 109

How Do G2 Users Rate Palo Alto Cortex XSIAM?

  • Has the product been a good partner in doing business?: 8.5/10 (Category avg: 9.2/10)
  • Unified Visibility: 7.9/10 (Category avg: 9.1/10)
  • Threat Hunting: 8.3/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Palo Alto Cortex XSIAM?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Large, 36% Medium

What Do G2 Reviewers Say About Palo Alto Cortex XSIAM?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Palo Alto Cortex XSIAM, benefiting from its intuitive interface and seamless integration.
  • Users value the advanced threat detection capabilities of Palo Alto Cortex XSIAM, ensuring both known and unknown threats are managed effectively.
  • Users value the seamless integrations of Palo Alto Cortex XSIAM, enhancing overall functionality across various platforms.
  • Users value the unified console of Palo Alto Cortex XSIAM for simplifying security management across endpoints, network, and cloud.
  • Users value the single console integration, highlighting its ease of use and reliability for threat detection.
Cons
  • Users find the Cortex XSIAM to be very expensive compared to other solutions, impacting overall satisfaction.
  • Users find the difficult learning curve of Palo Alto Cortex XSIAM a challenge due to its complexity and setup.
  • Users find the complexity of the console overwhelming, requiring significant time and expertise to navigate effectively.
  • Users report integration issues with Palo Alto Cortex XSIAM, facing challenges with non-native equipment and log maintenance.
  • Users find the UX improvement of Palo Alto Cortex XSIAM lacking in customization and intuitive design for features.

What Are Recent G2 Reviews of Palo Alto Cortex XSIAM?

What Are G2 Users Discussing About Palo Alto Cortex XSIAM?

Cynet

Cynet is the unified, AI-powered cybersecurity platform that delivers robust and comprehensive protection for security teams while maximizing operational efficiency for managed service providers (MSPs). This platform consolidates a wide array of security capabilities into a single, user-friendly interface, ensuring that organizations can effectively safeguard their digital assets without the complexity often associated with multi-solution environments. Cynet’s platform simplifies security management by integrating various functionalities, such as endpoint protection, threat detection, and incident response, into one cohesive system. This integration not only streamlines operations but also allows organizations to allocate their resources more effectively, ultimately enhancing their overall security posture. One of the standout features of Cynet’s platform is its remarkable performance in the MITRE ATT&CK Evaluations. Cynet delivered 100% visibility and 100% analytic coverage without requiring any configuration changes three years in a row. This capability ensures that organizations can monitor their environments comprehensively and respond to threats with precision. The platform’s built-in analytics and reporting tools provide actionable insights, enabling users to make informed decisions about their cybersecurity strategies. Additionally, Cynet offers 24/7 expert support, which is crucial for organizations that may not have in-house cybersecurity expertise. This round-the-clock assistance ensures that users can quickly address any security incidents or concerns, minimizing potential downtime and damage. The combination of advanced technology and dedicated support positions Cynet as a valuable partner for SMEs and service providers looking to enhance their cybersecurity measures. In summary, Cynet’s unified, AI-powered cybersecurity platform stands out in the crowded cybersecurity market by offering a unified solution tailored to the needs of MSPs. Its comprehensive features, exceptional performance in industry evaluations, and continuous expert support make it a compelling choice for organizations seeking to bolster their cybersecurity defenses while maintaining operational efficiency.

Average Rating: 4.7/5.0

Total Reviews: 218

How Do G2 Users Rate Cynet?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.3/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Cynet?

  • Seller: Cynet
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    335 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: SOC Analyst, Technical Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 58% Medium, 30% Small

What Do G2 Reviewers Say About Cynet?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Cynet, enjoying its simple implementation and daily operation.
  • Users appreciate the responsive SOC team and improved dashboard features, enhancing control and reducing notification noise.
  • Users value the effective threat detection of Cynet, appreciating its responsiveness and improved dashboard features.
  • Users commend Cynet's responsive customer support, quickly resolving issues and enhancing the overall experience with the product.
  • Users commend Cynet for its robust security features, seamless implementation, and excellent support, enhancing overall cybersecurity management.
Cons
  • Users find limited customization options in dashboards and integrations, affecting their overall experience with Cynet.
  • Users note feature limitations in customization and integration options, which may hinder user experience and flexibility.
  • Users find a lack of customization in dashboards and features, limiting their ability to tailor the platform effectively.
  • Users experience limited features with Cynet, particularly in reporting options and third-party integrations.
  • Users note that some missing features hinder full integration and customization, impacting overall user experience.

What Are Recent G2 Reviews of Cynet?

What Are G2 Users Discussing About Cynet?

Cortex XDR

Cortex XDR is the industry’s first extended detection and response platform that stops modern attacks by integrating data from any source. With Cortex XDR, you can harness the power of AI, analytics and rich data to detect stealthy threats. Your SOC team can cut through the noise and focus on what matters most with intelligent alert grouping and incident scoring. Cross-data insights accelerate investigations, so you can streamline incident response and recovery. Cortex XDR delivers peace of mind with best-in-class endpoint protection that achieved the highest combined protection and detection scores in the MITRE ATT&CK® round 3 evaluation. The Cortex XDR platform collects and analyzes all data, so you can gain complete visibility and holistic protection to secure what’s next.

Average Rating: 4.5/5.0

Total Reviews: 89

How Do G2 Users Rate Cortex XDR?

  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.5/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.5/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 7.4/10 (Category avg: 8.8/10)

Who Is the Company Behind Cortex XDR?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 40% Medium, 38% Large

What Do G2 Reviewers Say About Cortex XDR?

AI-generated summary from verified user reviews

Pros
  • Users praise the ease of use of Cortex XDR, highlighting its simple interface and excellent manageability.
  • Users value the rapid and accurate threat detection in Cortex XDR, enhancing their security and efficiency.
  • Users value the unified detection and response capability of Cortex XDR for efficient threat investigation.
  • Users value the intelligent alert system of Cortex XDR, which minimizes unnecessary notifications and enhances focus.
  • Users value the advanced AI technology in Cortex XDR, which delivers relevant alerts without overwhelming notifications.
Cons
  • Users experience a performance impact on lower-end systems with the Cortex XDR agent installed, complicating usability.
  • Users face compatibility issues with Cortex XDR, as it restricts core functionalities of the operating system.
  • Users find the complexity of Cortex XDR challenging due to its steep learning curve and management demands.
  • Users find the complex management of Cortex XDR challenging, especially when customizing detections and tuning policies.
  • Users find the difficult learning curve of Cortex XDR challenging, especially when tuning policies and customizing detections.

What Are Recent G2 Reviews of Cortex XDR?

What Are G2 Users Discussing About Cortex XDR?

Sophos Fusion

Sophos Fusion is a comprehensive, cloud-based cybersecurity management platform that unifies all Sophos next-generation security solutions into a single, intuitive interface. Designed to simplify and enhance cybersecurity management, it enables organizations to efficiently oversee and secure their IT infrastructure with advanced AI-driven protection and real-time data insights. Key Features and Functionality: - Unified Management Console: Provides centralized control over all Sophos security products, including endpoint, server, mobile, public cloud, firewall, email, wireless, and Zero Trust Network Access (ZTNA). - AI-Powered Cyber Defenses: Utilizes advanced artificial intelligence to deliver proactive threat detection and automated incident response, ensuring robust protection against evolving cyber threats. - Deep Data Analytics: Offers synchronized cross-product telemetry and access to SophosLabs Intelix threat intelligence, facilitating comprehensive cross-product investigations and informed decision-making. - High Availability and Scalability: Built on a cloud-native architecture hosted on public cloud platforms like AWS and Azure, ensuring high availability, seamless failover, and the ability to scale security measures as organizational needs grow. - Secure Architecture: Features a secure design with global services for identity and session management, scalable regional API and product services, and strict access controls to maintain data integrity and confidentiality. Primary Value and Solutions Provided: Sophos Fusion addresses the challenges IT administrators face in managing multiple security tools, responding to complex threats, and ensuring consistent protection across networks. By consolidating security management into a single platform, it reduces administrative burden, automates threat responses, and provides real-time insights, leading to: - Time and Effort Savings: Customers report a 50% reduction in time and effort spent managing IT security. - Enhanced Security Posture: Achieves an 85% reduction in security incidents through integrated and automated defenses. - Faster Issue Identification: Realizes a 90% reduction in time to identify issues, enabling swift remediation and minimizing potential damage. By integrating all security solutions into a cohesive system, Sophos Fusion empowers organizations to proactively defend against cyber threats, streamline security operations, and adapt to the dynamic cybersecurity landscape effectively.

Average Rating: 4.4/5.0

Total Reviews: 62

How Do G2 Users Rate Sophos Fusion?

  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.2/10)
  • Unified Visibility: 8.9/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.4/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Sophos Fusion?

  • Seller: Sophos
  • Year Founded: 1985
  • HQ Location: Oxfordshire
  • LinkedIn® Page: www.linkedin.com
    5,550 employees on LinkedIn®
  • Ownership: LSE:SOPH

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 55% Medium, 29% Small

What Do G2 Reviewers Say About Sophos Fusion?

AI-generated summary from verified user reviews

Pros
  • Users praise the ease of use of Sophos Fusion, benefiting from centralized management and intuitive interface.
  • Users commend the robust security features of Sophos Fusion that ensure comprehensive endpoint protection and risk management.
  • Users appreciate the all-in-one solution of Sophos Fusion, enabling easy management of multiple cybersecurity tools from one dashboard.
  • Users enjoy the easy integration of Sophos Fusion, streamlining security management on a single, intuitive platform.
  • Users value the effective management capabilities of Sophos Fusion, enhancing security visibility and operational efficiency.
Cons
  • Users experience slow performance with Sophos Fusion, particularly on lower-end devices, affecting task execution and responsiveness.
  • Users experience update issues that require reinstallation, leading to lost codes and frustrating support interactions.
  • Users face device limitations with Sophos Fusion, including high memory usage and lack of on-premises support.
  • Users face access issues with Sophos Fusion, complicating management for multiple clients and limiting usability.
  • Users experience alert issues with Sophos Fusion, as it sometimes fails to remember authorized senders and produces false positives.

What Are Recent G2 Reviews of Sophos Fusion?

What Are G2 Users Discussing About Sophos Fusion?

SentinelOne Singularity Endpoint

SentinelOne® Singularity™ Endpoint is an autonomous endpoint security platform that stops threats in real-time. It unifies endpoint protection (EPP), endpoint detection and response (EDR), and autonomous remediation to stop ransomware, zero-day exploits, supply chain attacks, and fileless malware. Singularity Endpoint protects workstations, mobile devices, servers, and cloud workloads across SaaS, on-premises, hybrid, and air-gapped environments. Behavioral and static AI detection models stop known and unknown threats by identifying how threats behave, not just what they look like. SentinelOne catches what signatures miss, without waiting on updates. Storyline® automatically correlates telemetry into one visual attack story, and patented one-click rollback restores systems to a trusted state in seconds. The result is stronger protection with fewer incidents and less operational overhead: lower dwell time, fewer false positives, and faster response. With Purple AI™, teams accelerate triage, threat hunting, and investigation. From alert to verdict without manual investigation. Purple AI's Agentic Investigation runs the analysis, surfaces the evidence, and tells your team exactly what to do next. The same SentinelOne agent that protects endpoints also defends every identity behind them. Detect credential abuse, shrink your attack surface, and contain identity threats from one console. Seamless integration of endpoint, identity, cloud, and third-party telemetry eliminates blind spots. Built AI-native from day one, Singularity Endpoint delivers best-in-industry coverage across Windows, macOS, Linux, and mobile operating systems, including legacy OSes. Trusted by more than 11,500 customers, SentinelOne is a six-time Gartner® Magic Quadrant™ Leader for Endpoint Protection.

Average Rating: 4.7/5.0

Total Reviews: 235

How Do G2 Users Rate SentinelOne Singularity Endpoint?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.3/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.4/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.1/10 (Category avg: 8.8/10)

Who Is the Company Behind SentinelOne Singularity Endpoint?

  • Seller: SentinelOne
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • LinkedIn® Page: www.linkedin.com
    3,529 employees on LinkedIn®
  • Ownership: NASDAQ: S

Who Uses This Product?

  • Who Uses This: Technical Support Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 43% Medium, 35% Large

What Do G2 Reviewers Say About SentinelOne Singularity Endpoint?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the tool efficiency of SentinelOne Singularity, noting its prompt malware detection and reliability.
  • Users praise the easy deployment and effective threat detection of SentinelOne Singularity Endpoint, enhancing overall experience.
  • Users commend the effective malware protection of SentinelOne Singularity, promptly detecting and blocking infection attempts.
  • Users appreciate the easy incident notification system of SentinelOne, which simplifies investigation and enhances reliability.
  • Users value the robust analytics and endpoint management features of SentinelOne Singularity, enhancing security and operational efficiency.
Cons
  • Users face challenges with update issues, including manual restarts and difficulties removing the software when necessary.
  • Users find the difficult learning curve of SentinelOne challenging, especially for beginners trying to understand its functionality.
  • Users find the frequent updates of SentinelOne Singularity Endpoint cumbersome, requiring manual restarts to keep software current.
  • Users face challenges with agent removal issues, particularly when the software goes offline or occupies excessive space.
  • Users experience ineffective alerts that complicate troubleshooting and require significant fine-tuning for optimal performance.

What Are Recent G2 Reviews of SentinelOne Singularity Endpoint?

What Are G2 Users Discussing About SentinelOne Singularity Endpoint?

Wiz

Wiz transforms cloud security for customers – including more than 50% of the Fortune 100 – by enabling a new operating model. With Wiz, organizations can democratize security across the development lifecycle, empowering them to build fast and securely. Its Cloud Native Application Protection Platform (CNAPP) consolidates CSPM, KSPM, CWPP, Vulnerability management, IaC scanning, CIEM, DSPM into a single platform. Wiz drives visibility, risk prioritization, and business agility. Protecting Your Cloud Environments Requires a Unified, Cloud Native Platform. Wiz connects to every cloud environment, scans every layer, and covers every aspect of your cloud security - including elements that normally require installing agents. Its comprehensive approach has all of these cloud security solutions built in. Hundreds of organizations worldwide, including 50 percent of the Fortune 100, to rapidly identify and remove critical risks in cloud environments. Its customers include Salesforce, Slack, Mars, BMW, Avery Dennison, Priceline, Cushman & Wakefield, DocuSign, Plaid, and Agoda, among others. Wiz is backed by Sequoia, Index Ventures, Insight Partners, Salesforce, Blackstone, Advent, Greenoaks, Lightspeed and Aglaé. Visit https://www.wiz.io for more information.

Average Rating: 4.7/5.0

Total Reviews: 928

How Do G2 Users Rate Wiz?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.2/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.2/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Wiz?

  • Seller: Google
  • Company Website:
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG

Who Uses This Product?

  • Who Uses This: Security Engineer, CISO
  • Top Industries: Financial Services, Computer Software
  • Company Size: 54% Large, 37% Medium

What Do G2 Reviewers Say About Wiz?

AI-generated summary from verified user reviews

Pros
  • Users praise the user-friendly capabilities of Wiz, highlighting excellent service and reporting improvements.
  • Users value the enhanced security features of Wiz, benefiting from improved visibility and innovation in cloud security.
  • Users find Wiz to be incredibly easy to use, with a friendly interface and great support enhancing the experience.
  • Users value the enhanced visibility from Wiz, enabling efficient data security management and quick access to essential resources.
  • Users find the setup of Wiz to be easy and fast, enhancing their overall experience with its intuitive interface.
Cons
  • Users indicate that improvement is needed in reporting, alert tuning, and AI-related features for Wiz.
  • Users desire more features and consistency in Wiz to improve experience and enhance AI-related security capabilities.
  • Users find the learning curve steep, struggling with navigation and overwhelming popups in Wiz's interface.
  • Users highlight the need for improvements in reporting and additional capabilities in AI security and alert tuning.
  • Users find the complexity of the platform can be overwhelming, requiring significant effort to navigate and manage effectively.

What Are Recent G2 Reviews of Wiz?

Barracuda Managed XDR

Barracuda Managed XDR is the comprehensive next-generation cybersecurity solution that protects organizations of all sizes against today’s ever-evolving threat landscape. Barracuda Managed XDR is a fully managed service instantly augmenting an organization’s IT staff, identifying signals amidst noise, and reducing TTR from days to seconds. The solution features advanced AI-driven threat protection, SIEM, SOAR, and enterprise-grade threat intelligence from 11+ billion IOCs and hundreds of ML-enriched detection rules aligned to the MITRE ATT&CK framework. Ingesting trillions of events across endpoints, servers, identity, cloud, email, and firewalls, the cloud-native solution detects, responds to, and eliminates cyberthreats in real time across the attack lifecycle. An ‘open’ XDR solution, Barracuda Managed XDR integrates with an organization’s existing technology, ensuring a smooth deployment while enhancing security resilience and operational efficiency. Barracuda Managed XDR is powered by Barracuda’s 24/7/365 global SOC, featuring five specialized expert-level teams delivering best-in-class SLAs and proactive real-time threat detection and response.

Average Rating: 4.5/5.0

Total Reviews: 54

How Do G2 Users Rate Barracuda Managed XDR?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.2/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 6.7/10 (Category avg: 8.8/10)

Who Is the Company Behind Barracuda Managed XDR?

  • Seller: Barracuda
  • Company Website:
  • Year Founded: 2002
  • HQ Location: Campbell, CA
  • LinkedIn® Page: www.linkedin.com
    2,327 employees on LinkedIn®
  • Ownership: Private

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Medium, 34% Small

What Do G2 Reviewers Say About Barracuda Managed XDR?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use and straightforward setup of Barracuda Managed XDR, enhancing overall security management.
  • Users appreciate the 24/7 proactive monitoring of Barracuda Managed XDR, enhancing security without overburdening tech teams.
  • Users value the 24/7 security and straightforward setup of Barracuda Managed XDR, enhancing protection effortlessly.
  • Users value the 24/7 security of Barracuda Managed XDR, ensuring proactive protection against cyber threats with minimal effort.
  • Users value the timely alerts from Barracuda Managed XDR, enhancing threat navigation and response efficiency.
Cons
  • Users find the lack of customization in Barracuda Managed XDR limits their ability to tailor reporting and management.
  • Users note a challenging learning curve with Barracuda Managed XDR, particularly during initial setup and feature navigation.
  • Users feel the interface is not user-friendly and desire more customization options, particularly for reporting and management.
  • Users find the portal issues cumbersome, requiring logins for endpoint management and complicating overall product handling.
  • Users find the agent on the endpoint device limited, requiring logins to the portal for program management.

What Are Recent G2 Reviews of Barracuda Managed XDR?

Rapid7 Next-Gen SIEM

Rapid7 InsightIDR is a SaaS SIEM for modern threat detection and response. InsightIDR enables security analysts to work more efficiently and effectively, by unifying diverse data sources, providing early and reliable out of the box detections, and delivering rich visual investigations and automation to expedite response. With a lightweight cloud deployment and intuitive UI and onboarding experience, InsightIDR customers recognize an accelerated return on their investment and start seeing valuable insights from Day 1. With InsightIDR, teams can advance their threat detection and response program without adding headcount.

Average Rating: 4.4/5.0

Total Reviews: 69

How Do G2 Users Rate Rapid7 Next-Gen SIEM?

  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.2/10)
  • Unified Visibility: 8.6/10 (Category avg: 9.1/10)
  • Threat Hunting: 8.5/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Rapid7 Next-Gen SIEM?

  • Seller: Rapid7
  • Year Founded: 2000
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    8,746 employees on LinkedIn®
  • Ownership: NASDAQ:RPD
  • Total Revenue (USD mm): $411

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 67% Medium, 30% Large

What Do G2 Reviewers Say About Rapid7 Next-Gen SIEM?

AI-generated summary from verified user reviews

Pros
  • Users commend the ease of use of Rapid7 Next-Gen SIEM for its intuitive implementation and clear alerts.
  • Users appreciate the easy integrations with third-party tools, enhancing the overall usability of Rapid7 Next-Gen SIEM.
  • Users appreciate the pre-built integrations of Rapid7 Next-Gen SIEM, facilitating easy connections with various third-party tools.
  • Users value the seamless integration of UEBA and deception tools, enhancing threat detection and speeding up investigations.
  • Users appreciate the visibility provided by Rapid7 Next-Gen SIEM, enabling easy log searching and clear alerting.
Cons
  • Users find the limited features of Rapid7 Next-Gen SIEM restrictive, hindering efficient alert creation and setup.
  • Users face challenges with limited alerting capabilities, making it hard to create effective and timely alerts.
  • Users find the limited alert management functionality challenging, particularly in creating and setting up pattern-based alerts.
  • Users find the difficult customization of Rapid7 Next-Gen SIEM hinders their ability to set effective alerts.
  • Users find the difficult setup of Rapid7 Next-Gen SIEM frustrating, especially with creating alerts effectively.

What Are Recent G2 Reviews of Rapid7 Next-Gen SIEM?

What Are G2 Users Discussing About Rapid7 Next-Gen SIEM?

Microsoft Defender XDR

Microsoft Defender XDR is a unified pre- and post-breach enterprise defense suite that natively coordinates detection, prevention, investigation, and response across endpoints, identities, email, and applications to provide integrated protection against sophisticated attacks.

Average Rating: 4.5/5.0

Total Reviews: 271

How Do G2 Users Rate Microsoft Defender XDR?

  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.2/10)
  • Unified Visibility: 8.7/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 8.8/10 (Category avg: 8.8/10)

Who Is the Company Behind Microsoft Defender XDR?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT
  • Phone: +1 (877) 276-2464

Who Uses This Product?

  • Who Uses This: Software Engineer, Security Consultant
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 40% Large, 38% Medium

What Do G2 Reviewers Say About Microsoft Defender XDR?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the automated response and remediation features of Microsoft Defender XDR, enhancing overall security efficiency.
  • Users value the quick and responsive customer support of Microsoft Defender XDR, enhancing their experience greatly.
  • Users appreciate the seamless integration of Microsoft Defender XDR, enhancing their defense against various cyber threats.
  • Users value the easy deployment of Microsoft Defender XDR, enhancing usability and efficiency in security management.
  • Users value the high detection efficiency of Microsoft Defender XDR when properly configured, enhancing security and usability.
Cons
  • Users note the high licensing costs and complexities involved in the setup and management of Microsoft Defender XDR.
  • Users find the steep learning curve of Microsoft Defender XDR challenging, making initial setup and management time-consuming.
  • Users find the steep learning curve challenging, making initial setup and effective use time-consuming for new users.
  • Users struggle with the high licensing costs and find the setup and management of Microsoft Defender XDR complex.
  • Users find the slow performance of Microsoft Defender XDR frustrating, impacting their overall experience and efficiency.

What Are Recent G2 Reviews of Microsoft Defender XDR?

What Are G2 Users Discussing About Microsoft Defender XDR?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024