Top Free Application Security Posture Management (ASPM) Software

How Many Application Security Posture Management (ASPM) Software Products Does G2 Track?

Total Products under this Category: 49

Category Stats (Oct 2026)

  • Average Rating: 4.55/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: APPCHECK (+0.11%) - Among all products in this category, APPCHECK recorded the largest rating increase compared to last month

Last updated: October 07, 2026

How Does G2 Rank Application Security Posture Management (ASPM) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,200+ Authentic Reviews
  • 49+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

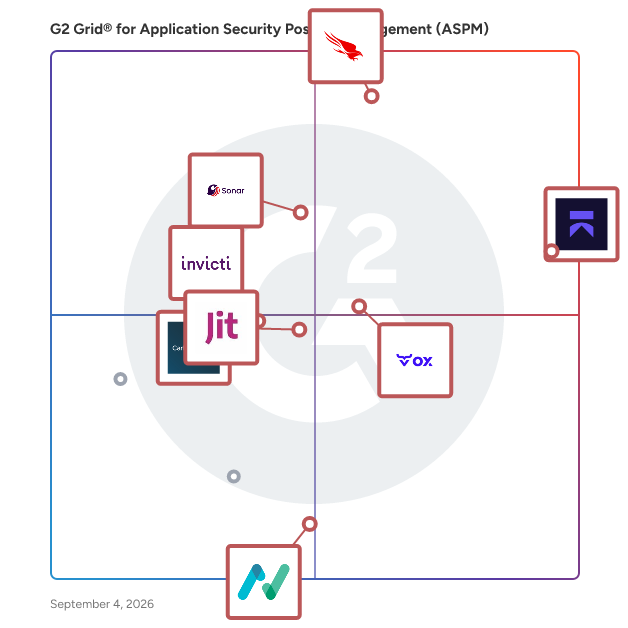
G2 Grid® for Application Security Posture Management (ASPM) Software

G2 Grid® for Application Security Posture Management (ASPM) Software plotting products by satisfaction and market presence

Highlighted products: Aikido Security, CrowdStrike Falcon Cloud Security, SonarQube, OX Security, Jit, Carbon Black App Control, Invicti, and APPCHECK.

Underlying data: [Grid® JSON](https://www.g2.com/categories/application-security-posture-management-aspm/grids.json?focus%5B%5D=aikido-security&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=sonarqube&focus%5B%5D=ox-security&focus%5B%5D=jit&focus%5B%5D=carbon-black-app-control&focus%5B%5D=invicti&focus%5B%5D=appcheck)

Aikido Security

Aikido Security is the developer-first security platform that unifies code, cloud, protection, and attack testing in one suite of best-in-class products. Built by developers for developers, Aikido helps teams of any size ship secure software faster, automate protection, and simulate real-world attacks with AI-driven precision. The platform’s proprietary AI cuts noise by 95%, delivers one-click fixes, and saves developers 10+ hours per week. Aikido Intel proactively uncovers vulnerabilities in open source packages before disclosure, helping secure more than 50,000 organizations worldwide, including Revolut, Niantic, Visma, Montblanc, and GoCardless.

Average Rating: 4.6/5.0

Total Reviews: 266

Who Is the Company Behind Aikido Security?

  • Seller: Aikido Security
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Ghent, Belgium
  • Twitter: @AikidoSecurity
    11,770 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    320 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Founder, CTO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 78% Small, 15% Medium

What Do G2 Reviewers Say About Aikido Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Aikido Security, thanks to its clear insights and seamless integration.
  • Users appreciate Aikido Security's robust security capabilities, providing a comprehensive and seamless integration in their workflow.
  • Users value the intuitive dashboard of Aikido Security, which simplifies security issue identification and management.
  • Users value the easy integrations of Aikido Security, enhancing workflows with seamless connections to existing GitLab repositories.
  • Users find Aikido's easy setup highly efficient, enabling quick implementation and immediate usability for security assessments.
Cons
  • Users note the lack of advanced features in Aikido Security, such as dark mode and in-depth analysis options.
  • Users find the pricing structure expensive for micro businesses, making upgrades difficult to justify.
  • Users note the limited features of Aikido Security, wishing for more customization and advanced options.
  • Users find the pricing issues challenging, especially for micro businesses, due to the steep upgrade costs.
  • Users feel Aikido Security is lacking features like advanced reporting and deeper compliance analysis compared to competitors.

What Are Recent G2 Reviews of Aikido Security?

SonarQube

Sonar, the industry standard for code verification and automated code review, helps reduce outages, improve security, and lower risks associated with AI and agentic coding. As an independent verification platform, Sonar enables organizations to securely develop at the speed of AI. Sonar is the foundation for high-performance software engineering, analyzing over 750 billion lines of code daily to ensure applications are secure, reliable, and maintainable. Rooted in the open source community, Sonar is trusted by 7M+ developers globally, including teams at ServiceNow, Booking.com, Deutsche Bank, AstraZeneca, and Ford Motor Company.

Average Rating: 4.4/5.0

Total Reviews: 153

Who Is the Company Behind SonarQube?

  • Seller: SonarSource Sàrl
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Geneva, Switzerland
  • Twitter: @SonarSource
    10,913 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,041 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: DevOps Engineer, Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 41% Large, 41% Medium

What Do G2 Reviewers Say About SonarQube?

AI-generated summary from verified user reviews

Pros
  • Users value SonarQube for its ability to quickly flag code quality and security issues, ensuring a reliable codebase.
  • Users value the flexible issue filtering and prioritization features of SonarQube, enhancing team productivity and focus.
  • Users appreciate how SonarQube quickly flags code quality and security issues, ensuring a clean and reliable codebase.
  • Users appreciate the ease of use of SonarQube, finding integration and actionable feedback simple and effective.
  • Users appreciate the easy integrations with CI/CD tools, enhancing their workflow and improving code quality effectively.
Cons
  • Users face software bugs that lead to false positives, complicating the experience and requiring significant knowledge to manage.
  • Users find the complex configuration of SonarQube challenging, especially for beginners needing extensive knowledge.
  • Users encounter false positives that complicate usage, despite helpful tools for review and customization of analysis.
  • Users find SonarQube's complexity in configuration and excessive warnings can make it cumbersome to use.
  • Users find the complex setup of SonarQube time-consuming, requiring significant effort to configure and tune effectively.

What Are Recent G2 Reviews of SonarQube?

What Are G2 Users Discussing About SonarQube?

OX Security

OX rewires your security program for the Mythos Age: the era where AI writes the code, chains the exploits, and moves faster than human-built defenses can track. OX is an AI Native Application Protection Platform (AINAPP) unifying security from Prompt to Runtime. It moves your control surface upstream to the prompt, preventing and governing risk at the source instead of chasing it downstream in runtime. OX Mind and OX AI Context Lake connect AI-user governance, code security, cloud and runtime enforcement, and agentic pentesting into one system that shares context across the entire Agentic Development Lifecycle (ADLC), replacing fragmented point tools with a single platform. The platform runs on four connected pillars: OX VibeSec: Prevents unsafe AI decisions at the point of creation and governs every AI user in the organization, not just developers using coding assistants. Full visibility into which agents, MCPs, skills, and packages run, with what permissions, against what data. OX Code: Separates exploitable risk from theoretical noise using evidence from your actual deployment, threat model, and threat intelligence. OX Cloud: Prevents misconfigurations and enforces runtime boundaries that code and agents cannot cross, watching what actually runs in production. OX Agentic Pentester: Continuously simulates adversarial agent behavior to prove exploit paths back to their exact source, feeding what it finds back into OX VibeSec to sharpen governance. OX connects to your existing stack and traces every finding back to its origin (the prompt, the AI user, or the endpoint that created it), then fixes issues at the source rather than flagging them after the fact. For new deployments, OX consolidates governance, code security, cloud enforcement, and pentesting into one platform. For existing stacks, OX layers governance on top and makes current tools smarter through continuous learning, so the same issue never gets created twice. Visit https://ox.security for more information.

Average Rating: 4.8/5.0

Total Reviews: 51

Who Is the Company Behind OX Security?

Who Uses This Product?

  • Who Uses This: Security Engineer
  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 63% Medium, 25% Large

What Do G2 Reviewers Say About OX Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the intuitive dashboard of OX Security, enhancing issue management and streamlining security processes effectively.
  • Users find OX Security highly user-friendly, benefiting from an intuitive dashboard and responsive support for seamless operations.
  • Users value the responsive and professional customer support of OX Security, enhancing their overall experience and efficiency.
  • Users value the seamless integration support from OX Security, enhancing their workflow with fast and user-friendly solutions.
  • Users appreciate the comprehensive security capabilities of OX Security, ensuring a streamlined and effective security management experience.
Cons
  • Users report integration issues with OX Security's limited documentation and insufficient support for various tools.
  • Users note some missing features in OX Security, which can affect its overall usability and integration capabilities.
  • Users find the complexity of OX Security daunting, with inadequate documentation and a steep learning curve for new users.
  • Users find OX Security's inadequate reporting limits their ability to effectively showcase security progress to management.
  • Users find the limited cloud integration with certain tools frustrating, impacting overall connectivity and functionality.

What Are Recent G2 Reviews of OX Security?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

APPCHECK

AppCheck is a Dynamic Application Security Testing (DAST) and network vulnerability testing solution, developed and supported by experienced penetration testers. We approach security testing as a hacker would, leveraging multiple proprietary crawling engines to analyse target behaviour across both modern and traditional technologies, including Single Page Applications (SPAs), APIs, and complex authentication flows such as SSO, 2FA, and TOTP. Organisations can conduct unlimited security assessments across Web Applications, SPAs, APIs, cloud services, networks, across internal or external assets. Supporting production and UAT testing, AppCheck also helps organisations ‘shift left’ by integrating with CI/CD pipelines and build servers, including ADO, GitHub, Jenkins, TeamCity, CircleCI, TravisCI, Bamboo, and GitLab CI/CD. Allowing automated security testing throughout development, identifying risks as soon as changes are introduced. AppCheck are proud to be part of the CVE Numbering Authority (CNA), contributing to global security research

Average Rating: 4.7/5.0

Total Reviews: 68

Who Is the Company Behind APPCHECK?

  • Seller: APPCHECK
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Leeds, GB
  • Twitter: @AppcheckNG
    649 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    104 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 49% Medium, 31% Small

What Do G2 Reviewers Say About APPCHECK?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of AppCheck, making complex processes straightforward and efficient.
  • Users commend AppCheck for its exceptional vulnerability detection, providing thorough coverage and easy integration into workflows.
  • Users value the excellent pricing and functionality of AppCheck, praising its usability and proactive support from the team.
  • Users commend AppCheck for its efficiency in pentesting, notably for thorough vulnerability coverage and seamless integration.
  • Users love the scanning efficiency of AppCheck, finding it reliable and easy to integrate within development workflows.
Cons
  • Users suggest that UX improvements in scoring, customization, and integrations could enhance the AppCheck experience.
  • Users find the API issues frustrating, as endpoint changes require a service request and delays functionality.
  • Users find difficult customization in AppCheck's reporting features, needing more flexibility for contextual adjustments.
  • Users experience a notable difficult learning curve with Appcheck, which may hinder initial ease of use.
  • Users find the false positives in scan results problematic, necessitating manual validation and complicating the reporting process.

What Are Recent G2 Reviews of APPCHECK?

DefectDojo

DefectDojo unifies and automates vulnerability management, enabling security teams to focus on strategic, data-driven analysis. We help teams reduce time spent on manual tracking and consolidate vulnerabilities from existing tools for seamless vulnerability management.

Average Rating: 4.6/5.0

Total Reviews: 11

Who Is the Company Behind DefectDojo?

  • Seller: DefectDojo
  • Year Founded: 2017
  • HQ Location: Austin, US
  • Twitter: @defectdojo
    699 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    27 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 64% Medium, 36% Small

What Are Recent G2 Reviews of DefectDojo?

What Are G2 Users Discussing About DefectDojo?

Edgescan

What Is Edgescan? Edgescan is a cybersecurity company that helps organizations proactively identify, validate, and prioritize vulnerabilities across their applications, API’s and digital landscape. The company specializes in continuous vulnerability assessment, automated penetration testing, Attack Surface Management and Penetration Testing as a Service (PTaaS). Edgescan also delivers Autonomous Penetration Testing via "Edgescan Atomic". Atomic is an AI powered autonomous penetration testing capability available exclusively to Edgescan customers. Each Atomic Attack Credit provides an autonomous penetration test, allowing organizations to perform an additional autonomous penetration test when required Atomic complements PTaaS by providing another way to assess security as environments evolve. (Supercharge your security with AI) Edgescan combines advanced automation with certified security experts, including professionals holding credentials such as CREST and OSCP, to deliver highly accurate and actionable security testing. This hybrid approach allows organizations to move beyond traditional point-in-time penetration tests and operate a continuous proactive cybersecurity program. The Edgescan platform is designed primarily for web application and API security, enabling organizations to continuously assess their attack surface and identify vulnerabilities throughout the development lifecycle but also delivers “full stack” coverage to detect host layer CVE’s. With a client retention rate of over 90%, Edgescan has built long-term partnerships by delivering measurable improvements in security efficiency, risk visibility, and vulnerability management. Key Features and Capabilities of Edgescan Automated Penetration Testing Edgescan uses intelligent automation to continuously assess applications, APIs, hosts, and cloud environments for vulnerabilities. This enables frequent, scalable security testing across modern and distributed architectures. Human‑Validated Testing Findings are reviewed and manually validated by certified security experts to eliminate false positives and provide deeper insight into real‑world exploitability. Each result is accurate, contextual, and actionable. Penetration Testing as a Service (PTaaS) Edgescan’s PTaaS model extends beyond automated testing by allowing expert testers to focus on vulnerabilities that require human analysis, including: • Business logic flaws • Authentication and authorization weaknesses • Context-dependent exposures • Complex attack chains and privilege escalation paths Cyber Analytics and AI‑Assisted Validation AI-driven analysis enhances detection, verifies exploitability, and increases accuracy. This reduces noise and gives security teams a clearer picture of genuine threats. Integrated Threat Intelligence Edgescan correlates vulnerabilities with real-world threat intelligence, including known exploits and ransomware activity to help organizations prioritize the most dangerous exposures first. Risk‑Based Prioritization Findings are prioritized based on exploitability, severity, threat context, and business impact, ensuring teams focus on the issues that matter most. Primary Value: What Edgescan Solves for Clients Edgescan enables organizations to shift from reactive vulnerability management to a continuous, proactive security model. Traditional scanners and periodic penetration tests frequently produce large volumes of unvalidated findings. This creates noise and forces security teams to spend hours determining which issues are real and critical. Edgescan solves this by combining: Automation for continuous testing Human expertise for validation and complex analysis Cyber analytics and AI for accuracy and prioritization Key Benefits Significant efficiency gains: reducing thousands of hours spent on manual validation. Higher accuracy, thanks to expert‑validated findings and reduced false positives. Clear prioritization, using threat intelligence and ransomware insights to highlight the highest‑risk exposures. Continuous security improvement, enabling rapid detection, faster remediation, and scalable vulnerability management. By unifying automation, human expertise, AI, and threat intelligence, Edgescan empowers organizations to maintain a continuous cybersecurity program that strengthens overall security posture while dramatically reducing operational burden.

Average Rating: 4.6/5.0

Total Reviews: 58

Who Is the Company Behind Edgescan?

  • Seller: Edgescan
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Dublin, Dublin
  • Twitter: @edgescan
    2,256 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    88 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 38% Large, 28% Medium

What Do G2 Reviewers Say About Edgescan?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Edgescan, highlighting its intuitive interface and straightforward navigation.
  • Users value the automated vulnerability detection features of Edgescan for efficient risk assessment and remediation support.
  • Users value the excellent customer support from Edgescan, noting their responsiveness and proactivity in addressing queries.
  • Users value the detailed vulnerability identification from Edgescan, enabling effective risk management and threat mitigation strategies.
  • Users value Edgescan for its intuitive interface and comprehensive functionality that streamlines security assessments and support.
Cons
  • Users find the complex UI of Edgescan challenging, often requiring guidance to navigate key functions effectively.
  • Users find limited customization options frustrating, particularly with filtering systems and administrative functionalities.
  • Users find the poor interface design of Edgescan challenging, causing navigation and task completion difficulties.
  • Users experience slow performance with Edgescan as manual reviews lead to longer scan completion times.
  • Users find the user interface challenging and unintuitive, leading to difficulties in navigation and task completion.

What Are Recent G2 Reviews of Edgescan?

What Are G2 Users Discussing About Edgescan?
Mend.io

Modern risk doesn't live in one layer, it lives between them. Mend.io is built for every risk, across AI and AppSec, securing the code layer, the AI layer, and the interactions between them. From discovery and red teaming to guardrails and runtime protection, Mend.io delivers continuous protection across the entire AI application lifecycle. Mend.io solutions include: 1. Mend AI secures the layer where modern risk actually lives—the interaction between code and AI. It continuously discovers AI components (agents, prompts, models), tests real behavioral risk through automated red teaming, and enforces in-app runtime guardrails for one continuous control system for the AI lifecycle. 2. Mend AppSec secures the modern code layer by continuously discovering and prioritizing risk across code, libraries, containers, and dependencies, giving teams the clarity they need to reduce exposure and ship secure software faster. 3. Mend Renovate secures the foundation of every codebase by automatically updating dependencies, rating the likelihood each update will succeed without breaking changes, and grouping them by confidence level so teams can resolve them faster.

Average Rating: 4.3/5.0

Total Reviews: 117

Who Is the Company Behind Mend.io?

  • Seller: Mend
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Boston, Massachusetts
  • Twitter: @Mend_io
    11,256 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    259 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 36% Small, 33% Large

What Do G2 Reviewers Say About Mend.io?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the scanning efficiency of Mend.io, enabling quick and accurate scans across multiple repositories seamlessly.
  • Users appreciate the ease of use of Mend.io, made simpler by effective integrations and an attractive interface.
  • Users value the easy integrations of Mend.io, allowing seamless scanning across multiple repositories and CI/CD platforms.
  • Users appreciate the quick and accurate scanning capabilities of Mend.io, benefiting from a range of integrations.
  • Users value the automated vulnerability detection of Mend.io, enhancing efficiency in identifying and addressing issues seamlessly.
Cons
  • Users face integration issues with Mend.io, finding it difficult to connect on-premise tools and features like Jira.
  • Users express concern over limited features in Mend.io, necessitating workarounds for optimal functionality and integration.
  • Users find the missing features in Mend.io cumbersome, often resorting to workarounds for integration and functionality.
  • Users face complex implementation, with challenging integration and frequent false positives affecting their experience.
  • Users find the confusing interface challenging due to the awkward transitions between different portals.

What Are Recent G2 Reviews of Mend.io?

What Are G2 Users Discussing About Mend.io?

Flyingduck

Flyingduck is a Comprehensive Code security Intelligence platform that identifies and remediates security vulnerabilities in the code base. Key modules are SBOM Compliance, SCA, SAST, Secrets Analysis. We also identify Business Logic Issues in the code such as OTP Bypass, Transaction Manipulation type issues with our Deep Logic Analysis AI engine.

Average Rating: 5.0/5.0

Total Reviews: 5

Who Is the Company Behind Flyingduck?

  • Seller: Flyingduck
  • Year Founded: 2024
  • HQ Location: Hyderabad, IN
  • LinkedIn® Page: www.linkedin.com
    17 employees on LinkedIn®
  • Ownership: Sarat Lingamallu
  • Phone: +919550681242

Who Uses This Product?

  • Company Size: 60% Medium, 20% Large

What Are Recent G2 Reviews of Flyingduck?

Whitespots Security Portal

The ASPM (Application Security Posture Management) platform that runs on your infrastructure, not ours. Air-gapped if you need it. 🔌 Onboard an entire repo group with one webhook. No pipeline rewrites, no CI expertise, no repo left unscanned 🔎 30+ scanners out of the box across code, dependencies, secrets, IaC, domains, containers, hosts and cloud. Or plug in ANY tool you already pay for 🔥 Duplicates merged across tools, false positives stripped automatically. What survives is real 🧑‍💻 Findings land where developers already are: Jira, merge request comments, IDE ⏱️ Every finding gets an owning team and an SLA clock. Quality gate blocks the release when you say so 📈 One risk number for the board, WRT, tracked against a risk appetite you set 💶 Fixed price per organization. No per-developer maths, no per-seat surprises Your code never leaves your perimeter. The only outbound connection is license activation.

Average Rating: 5.0/5.0

Total Reviews: 10

Who Is the Company Behind Whitespots Security Portal?

Who Uses This Product?

  • Company Size: 60% Medium, 20% Large

What Do G2 Reviewers Say About Whitespots Security Portal?

AI-generated summary from verified user reviews

Pros
  • Users praise the effortless setup of Whitespots Security Portal, seamlessly integrating into their workflows without complications.
  • Users highlight the intuitive UI/UX and seamless integration of Whitespots Security Portal, enhancing workflow and efficiency.
  • Users value the speed and ease of integration of Whitespots Security Portal, enhancing their security workflow effortlessly.
  • Users appreciate the intuitive UI of Whitespots Security Portal, which enhances monitoring and response efficiency.
  • Users value the enhanced vulnerability detection of Whitespots, significantly improving overall security and monitoring efficiency.
Cons
  • Users note poor analytics in the Whitespots Security Portal, particularly for specialized management reports.
  • Users find the poor documentation challenging, particularly for advanced features and initial onboarding processes.
  • Users find the interface not always user-friendly, though support resolves issues upon request.

What Are Recent G2 Reviews of Whitespots Security Portal?

Arnica

Arnica is a comprehensive application security posture management (ASPM) platform that protects developers, source code, and products throughout the software development lifecycle. The platform provides real-time application security scanning with 100% coverage across the software supply chain, addressing risks in Static Application Security Testing (SAST), Software Composition Analysis (SCA), Infrastructure as Code (IaC), hardcoded secrets detection, and more. At its core, Arnica offers AI-native security governance that takes control of AI-generated code through advanced AI SAST scanning and agentic rules enforcement. The platform automatically injects centrally-controlled security requirements into AI coding agents like Copilot, Cursor, and Claude at the point of code generation, ensuring every line of AI-written code is secure by default before vulnerabilities reach production. This approach addresses 92% of risks before they ever reach production environments. Arnica's pipelineless architecture provides automatic coverage for every repository without requiring CI/CD pipeline integrations or IDE deployments. The platform scans every code change at the feature branch level, delivering developer-native workflows that keep teams focused on building features rather than chasing security issues. Risk prioritization is enhanced through OWASP Top 10, CVSS, EPSS, and KEV scoring, combined with organizational context to surface the most critical vulnerabilities. The platform excels in developer experience by delivering security findings directly within existing workflows through Slack, Microsoft Teams, pull request comments, and automated ticket management in Jira and Azure DevOps Boards. AI-powered mitigation suggestions provide context-aware, automated fixes that align with organizational coding standards, significantly reducing mean-time-to-remediation. Key security capabilities include real-time secrets detection with automatic validation and mitigation, comprehensive container scanning that maps vulnerabilities directly to source code, and intelligent dependency management with automated SCA upgrades. The platform maintains SOC 2 Type 2 compliance and ISO 27001 certification, ensuring enterprise-grade security standards. Arnica's unique value proposition lies in its ability to scale security across entire organizations while maintaining development velocity, providing complete visibility into code risks, and enabling proactive security measures that prevent vulnerabilities from reaching production environments.

Average Rating: 4.8/5.0

Total Reviews: 9

Who Is the Company Behind Arnica?

  • Seller: Arnica
  • Company Website:
  • Year Founded: 2021
  • HQ Location: Alpharetta, Georgia
  • Twitter: @arnicaio
    124 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    64 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 56% Large, 33% Small

What Do G2 Reviewers Say About Arnica?

AI-generated summary from verified user reviews

Pros
  • Users value the accuracy of findings from Arnica, enhancing security through effective management of privileges.
  • Users value Arnica for its actionable recommendations, simplifying the management of elevated privileges in source code repositories.
  • Users appreciate the easy setup and administration of Arnica, which saves valuable time and effort.
  • Users love the easy setup of Arnica, making administration a quick and efficient process.
  • Users value Arnica for its ability to reduce attack surface by identifying and rectifying excessive privileged access efficiently.
Cons
  • Users find the paid features limited for smaller teams, restricting access to crucial protections in Arnica.

What Are Recent G2 Reviews of Arnica?

What Are G2 Users Discussing About Arnica?

AccuKnox

AccuKnox Zero Trust CNAPP cloud security protects public and private clouds, Kubernetes and VMs. AccuKnox is a AI-powered Zero Trust Cloud Native Security Platform that helps organizations comply with various frameworks and over 33+ compliance controls, including MITRE, NIST, STIG, CIS, PCI-DSS, GDPR, and SOC2. AccuKnox enhances InfraSec and DevSecOps teams by enabling them to detect, prioritize, prevent and protect against advanced and sophisticated cloud attacks. Key Benefits 1. Code to Cloud Security 2. Easy Deployment 3. Extensive Coverage. 4. Preemptive Attack Mitigation 5. Open Source and Innovative Key Differentiators - Inline Preemptive Security (as opposed to Post-attack mitigation) - Secures modern workloads (Kubernetes) and traditional workloads (VMs) - Multi-Cloud, Private, Air-gapped, and Hybrid Cloud Security - IaC – Infrastructure As Code scanning - Secures AI/ML workloads like Jupyter Notebooks Features - Automated Zero Trust Cloud Security (Public, Private, Hybrid, Air-gapped) - Vulnerability Management & Prioritization - Run-time security, Micro-segmentation - Application Firewalling, Kernel Hardening - Drift Detection & Audit Trail - Continuous Diagnostics & Mitigation - GRC – CIS, HIPAA, GDPR, SOC2, STIG, MITRE, NIST - Securing Mission-Critical Workloads like Vault - Securing AI workbenches like Jupyter Notebooks - Cryptojacking and TNTBotinger Attacks With over 15+ patents, we're proud to offer an OpenSource, DevSecOps-led delivery model. To top it off, we have an ongoing R&D partnership with the esteemed SRI International. We deliver both Static and Runtime Security, anchored on innovations in Cloud Security and AI/ML-based Anomaly Detection. Static Code Analysis - Deeply analyze your code for vulnerabilities and weaknesses. CI/CD Pipelines Scanning - Continuously scan your pipelines for security flaws and risks. Container Security - Fortify your containers with robust security measures. Kubernetes Orchestration - Seamlessly manage and secure your Kubernetes environments. Secret Scanning - Detect and protect sensitive information from unauthorized access.

Average Rating: 4.4/5.0

Total Reviews: 12

Who Is the Company Behind AccuKnox?

  • Seller: Accuknox
  • Year Founded: 2020
  • HQ Location: California, USA
  • Twitter: @AccuKnox
    341 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    197 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 46% Large, 31% Medium

What Do G2 Reviewers Say About AccuKnox?

AI-generated summary from verified user reviews

Pros
  • Users highly value AccuKnox for its comprehensive security features that enhance cloud and Kubernetes environments.
  • Users highlight the high security level of AccuKnox, ensuring robust protection for cloud workloads and integrations.
  • Users appreciate the seamless cloud integration of AccuKnox, enhancing security and simplifying compliance with major providers.
  • Users value AccuKnox for its continuous compliance features, enhancing security and adaptability in their cloud environments.
  • Users praise the exceptional customer support from AccuKnox, highlighting their quick response and detailed understanding of needs.
Cons
  • Users find the difficult learning curve challenging, requiring prior knowledge of Kubernetes to manage AccuKnox effectively.
  • Users find the complex setup of AccuKnox challenging, particularly for those lacking security management experience.
  • Users find AccuKnox to be cost prohibitive, which may deter some from considering the solution.
  • Users often experience poor customer support, citing slow responses and the need for frequent follow-ups.
  • Users find the setup and management complexity of AccuKnox challenging, particularly for those with limited security knowledge.

What Are Recent G2 Reviews of AccuKnox?

Phoenix Security

Phoenix Security is a Contextual ASPM focused on product security. It combines risk-based Vulnerability Management, Application Security Posture Management, and Cloud into a risk and remediation-first platform. Phoenix was founded by the team running Application security and Cloud security posture for HSBC. What sets Phoenix apart is the risk-based quantitative view, the level of customization, and the scanning code to cloud vulnerabilities. Phoenix security utilizes threat intelligence, dependency analysis, and cloud analysis to detect which category of vulnerabilities needs to be addressed and minimize the false positives.

Average Rating: 5.0/5.0

Total Reviews: 1

Who Is the Company Behind Phoenix Security?

  • Seller: Phoenix Security
  • Year Founded: 2021
  • HQ Location: London, GB
  • Twitter: @sec_phoenix
    268 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    27 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of Phoenix Security?

Xygeni

Xygeni: AI-Native ASPM for the Software Supply Chain Xygeni is an AI-native ASPM (Application Security Posture Management) platform that unifies native and third-party security findings into one prioritized view. Its own detection engines cover SAST, SCA, DAST, Secrets, IaC, Container, CI/CD, and Build Security, and it also ingests results from tools like Snyk, Veracode, and Checkmarx so teams don't have to abandon what they've already invested in. Every finding, regardless of source, gets scored by exploitability, reachability, and business impact through Xygeni's Dynamic Funnels, which is what drives its reported 90% cut in alert noise. Two AI systems sit underneath the platform. CoreAI acts as a correlation and reporting layer for security leaders, turning scattered findings into a single risk narrative. DevAI works earlier, inside the developer's IDE and AI coding assistants, catching problems in both human-written and AI-generated code and proposing fixes before a pull request is even opened. On the supply chain side, Xygeni's MEW engine (Malware Early Warning) is built to catch malicious open-source packages the moment they hit a public registry, ahead of when a formal malware signature would normally exist. Shield takes that enforcement to the developer's own machine, blocking unauthorized package downloads at the OS level before they reach disk. Xygeni also runs a dedicated Code Quality engine across ten languages, ranking maintainability and complexity issues alongside security findings in the same console, so a team can see when the messiest file is also the riskiest one. The platform connects to GitHub, GitLab, Bitbucket, Jenkins, and Azure DevOps, and deploys as SaaS, on-premises, or fully air-gapped. Xygeni was named Hot Company in ASPM and in GenAI Application Security at the 2026 Global InfoSec Awards.

Average Rating: 4.6/5.0

Total Reviews: 4

Who Is the Company Behind Xygeni?

  • Seller: Xygeni Security
  • Year Founded: 2021
  • HQ Location: Madrid, ES
  • Twitter: @xygeni
    178 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    31 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 60% Small, 40% Medium

What Do G2 Reviewers Say About Xygeni?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the comprehensive security features of Xygeni, fostering a secure development environment without hindering productivity.
  • Users value the effective prioritization of security issues in Xygeni, allowing teams to focus on critical threats quickly.
  • Users value the effective risk management of Xygeni, enhancing security without hindering software development processes.
  • Users appreciate the robust security features of Xygeni, enhancing their development process while ensuring compliance and risk management.
  • Users value the seamless CI/CD integration of Xygeni, enabling early vulnerability detection without impacting release schedules.
Cons
  • Users face difficult setup issues with Xygeni, especially when dealing with certain edge cases requiring manual adjustments.
  • Users find the learning curve challenging for newcomers despite a generally intuitive platform, requiring familiarity with AppSec practices.

What Are Recent G2 Reviews of Xygeni?

Heeler

Heeler empowers application security teams to shift left with the context they need to reduce noise, accelerate remediation, and move beyond traditional vulnerability management. By combining ASPM, SCA with static and runtime context, and runtime threat modeling, Heeler transforms AppSec programs from reactive firefighting to proactive, scalable security. How Heeler Helps AppSec Teams • Reduce Noise: AppSec teams and developers are drowning in findings. Heeler delivers unified code, runtime, business and security context, reducing alert noise by up to 95%, so teams can focus on critical issues and fix what matters most. • Fix Remediation: Remediation is broken. Most effort is spent reaching a fix—not implementing it. Heeler automates the remediation lifecycle, cutting effort and time, enabling AppSec teams to scale alongside engineering. • Move Beyond Vulnerabilities: With Heeler, continuous runtime threat modeling becomes a reality. Decompose running applications, track changes, compare deployments, and stop risks in real time—all before they reach production. Why Heeler is Essential Modern applications are more complex and dynamic than ever, expanding attack surfaces and making end-to-end security modeling nearly impossible without the right tools. Heeler bridges this gap, addressing the root causes of unscalable AppSec programs: • Lack of Context: Disparate data silos make understanding application behavior and identifying risks challenging. • Labor-Intensive Processes: Without unified context, security efforts are manual, unscalable, and push risk identification too far right. • Firefighting Mode: Security and engineering teams are trapped addressing too many findings and often focus their time on the wrong threats, leaving no bandwidth for secure-by-design initiatives. Key Capabilities • ProductDNA (Unified Context): Automates a real-time service catalog, mapping changesets to deployments and modeling every service with integrated code, runtime, business, and security context. • Runtime Threat Modeling: Enables continuous threat modeling with tools to decompose applications, track changes, compare deployments, and uncover risks in real time. • ASPM: Heeler reduces alert noise by up to 95% and automates remediation workflows, scaling security seamlessly with engineering demands. • SCA with Static and Runtime Context: Combines static and runtime data with business and deployment context, delivering next-gen SCA that prioritizes what matters, strengthens security, and simplifies AppSec workflows. Heeler ensures AppSec teams and developers have the context they need to shift left and build secure-by-design applications—effortlessly.

Who Is the Company Behind Heeler?

Proscan

Proscan is a unified application security platform designed to help organizations streamline the management of their security tools. By integrating multiple standalone solutions into a single cohesive experience, Proscan provides comprehensive security visibility across the entire software stack. This platform replaces the complexity of managing various tools for static analysis, dynamic testing, and dependency scanning, allowing teams to focus on building secure applications without the hassle of juggling disparate systems. The platform is particularly beneficial for security teams, developers, and engineering leaders who require a consolidated view of application security risks. Proscan combines nine specialized security scanners, including Static Application Security Testing (SAST), which analyzes source code in over 30 programming languages using advanced detection methods. Dynamic Application Security Testing (DAST) further enhances security by testing live applications, identifying vulnerabilities that may only become apparent during runtime. Additionally, Software Composition Analysis (SCA) evaluates open-source dependencies across 196 package ecosystems, helping organizations detect known vulnerabilities before they can impact production environments. Proscan's capabilities extend beyond code analysis. It includes scanning for hardcoded secrets, misconfigurations in Infrastructure-as-Code, and vulnerabilities in container images. The platform also offers API security testing that validates endpoints against the OWASP API Security Top 10, ensuring robust protection for applications that leverage APIs. For organizations developing AI-powered applications, Proscan features a dedicated AI and LLM security scanner that identifies potential risks associated with prompt injections and other vulnerabilities, utilizing over 4,600 techniques mapped to the OWASP LLM Top 10. Artificial intelligence plays a crucial role in enhancing Proscan's efficiency and accuracy. The platform employs machine-learning algorithms to reduce false positives and prioritize vulnerabilities based on their potential impact. This intelligent approach allows teams to focus on the most critical security issues while providing clear explanations and actionable remediation guidance. Proscan integrates seamlessly into existing development workflows, offering IDE plugins and native CI/CD integrations that ensure security checks are part of the development process without causing disruptions. Compliance readiness is another key feature of Proscan, as it generates audit-ready reports aligned with major security standards, including OWASP Top 10, PCI DSS, HIPAA, and GDPR. This automated evidence collection simplifies the compliance process, providing organizations with the necessary documentation in various formats. Proscan is designed for security teams looking to consolidate fragmented toolchains, developers needing quick feedback, and managed security service providers managing multiple client environments, making it a versatile solution for modern application security challenges.

Who Is the Company Behind Proscan?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024