Best AI SOC Agents for Small Business

How Many AI SOC Agents Products Does G2 Track?

Total Products under this Category: 56

Category Stats (Nov 2026)

  • Average Rating: 4.62/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Mate Security (+8.57%) - Among all products in this category, Mate Security recorded the largest rating increase compared to last month

Last updated: November 12, 2026

How Does G2 Rank AI SOC Agents Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,100+ Authentic Reviews
  • 56+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

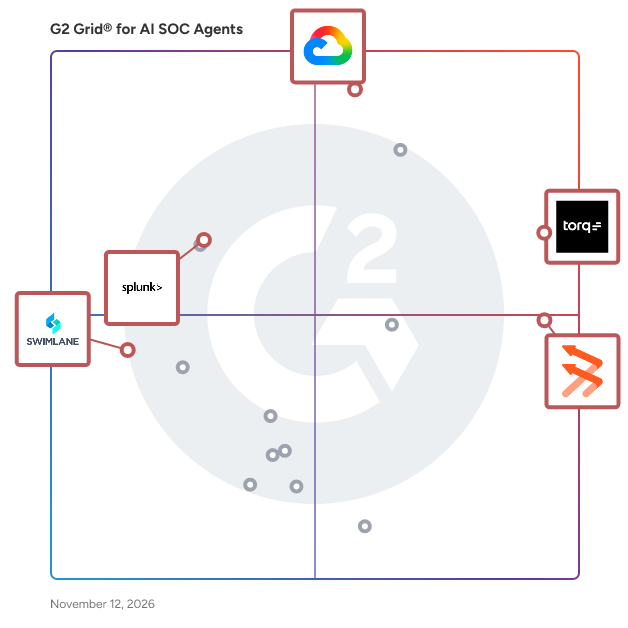
G2 Grid® for AI SOC Agents

G2 Grid® for AI SOC Agents plotting products by satisfaction and market presence

Highlighted products: Google Security Operations, UnderDefense MAXI, Torq AI SOC Platform, Splunk Enterprise Security, and Swimlane.

Underlying data: [Grid® JSON](https://www.g2.com/categories/ai-soc-agents/grids.json?focus%5B%5D=google-security-operations&focus%5B%5D=underdefense-maxi&focus%5B%5D=torq-ai-soc-platform&focus%5B%5D=splunk-enterprise-security&focus%5B%5D=swimlane&segment=small-business)

Google Security Operations

Google Security Operations offers a unified experience across SIEM, SOAR, and threat intelligence to drive better detection, investigation, and response. Collect security telemetry data, apply threat intel to identify high priority threats, drive response with playbook automation, case management, and collaboration. It also provides Gemini-native agentic defense to help autonomously handle workflows like alert triage, threat hunting, and detection engineering. Google Security Operations also supports AI Threat Defense to monitor, detect, and respond to threats from code you do not own or cannot patch.

Average Rating: 4.4/5.0

Total Reviews: 125

Who Is the Company Behind Google Security Operations?

  • Seller: Google
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG
  • Phone: +1 (650) 253-0000

Who Uses This Product?

  • Who Uses This: Developer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 37% Medium, 36% Small

What Do G2 Reviewers Say About Google Security Operations?

AI-generated summary from verified user reviews

Pros
  • Users value the centralized detection and investigation capabilities of Google Security Operations for efficient threat management.
  • Users appreciate the scalability and efficiency of Google Security Operations for effective threat detection and response.
  • Users find Google Security Operations to have a user-friendly interface, enabling quick analysis and effective threat responses.
  • Users value the comprehensive security capabilities of Google Security Operations for effective threat detection and response.
  • Users appreciate the seamless integrations of Google Security Operations, enhancing threat detection and data analysis across the ecosystem.
Cons
  • Users feel that the high cost of Google Security Operations is a significant drawback affecting overall satisfaction.
  • Users find a steep learning curve when trying to utilize Google Security Operations effectively, especially for the inexperienced.
  • Users find the implementation complexity of Google Security Operations challenging, requiring significant time and resources to manage.
  • Users find the learning difficulty of Google Security Operations challenging, requiring substantial time to master its features.
  • Users find limited customization in Google Security Operations hinders adaptability to specific security requirements and user-friendliness.

What Are Recent G2 Reviews of Google Security Operations?

UnderDefense MAXI

UnderDefense is an Agentic AI SOC & Compliance Automation platform trusted by 200+ enterprises in the US and EU. It works on top of the security stack you already own — no rip-and-replace, no added headcount — so your team spends its time on decisions, not triage. ◆ 10+ years of operations with zero ransomware incidents ◆ 250+ integrations across any SIEM, EDR, or cloud stack ◆ 24/7 IR team available whenever you need urgent support WHAT WE OFFER AGENTIC AI SOC UnderDefense Agentic AI SOC works on top of your existing security stack, turning every security team into a machine-speed defense unit without tool replacement or headcount expansion. It takes over the investigative routine that pulls your team away from strategic decisions: enrichment, correlation, triage. ▸ Investigation at Machine Speed: Agentic AI SOC accesses tools, enriches data, and performs deep cross-environment investigations at machine speed. It correlates, triages, and forms conclusions, offloading all repetitive work from your team. ▸ 2 Minutes Per Alert: Complete SIEM queries, threat intel checks, and cross-system correlations in 2 minutes. Every step fully observable and auditable. ▸ Human at Every Decision Point: The platform verifies suspicious activity with end-users via Slack or Teams, then routes containment decisions to your team or our 24/7 IR experts. COMPLIANCE AUTOMATION Stop chasing spreadsheets. UnderDefense MAXI Compliance AI automatically collects continuous evidence across ISO 27001, SOC 2, PCI DSS, GDPR, and HIPAA, and publishes your live posture through a shareable Trust Center link. ▸ 40% audit-ready in the first 40 minutes ▸ 2X faster time-to-compliance vs. traditional audit ▸ 24/7 continuous monitoring — posture always current, not point-in-time WHY WE ARE BETTER ✓ No rip-and-replace: Works with your current SIEM (Splunk, Sentinel, Chronicle, QRadar, Elastic), EDR, and cloud tools. Logs stay in your data lake. ✓ True Multi-Environment Coverage: Comprehensive visibility across on-premises, cloud (AWS, GCP, Azure), SaaS, network, identity, and OT/SCADA environments. ✓ The Only Agentic AI SOC with on-prem deployment: Full AI SOC inside your own infrastructure. No telemetry leaving your environment. Air-gapped available. ✓ Right-Sized for Any Enterprise: Detection engineering and support tailored to your organization, not a one-size-fits-all template. Start your free trial at underdefense.com

Average Rating: 4.9/5.0

Total Reviews: 78

Who Is the Company Behind UnderDefense MAXI?

Who Uses This Product?

  • Who Uses This: CEO
  • Top Industries: Marketing and Advertising, Information Technology and Services
  • Company Size: 51% Small, 43% Medium

What Do G2 Reviewers Say About UnderDefense MAXI?

AI-generated summary from verified user reviews

Pros
  • Users value the high visibility UnderDefense MAXI provides into security alerts, streamlining threat management and response.
  • Users commend the responsive and effective customer support of UnderDefense MAXI, enhancing their cybersecurity management and experience.
  • Users commend UnderDefense MAXI for its effective cybersecurity solutions, enhancing security management and response efficiency.
  • Users value the information accuracy provided by UnderDefense, which clarifies security issues and enhances response efficiency.
  • Users highlight the quick issue resolution by UnderDefense, improving security alert management and enhancing overall security operations.
Cons
  • Users feel a lack of automation features limits control over the dashboard for UnderDefense MAXI.
  • Users desire more control over the dashboard, seeking enhanced customization and automated update options with UnderDefense MAXI.
  • Users note that limited integration requires significant setup time to ensure proper tool configuration.
  • Users find the setup process challenging, requiring significant time and effort for proper tool integration.

What Are Recent G2 Reviews of UnderDefense MAXI?

Torq AI SOC Platform

Torq is the AI SOC platform that combines agentic insights and automation so that enterprises can triage, investigate, and respond to actual risks, faster. Torq streamlines every step from alert through resolution. The platform analyzes your risk context to identify your biggest threats. Working alongside your SecOps staff, the Torq platform integrates with your security stack to facilitate containment and remediation workflows.

Average Rating: 4.8/5.0

Total Reviews: 166

Who Is the Company Behind Torq AI SOC Platform?

  • Seller: torq
  • Company Website:
  • Year Founded: 2020
  • HQ Location: New York, US
  • LinkedIn® Page: www.linkedin.com
    470 employees on LinkedIn®
  • Total Revenue (USD mm): $21

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 49% Medium, 30% Small

What Do G2 Reviewers Say About Torq AI SOC Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the user-friendly interface of Torq AI SOC Platform, enhancing their incident management and workflow efficiency.
  • Users value the strong security overview provided by Torq AI SOC Platform, enhancing incident tracking and vulnerability management.
  • Users appreciate the seamless automation of Torq AI SOC Platform, enhancing security and simplifying workflow management.
  • Users value the intuitive dashboards of Torq AI SOC Platform, centralizing incident views and enhancing security operations.
  • Users appreciate the comprehensive threat detection of Torq AI, delivering crucial insights and enhancing security across networks.
Cons
  • Users find the difficult learning curve challenging, requiring time and training to fully utilize Torq AI SOC Platform.
  • Users note a slight learning curve with the Torq AI SOC Platform, making it challenging for beginners to master.
  • Users feel the missing built-in playbooks hinder the ease of onboarding and overall management within the Torq AI SOC Platform.
  • Users suggest improvement needed in documentation and feature management for better usability of Torq AI SOC Platform.
  • Users experience poor interface design, with issues like unresponsive buttons and unintuitive navigation that hinder efficiency.

What Are Recent G2 Reviews of Torq AI SOC Platform?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Splunk Enterprise Security

Splunk Enterprise Security (ES) is a data-centric, modern security information and event management (SIEM) solution that delivers data-driven insights for full breadth visibility into your security posture so you can protect your business and mitigate risk at scale. With unparalleled search and reporting, advanced analytics, integrated intelligence, and prepackaged security content, Splunk ES accelerates threat detection and investigation, letting you determine the scope of high-priority threats to your environment so you can quickly take action. Built on an open and scalable data platform, you can stay agile in the face of evolving threats and business needs. Our extensive ecosystem of Splunk, partner, and community-built integrations as well as flexible deployment options ensure your technology investments are working in tandem with Splunk ES whilst meeting you wherever you are on your cloud, multi-cloud, or hybrid journey.

Average Rating: 4.3/5.0

Total Reviews: 226

Who Is the Company Behind Splunk Enterprise Security?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO
  • Phone: 847-678-6600

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 60% Large, 30% Medium

What Do G2 Reviewers Say About Splunk Enterprise Security?

AI-generated summary from verified user reviews

Pros
  • Users value the powerful log analytics of Splunk Enterprise Security, enhancing their ability to analyze and correlate logs effectively.
  • Users benefit from the smart threat detection of Splunk Enterprise Security, enabling early identification of security issues.
  • Users value the extensive integration options of Splunk Enterprise Security, enhancing their existing Splunk investments and workflows.
  • Users value the versatility in data handling of Splunk Enterprise Security, enhancing insights and decision-making across domains.
  • Users appreciate the real-time monitoring capabilities of Splunk Enterprise Security, enhancing their cybersecurity responsiveness and decision-making.
Cons
  • Users find the complex setup of Splunk Enterprise Security time-consuming and challenging, impacting initial deployment effectiveness.
  • Users find the difficult learning curve of Splunk Enterprise Security challenging, especially for those new to data analysis.
  • Users often cite high costs at scale as a significant drawback, especially with growing data ingestion needs.
  • Users express concerns about poor customer support, highlighting the need for more responsive assistance and resources.
  • Users often face setup difficulties with Splunk Enterprise Security, requiring significant time and resources for configuration.

What Are Recent G2 Reviews of Splunk Enterprise Security?

What Are G2 Users Discussing About Splunk Enterprise Security?

Swimlane

Swimlane automates the work security teams hate. As the leader in agentic AI security automation, Swimlane unifies operations across the SOC and beyond with its platform, Swimlane Turbine. The problem is real: over three million SecOps roles sit unfilled, and analysts drown in alerts while juggling 30+ disconnected tools, each with its own schema and quirks. Meanwhile, the average breach now costs $4.5 million. Swimlane closes that gap. Swimlane Hero AI, embedded within the Turbine platform, turns natural-language prompts into automated investigations and responses, cutting MTTR by 75%. Analysts trigger remediation with one click, backed by NIST-aligned case management. Turbine Canvas lets teams build playbooks and agents with no, low, or full code, so automation doesn't wait on a developer's calendar. The Swimlane Marketplace adds a growing library of agents, integrations, and playbooks, built on demand at no cost, ending vendor lock-in for good. Under the hood, Swimlane's Active Sensing Fabric ingests data at scale, pushing capability beyond traditional SOAR. Cloud-native architecture backs it up: one customer runs 25 million automated actions a day at 75,000 actions per minute. That's not a demo number. That's production. Analysts get customizable dashboards and AI-augmented reporting that turn raw activity into KPIs executives actually read, proving ROI without a translation layer. The market has taken notice. Independent evaluations against 15+ competitors all point the same direction: Swimlane leads. Inc. named it Best in Business. Customers at Northern Power, Toshiba, Weedmaps, and InComm Payments back that up, citing customizable playbooks, dashboards, and a professional services team that shows up when it counts. Swimlane doesn't just orchestrate security tasks. It gives every security function, from vulnerability management to compliance to business continuity, a way to move faster than the threats they're chasing.

Average Rating: 4.5/5.0

Total Reviews: 45

Who Is the Company Behind Swimlane?

  • Seller: Swimlane
  • Year Founded: 2014
  • HQ Location: Boulder, US
  • LinkedIn® Page: www.linkedin.com
    271 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 60% Medium, 31% Small

What Do G2 Reviewers Say About Swimlane?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Swimlane, appreciating its low-code automation and seamless integration capabilities.
  • Users appreciate the easy integrations of Swimlane, enhancing their playbooks with fast and robust connectivity options.
  • Users appreciate the personalization and robust integration features of Swimlane, enhancing usability and flexibility in security management.
  • Users value the seamless integrations of Swimlane, enhancing playbook creation and collaboration across various technologies.
  • Users value the flexibility of low-code automation in Swimlane, enabling extensive opportunities for security operations enhancements.
Cons
  • Users find Swimlane complex to set up and maintain, but support is timely and helpful in overcoming challenges.
  • Users find the learning curve steep initially with Swimlane, requiring time to become comfortable and proficient.
  • Users find the limited resources available for Swimlane challenging, particularly during initial deployment and playbook design.
  • Users report poor customer support, with slow responses and challenges in diagnosing upgrade issues.
  • Users find Swimlane's poor interface design cluttered and difficult to navigate, requiring a more modern refresh.

What Are Recent G2 Reviews of Swimlane?

What Are G2 Users Discussing About Swimlane?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated