Best Enterprise Static Application Security Testing (SAST) Software

How Many Static Application Security Testing (SAST) Software Products Does G2 Track?

Total Products under this Category: 154

Category Stats (Nov 2026)

  • Average Rating: 4.54/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Endor Labs (+0.46%) - Among all products in this category, Endor Labs recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Static Application Security Testing (SAST) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,900+ Authentic Reviews
  • 154+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

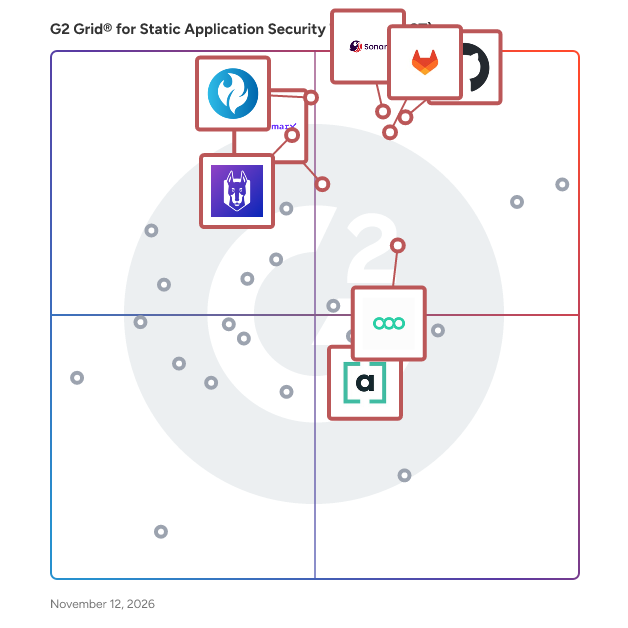
G2 Grid® for Static Application Security Testing (SAST) Software

G2 Grid® for Static Application Security Testing (SAST) Software plotting products by satisfaction and market presence

Highlighted products: HCL AppScan, SonarQube, GitLab, GitHub, Arnica, Checkmarx, Semgrep, and Snyk.

Underlying data: [Grid® JSON](https://www.g2.com/categories/static-application-security-testing-sast/grids.json?focus%5B%5D=hcl-appscan&focus%5B%5D=sonarqube&focus%5B%5D=gitlab&focus%5B%5D=github&focus%5B%5D=arnica&focus%5B%5D=checkmarx&focus%5B%5D=semgrep&focus%5B%5D=snyk&segment=enterprise)

HCL AppScan

HCL AppScan is a comprehensive suite of market-leading application security testing solutions (SAST, DAST, IAST, SCA, API), available on-premises and on-cloud. These powerful DevSecOps tools pinpoint application vulnerabilities, allowing for quick remediation in every phase of the software development lifecycle. Fast and Accurate Scanning for Secure DevOps Developers and DevOps teams can quickly and accurately scan code, applications, and APIs for security vulnerabilities while applications are being developed. This allows companies to fix issues at the earliest stages of the software development lifecycle, when it is least costly to the business. Focus on the Fix Continuous monitoring with IAST, along with auto issue correlation with DAST and SAST scan results allows DevOps teams to group and prioritize findings for faster, more streamlined remediation. Enterprise Management for Security Teams Centralized, easy-to-use dashboards provide visibility and oversight of all security scanning and remediation, and allow users to set scan parameters and compliance policies.

Average Rating: 4.2/5.0

Total Reviews: 125

How Do G2 Users Rate HCL AppScan?

  • Test Automation: 8.9/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.1/10)
  • Quality of Support: 8.5/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 8.6/10 (Category avg: 8.5/10)

Who Is the Company Behind HCL AppScan?

  • Seller: HCL Technologies
  • Company Website:
  • Year Founded: 1999
  • HQ Location: Noida, Uttar Pradesh
  • LinkedIn® Page: www.linkedin.com
    258,955 employees on LinkedIn®
  • Ownership: NSE - National Stock Exchange of India

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Large, 25% Medium

What Are Recent G2 Reviews of HCL AppScan?

What Are G2 Users Discussing About HCL AppScan?

SonarQube

Sonar, the industry standard for code verification and automated code review, helps reduce outages, improve security, and lower risks associated with AI and agentic coding. As an independent verification platform, Sonar enables organizations to securely develop at the speed of AI. Sonar is the foundation for high-performance software engineering, analyzing over 750 billion lines of code daily to ensure applications are secure, reliable, and maintainable. Rooted in the open source community, Sonar is trusted by 7M+ developers globally, including teams at ServiceNow, Booking.com, Deutsche Bank, AstraZeneca, and Ford Motor Company.

Average Rating: 4.4/5.0

Total Reviews: 164

How Do G2 Users Rate SonarQube?

  • Test Automation: 6.7/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.1/10)
  • Quality of Support: 8.2/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 7.1/10 (Category avg: 8.5/10)

Who Is the Company Behind SonarQube?

  • Seller: Sonar
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Geneva, Switzerland
  • LinkedIn® Page: www.linkedin.com
    1,041 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, DevOps Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 41% Large, 41% Medium

What Do G2 Reviewers Say About SonarQube?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the high-quality code analysis from SonarQube, ensuring cleaner, more reliable, and maintainable code.
  • Users appreciate SonarQube's separation of new and old code, enhancing prioritization of findings and improving overall code quality.
  • Users appreciate the effective issue identification of SonarQube, which enhances code quality and facilitates timely resolutions.
  • Users appreciate the ease of use of SonarQube, highlighting its simple setup and seamless CI/CD integration.
  • Users appreciate the easy integrations of SonarQube with CI/CD workflows, enhancing overall code quality and efficiency.
Cons
  • Users often face software bugs in SonarQube, leading to confusion with false positives and complex error messages.
  • Users find the complex configuration of SonarQube challenging, especially with initial setup and rule tuning in large projects.
  • Users report experiencing false positives that necessitate extra time for manual review and adjustments.
  • Users find the configuration complexity of SonarQube challenging, particularly with large projects and excessive warnings.
  • Users find the initial setup and configuration complex, especially for large projects, requiring time and careful tuning.

What Are Recent G2 Reviews of SonarQube?

What Are G2 Users Discussing About SonarQube?

GitLab

GitLab is the most comprehensive AI-Powered DevSecOps platform that enables software innovation by empowering development, security, and operations teams to build better software, faster. With GitLab, teams can create, deliver, and manage code quickly and continuously instead of managing disparate tools and scripts. GitLab helps your teams across the complete DevSecOps lifecycle, from developing, securing, and deploying software. What makes us truly different? - Flexibility: Consume as a service or manage your own deployment - Cloud-Agnostic: Deploy anywhere with no vendor lock-in - No rip and replace: Scale to a platform approach at your own pace

Average Rating: 4.5/5.0

Total Reviews: 888

How Do G2 Users Rate GitLab?

  • Test Automation: 9.2/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.1/10)
  • Quality of Support: 8.5/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 8.9/10 (Category avg: 8.5/10)

Who Is the Company Behind GitLab?

  • Seller: GitLab Inc.
  • Year Founded: 2014
  • HQ Location: San Francisco, California
  • LinkedIn® Page: www.linkedin.com
    3,431 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 37% Medium, 37% Small

What Do G2 Reviewers Say About GitLab?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use in GitLab, appreciating its intuitive interface and straightforward setup for seamless collaboration.
  • Users appreciate the powerful all-in-one functionalities of GitLab that enhance collaboration and streamline development workflows.
  • Users value GitLab's integrated CI/CD feature, enhancing collaboration and streamlining code management seamlessly.
  • Users value the integrated CI/CD in GitLab, enhancing workflow efficiency and collaboration seamlessly.
  • Users value the seamless integration of GitLab with security tools, enhancing workflow efficiency and convenience.
Cons
  • Users find the complexity of the interface challenging, especially with large projects and advanced features being tiered.
  • Users find the difficult learning curve challenging, particularly when adapting to GitLab's complex features and structure.
  • Users often find the confusing interface of GitLab challenging, especially when navigating its extensive features and settings.
  • Users find the complex user interface challenging, especially with large projects, affecting performance and usability.
  • Users find the learning curve steep when adapting to GitLab's many features and unique group structures.

What Are Recent G2 Reviews of GitLab?

What Are G2 Users Discussing About GitLab?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

GitHub

GitHub is where the world builds software. Millions of individuals, organizations and businesses around the world use GitHub to discover, share, and contribute software. Developers at startups to Fortune 50 companies use GitHub, every step of the way.

Average Rating: 4.7/5.0

Total Reviews: 2,368

How Do G2 Users Rate GitHub?

  • Test Automation: 8.6/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.1/10)
  • Quality of Support: 8.7/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 8.4/10 (Category avg: 8.5/10)

Who Is the Company Behind GitHub?

  • Seller: GitHub
  • Year Founded: 2008
  • HQ Location: San Francisco, CA
  • LinkedIn® Page: www.linkedin.com
    6,653 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 47% Small, 31% Medium

What Do G2 Reviewers Say About GitHub?

AI-generated summary from verified user reviews

Pros
  • Users love the user-friendly interface of GitHub, enjoying seamless collaboration and efficient project management.
  • Users value the ease of use of GitHub, praising its intuitive interface and seamless collaboration features.
  • Users value the efficient team collaboration GitHub offers, streamlining workflows and enhancing project management.
  • Users value the smooth collaboration on GitHub, appreciating its all-in-one platform for managing projects and code.
  • Users appreciate how GitHub offers integrated version control, enhancing collaboration and workflow efficiency in development projects.
Cons
  • Users find the complexity of GitHub's features challenging, especially for new team members adapting to advanced workflows.
  • Users find the steep learning curve challenging, especially for advanced features and managing complex repositories.
  • Users find the difficulty for beginners in mastering advanced features and git commands to be quite challenging.
  • Users find the learning difficulty challenging, especially with advanced features and complex workflows for newcomers.
  • Users find the steep learning curve for advanced features challenging, especially for beginners navigating Git commands and workflows.

What Are Recent G2 Reviews of GitHub?

What Are G2 Users Discussing About GitHub?

Arnica

Arnica is a comprehensive application security posture management (ASPM) platform that protects developers, source code, and products throughout the software development lifecycle. The platform provides real-time application security scanning with 100% coverage across the software supply chain, addressing risks in Static Application Security Testing (SAST), Software Composition Analysis (SCA), Infrastructure as Code (IaC), hardcoded secrets detection, and more. At its core, Arnica offers AI-native security governance that takes control of AI-generated code through advanced AI SAST scanning and agentic rules enforcement. The platform automatically injects centrally-controlled security requirements into AI coding agents like Copilot, Cursor, and Claude at the point of code generation, ensuring every line of AI-written code is secure by default before vulnerabilities reach production. This approach addresses 92% of risks before they ever reach production environments. Arnica's pipelineless architecture provides automatic coverage for every repository without requiring CI/CD pipeline integrations or IDE deployments. The platform scans every code change at the feature branch level, delivering developer-native workflows that keep teams focused on building features rather than chasing security issues. Risk prioritization is enhanced through OWASP Top 10, CVSS, EPSS, and KEV scoring, combined with organizational context to surface the most critical vulnerabilities. The platform excels in developer experience by delivering security findings directly within existing workflows through Slack, Microsoft Teams, pull request comments, and automated ticket management in Jira and Azure DevOps Boards. AI-powered mitigation suggestions provide context-aware, automated fixes that align with organizational coding standards, significantly reducing mean-time-to-remediation. Key security capabilities include real-time secrets detection with automatic validation and mitigation, comprehensive container scanning that maps vulnerabilities directly to source code, and intelligent dependency management with automated SCA upgrades. The platform maintains SOC 2 Type 2 compliance and ISO 27001 certification, ensuring enterprise-grade security standards. Arnica's unique value proposition lies in its ability to scale security across entire organizations while maintaining development velocity, providing complete visibility into code risks, and enabling proactive security measures that prevent vulnerabilities from reaching production environments.

Average Rating: 4.4/5.0

Total Reviews: 36

How Do G2 Users Rate Arnica?

  • Test Automation: 10.0/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.1/10)
  • Quality of Support: 8.8/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 10.0/10 (Category avg: 8.5/10)

Who Is the Company Behind Arnica?

  • Seller: Arnica
  • Company Website:
  • Year Founded: 2021
  • HQ Location: Alpharetta, Georgia
  • LinkedIn® Page: www.linkedin.com
    64 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Retail
  • Company Size: 62% Large, 22% Medium

What Do G2 Reviewers Say About Arnica?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the accuracy of findings from Arnica, effectively managing elevated privileges and reducing security risks.
  • Users value the actionable recommendations from Arnica, simplifying the removal of unused elevated privileges for enhanced security.
  • Users love the easy setup and administration of Arnica, saving time while meeting their needs effectively.
  • Users love the easy setup of Arnica, appreciating the quick and efficient administration process.
  • Users value Arnica for its ability to effectively remediate over-provisioning and enhance security without developer input.
Cons
  • Users note the limited access to features in Arnica for smaller teams not on GitHub Enterprise.

What Are Recent G2 Reviews of Arnica?

What Are G2 Users Discussing About Arnica?

Checkmarx

Checkmarx exists so the world can innovate faster than it ever has and still trust what it builds. That purpose starts with closing the Risk Gap — the widening distance between how fast software gets created and how fast risk can be understood and removed. As AI compresses the software development lifecycle from months to minutes, the old model of shipping code with known vulnerabilities and racing to patch it before attackers strike no longer works. Checkmarx's foundation: decades of deterministic threat intelligence and trillions of lines of code scanned each year. The Checkmarx One platform gives enterprises comprehensive application security, built to capture risk, eliminate vulnerabilities, and unify governance. Checkmarx Fusion now pairs that foundation with Claude-powered AI reasoning, unifying both engines to lead the category in detection accuracy. From there, the Checkmarx Assist family — Developer Assist, Triage Assist, and Remediation Assist — prevents vulnerabilities at the point of creation, prioritizes findings by real-world attackability, and generates review-ready fixes, so nothing sits in backlog waiting on a human to catch up. Checkmarx keeps detection and remediation independent. Instead of having the same system that writes the code grade its own work, security teams get oversight they can trust. This is the promise at the center of the mission: developers and agents never have to become security experts, and security leaders never have to take security on faith so enterprises can innovate at machine speed without ever trading speed for certainty.

Average Rating: 4.2/5.0

Total Reviews: 46

How Do G2 Users Rate Checkmarx?

  • Test Automation: 8.9/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.1/10)
  • Quality of Support: 8.4/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 6.7/10 (Category avg: 8.5/10)

Who Is the Company Behind Checkmarx?

  • Seller: Checkmarx
  • Company Website:
  • Year Founded: 2006
  • HQ Location: Paramus, NJ
  • LinkedIn® Page: www.linkedin.com
    997 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 56% Large, 22% Medium

What Do G2 Reviewers Say About Checkmarx?

AI-generated summary from verified user reviews

Pros
  • Users find Checkmarx easy to implement into existing repositories, appreciating its user-friendly interface and comprehensive features.
  • Users appreciate the intuitive user interface of Checkmarx, making security reviews straightforward and user-friendly.
  • Users value the accuracy of results from Checkmarx, noting its effective code review and user-friendly interface.
  • Users appreciate the automation of security reviews in Checkmarx, praising its ease of implementation and user-friendly interface.
  • Users commend Checkmarx for its excellent customer support, consistently available to assist with any issues that arise.
Cons
  • Users experience a high number of false positives with Checkmarx, especially when analyzing Kotlin based projects.
  • Users are frustrated with Checkmarx's poor feature support for Kotlin, leading to numerous false positives in scans.
  • Users note a significant issue with false positives in Kotlin support, affecting their experience when using Checkmarx.
  • Users feel that the poor navigation in Checkmarx hinders their ability to efficiently use the dashboards.

What Are Recent G2 Reviews of Checkmarx?

What Are G2 Users Discussing About Checkmarx?

Semgrep

Semgrep is a modern static analysis (SAST), software composition analysis (SCA), and secrets detection platform designed for both developers and security teams. It combines fast, deterministic analysis with context-aware AI that triages findings like a senior security engineer. The AI Assistant helps reduce false positives, prioritize meaningful results, and offers clear remediation guidance. Its “Memories” feature learns from past decisions to further reduce triage noise over time. Semgrep also supports deep analysis of transitive dependencies, not just direct ones, helping teams surface and address hidden risks in their supply chain. It integrates well into modern development workflows and is easy to customize across environments.

Average Rating: 4.6/5.0

Total Reviews: 56

How Do G2 Users Rate Semgrep?

  • Test Automation: 9.2/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.1/10)
  • Quality of Support: 8.8/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 7.5/10 (Category avg: 8.5/10)

Who Is the Company Behind Semgrep?

  • Seller: Semgrep
  • Year Founded: 2017
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    265 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 45% Large, 43% Medium

What Do G2 Reviewers Say About Semgrep?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Semgrep, enabled by its intuitive syntax and smooth integration with CI/CD.
  • Users appreciate the flexibility and speed of Semgrep in enforcing coding standards and catching vulnerabilities effectively.
  • Users appreciate the effective vulnerability detection of Semgrep, facilitating quick identification and resolution of security issues.
  • Users appreciate the scanning efficiency of Semgrep, benefiting from rapid scans and streamlined CI/CD integration.
  • Users value Semgrep for its effective security vulnerability detection, enabling quick resolutions without hindering development speed.
Cons
  • Users find Semgrep not user-friendly due to a steep learning curve and complex initial setup requirements.
  • Users find the limited features of Semgrep restrict its usability and complicate effective vulnerability management.
  • Users find the difficult learning curve for Semgrep daunting, especially for creating advanced rules and setups.
  • Users express concerns about the lack of guidance in creating custom rules, complicating effective use of Semgrep.
  • Users note a steep learning curve for Semgrep's rule syntax, making it challenging for newcomers to master.

What Are Recent G2 Reviews of Semgrep?

Snyk

Snyk (pronounced sneak) is a developer security platform for securing custom code, open source dependencies, containers, and cloud infrastructure all from a single platform. Snyk’s developer security solutions enable modern applications to be built securely, empowering developers to own and build security for the whole application, from code & open source to containers & cloud infrastructure. Secure while you code in your IDE: find issues quickly using the scanner, fix issues easily with remediation advice, verify the updated code. Integrate your source code repositories to secure applications: integrate a repository to find issues, prioritize with context, fix & merge. Secure your containers as you build, throughout the SDLC: start fixing containers as soon as your write a Dockerfile, continuously monitor container images throughout their lifecycle, and prioritize with context. Secure build and deployment pipelines: Integrate natively with your CI/CD tool, configure your rules, find & fix issues in your application, and monitor your applications. Secure your apps quickly with Snyk’s vulnerability scanning and automated fixes - Try for Free!

Average Rating: 4.5/5.0

Total Reviews: 136

How Do G2 Users Rate Snyk?

  • Test Automation: 7.8/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.1/10)
  • Quality of Support: 8.6/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 6.2/10 (Category avg: 8.5/10)

Who Is the Company Behind Snyk?

  • Seller: Snyk
  • HQ Location: Boston, Massachusetts
  • LinkedIn® Page: www.linkedin.com
    1,764 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 45% Medium, 35% Small

What Do G2 Reviewers Say About Snyk?

AI-generated summary from verified user reviews

Pros
  • Users appreciate Snyk's vulnerability detection, which enables timely identification and remediation of security issues.
  • Users value Snyk for its rapid vulnerability identification, significantly enhancing code security and DevOps efficiency.
  • Users value Snyk's easy integration setup, enhancing workflow and efficiency in vulnerability management within CI/CD pipelines.
  • Users find Snyk's easy setup with GitHub highly beneficial for seamless integration and vulnerability management.
  • Users appreciate the intuitive GUI and robust organizational features of Snyk, streamlining vulnerability management and reporting.
Cons
  • Users experience false positives from Snyk, leading to confusion and delays in their workflow.
  • Users find the poor interface design of Snyk inconvenient and seek better integration and usability.
  • Users express concerns over high pricing, especially for full feature access, though they see long-term value.
  • Users face scanning issues with false positives, slow scans, and lack of integration affecting workflow efficiency.
  • Users experience false positives and slow scans with Snyk, complicating integration and reducing effectiveness in detecting issues.

What Are Recent G2 Reviews of Snyk?

What Are G2 Users Discussing About Snyk?

Mend.io

Modern risk doesn't live in one layer, it lives between them. Mend.io is built for every risk, across AI and AppSec, securing the code layer, the AI layer, and the interactions between them. From discovery and red teaming to guardrails and runtime protection, Mend.io delivers continuous protection across the entire AI application lifecycle. Mend.io solutions include: 1. Mend AI secures the layer where modern risk actually lives—the interaction between code and AI. It continuously discovers AI components (agents, prompts, models), tests real behavioral risk through automated red teaming, and enforces in-app runtime guardrails for one continuous control system for the AI lifecycle. 2. Mend AppSec secures the modern code layer by continuously discovering and prioritizing risk across code, libraries, containers, and dependencies, giving teams the clarity they need to reduce exposure and ship secure software faster. 3. Mend Renovate secures the foundation of every codebase by automatically updating dependencies, rating the likelihood each update will succeed without breaking changes, and grouping them by confidence level so teams can resolve them faster.

Average Rating: 4.3/5.0

Total Reviews: 117

How Do G2 Users Rate Mend.io?

  • Test Automation: 7.2/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.1/10)
  • Quality of Support: 8.7/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 8.3/10 (Category avg: 8.5/10)

Who Is the Company Behind Mend.io?

  • Seller: Mend
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Boston, Massachusetts
  • LinkedIn® Page: www.linkedin.com
    259 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 36% Small, 33% Large

What Do G2 Reviewers Say About Mend.io?

AI-generated summary from verified user reviews

Pros
  • Users highlight the scanning efficiency of Mend.io, enabling seamless integration and effective source code analysis.
  • Users appreciate the ease of use of Mend.io, finding it helpful and easy to integrate into their workflow.
  • Users value the easy integrations with source code repositories, making security management efficient and straightforward.
  • Users praise Mend.io for its quick and accurate scanning capabilities, enhancing efficiency across various platforms.
  • Users value the automated vulnerability detection in Mend.io, enabling quick identification and resolution of critical issues.
Cons
  • Users face integration issues, finding it challenging to connect with on-premise tools and experiencing configuration problems.
  • Users find the limited features of Mend.io challenging, requiring workarounds for integration and specific use cases.
  • Users find missing features in Mend.io, struggling with integration and needing additional functionality for their workflows.
  • Users report complex implementation with numerous issues, including false positives and difficult integration processes.
  • Users find the interface confusing due to navigating between different portals for SAST and SCA products.

What Are Recent G2 Reviews of Mend.io?

What Are G2 Users Discussing About Mend.io?

Black Duck Polaris Platform

Black Duck builds trust in software by enabling organizations to manage application security, quality, and compliance risks at the speed their business demands. Black Duck solutions help developers to secure code as fast as they write it, development and DevSecOps teams to automate testing within development pipelines without compromising velocity, and security teams to proactively manage risk and focus remediation efforts on what matters most. With Black Duck, organizations can transform the way they build and deliver software, aligning people, processes, and technology to intelligently address software risks across their portfolio and at all stages of the application lifecycle.

Average Rating: 4.2/5.0

Total Reviews: 103

How Do G2 Users Rate Black Duck Polaris Platform?

  • Test Automation: 8.1/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.4/10 (Category avg: 9.1/10)
  • Quality of Support: 8.5/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 8.6/10 (Category avg: 8.5/10)

Who Is the Company Behind Black Duck Polaris Platform?

  • Seller: Black Duck
  • Year Founded: 2024
  • HQ Location: Burlington, US
  • LinkedIn® Page: www.linkedin.com
    1,317 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 53% Large, 32% Medium

What Do G2 Reviewers Say About Black Duck Polaris Platform?

AI-generated summary from verified user reviews

Pros
  • Users commend the accuracy of findings in Black Duck Polaris, especially its powerful engine for identifying open source issues.
  • Users praise the powerful open source issue identification by Black Duck Polaris, benefiting from extensive Black Duck Knowledge.
Cons
  • Users note that the platform requires huge resource constraints for on-prem deployment, impacting its usability.

What Are Recent G2 Reviews of Black Duck Polaris Platform?

What Are G2 Users Discussing About Black Duck Polaris Platform?

JFrog

JFrog Ltd. (Nasdaq: FROG), the creators of the unified DevOps, DevSecOps, DevGovOps and MLOps platform, is on a mission to create a world of software delivered without friction from development to production. Driven by a “Liquid Software” vision to keep software continuously flowing, secure, and always up to date, the JFrog Platform serves as the definitive software supply chain system of record. It is uniquely engineered to power organizations as they build, manage, and distribute trusted software with unprecedented speed, security, and scale across hybrid and multi-cloud environments. As software engineering evolves in the AI era, JFrog’s newest offerings address the industry's most pressing trend: the rise of agentic software development and the hidden security risks of "Shadow AI." In response to threat actors increasingly targeting developer workflows including a massive surge in malicious open-source AI models and infected packages; JFrog has expanded its platform capabilities to deliver absolute end-to-end visibility and automated compliance. Key new innovations include the JFrog AI Catalog, which enables organizations to centralize, govern, and control the lifecycle of AI models approved for enterprise use. To secure autonomous coding environments, JFrog introduced the Universal MCP Registry and the Agent Skills Registry (developed alongside NVIDIA). These new solutions establish the industry’s first enterprise-grade trust layer to safely manage and store AI agent skills, monitor connections, and instantly block unsafe developer tools or malicious coding extensions right where developers work. Furthermore, the integration of advanced DevGovOps and Runtime Security tools allows teams to replace slow, manual compliance audits with continuous, background policy enforcement. By shifting security left directly into the binary pipeline, JFrog ensures that the volume of AI-assisted code does not outpace an organization's ability to verify its safety. Today, millions of users and approximately 6,600 organizations worldwide, including a majority of the Fortune 100, depend on the universal JFrog Platform to eliminate point-solution fatigue, bridge the governance gap, and securely embrace digital transformation. Learn more at www.jfrog.com or follow us on X @JFrog.

Average Rating: 4.2/5.0

Total Reviews: 178

How Do G2 Users Rate JFrog?

  • Has the product been a good partner in doing business?: 8.5/10 (Category avg: 9.1/10)
  • Quality of Support: 8.4/10 (Category avg: 9.2/10)

Who Is the Company Behind JFrog?

  • Seller: JFrog Ltd
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    2,527 employees on LinkedIn®
  • Ownership: NASDAQ: FROG

Who Uses This Product?

  • Who Uses This: Software Engineer, DevOps Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 48% Large, 30% Medium

What Do G2 Reviewers Say About JFrog?

AI-generated summary from verified user reviews

Pros
  • Users highlight the centralized platform of JFrog, facilitating efficient management of artifacts and secure sharing across environments.
  • Users value the centralized repository management in JFrog, making artifact storage and sharing seamless and efficient.
  • Users appreciate the ease of deployment with JFrog, seamlessly integrating CI/CD and security into a single platform.
  • Users value the seamless integrations of JFrog with various CI/CD tools, enhancing their workflow and automation.
  • Users appreciate the easy integrations of JFrog with CI/CD tools, enhancing their DevOps workflows seamlessly.
Cons
  • Users find JFrog's complexity in workflows challenging, especially for newcomers navigating its powerful features.
  • Users note the expensive cost compared to similar products, making it a less attractive option for some.
  • Users find the steep learning curve of JFrog challenging, requiring significant time and training to navigate effectively.
  • Users find difficult learning curves with JFrog, often requiring extensive training to navigate its complex functionalities.
  • Users find the learning difficulty of JFrog frustrating, requiring significant time and training to master its features.

What Are Recent G2 Reviews of JFrog?

What Are G2 Users Discussing About JFrog?

Invicti

Invicti (formerly known as Netsparker) is an enterprise application and API security testing platform that helps organizations secure thousands of web applications and APIs at scale while dramatically reducing the risk of attack. Combining advanced DAST and IAST capabilities in a single platform, Invicti enables security teams to continuously identify, prioritize, and remediate vulnerabilities across complex modern environments with confidence and automation. With Invicti, security teams can: - Automate application security testing workflows and save hundreds of hours every month - Discover and secure all web applications and APIs, including forgotten, unmanaged, and shadow assets - Deliver actionable, developer-friendly feedback that helps teams remediate vulnerabilities faster and build more secure code over time - Reduce false positives with proof-based scanning technology that validates exploitable vulnerabilities - Scale application security programs across large enterprises without slowing development teams - Integrate security seamlessly into existing DevSecOps and CI/CD workflows Built for organizations with the most demanding security requirements, Invicti empowers teams to confidently secure their entire attack surface with accuracy, scalability, and automation.

Average Rating: 4.5/5.0

Total Reviews: 69

How Do G2 Users Rate Invicti?

  • Test Automation: 10.0/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.1/10)
  • Quality of Support: 8.9/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 10.0/10 (Category avg: 8.5/10)

Who Is the Company Behind Invicti?

  • Seller: Invicti Security
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Austin, Texas
  • LinkedIn® Page: www.linkedin.com
    326 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 46% Large, 29% Medium

What Do G2 Reviewers Say About Invicti?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Invicti, highlighting its quick setup and straightforward report generation.
  • Users value the effective scanning technology of Invicti, enabling accurate identification of vulnerabilities and streamlined workflows.
  • Users value the accuracy and integration capabilities of Invicti, enhancing efficiency and simplifying reporting processes.
  • Users appreciate the well-formatted and easy-to-read reports from Invicti, simplifying certification processes significantly.
  • Users value the super accurate vulnerability detection of Invicti, enhancing their security workflows efficiently.
Cons
  • Users find the customer support inadequate, struggling with timely responses and effective solutions to issues.
  • Users experience slow performance during scans and setup, which affects their overall satisfaction with Invicti.
  • Users experience slow scanning issues with Invicti, affecting efficiency despite good support and solid performance once set up.
  • Users face API scanning issues with Invicti, limiting its effectiveness for their specific needs despite good support.
  • Users find the complex setup to be overwhelming initially, impacting the ease of using Invicti effectively.

What Are Recent G2 Reviews of Invicti?

What Are G2 Users Discussing About Invicti?

Contrast Security

Contrast Security is the global leader in Application Detection and Response (ADR), empowering organizations to see and stop attacks on applications and APIs in real time. Contrast embeds patented threat sensors directly into the software, delivering unmatched visibility and protection. With continuous, real-time defense, Contrast uncovers hidden application layer risks that traditional solutions miss. Contrast’s powerful Runtime Security technology equips developers, AppSec teams and SecOps with one platform that proactively protects and defends applications and APIs against evolving threats.

Average Rating: 4.5/5.0

Total Reviews: 49

How Do G2 Users Rate Contrast Security?

  • Test Automation: 8.3/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.1/10)
  • Quality of Support: 9.3/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 9.0/10 (Category avg: 8.5/10)

Who Is the Company Behind Contrast Security?

Who Uses This Product?

  • Top Industries: Insurance, Information Technology and Services
  • Company Size: 67% Large, 20% Medium

What Do G2 Reviewers Say About Contrast Security?

AI-generated summary from verified user reviews

Pros
  • Users value the accuracy of findings from Contrast Security, ensuring greater precision in identifying vulnerabilities.
  • Users value the accuracy of results from Contrast Security, benefiting from precise vulnerability monitoring and analysis.
  • Users commend the real-time vulnerability detection of Contrast Security, appreciating its quick feedback and agile support.
Cons
  • Users experienced performance issues with Contrast Security, particularly with Java applications, but found support helpful in resolving them.

What Are Recent G2 Reviews of Contrast Security?

What Are G2 Users Discussing About Contrast Security?

CodeScan

CodeScan Shield addresses code quality, security, and compliance liabilities with two automated modules: CodeScan and OrgScan. CodeScan provides static code analysis for total visibility into code health from the moment it’s written through production. OrgScan governs organizational policies by enforcing the security and compliance rules mandated for your Salesforce environment. Together, they ensure the code that makes up your Salesforce environment and the way the environment is being utilized will always meet high standards. The result is strengthened data security, streamlined DevSecOps processes, and an assurance of meeting compliance standards—avoiding potentially thousands of dollars in fines and lost opportunities. CodeScan Shield protects your Salesforce org from both the inside and outside. CodeScan provides dashboards and reports for consistent code visibility, while also alerting developers the moment new errors are introduced. OrgScan analyzes Salesforce policies to ensure the organization remains compliant with client-mandated specifications and guidelines. Violations are flagged and recorded in an interactive dashboard. Progress is tracked for policy reviews. Collectively, these features ensure admins maintain governance control within their organization. CodeScan Shield is part of AutoRABIT’s complete DevSecOps platform. Enabling Salesforce DevOps teams with CodeScan Shield’s powerful technology produces high-quality, secure applications and updates at speed.

Average Rating: 4.6/5.0

Total Reviews: 30

How Do G2 Users Rate CodeScan?

  • Test Automation: 7.3/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.1/10)
  • Quality of Support: 9.0/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 8.3/10 (Category avg: 8.5/10)

Who Is the Company Behind CodeScan?

  • Seller: AutoRABIT
  • Year Founded: 2015
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    283 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 44% Large, 38% Medium

What Are Recent G2 Reviews of CodeScan?

What Are G2 Users Discussing About CodeScan?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated